
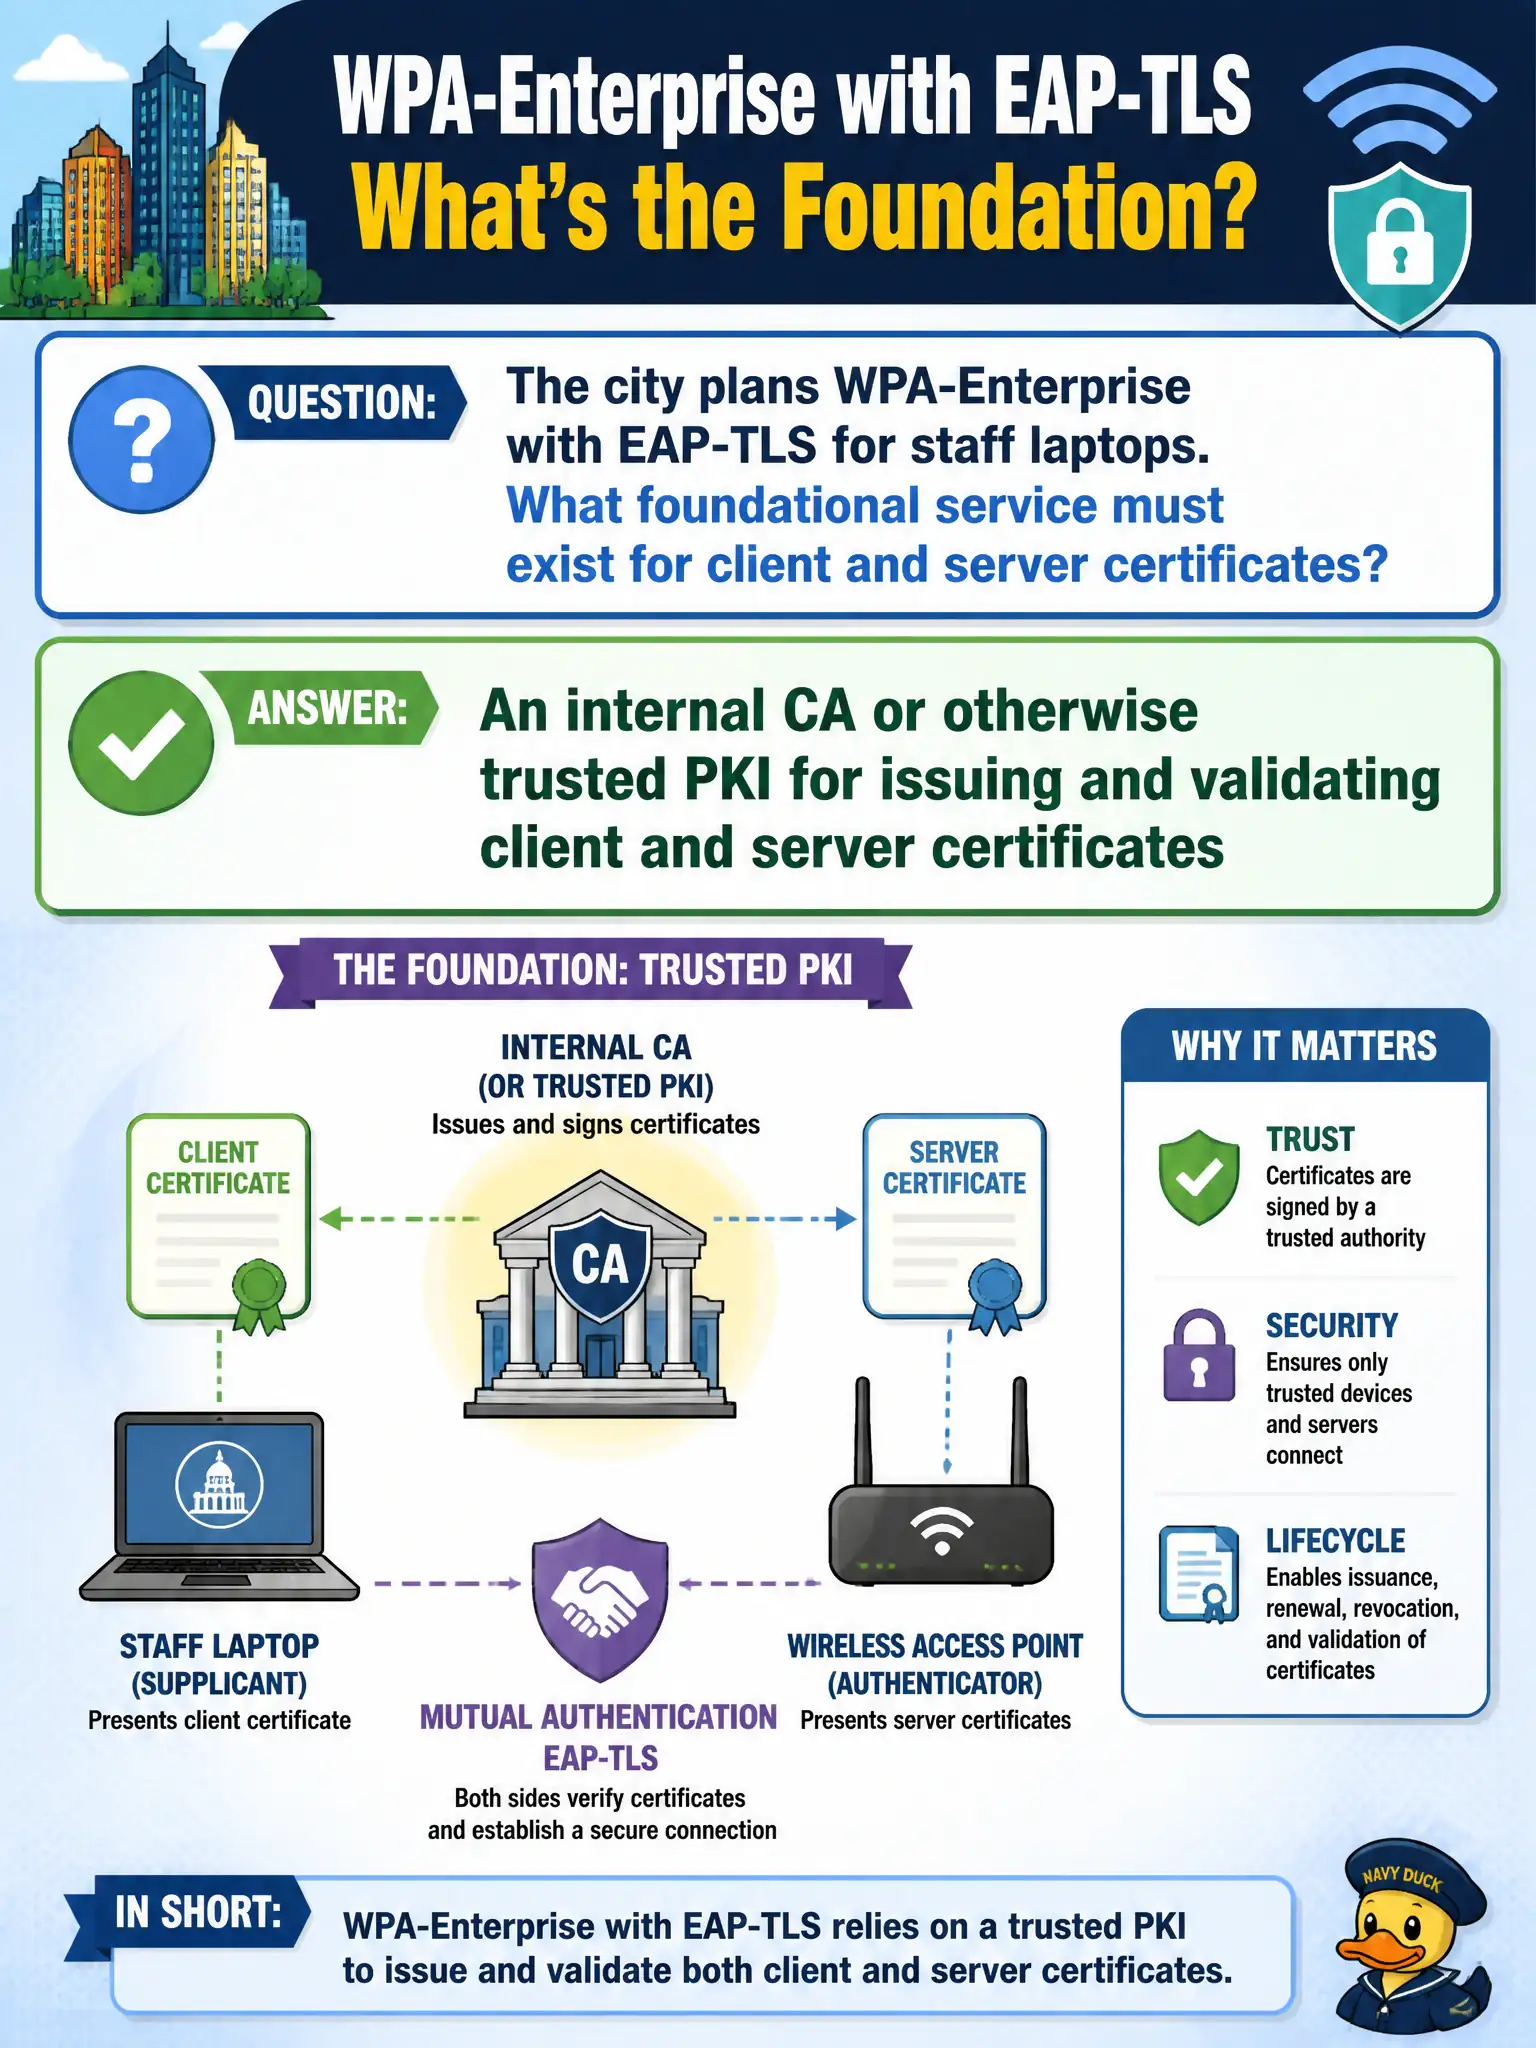
The city plans WPA-Enterprise with EAP-TLS for staff laptops. What foundational service must exist for client and server certificates?
Select an answer to reveal the explanation.
Short Explanation
EAP-TLS lives and dies on certificates, so you need a trusted CA/PKI. FTP’d PSKs, skipped checks, or MAC lists are not that foundation.
Full Explanation
When the city plans WPA-Enterprise with EAP-TLS for staff laptops, the foundational service that must exist is an internal CA or otherwise trusted PKI for issuing and validating client and server certificates. EAP-TLS mutual certificate authentication depends on trustworthy issuance, revocation information, and trust-anchor distribution to both RADIUS and clients. Without PKI, EAP-TLS is a configuration checkbox with nothing trustworthy for the parties to present or validate on a municipal staff SSID. A public FTP server hosting shared PSK files is not a certificate authority and actively undermines Enterprise goals. A captive portal that skips certificate checks for convenience teaches clients the opposite of TLS hygiene. MAC ACL entries are not a substitute for certificates and provide only weak, spoofable identity unsuitable as the EAP-TLS foundation. Exam caveat: server certificate validation on clients is as important as issuing client certificates—PKI includes trust configuration and revocation checking, not only enrollment quantity metrics. Operational check: enroll a lab laptop with a client certificate from the city CA, configure the SSID for EAP-TLS with server validation enabled, confirm successful authentication, then revoke the certificate and confirm subsequent access fails as expected.