
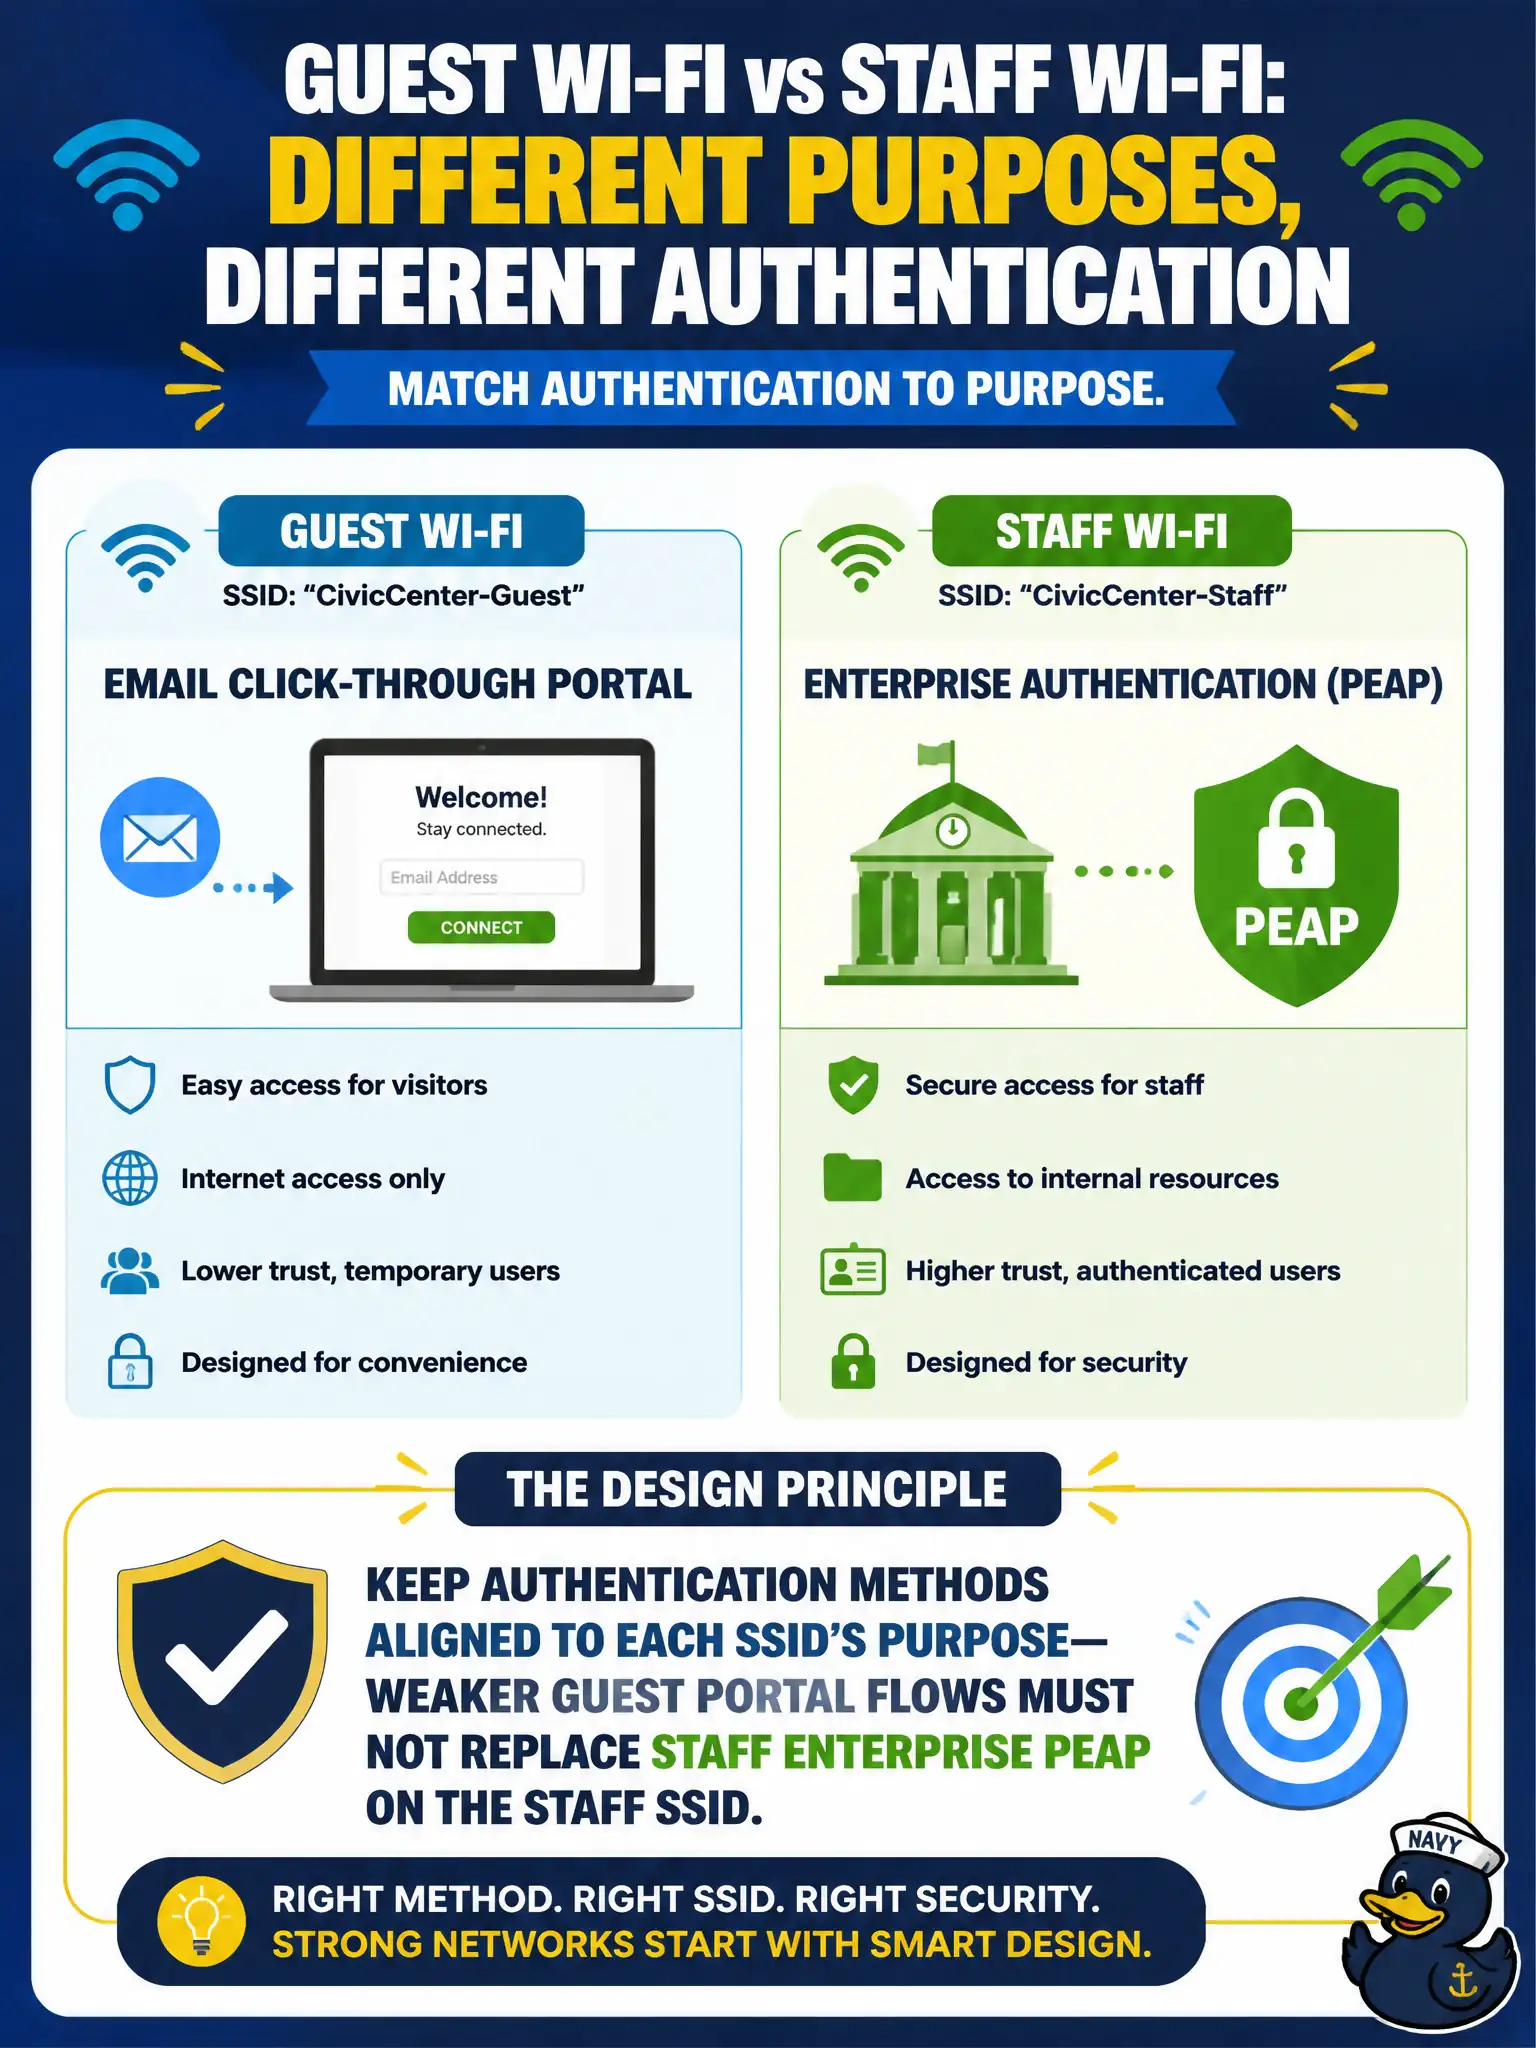
Guest Wi-Fi at the civic center uses an email click-through portal, while the staff SSID uses PEAP. What design principle should remain true?
Select an answer to reveal the explanation.
Short Explanation
Right lock for the right door: guests can click an email portal; staff still need PEAP (or better) on the staff SSID. Don’t drag employees onto the guest path or borrow staff passwords for visitors.
Full Explanation
Guest Wi-Fi at the civic center may use an email click-through portal while the staff SSID uses PEAP, but authentication methods must stay aligned to each SSID’s purpose—weaker guest portal flows must not replace staff Enterprise PEAP on the staff SSID. Moving staff PEAP users onto the guest portal to simplify AAA downgrades staff security. Requiring guests to complete PEAP with staff AD passwords invites credential theft and over-privileging. Disabling encryption on the staff SSID because the guest portal collected an email confuses portal identity proof with link confidentiality. Exam caveat: different SSIDs intentionally use different auth strengths; do not “simplify” by collapsing staff into guest controls. Operational check: verify staff SSID still requires PEAP (or stronger), guest remains on portal/VLAN isolation, and no shared credential path exists between them. Include this separation check in the civic center quarterly wireless audit. In municipal WLAN operations, record the rationale in the change ticket so future on-call staff know which control was chosen and which failure modes the rejected options would create for city services. Re-validate after the next maintenance window that the same control still holds under the infrastructure versions and client fleets used by the civic environment.