
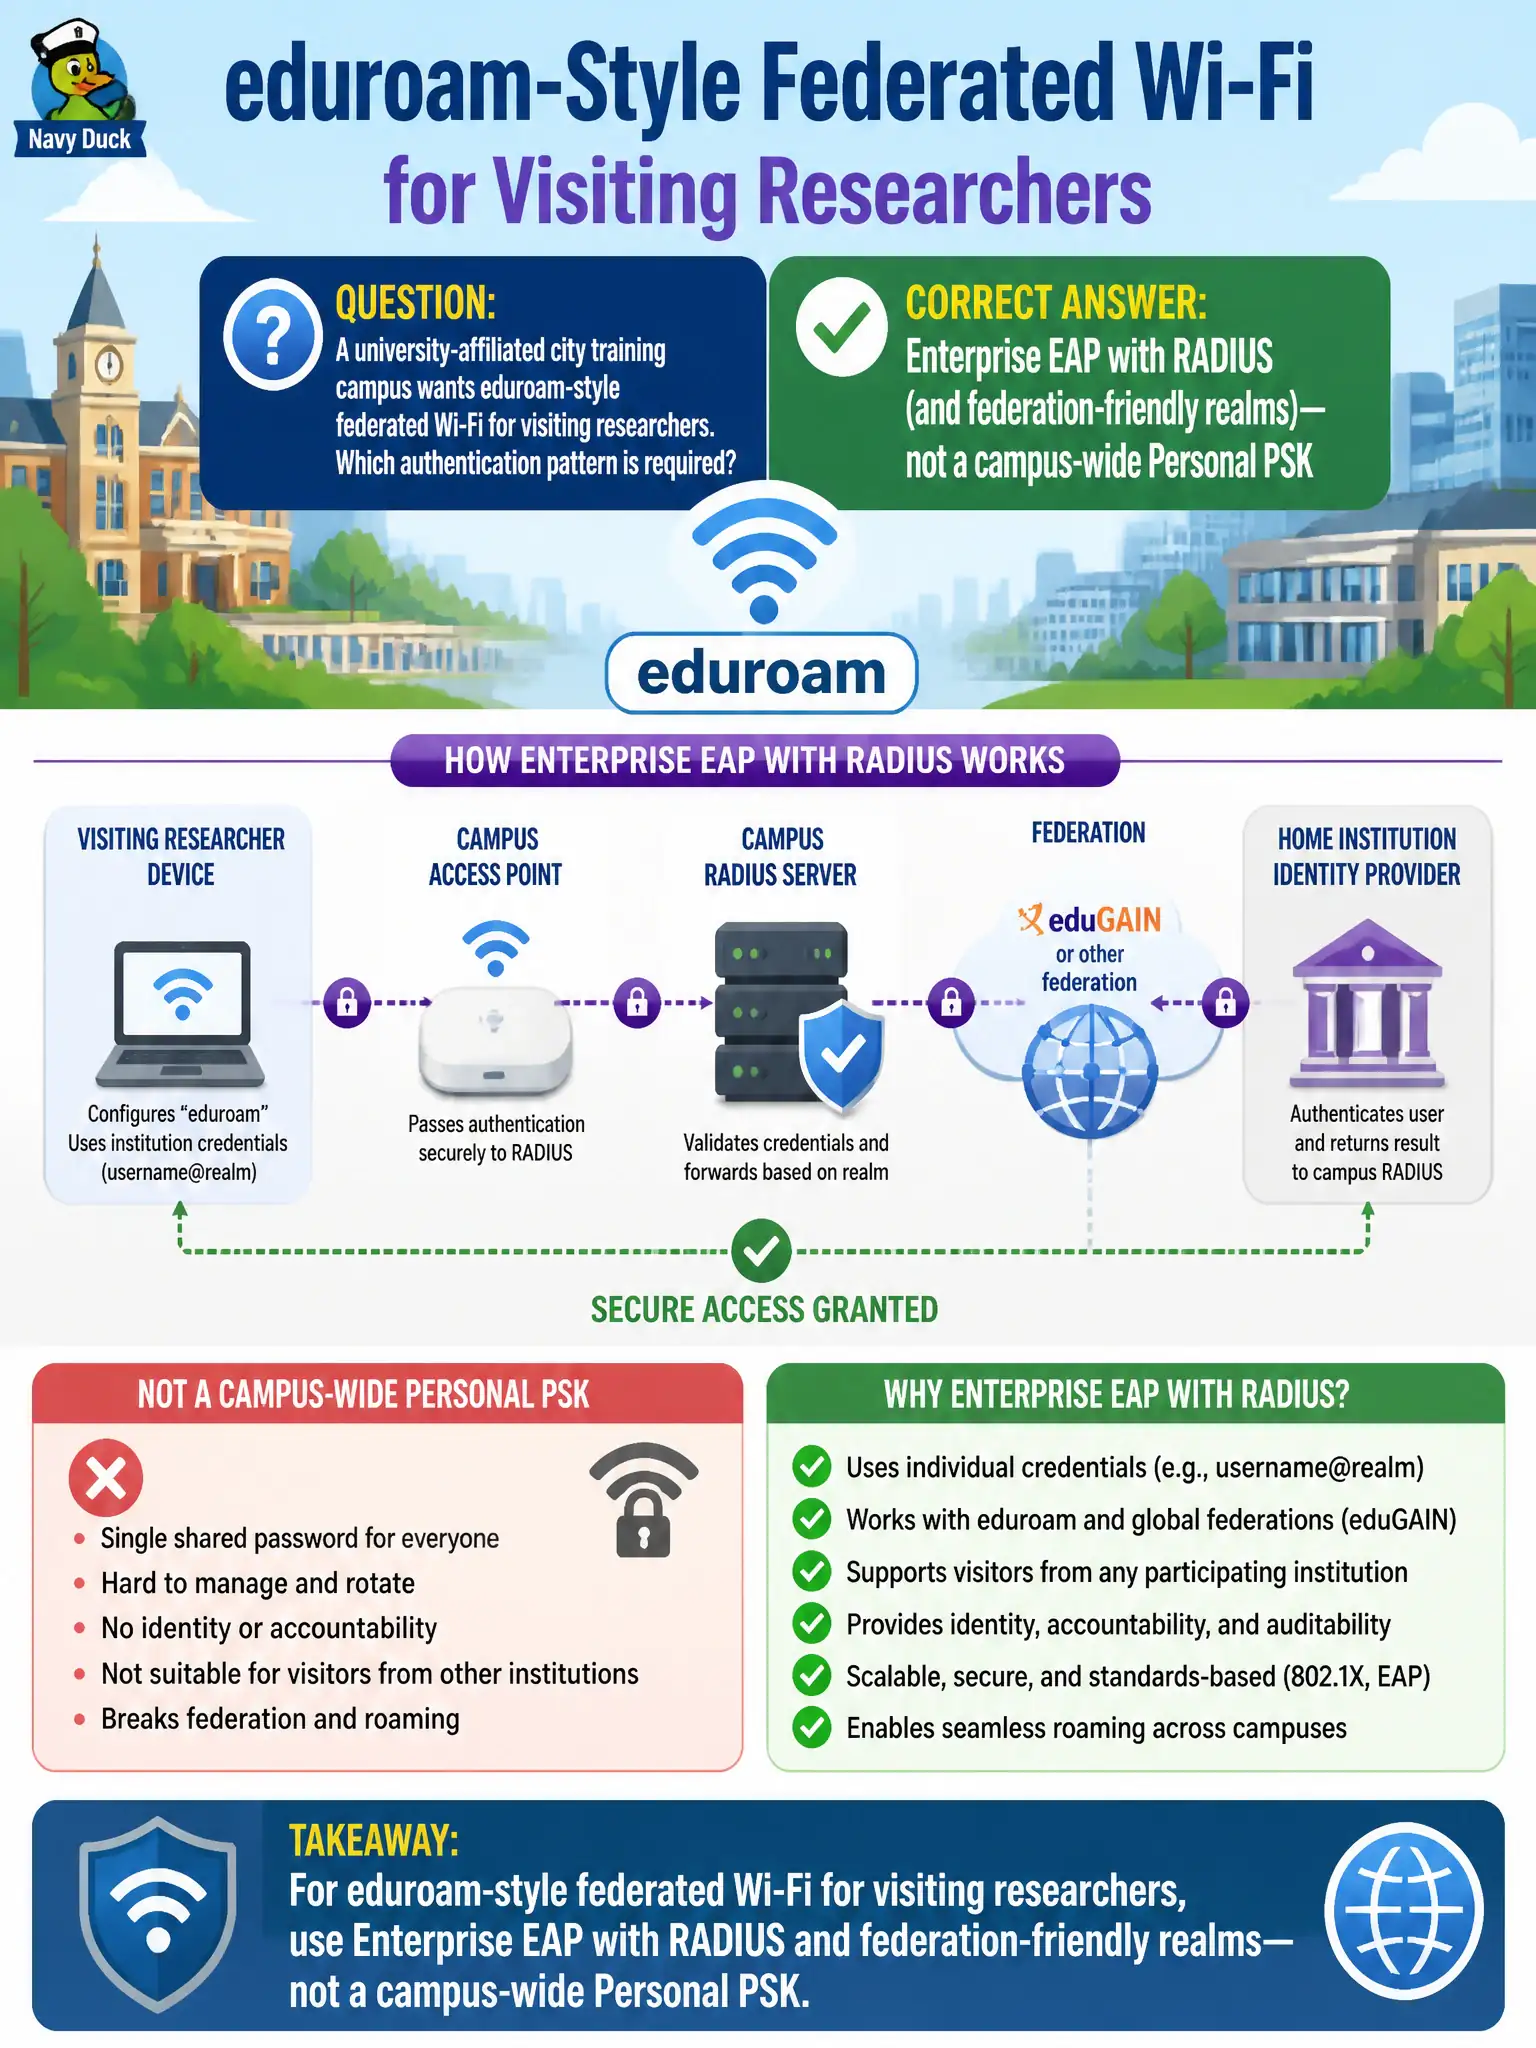
A university-affiliated city training campus wants eduroam-style federated Wi-Fi for visiting researchers. Which authentication pattern is required?
Select an answer to reveal the explanation.
Short Explanation
Federated campus Wi-Fi is an Enterprise EAP/RADIUS world—realms, home AAA, visiting users. A single slide-deck PSK or WEP shared across schools isn’t eduroam-style design.
Full Explanation
A university-affiliated city training campus wanting eduroam-style federated Wi-Fi for visiting researchers requires Enterprise EAP with RADIUS and federation-friendly realms—not a campus-wide Personal PSK. One WPA2-Personal passphrase on orientation slides cannot federate identities across institutions. Open authentication with MAC filtering lacks federated user auth. WEP with quarterly key ceremonies between schools is deprecated and non-federated. Exam caveat: federation patterns (eduroam-style) are Enterprise RADIUS/EAP realm designs; Personal PSK cannot provide inter-realm trust. Operational check: configure RADIUS realm routing for visiting researchers, test a partner IdP login on the campus SSID, validate VLAN/ACL assignment for visitors, and document support contacts. Align the build with municipal and university federation agreements before advertising the service. In municipal WLAN operations, record the rationale in the change ticket so future on-call staff know which control was chosen and which failure modes the rejected options would create for city services. Re-validate after the next maintenance window that the same control still holds under the infrastructure versions and client fleets used by the civic environment.