
Contractor badges at a municipal data center map to Active Directory groups that should control Wi-Fi access. Which authentication approach should be selected?
Select an answer to reveal the explanation.
Short Explanation
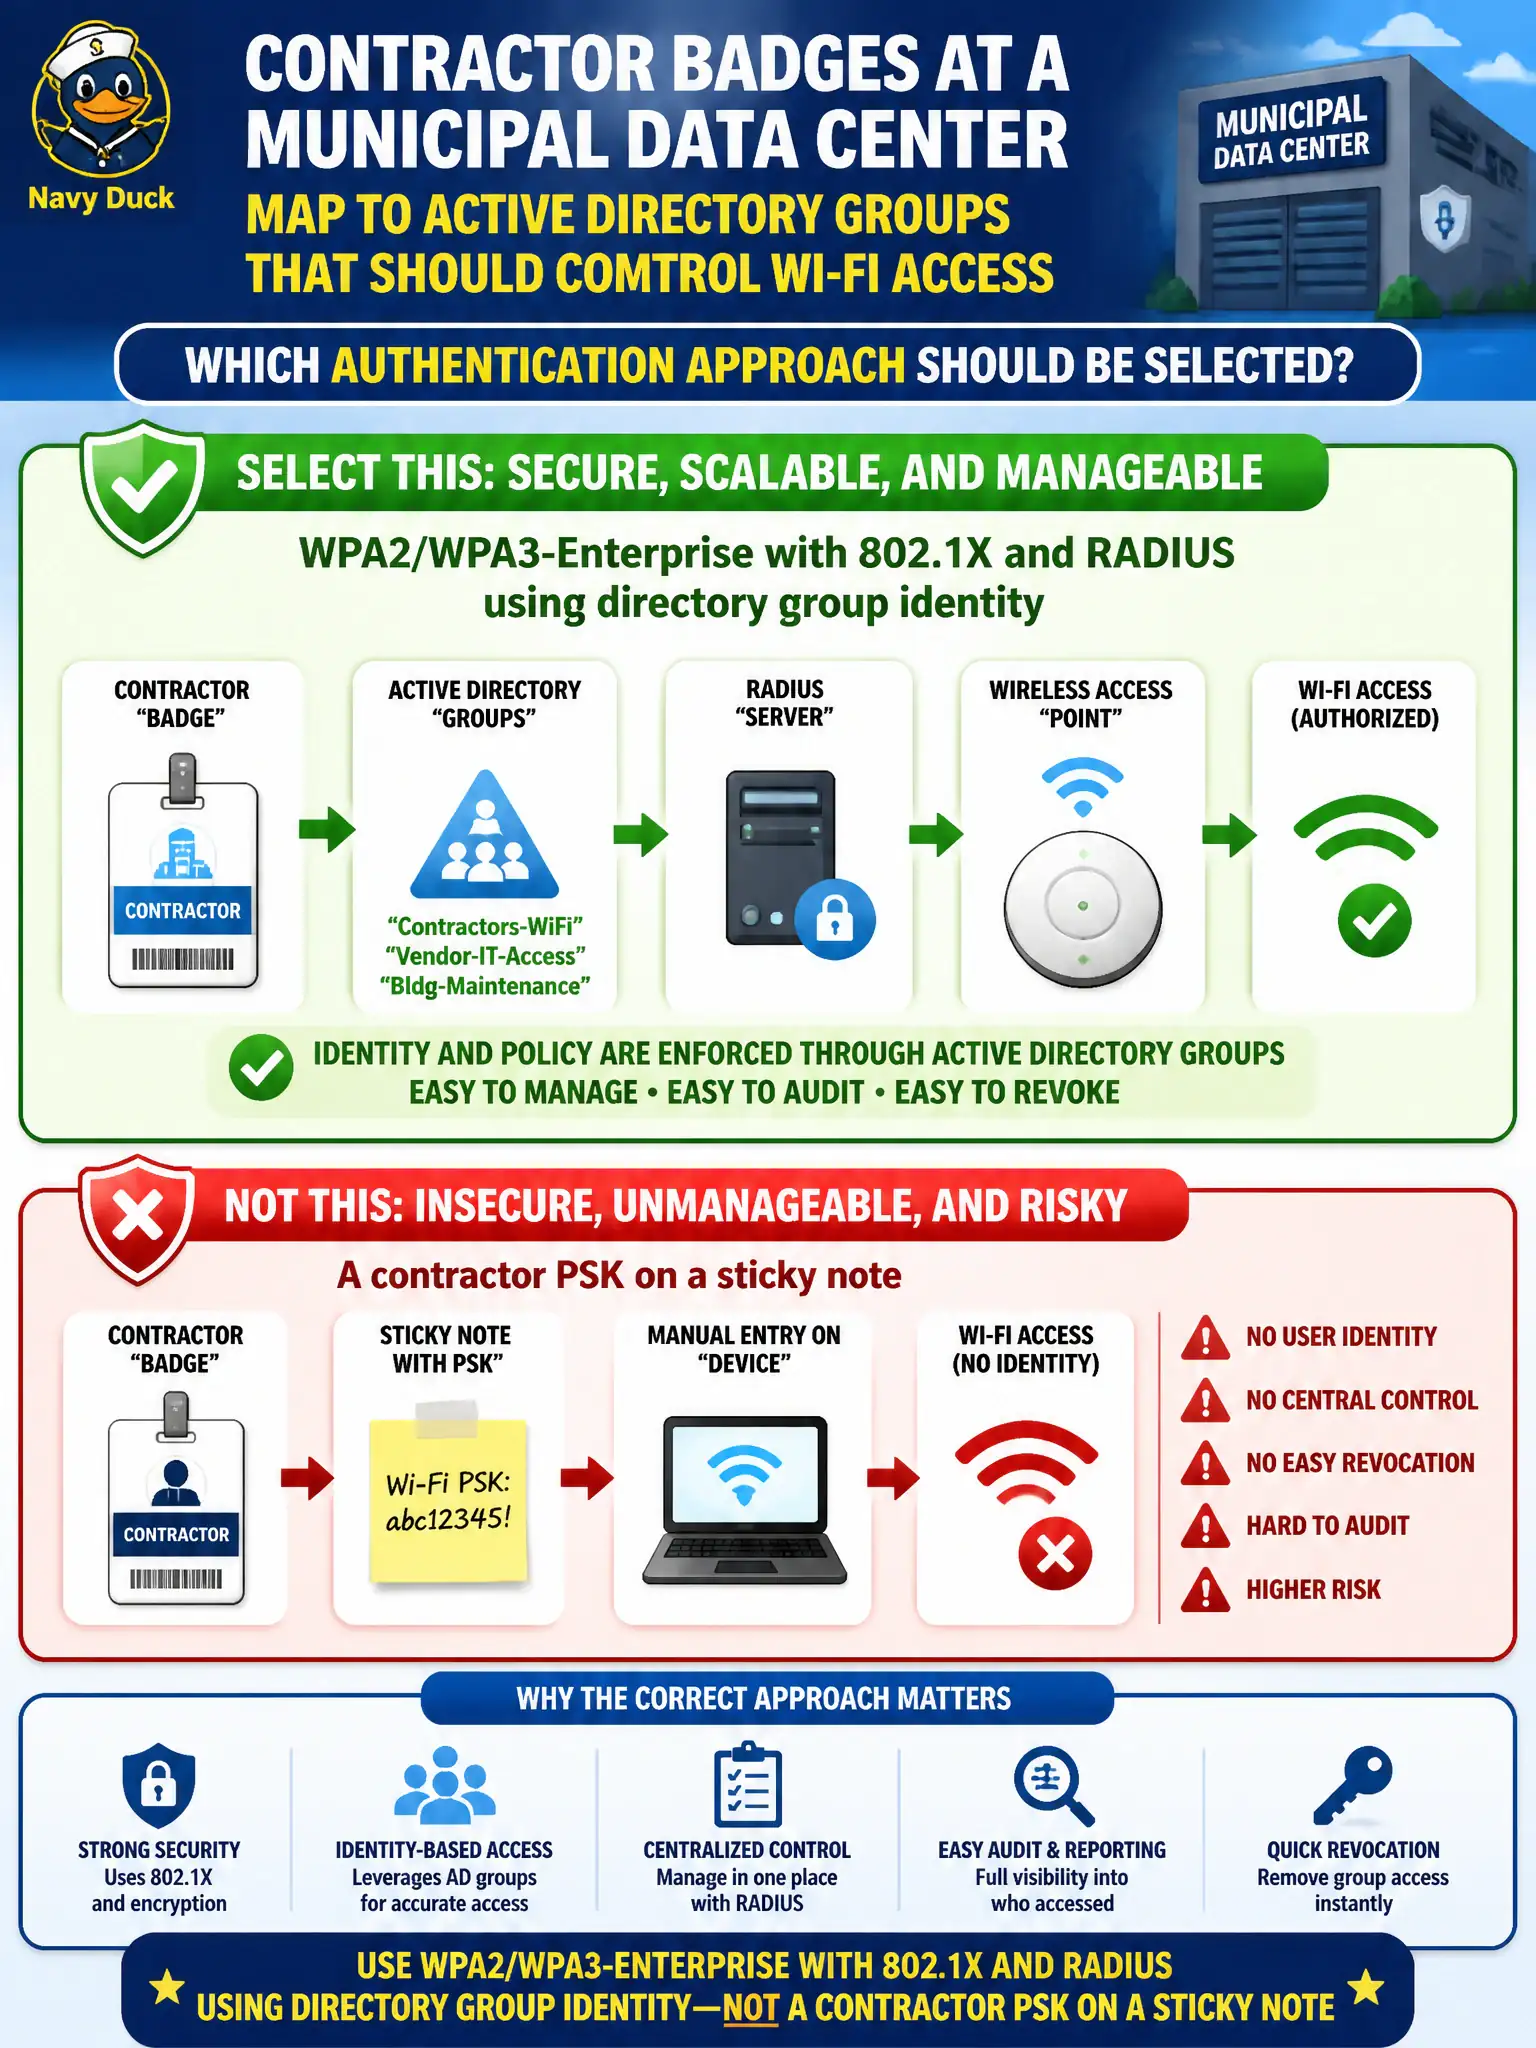
If badges already map to AD groups, use Enterprise 802.1X and RADIUS so Wi-Fi follows identity—not a sticky-note PSK for ‘all contractors.’ MACs and open SSIDs don’t read group membership.
Full Explanation
Contractor badges at a municipal data center that map to Active Directory groups should drive Wi-Fi access through WPA2/WPA3-Enterprise with 802.1X and RADIUS using directory group identity—not a contractor PSK on a sticky note. One shared WPA2-Personal passphrase emailed to every contractor firm cannot enforce group-based access or clean offboarding. An open SSID with the passphrase on visitor lanyards is worse. MAC allow-listing alone without user or group identity fails badge-driven authorization goals. Exam caveat: directory group control implies Enterprise AAA with authorization attributes—Personal and MAC-only designs cannot express AD group policy meaningfully. Operational check: map badge AD groups to RADIUS authorization (VLAN/ACL/role), test contractor join/leave, and confirm access revokes when the group membership ends. Document the group-to-role mapping in the municipal data-center WLAN access matrix. In municipal WLAN operations, record the rationale in the change ticket so future on-call staff know which control was chosen and which failure modes the rejected options would create for city services. Re-validate after the next maintenance window that the same control still holds under the infrastructure versions and client fleets used by the civic environment.