
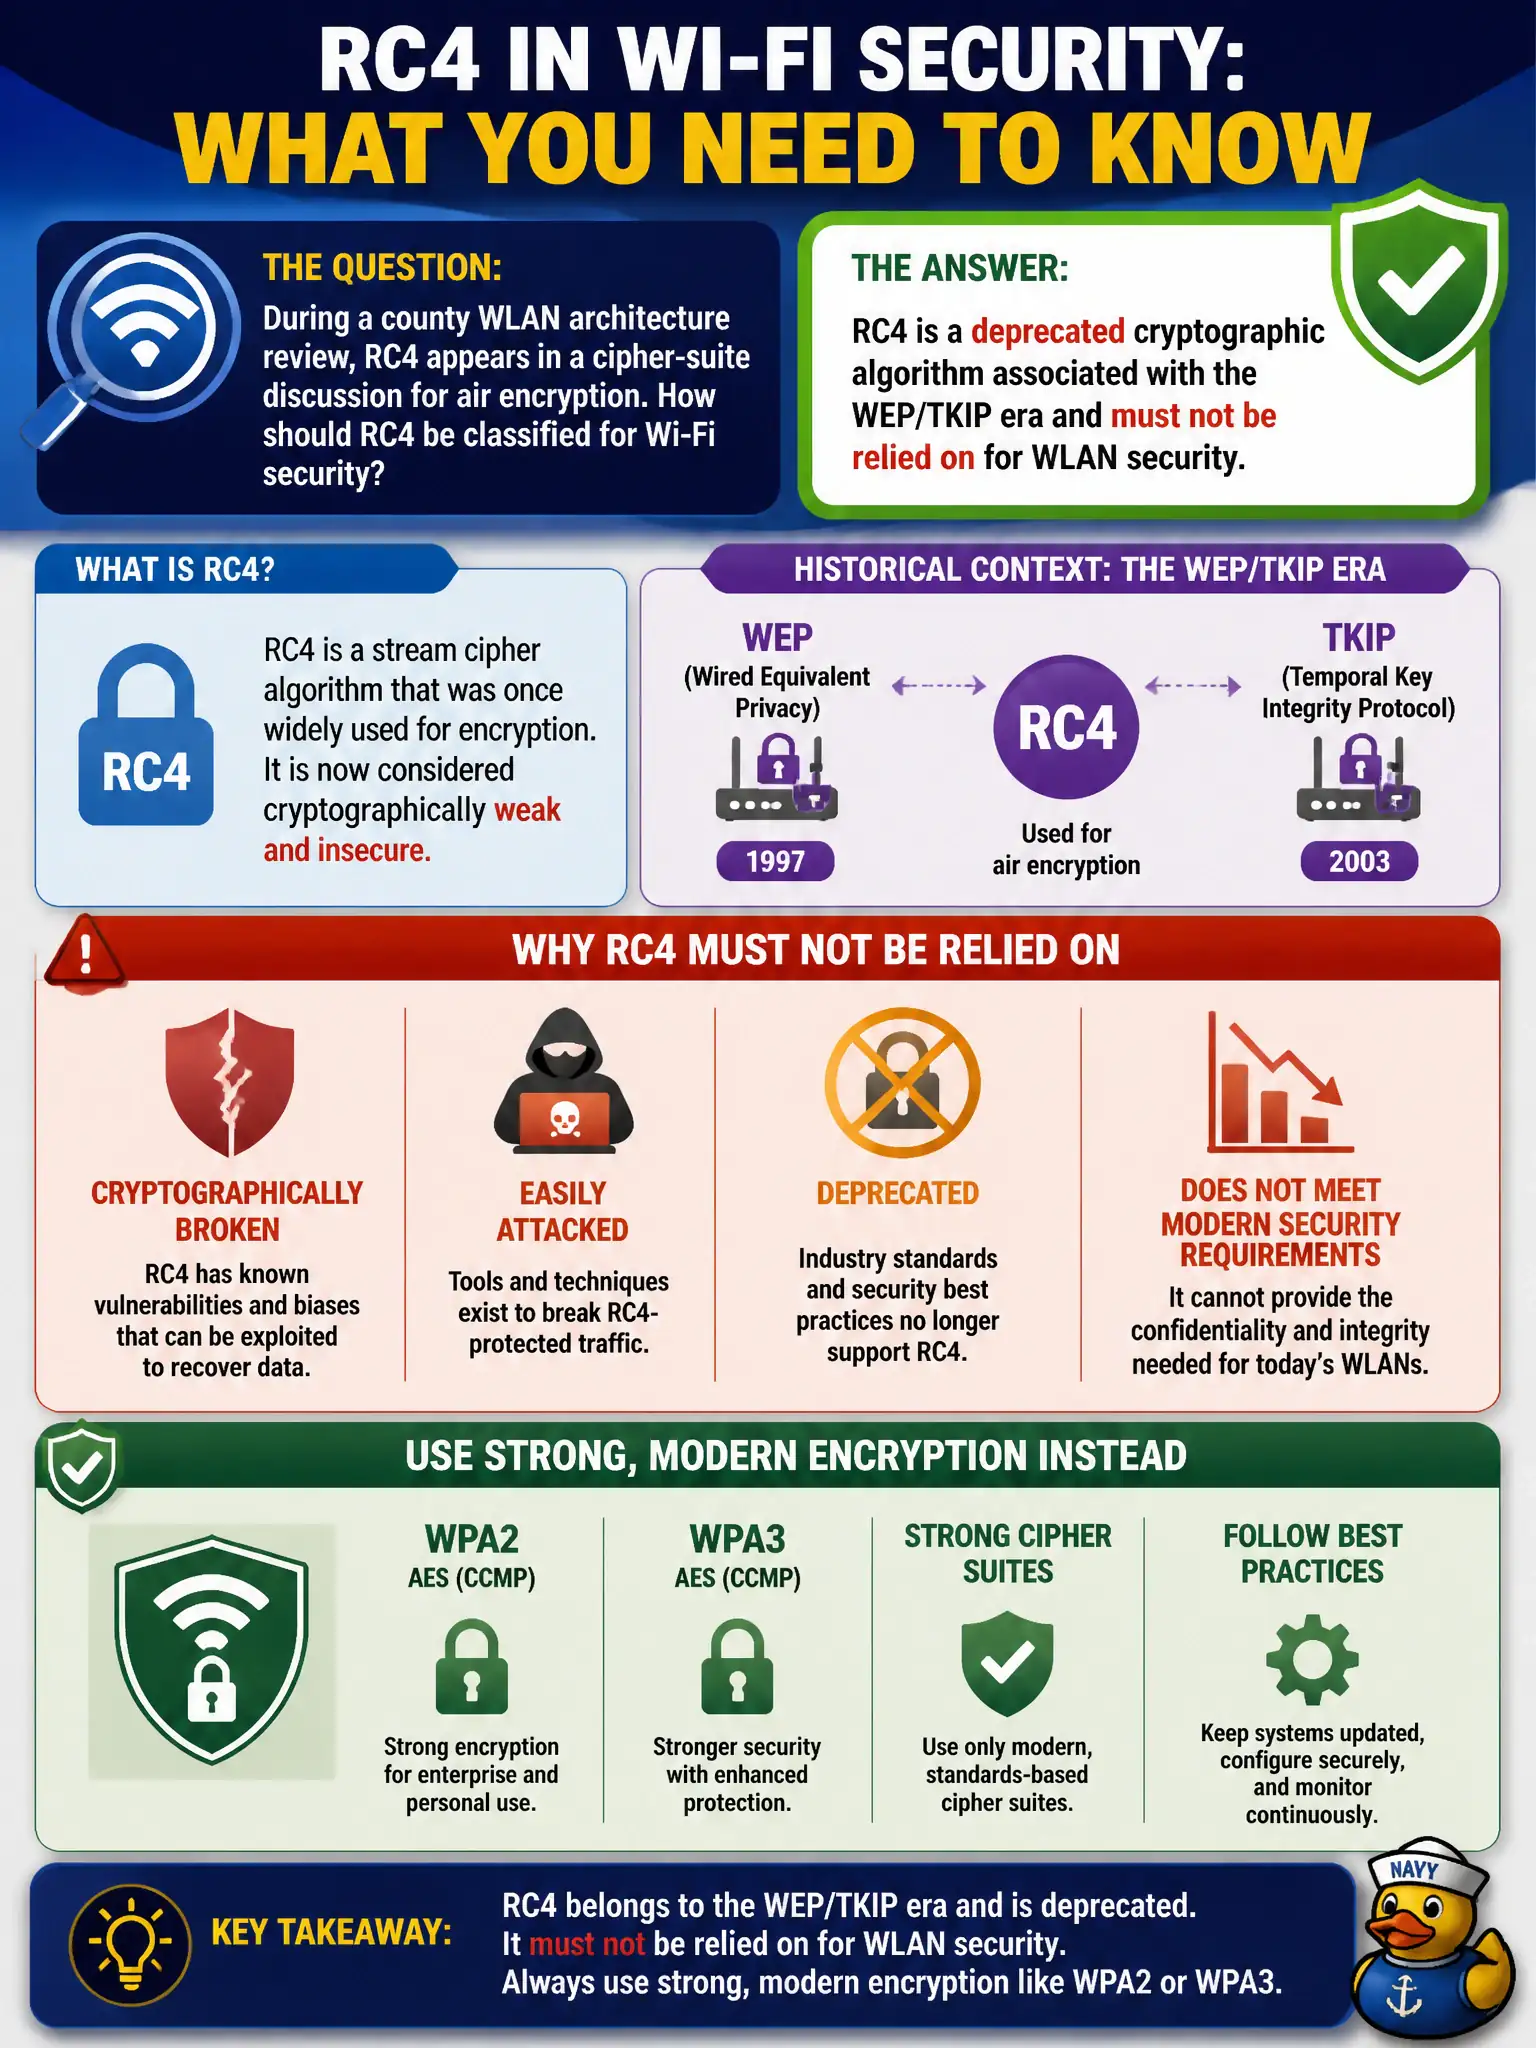
During a county WLAN architecture review, RC4 appears in a cipher-suite discussion for air encryption. How should RC4 be classified for Wi-Fi security?
Select an answer to reveal the explanation.
Short Explanation
RC4 is the old stream-cipher workhorse that rode along with WEP and TKIP—and that whole neighborhood is condemned. Do not plan new county Wi-Fi security around it; AES-based suites are the grown-up answer.
Full Explanation
RC4 is a deprecated cryptographic algorithm associated with the WEP and TKIP constructions and must not be relied on for WLAN air encryption in a county architecture review. Modern civic WLAN designs use AES-based CCMP and GCMP (and related modes), not RC4 stream-cipher constructions from the early 802.11 security era. Claiming RC4 is mandatory for WPA3-Enterprise 192-bit mode is false; that mode is built around strong AES suites, not RC4. Asserting RC4 replaced AES-CCMP as the 2024 civic standard reverses history. Saying RC4 is only deprecated for HTTPS, never for 802.11, ignores CWSP deprecated-solutions coverage of RC4 in the Wi-Fi security stack. Exam caveat: when an item names RC4, WEP, TKIP, or original WPA together, the expected judgment is elimination and migration to AES-based robust security—not clever reuse or sector carve-outs. Operational check: search controller templates and RSN IE reports for TKIP/WEP/RC4-era suites, remediate any SSID still offering them, and re-scan after change windows. File the finding under the county deprecated-crypto backlog with owners and dates so architecture reviews do not rediscover the same RC4 discussion annually. In municipal WLAN operations, record the rationale in the change ticket so future on-call staff know which control was chosen and which failure modes the rejected options would create for city services. Re-validate after the next maintenance window that the same control still holds under the infrastructure versions and client fleets used by the civic environment.