
Config audits show drift re-enabled cleartext HTTP administration on several library-branch access points that policy requires to use HTTPS-only management. What remediation best restores policy conformance?
Select an answer to reveal the explanation.
Short Explanation
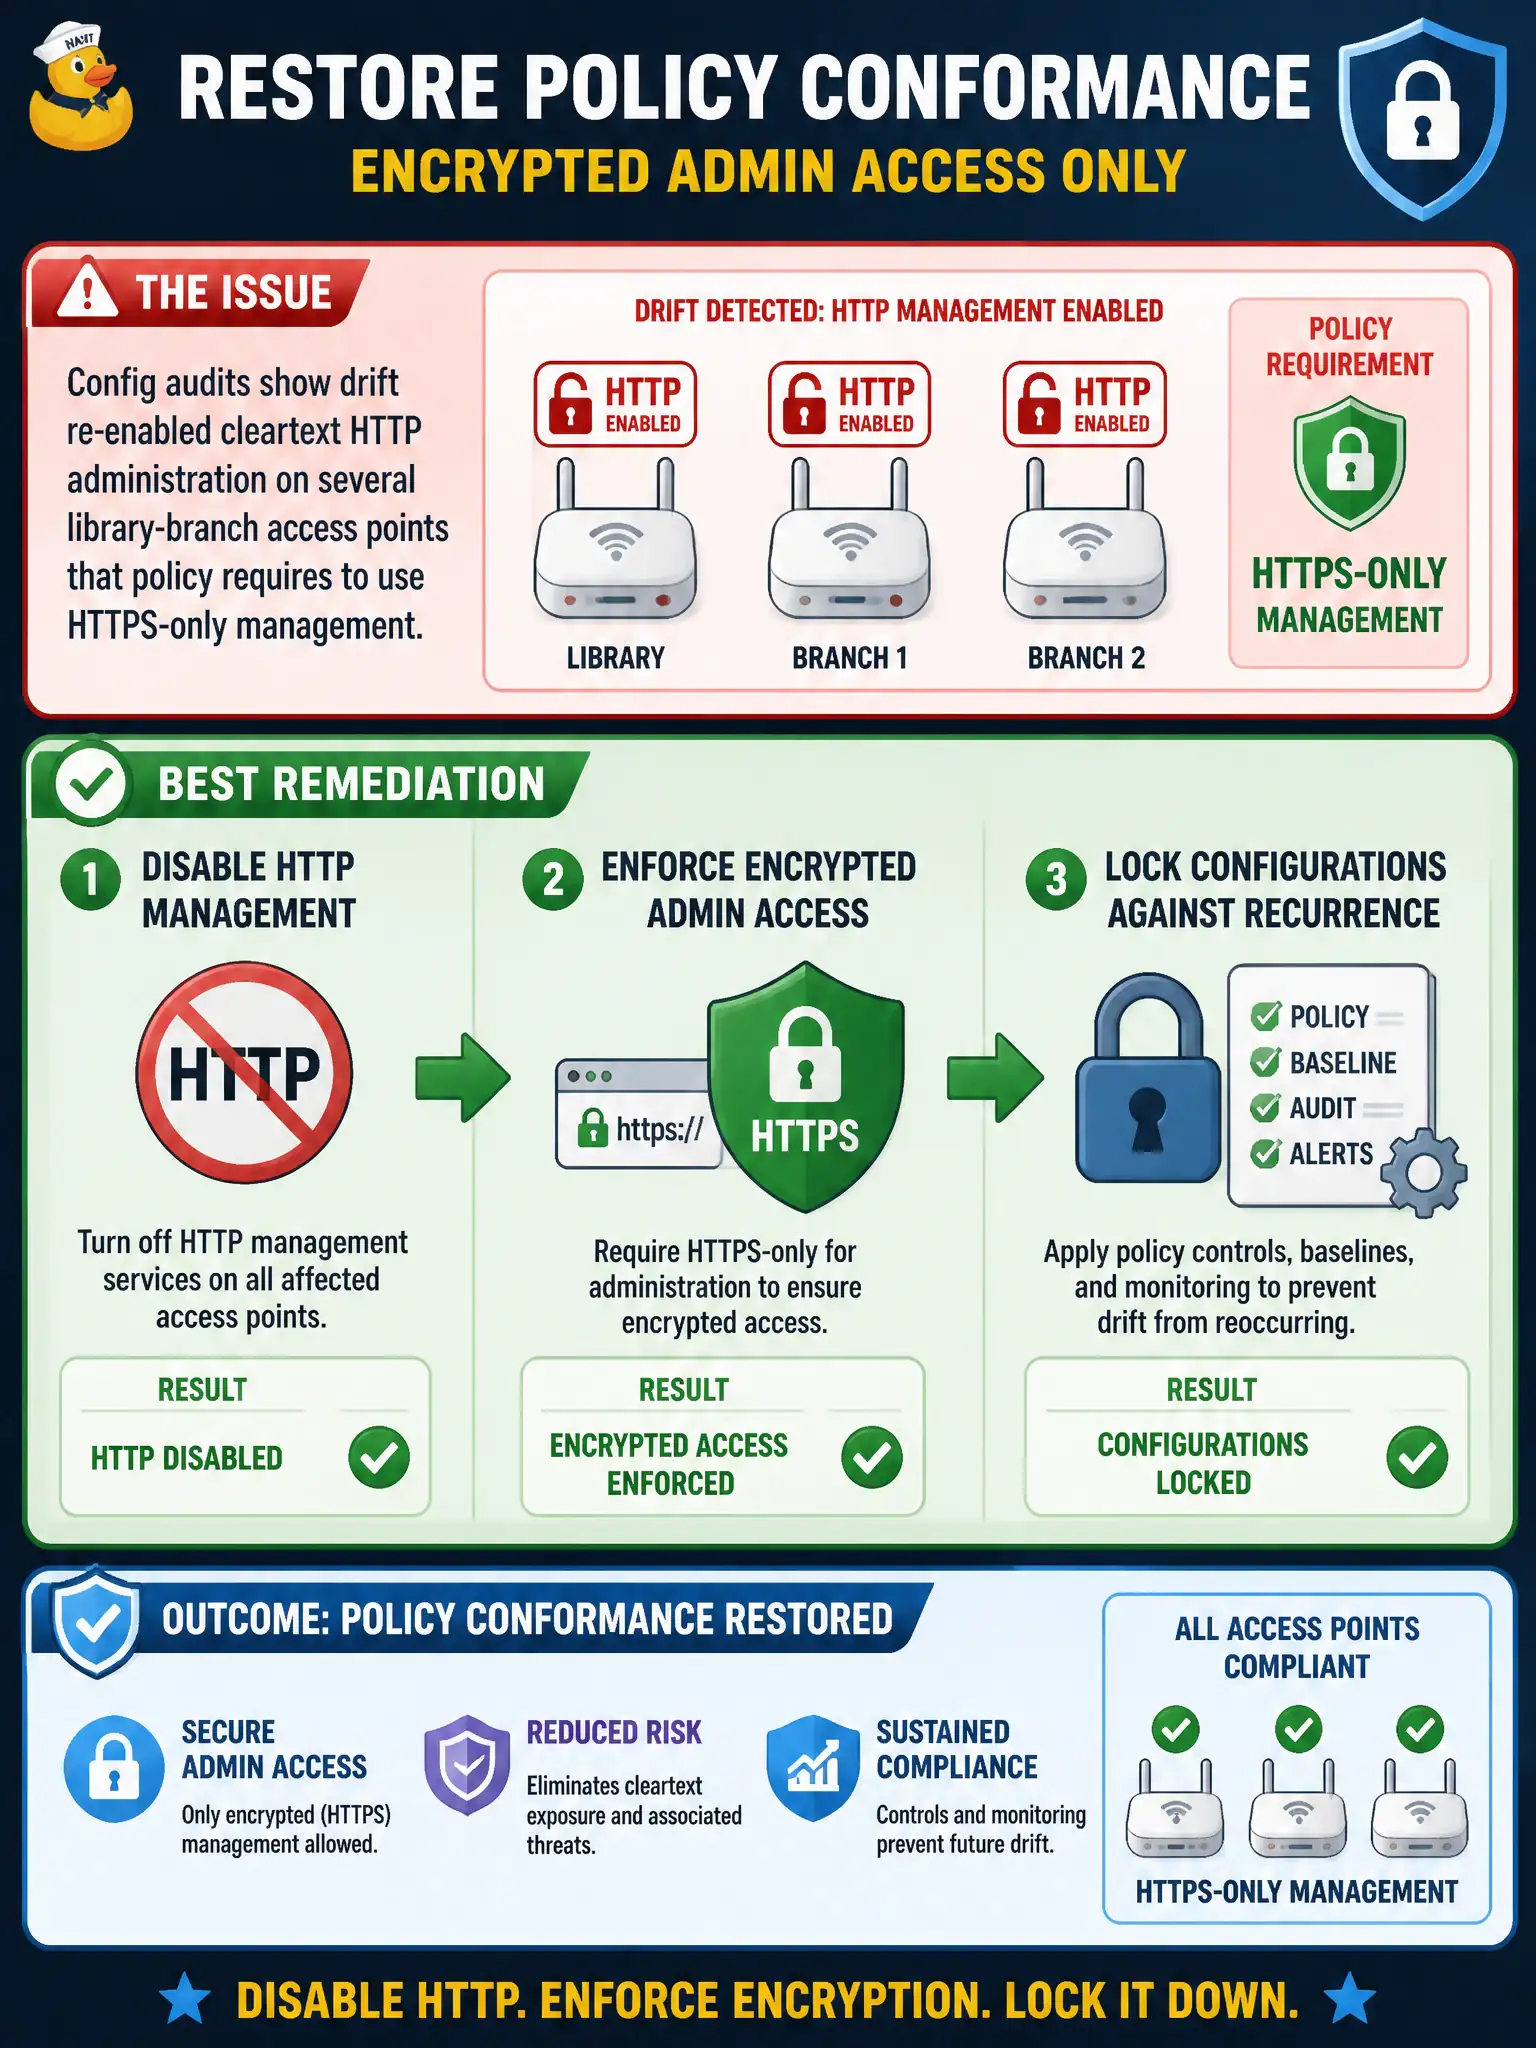
Policy said “use the locked front door,” and drift propped the side door open again. Turn HTTP admin off, force HTTPS (or equivalent secure management), and harden so the setting cannot quietly flip back. MAC filtering on users does not fix an open management path.
Full Explanation
Config audits showing drift that re-enabled cleartext HTTP administration on several library-branch access points—when policy requires HTTPS-only management—should be remediated by disabling HTTP management, enforcing encrypted admin access, and locking configurations against recurrence. Cleartext admin sessions expose credentials and management commands on branch networks that often share facilities with the public. Leaving HTTP enabled and relying on MAC filtering of client associations as the admin control confuses client association policy with management-plane protection and still leaves HTTP eavesdroppable. Publishing the HTTP admin URLs on the public library Wi-Fi page so staff can find them faster advertises the weak interface. Replacing RADIUS with a shared staff PSK so administration becomes simpler to monitor weakens authentication and does not encrypt management HTTP. Remediation must both fix the drift and prevent templates from reintroducing HTTP. Exam caveat: management-plane encryption (HTTPS/SSH) is distinct from client WLAN encryption; both are required by mature municipal policy. Operational check: disable HTTP on affected APs/controllers, enforce HTTPS/SSH, push a compliant template to all library branches, alert on configuration drift that re-enables HTTP, and retain audit screenshots showing remediation.