
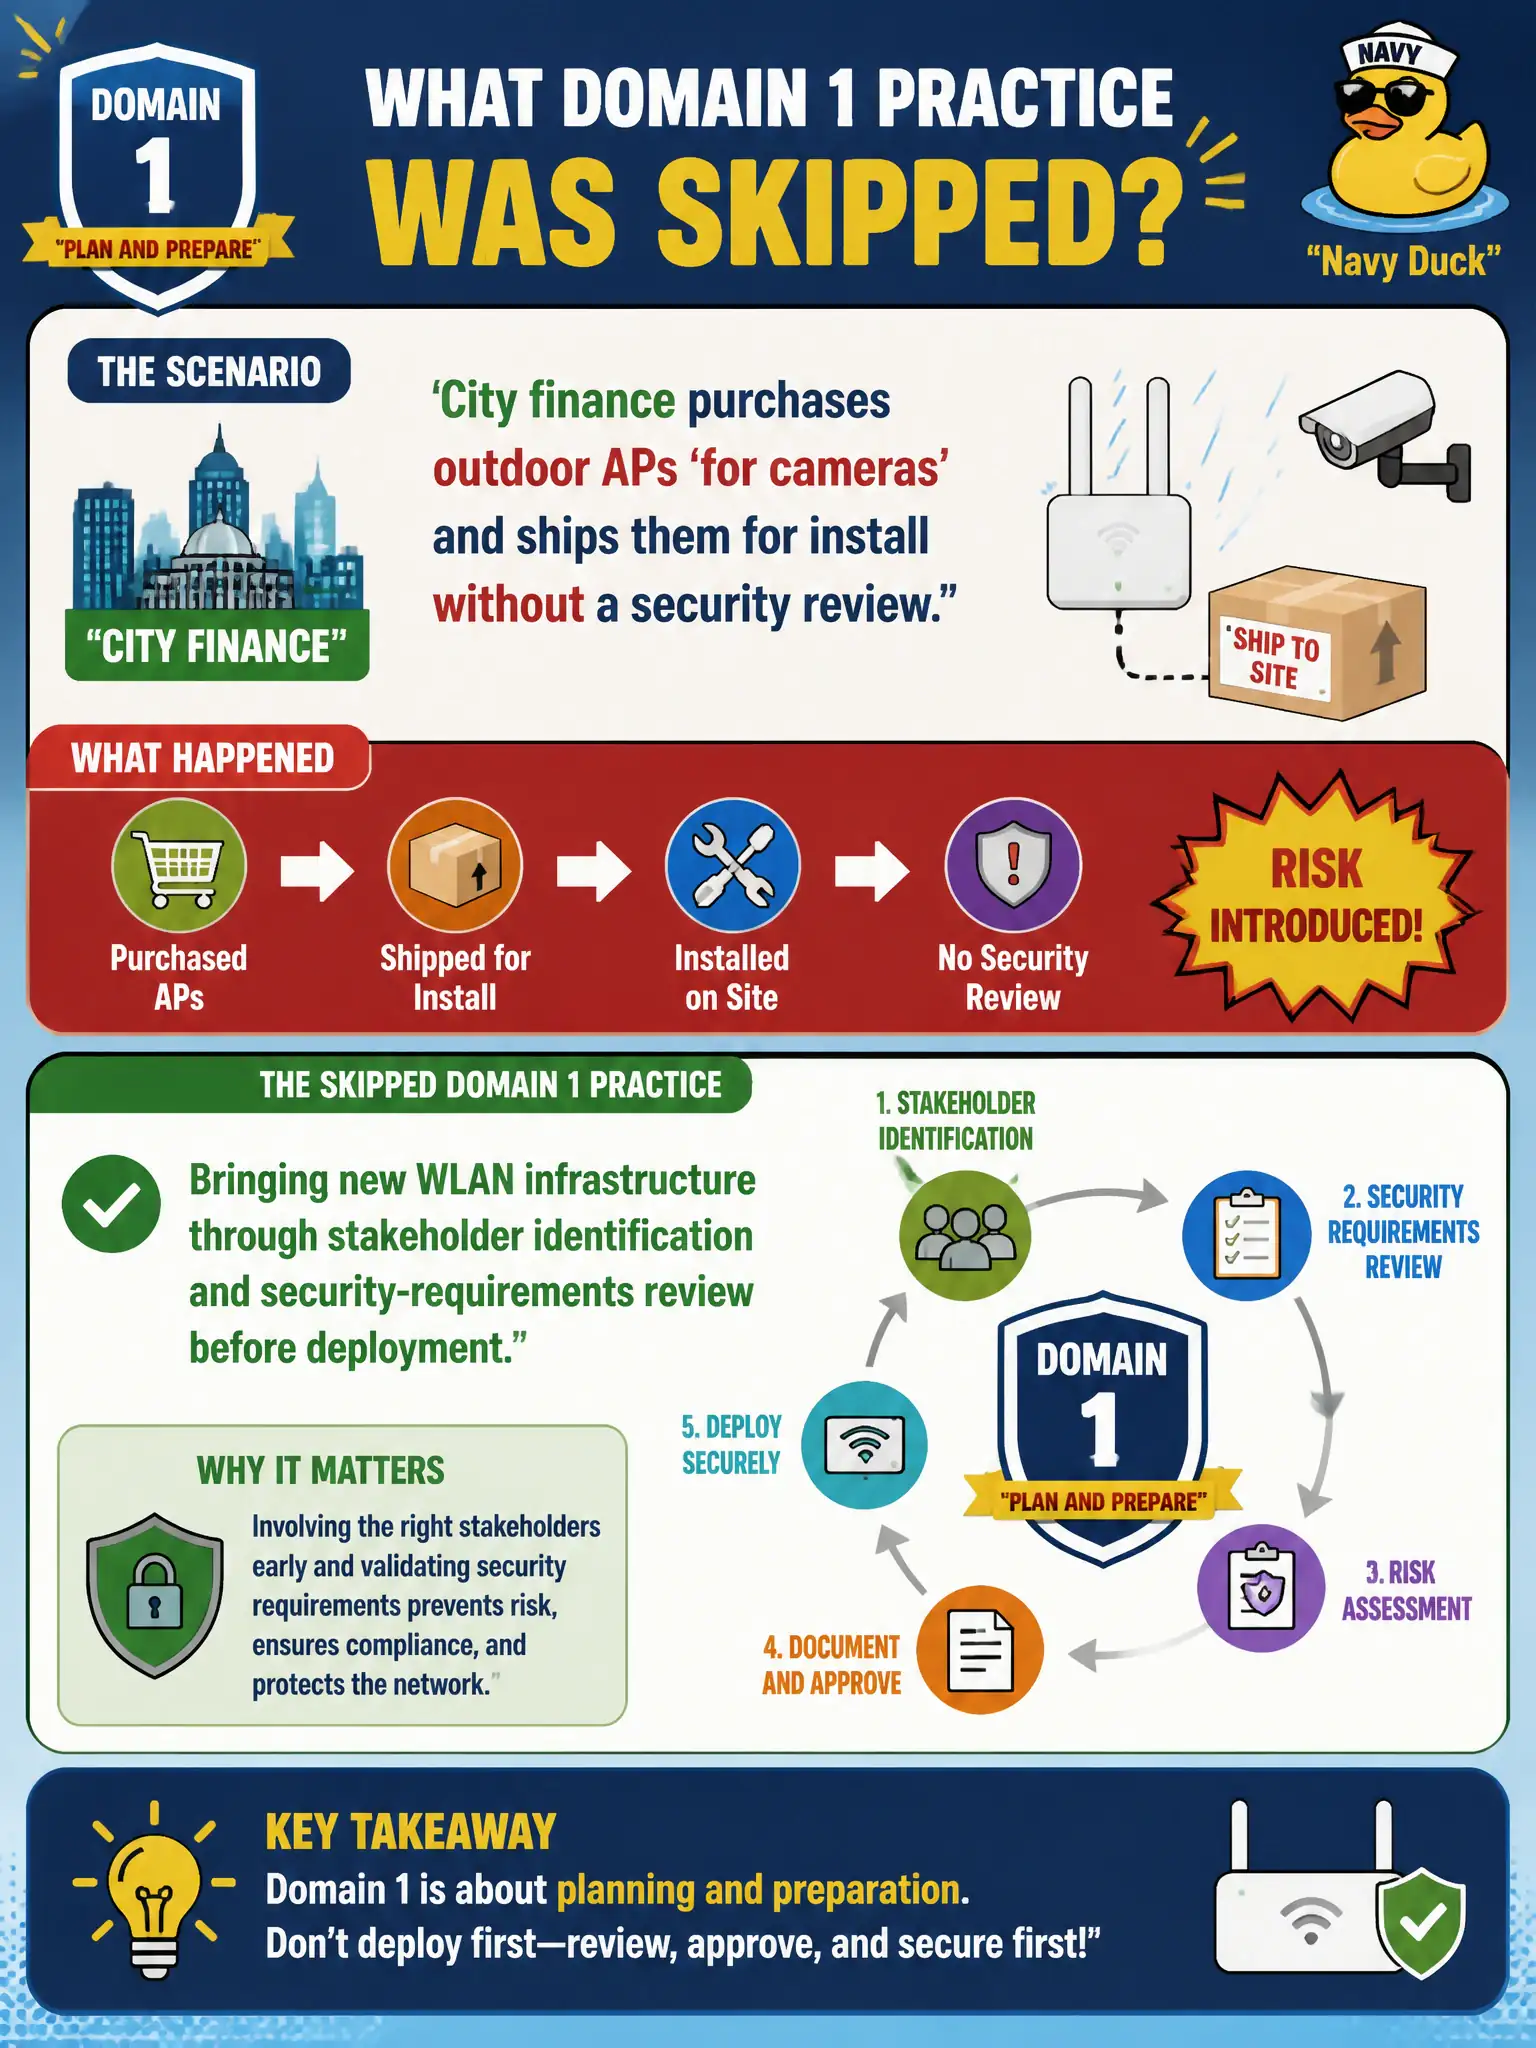
City finance purchases outdoor APs "for cameras" and ships them for install without a security review. What Domain 1 practice was skipped?
Select an answer to reveal the explanation.
Short Explanation
Finance buying APs like office chairs skips the security gate. New wireless infrastructure needs stakeholders and requirements review before it hits a pole.
Full Explanation
When city finance purchases outdoor APs "for cameras" and ships them for install without a security review, the Domain 1 practice skipped is bringing new WLAN infrastructure through stakeholder identification and security-requirements review before deployment. Unreviewed APs may use default credentials, outdated firmware, wrong VLAN trunks, or bridge camera traffic into staff networks. Choosing paint color for the enclosures only addresses aesthetics. Writing CWNA antenna math as the only gate evaluates coverage geometry, not authentication, management-plane security, or segmentation. Waiting until after a breach to inventory the devices inverts the control lifecycle and maximizes blast radius. Municipal procurement and facilities frequently introduce WLAN-class gear outside the wireless team's project list; requirements review must catch those purchases. Exam caveat: any AP-class or wireless bridge purchase is WLAN infrastructure for Domain 1 purposes, regardless of which department funded it. Operational check: add a purchase and install gate requiring WLAN security review for AP-class devices, inventory the outdoor units before go-live, validate management authentication, firmware level, logging, and segmentation against policy, and refuse activation until the review checklist is complete.