
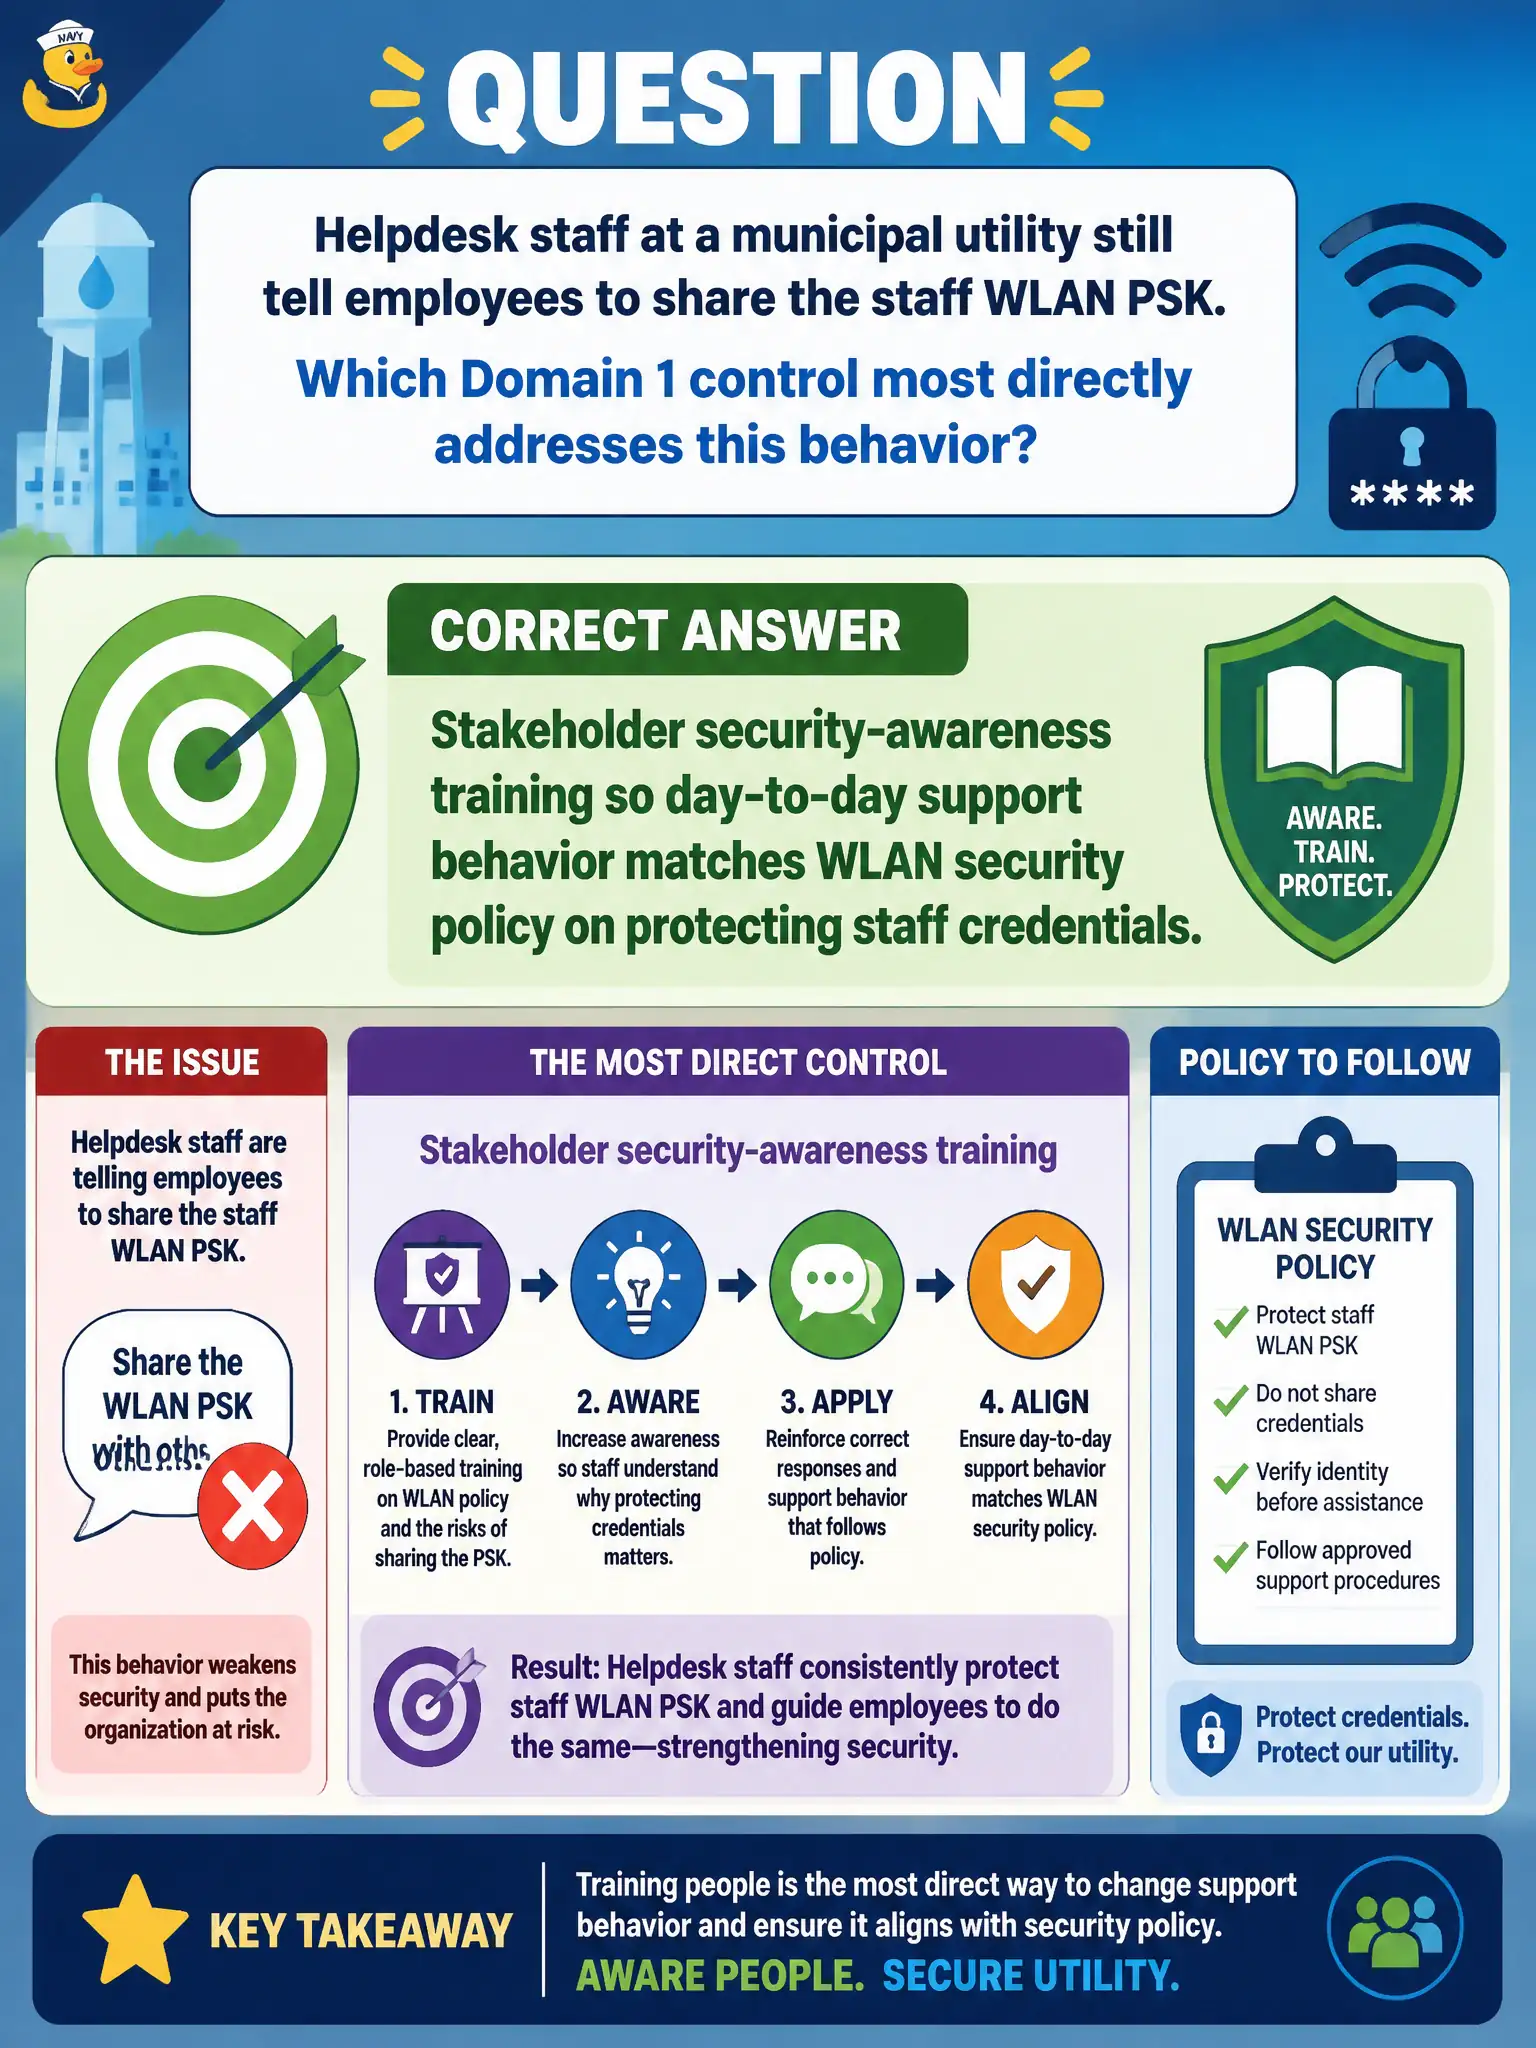
Helpdesk staff at a municipal utility still tell employees to share the staff WLAN PSK. Which Domain 1 control most directly addresses this behavior?
Select an answer to reveal the explanation.
Short Explanation
If helpdesk hands out the staff PSK like a Wi-Fi coupon, training—not louder radios—is the fix. People need to know policy forbids sharing that secret.
Full Explanation
When helpdesk staff at a municipal utility still tell employees to share the staff WLAN PSK, the Domain 1 control that most directly addresses the behavior is stakeholder security-awareness training so day-to-day support matches WLAN security policy on protecting staff credentials. Technical architecture cannot succeed if front-line support coaches users into the insecure practice the policy forbids. Buying more decorative AP covers does not change credential-handling advice. Increasing transmit power citywide is an RF change unrelated to PSK hygiene. Disabling all staff accounts as punishment without training creates outage and resentment without teaching the correct support behavior. Shared PSKs are already a weak pattern for staff networks; instructing employees to share them amplifies blast radius when a passphrase leaks. Awareness should also steer the organization toward Enterprise authentication where feasible. Exam caveat: awareness training complements technical controls; if Personal mode remains temporarily, combine training with rotation procedures, least-privilege distribution, and a migration plan to 802.1X. Operational check: update helpdesk scripts and knowledge-base articles to forbid PSK sharing, deliver short WLAN security awareness to support tiers, sample recent tickets for credential-handling advice, rotate any widely shared keys, and track reduction in insecure guidance.