
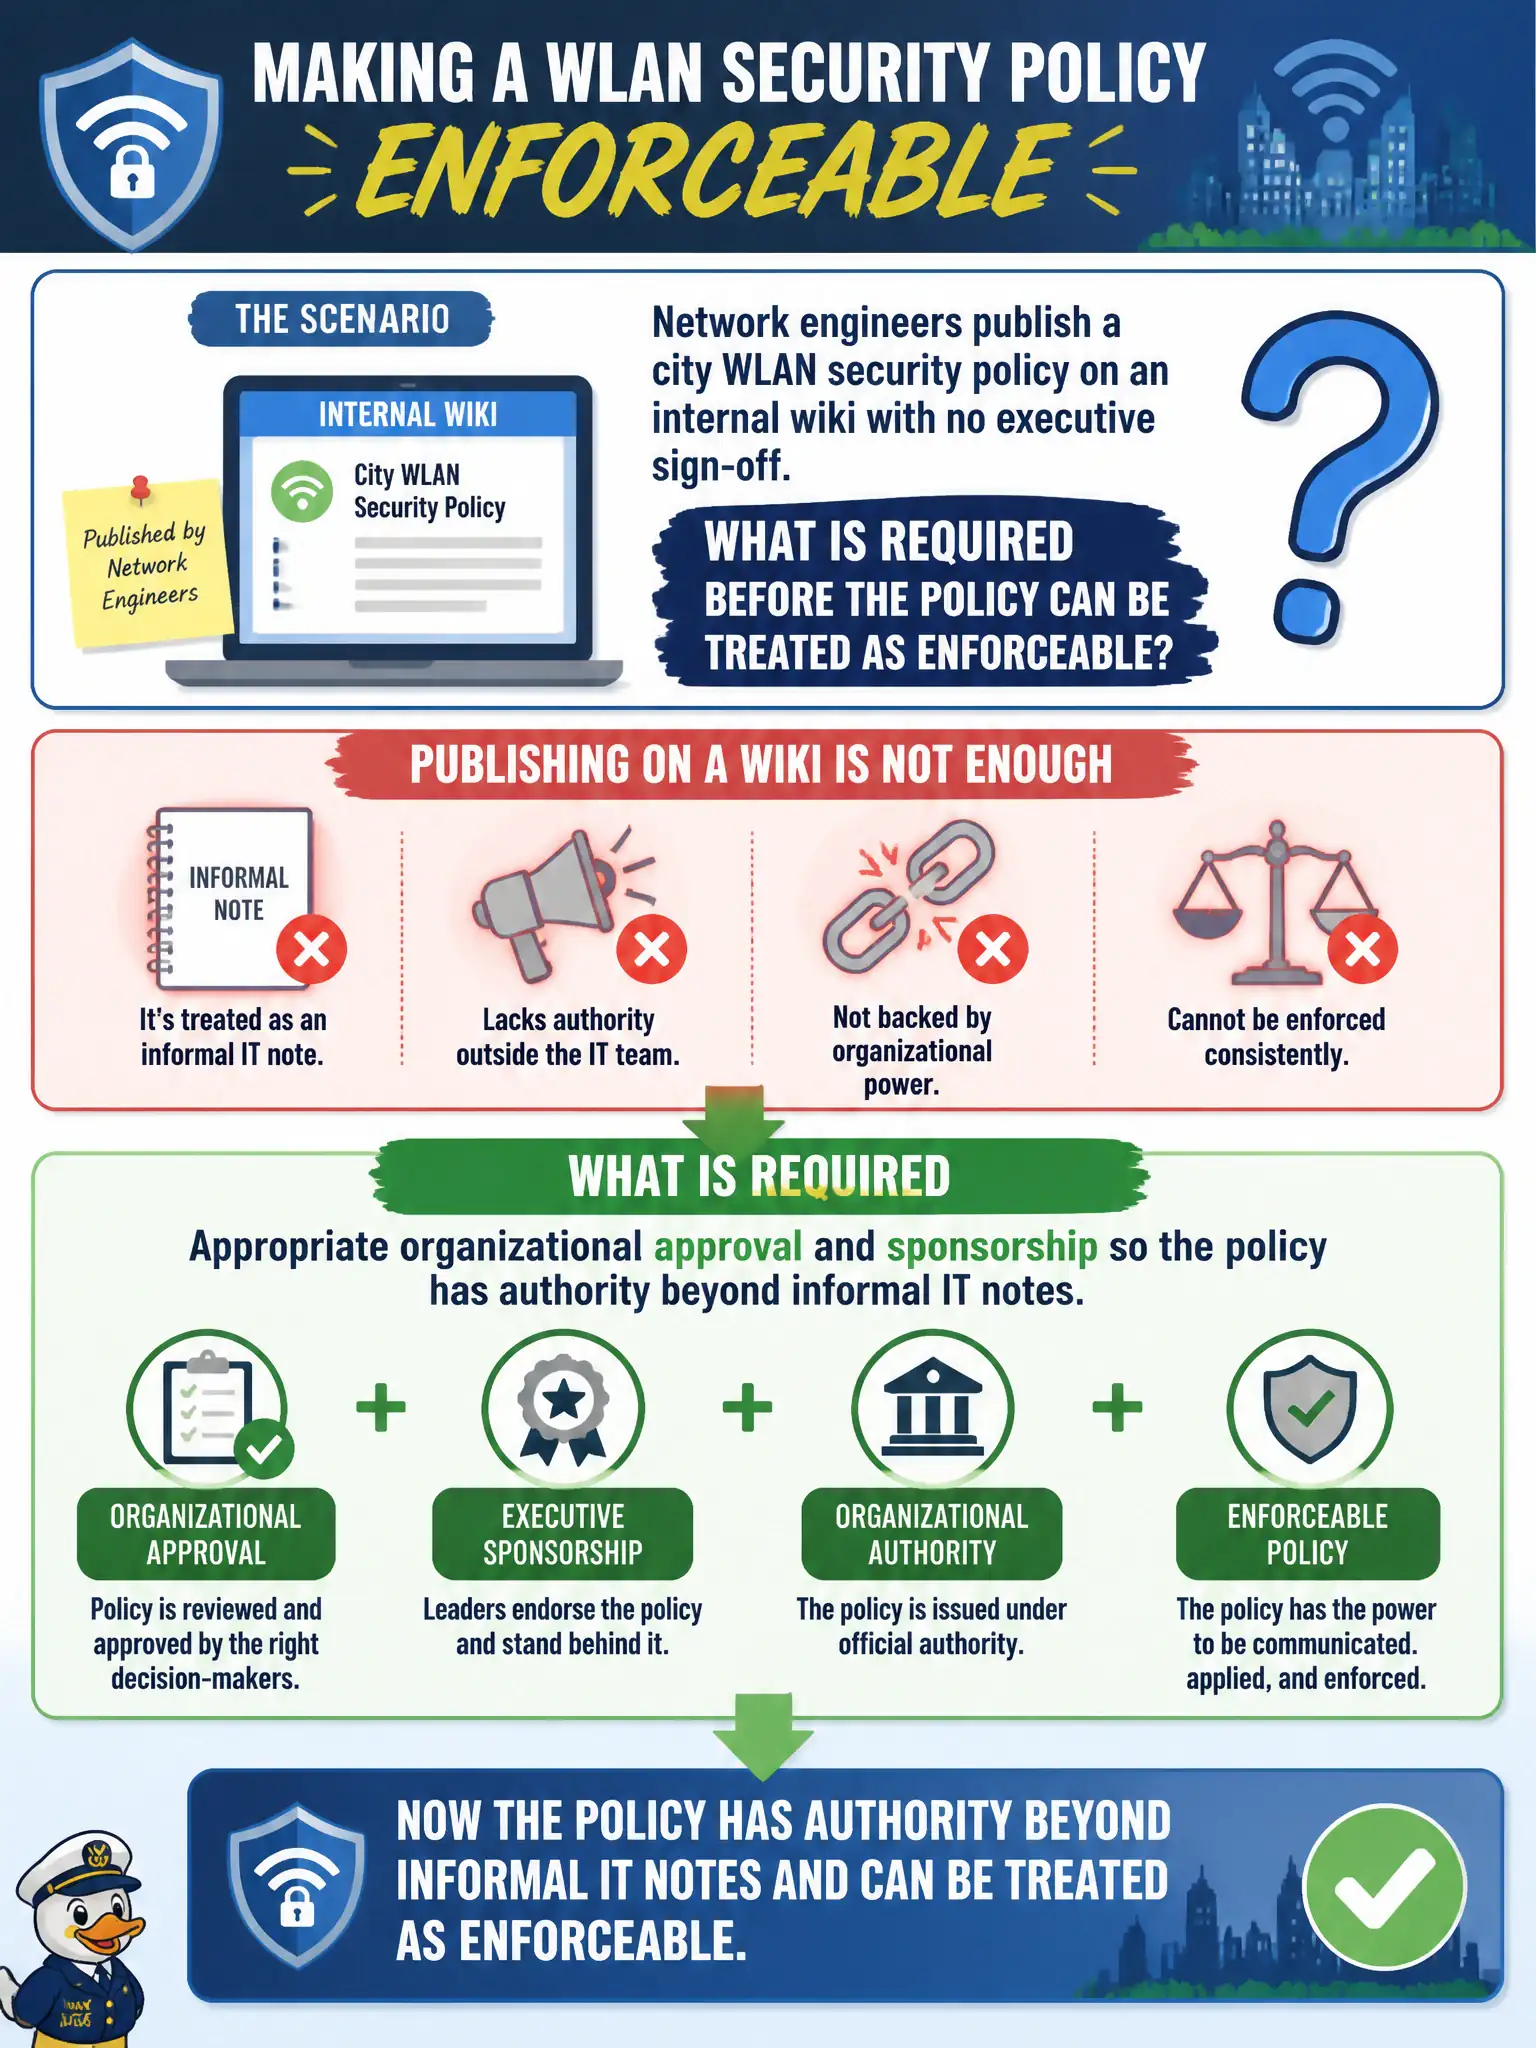
Network engineers publish a city WLAN security policy on an internal wiki with no executive sign-off. What is required before the policy can be treated as enforceable?
Select an answer to reveal the explanation.
Short Explanation
A wiki page without leadership ink is a suggestion, not policy. Get proper approval and sponsorship so helpdesk and auditors know it actually rules.
Full Explanation
When network engineers publish a city WLAN security policy on an internal wiki with no executive sign-off, the document remains informal guidance rather than an enforceable policy. Appropriate organizational approval and sponsorship are required so the policy has authority beyond IT notes and can bind helpdesk behavior, procurement, and operational exceptions. A humorous meme thread reacting to the draft creates awareness theater without approval. Anonymous edits from every employee overnight destroy integrity of the control set. Publishing the draft only on a personal blog places municipal security rules outside official custody and version control. Enforceable policy needs a defined approver, an effective date, a controlled publishing location, and a change process—none of which a casual wiki post provides. Exam caveat: the exact approver (CISO, CIO, city manager, council, or board) depends on charter, but sponsorship above the drafting engineers is required for enforceability. Operational check: route the draft through the city's formal policy approval workflow, capture signatures or recorded decisions, publish the approved version in the official policy repository with versioning, communicate effective dates to operations and helpdesk, and retire the informal wiki copy or mark it as non-authoritative.