
Contractors on the civic WLAN must land in a restricted role and VLAN via AAA. How should that be enforced?
Select an answer to reveal the explanation.
Short Explanation
Do not trust contractors to pick the right SSID like it is a lunch menu. Let RADIUS hand back the role and VLAN so RBAC does the steering. Domain-admin Wi-Fi for vendors is how audits get exciting.
Full Explanation
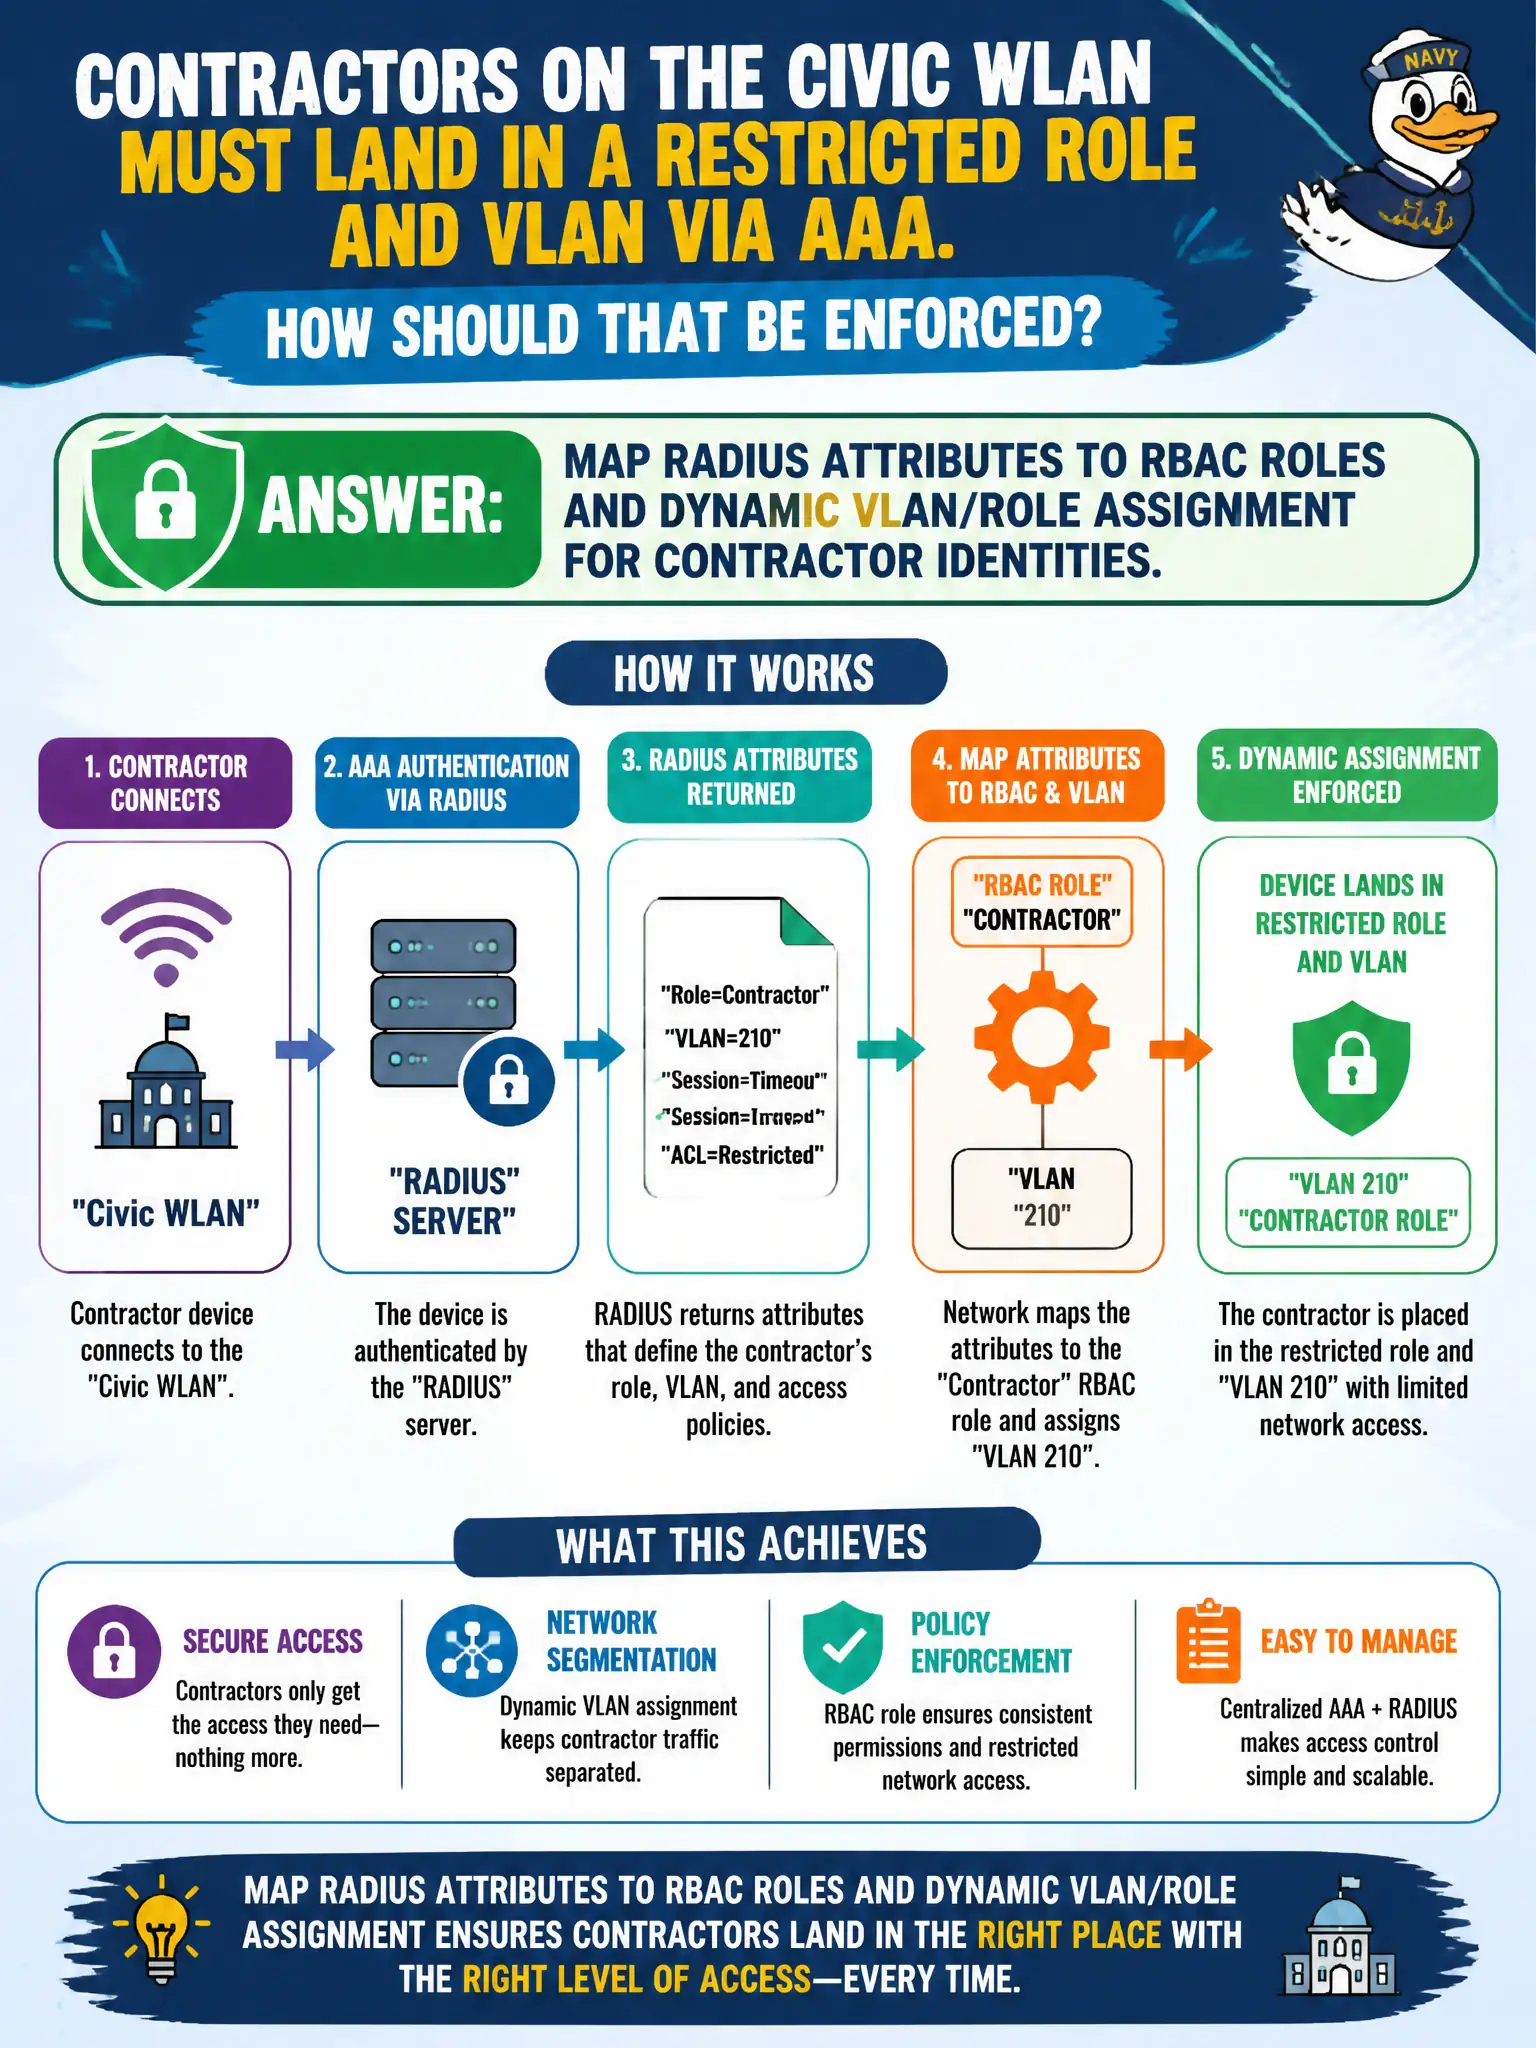
Contractors on the civic WLAN must land in a restricted role and VLAN via AAA, not via hopeful SSID self-selection. Mapping RADIUS attributes to RBAC roles and dynamic VLAN or role assignment for contractor identities enforces least privilege at join time and keeps accounting tied to who connected. Cities that host vendors in council chambers and project trailers need this machine-enforced separation.
Asking contractors to remember which SSID is safe and self-select correctly each morning fails under pressure and social engineering. Giving contractors domain-admin wireless profiles for troubleshooting convenience is privilege abuse. Disabling AAA accounting so contractor sessions leave no trail removes investigative capability.
Exam caveat: dynamic VLAN/role design must match switch/controller enforcement and DNS/DHCP services on the contractor segment. Operational check: authenticate a contractor test identity, confirm the assigned role/VLAN and blocked routes to sensitive subnets, and verify accounting logs show the session. In municipal WLAN programs, write the control into standards and verify it during change review so the next project inherits the same bar rather than rediscovering the failure mode under outage pressure.