
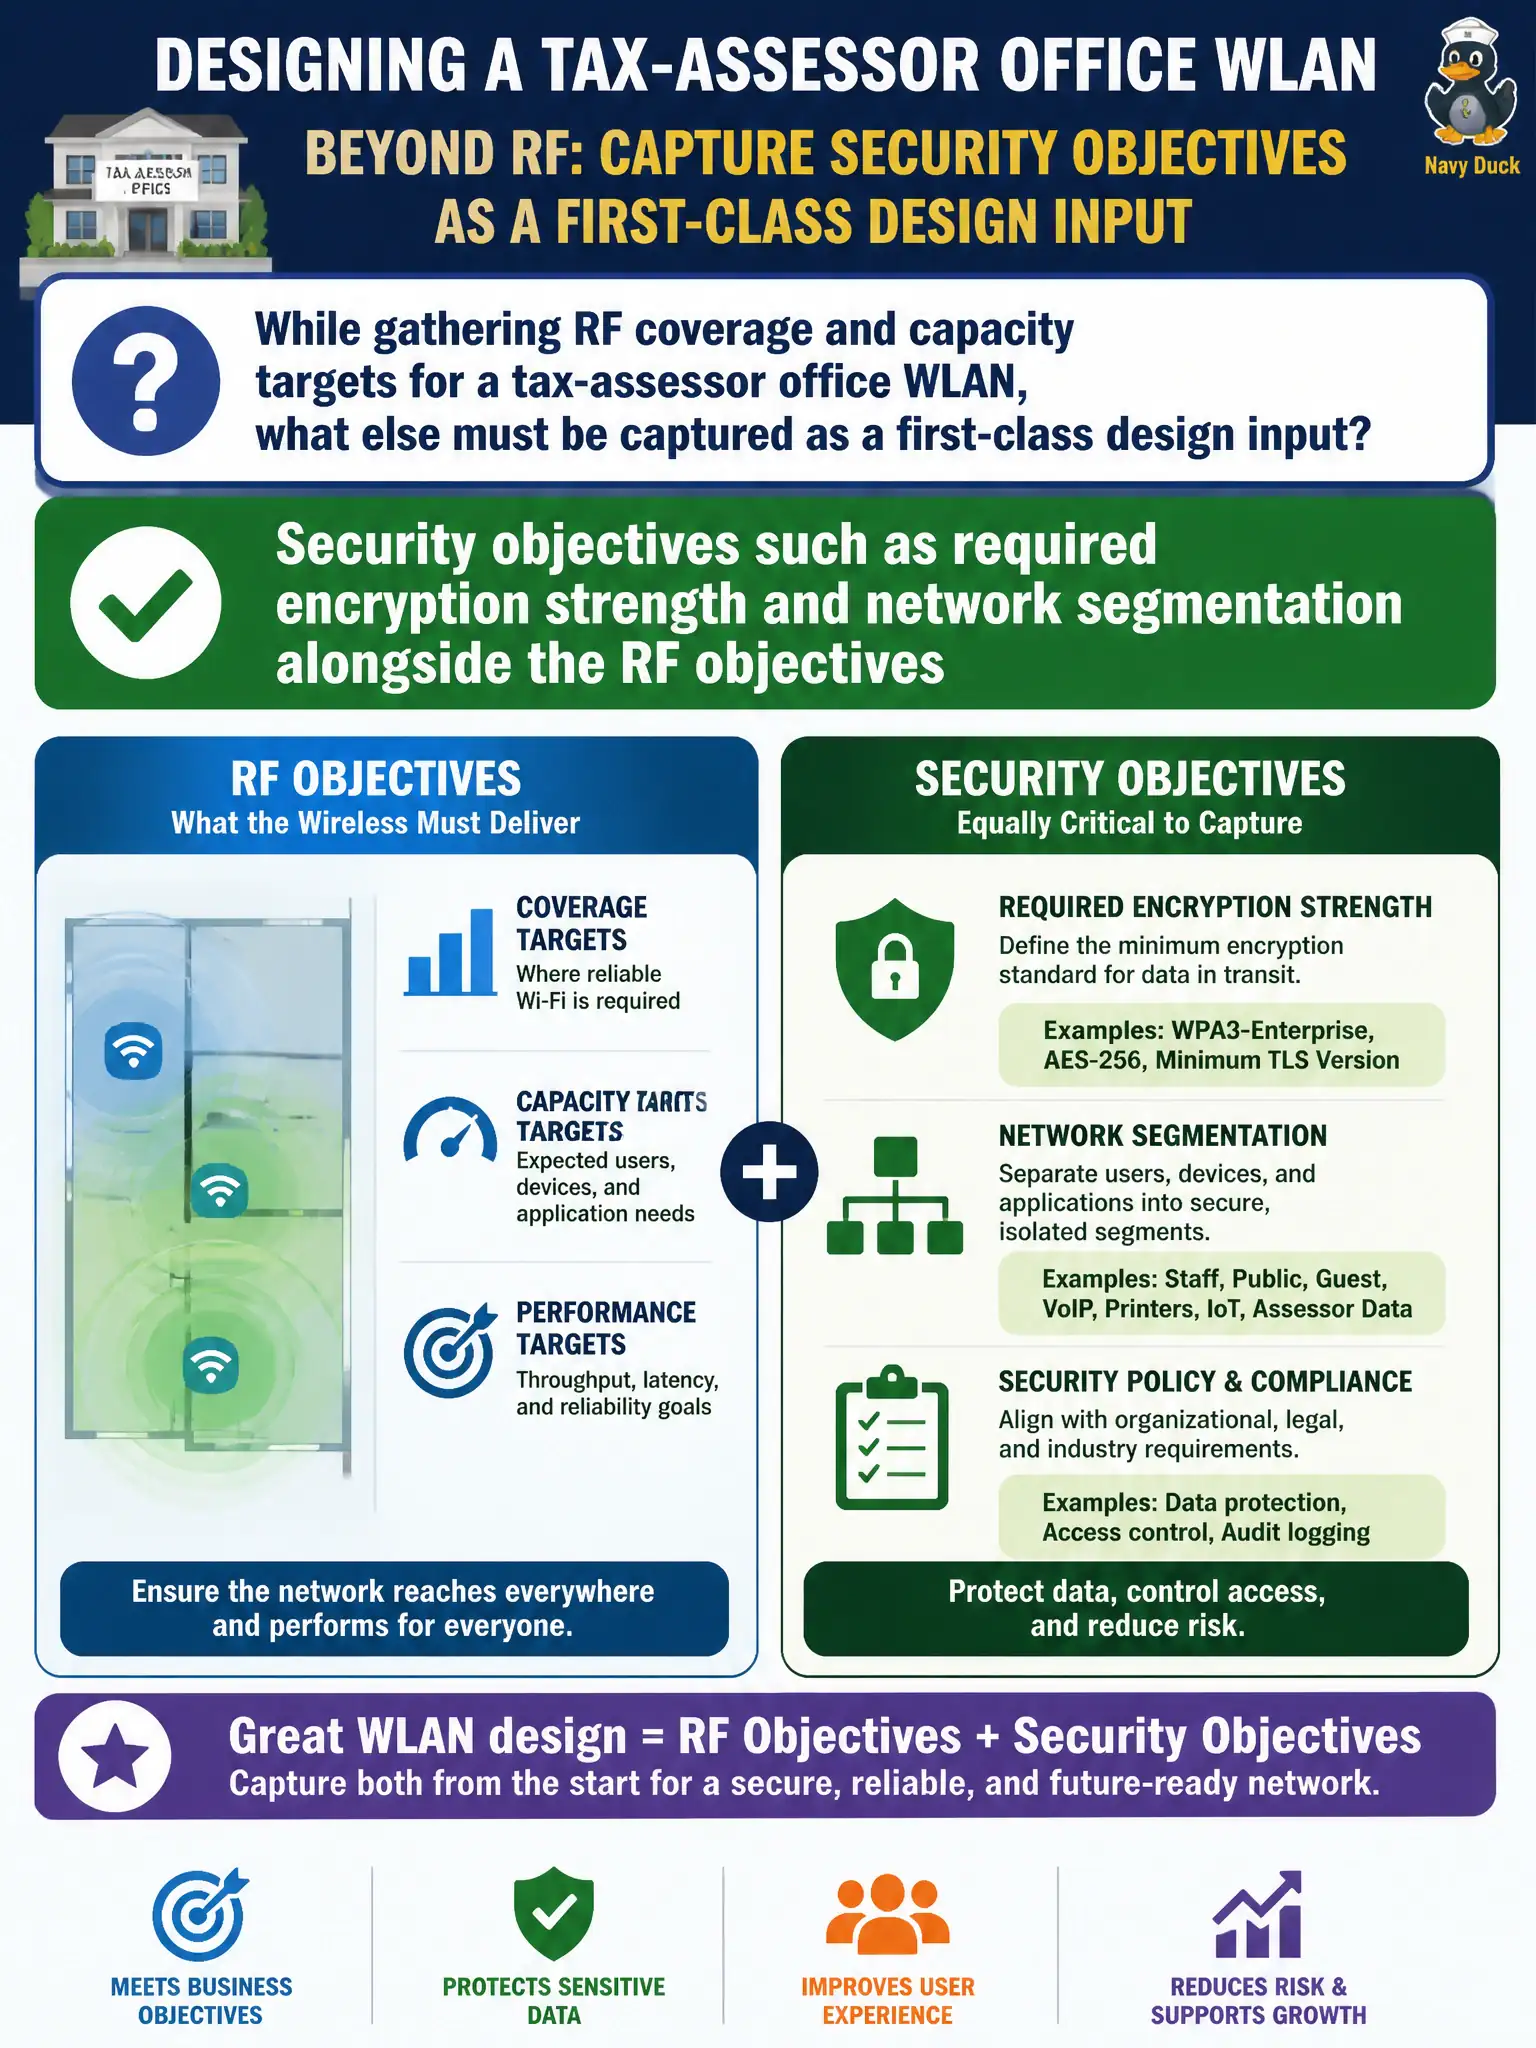
While gathering RF coverage and capacity targets for a tax-assessor office WLAN, what else must be captured as a first-class design input?
Select an answer to reveal the explanation.
Short Explanation
RF heatmaps without a security story are half a design. Write encryption and segmentation goals next to coverage and capacity so the architecture isn’t bolted on after install day. Pretty signal with a flat network is how assessor data wanders.
Full Explanation
RF coverage and capacity targets for a tax-assessor office are incomplete design inputs without parallel security objectives. Encryption strength, authentication method, and network segmentation must be captured as first-class requirements beside SNR and density so the WLAN does not become a soft path into assessor systems or tax data. Civic financial and property systems heighten the cost of treating security as a later ticket after APs are already mounted.
Capturing only decorative AP color choices while deferring encryption trivializes risk and teaches installers the wrong priority order. Promising WEP forever for legacy scanners locks in broken crypto. Bridging a guest open SSID directly into the assessor database VLAN collapses segmentation at the worst possible boundary for a public finance workflow.
Exam caveat: security objectives can drive SSID count, AAA design, and VLAN architecture—capture them before predictive AP placement freezes the wrong topology. Operational check: ensure the requirements document lists encryption/AKM, segmentation, and monitoring goals next to RF metrics, and verify the draft design’s SSID/VLAN map implements those controls before BoM approval.