
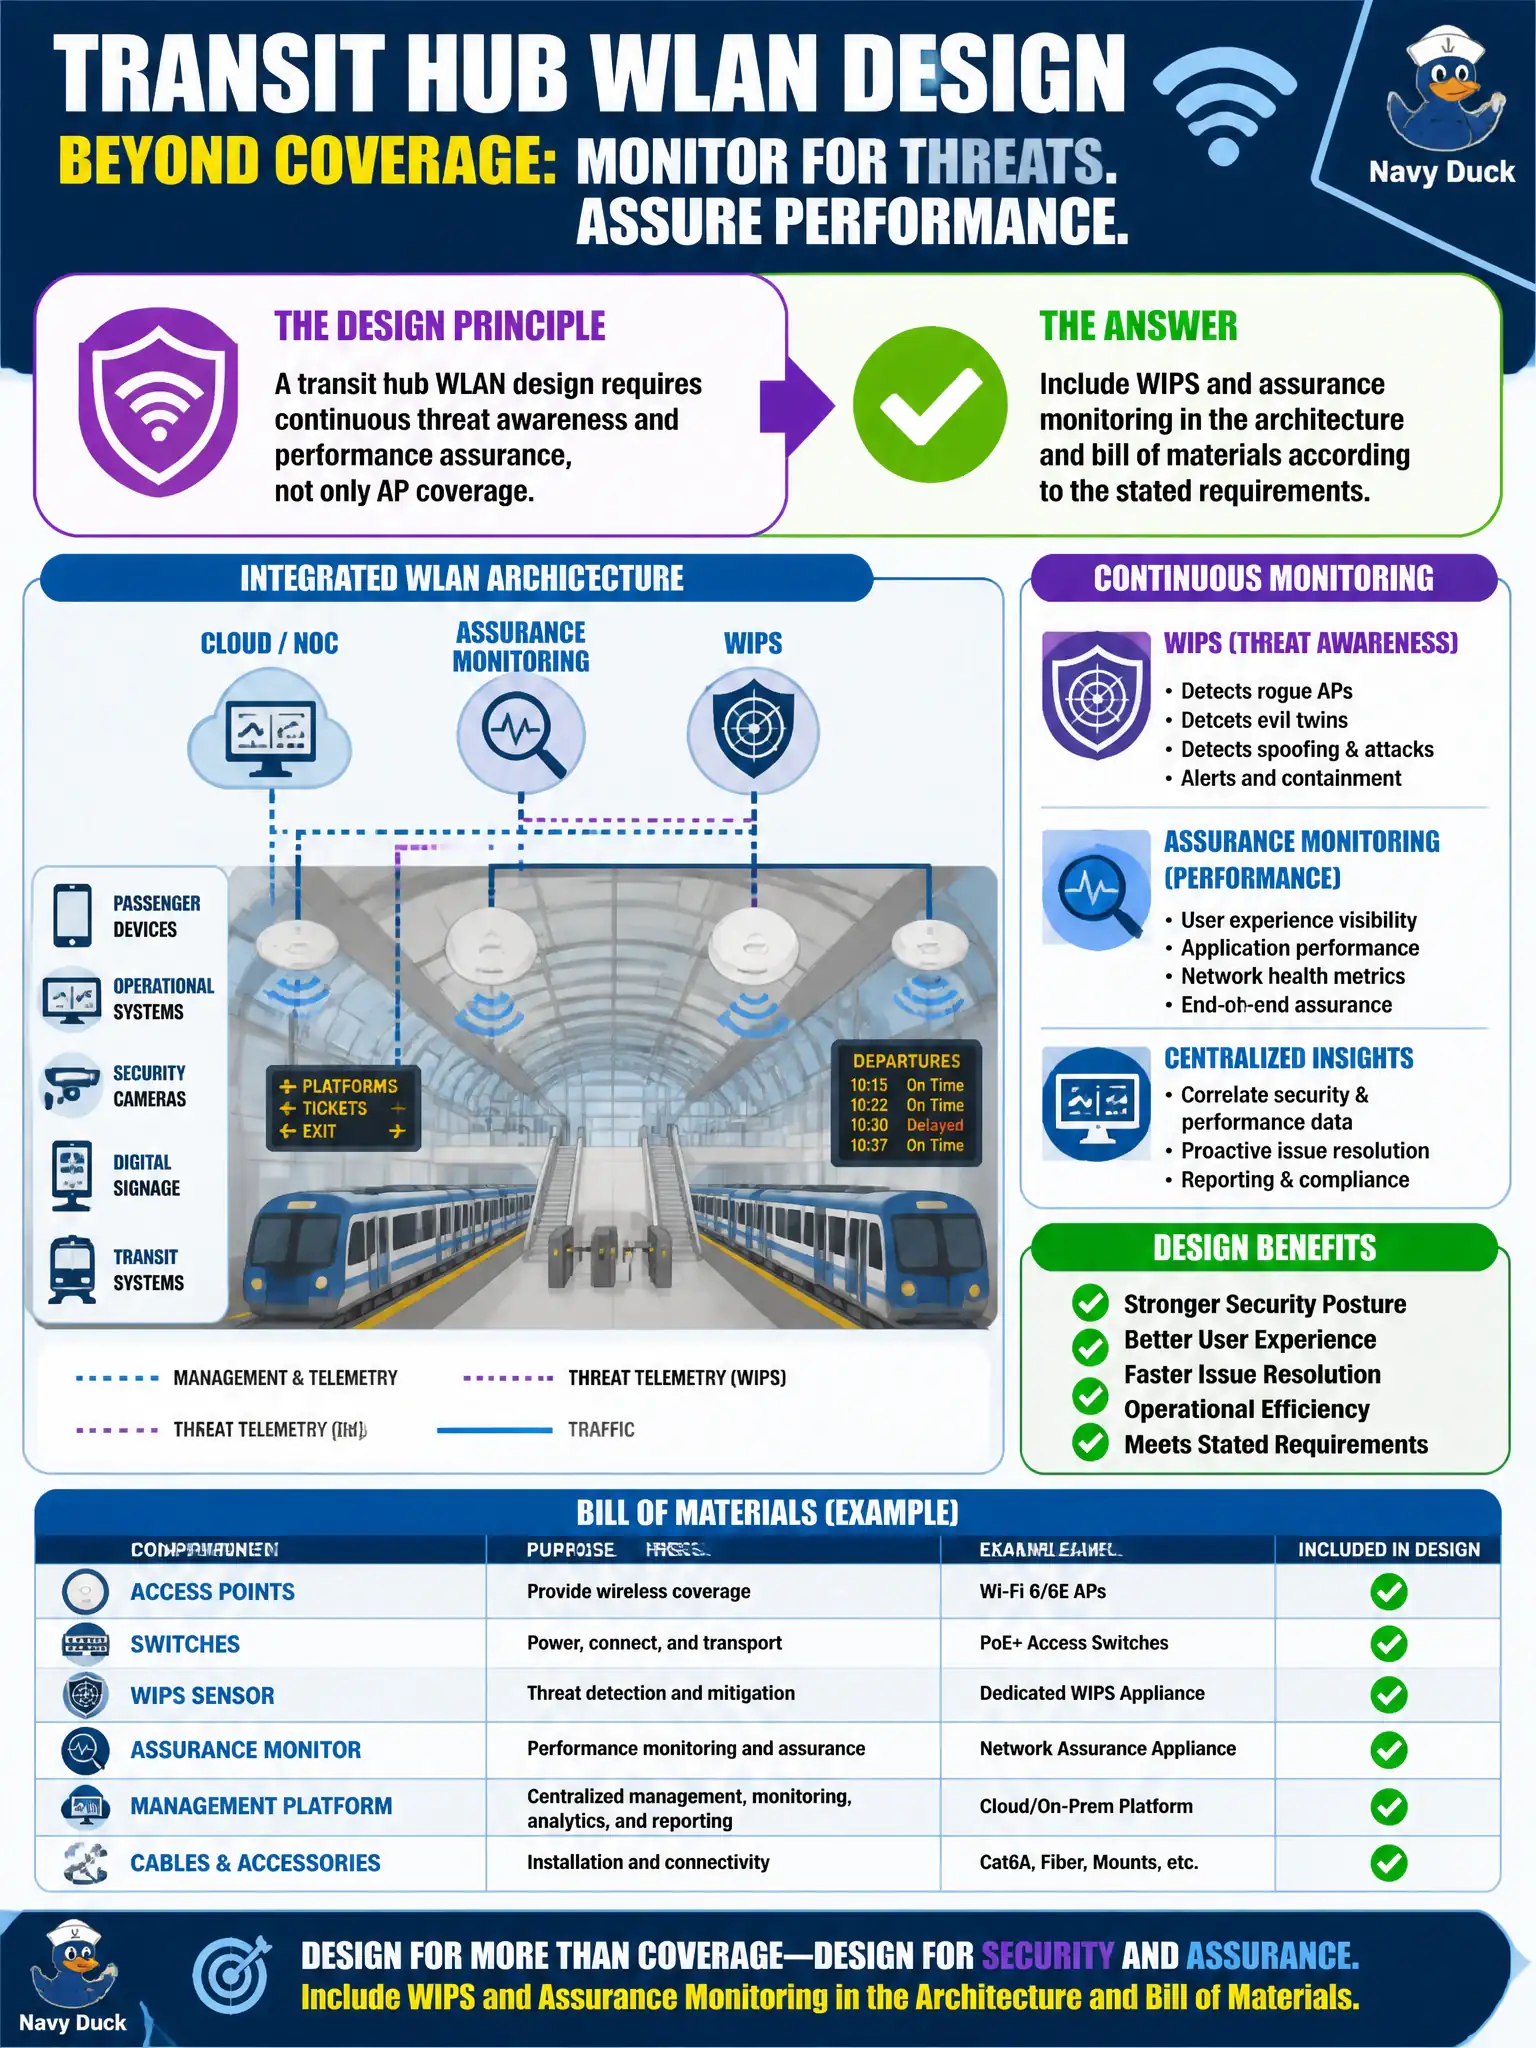
A transit hub WLAN design requires continuous threat awareness and performance assurance, not only AP coverage. How should monitoring be treated in the design package?
Select an answer to reveal the explanation.
Short Explanation
If the hub needs WIPS and assurance, put them in the architecture and on the BoM now. Heatmaps do not watch for rogue APs after opening day.
Full Explanation
Continuous threat awareness and performance assurance are architecture and BoM items, not optional post-breach add-ons. For a transit hub WLAN that requires those capabilities—not only AP coverage—the design package should include WIPS and assurance monitoring in the architecture and bill of materials according to the stated requirements. Coverage heatmaps do not detect evil twins or assure application performance for travelers and staff.
Omitting WIPS and assurance tools because coverage heatmaps already prove security fails by concept: heatmaps prove RF intent, not threat detection or ongoing assurance. Adding monitoring only after a breach fails by concept: reactive purchase leaves the hub blind during the incident window. Substituting consumer antivirus on kiosks for network WIPS and WLAN assurance fails by concept: endpoint AV does not replace over-the-air threat detection or WLAN performance assurance.
Exam caveat: CWNE designs that state monitoring requirements must carry them into architecture and BoM before procurement.
Operational check: List WIPS and assurance sensors or licenses in the transit-hub BoM, define alert integration to the NOC, and verify detection and assurance dashboards in acceptance testing.