
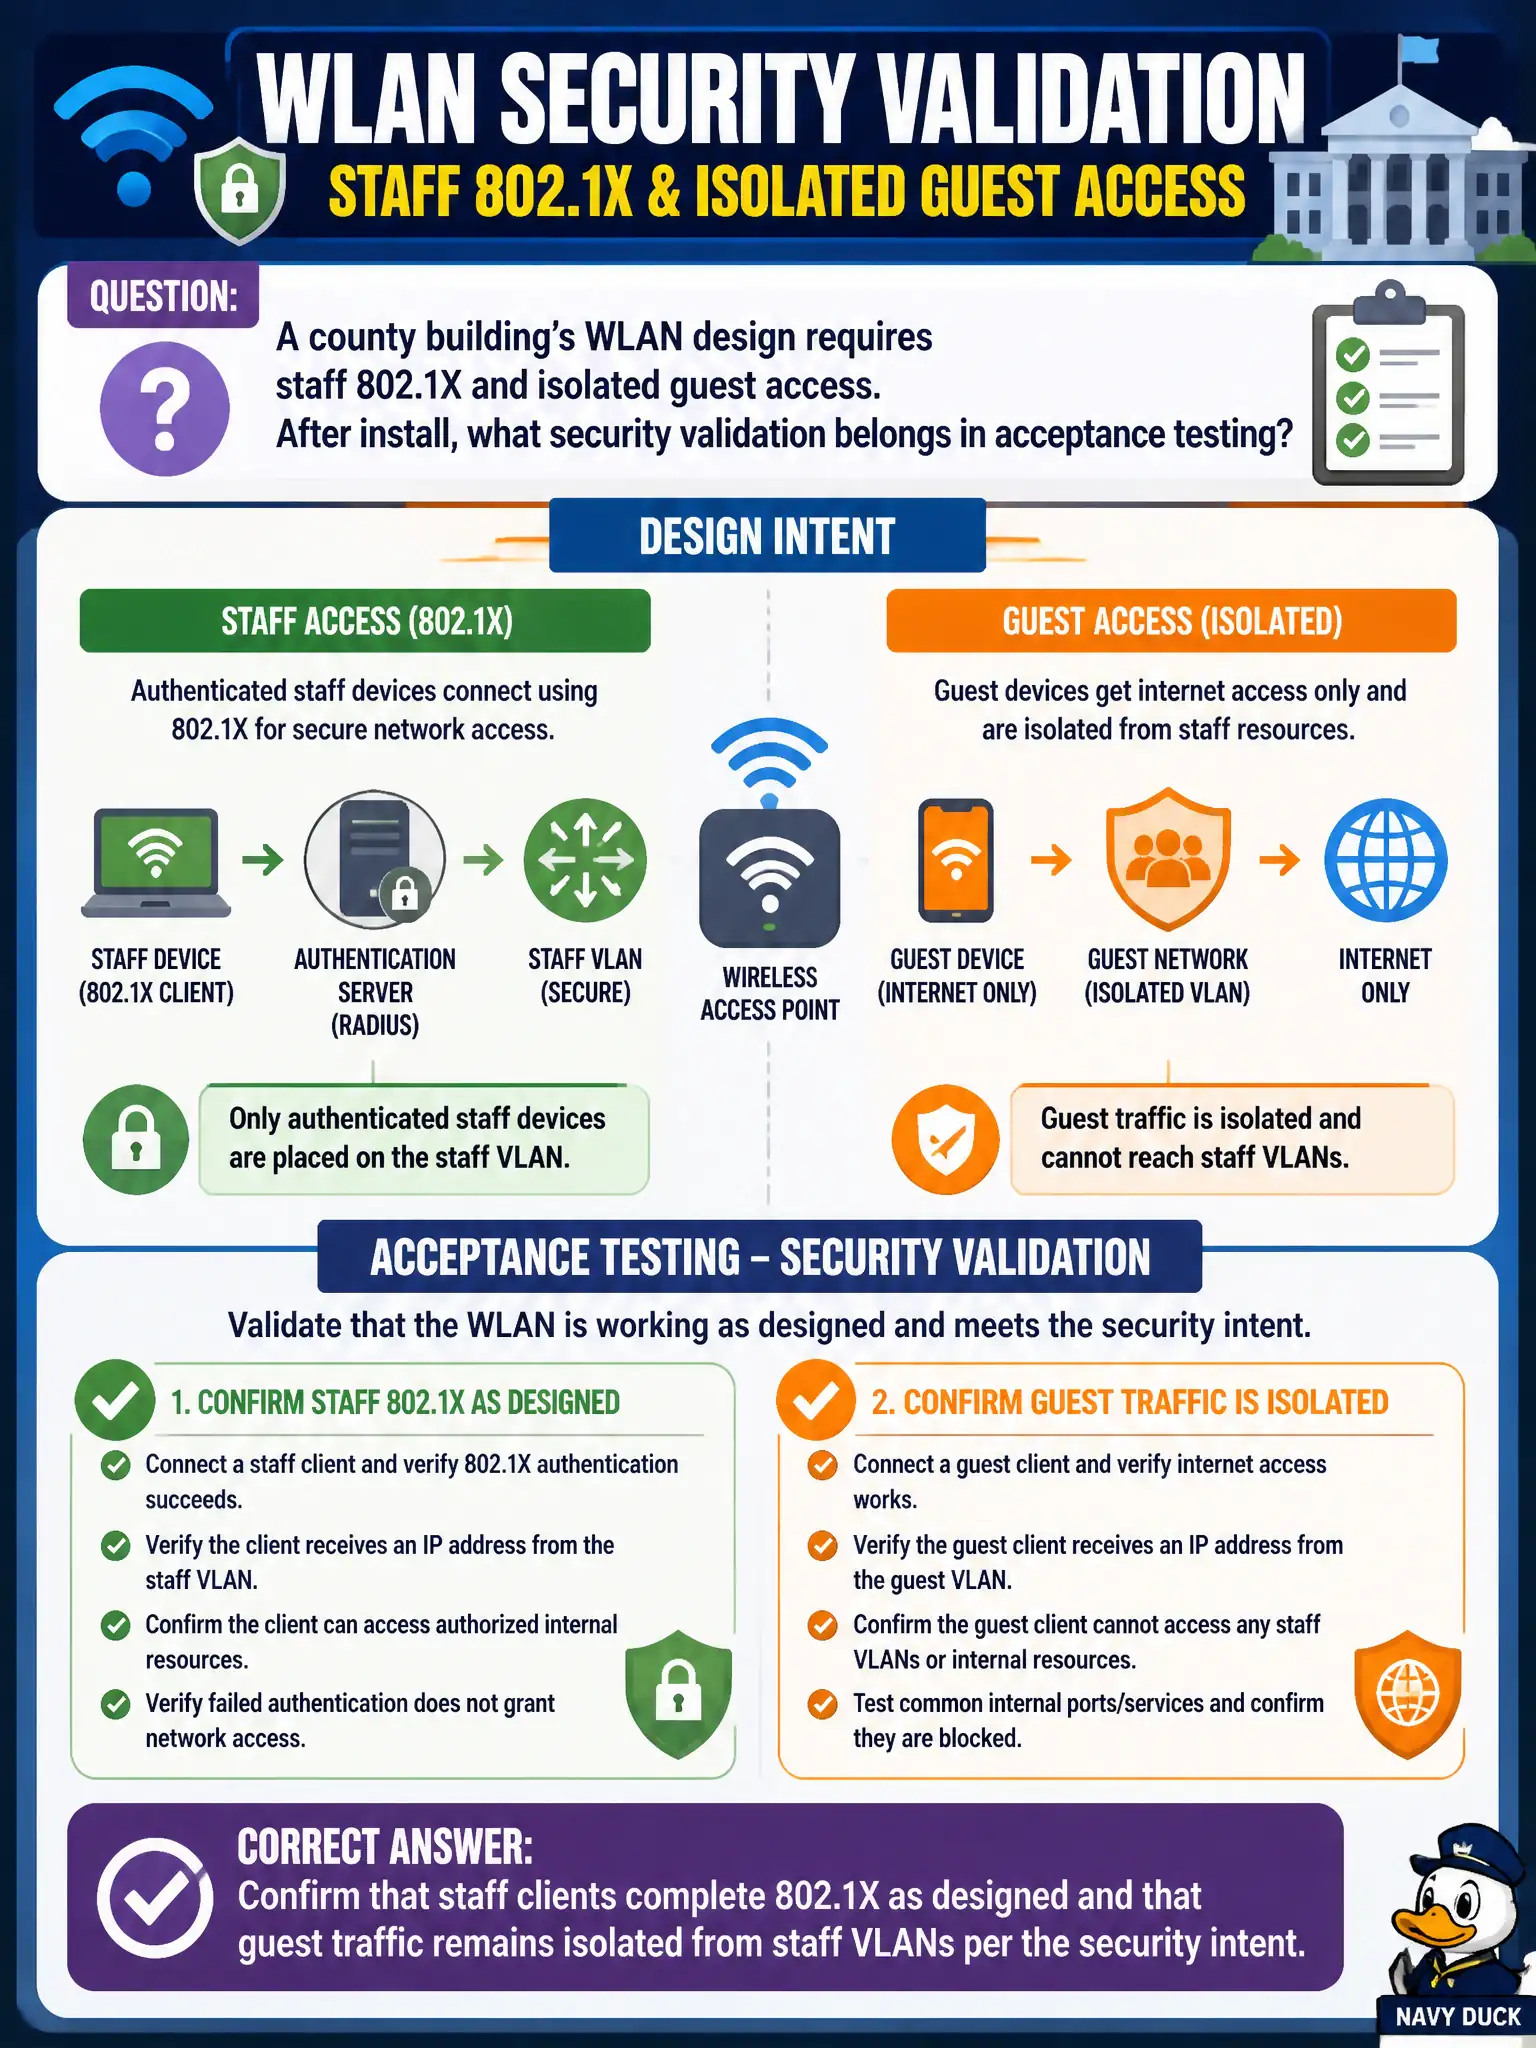
A county building's WLAN design requires staff 802.1X and isolated guest access. After install, what security validation belongs in acceptance testing?
Select an answer to reveal the explanation.
Short Explanation
Pretty heatmaps do not prove 802.1X or guest isolation. Acceptance has to show staff auth works and guests cannot wander into staff VLANs—security was part of the design, so test it.
Full Explanation
Security intent in the design must be proven at acceptance, not assumed from green RF maps. After install in a county building that requires staff 802.1X and isolated guest access, acceptance testing should confirm that staff clients complete 802.1X as designed and that guest traffic remains isolated from staff VLANs per the security intent. Internet reachability alone does not prove authentication success or segmentation integrity between communities.
Only confirming that guest and staff SSIDs both reach the Internet without checking authentication or isolation fails by concept: connectivity can succeed while 802.1X is bypassed or VLANs are bridged. Skipping security tests if the RF heatmap is green fails by concept: RF quality does not validate AAA or isolation. Replacing 802.1X with an open staff SSID temporarily to simplify testing fails by concept: that abandons the security requirement under test.
Exam caveat: CWNE acceptance includes security join and isolation tests alongside RF validation for municipal staff and guest designs.
Operational check: Join a staff client with 802.1X and capture success, join guest and attempt staff-VLAN reachability, document isolation results, and fail acceptance until both match the security design.