
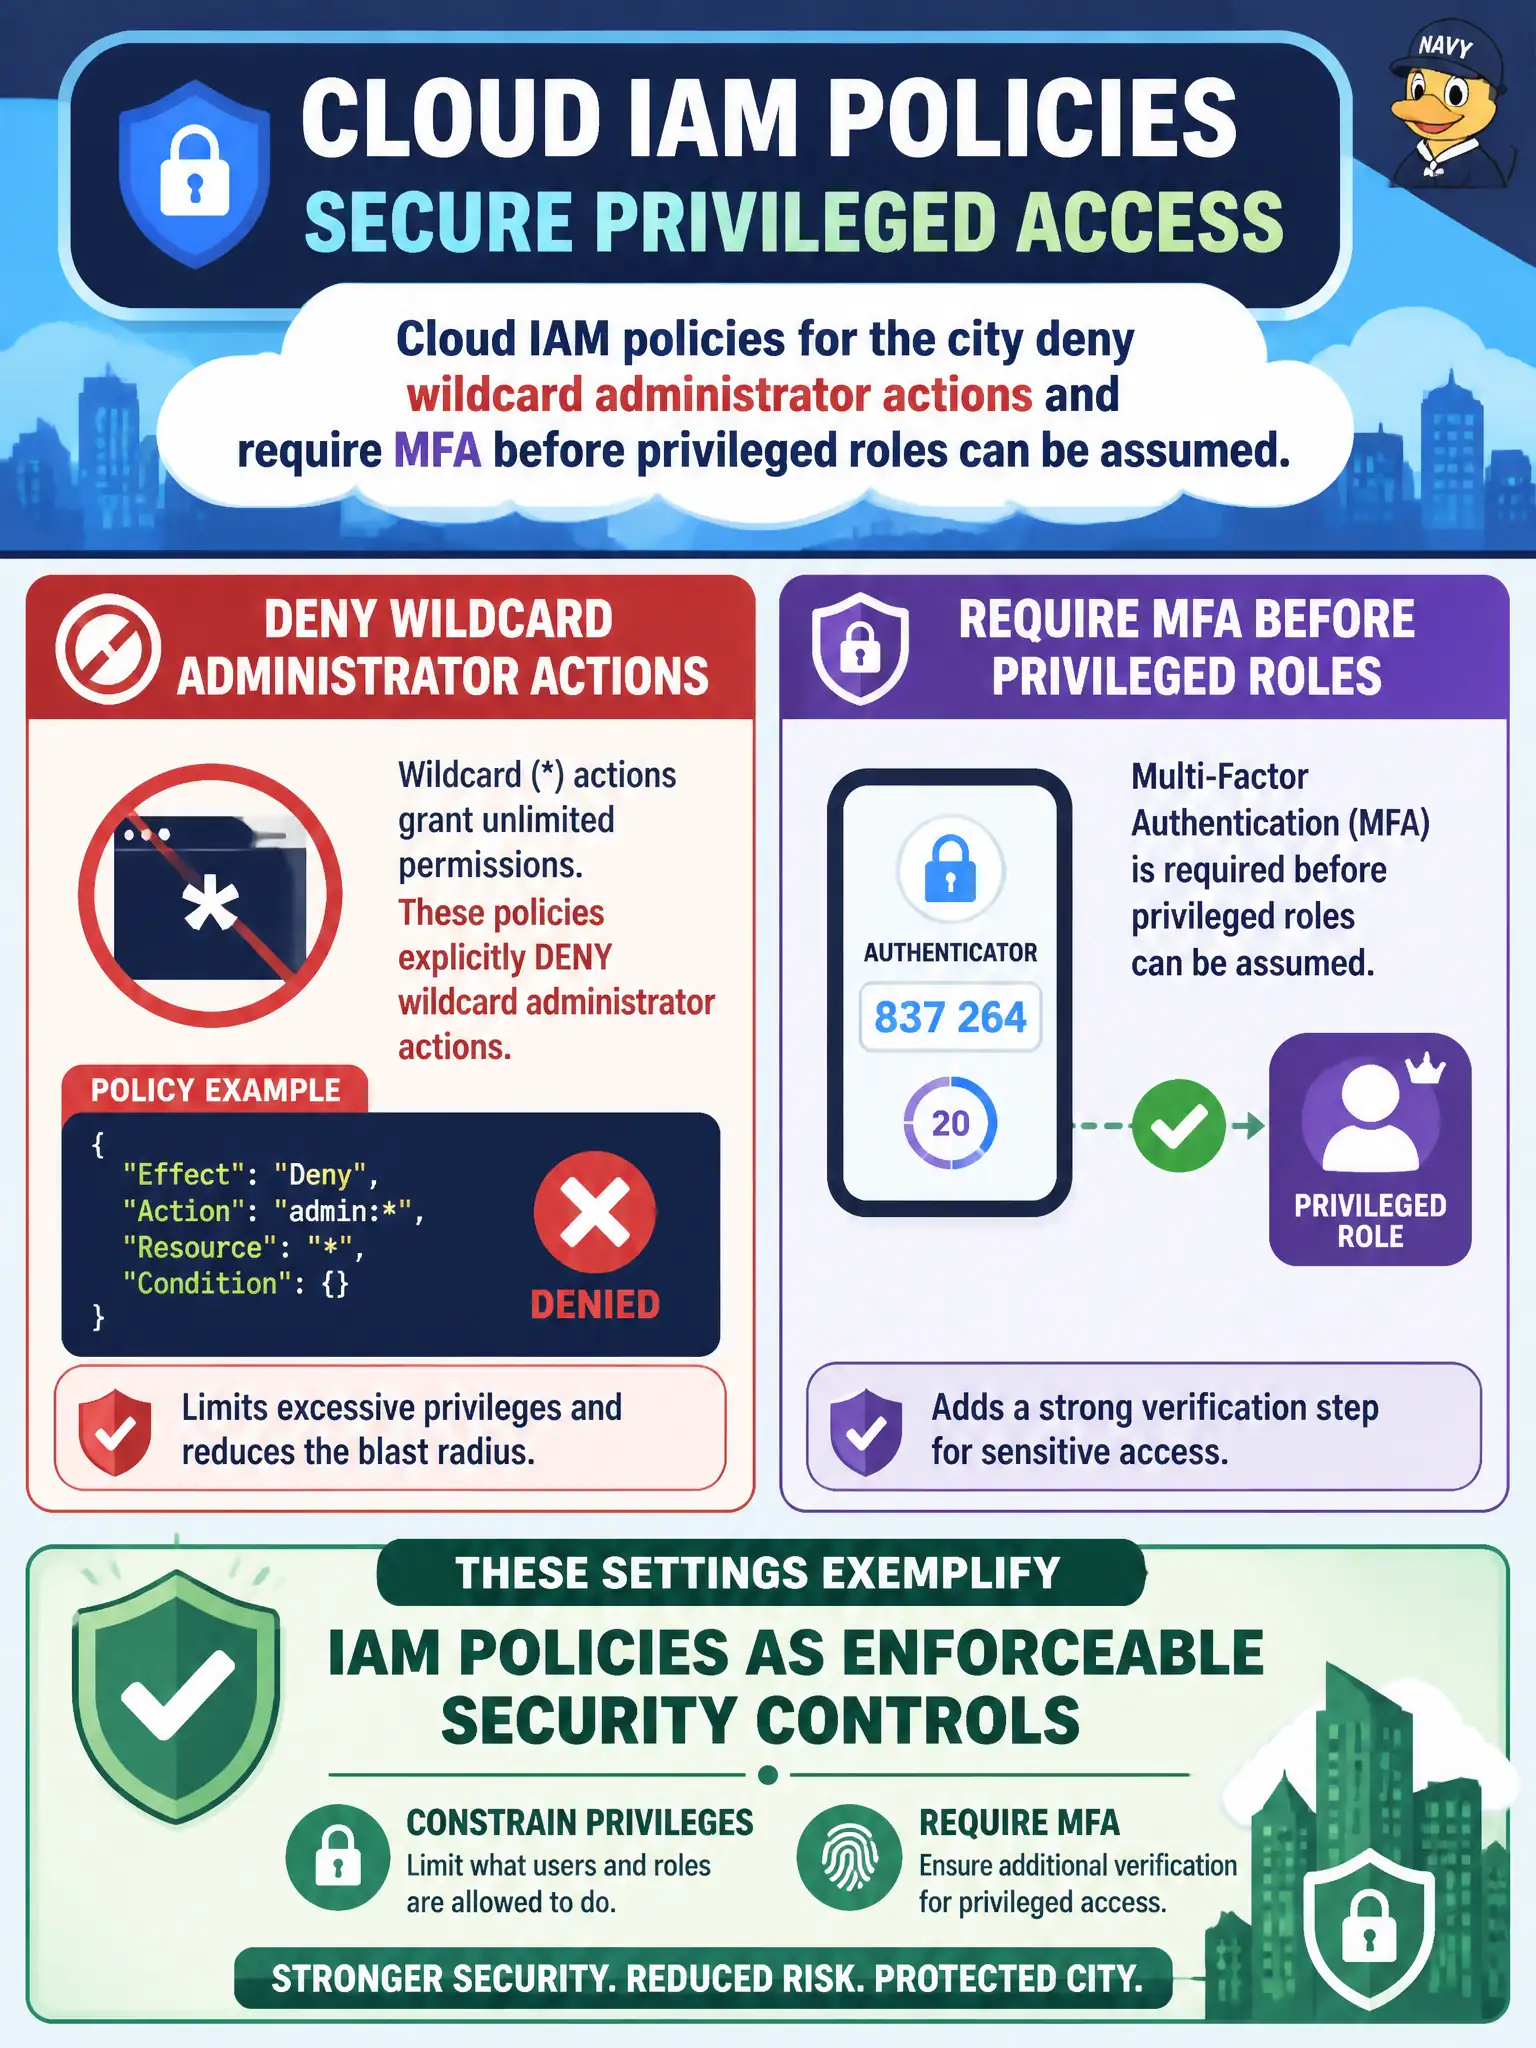
Cloud IAM policies for the city deny wildcard administrator actions and require MFA before privileged roles can be assumed. What do these settings exemplify?
Select an answer to reveal the explanation.
Short Explanation
IAM policies are not sticky notes—they are the rules the cloud actually enforces. Blocking wildcard admin and demanding MFA for privileged roles hardens who can do damage. Writing Action:* for everyone is the anti-pattern these controls fix.
Full Explanation
IAM policies are enforceable security controls that authorize or deny API actions at runtime. Denying wildcard administrator actions and requiring MFA before privileged roles can be assumed exemplifies using IAM policy as a live control plane constraint—not optional documentation—for the city’s cloud identities. Policies shape what humans and services can actually do.
Optional documentation notes that never enforce runtime authorization are not IAM policies in effect. Network cable labeling standards do not authorize cloud actions. Unrestricted Action:* policies attached to every identity are the opposite of constrained privilege.
Exam caveat: identity-based and resource-based policies, deny vs allow evaluation, and conditions (such as MFA) are core IAM exam topics. Prefer least privilege over wildcards.
Operational check: inspect privileged role trust/policy for MFA conditions, search for Action:* Allow statements, remediate wildcards, test that privileged assume-role fails without MFA, and continuous-monitor policy changes. Include IAM policy review in quarterly municipal access certifications.
Use policy-as-code tests in CI to reject IAM templates that reintroduce Action:* or drop MFA conditions on privileged role assumption, preventing documentation drift from becoming runtime authorization drift.