
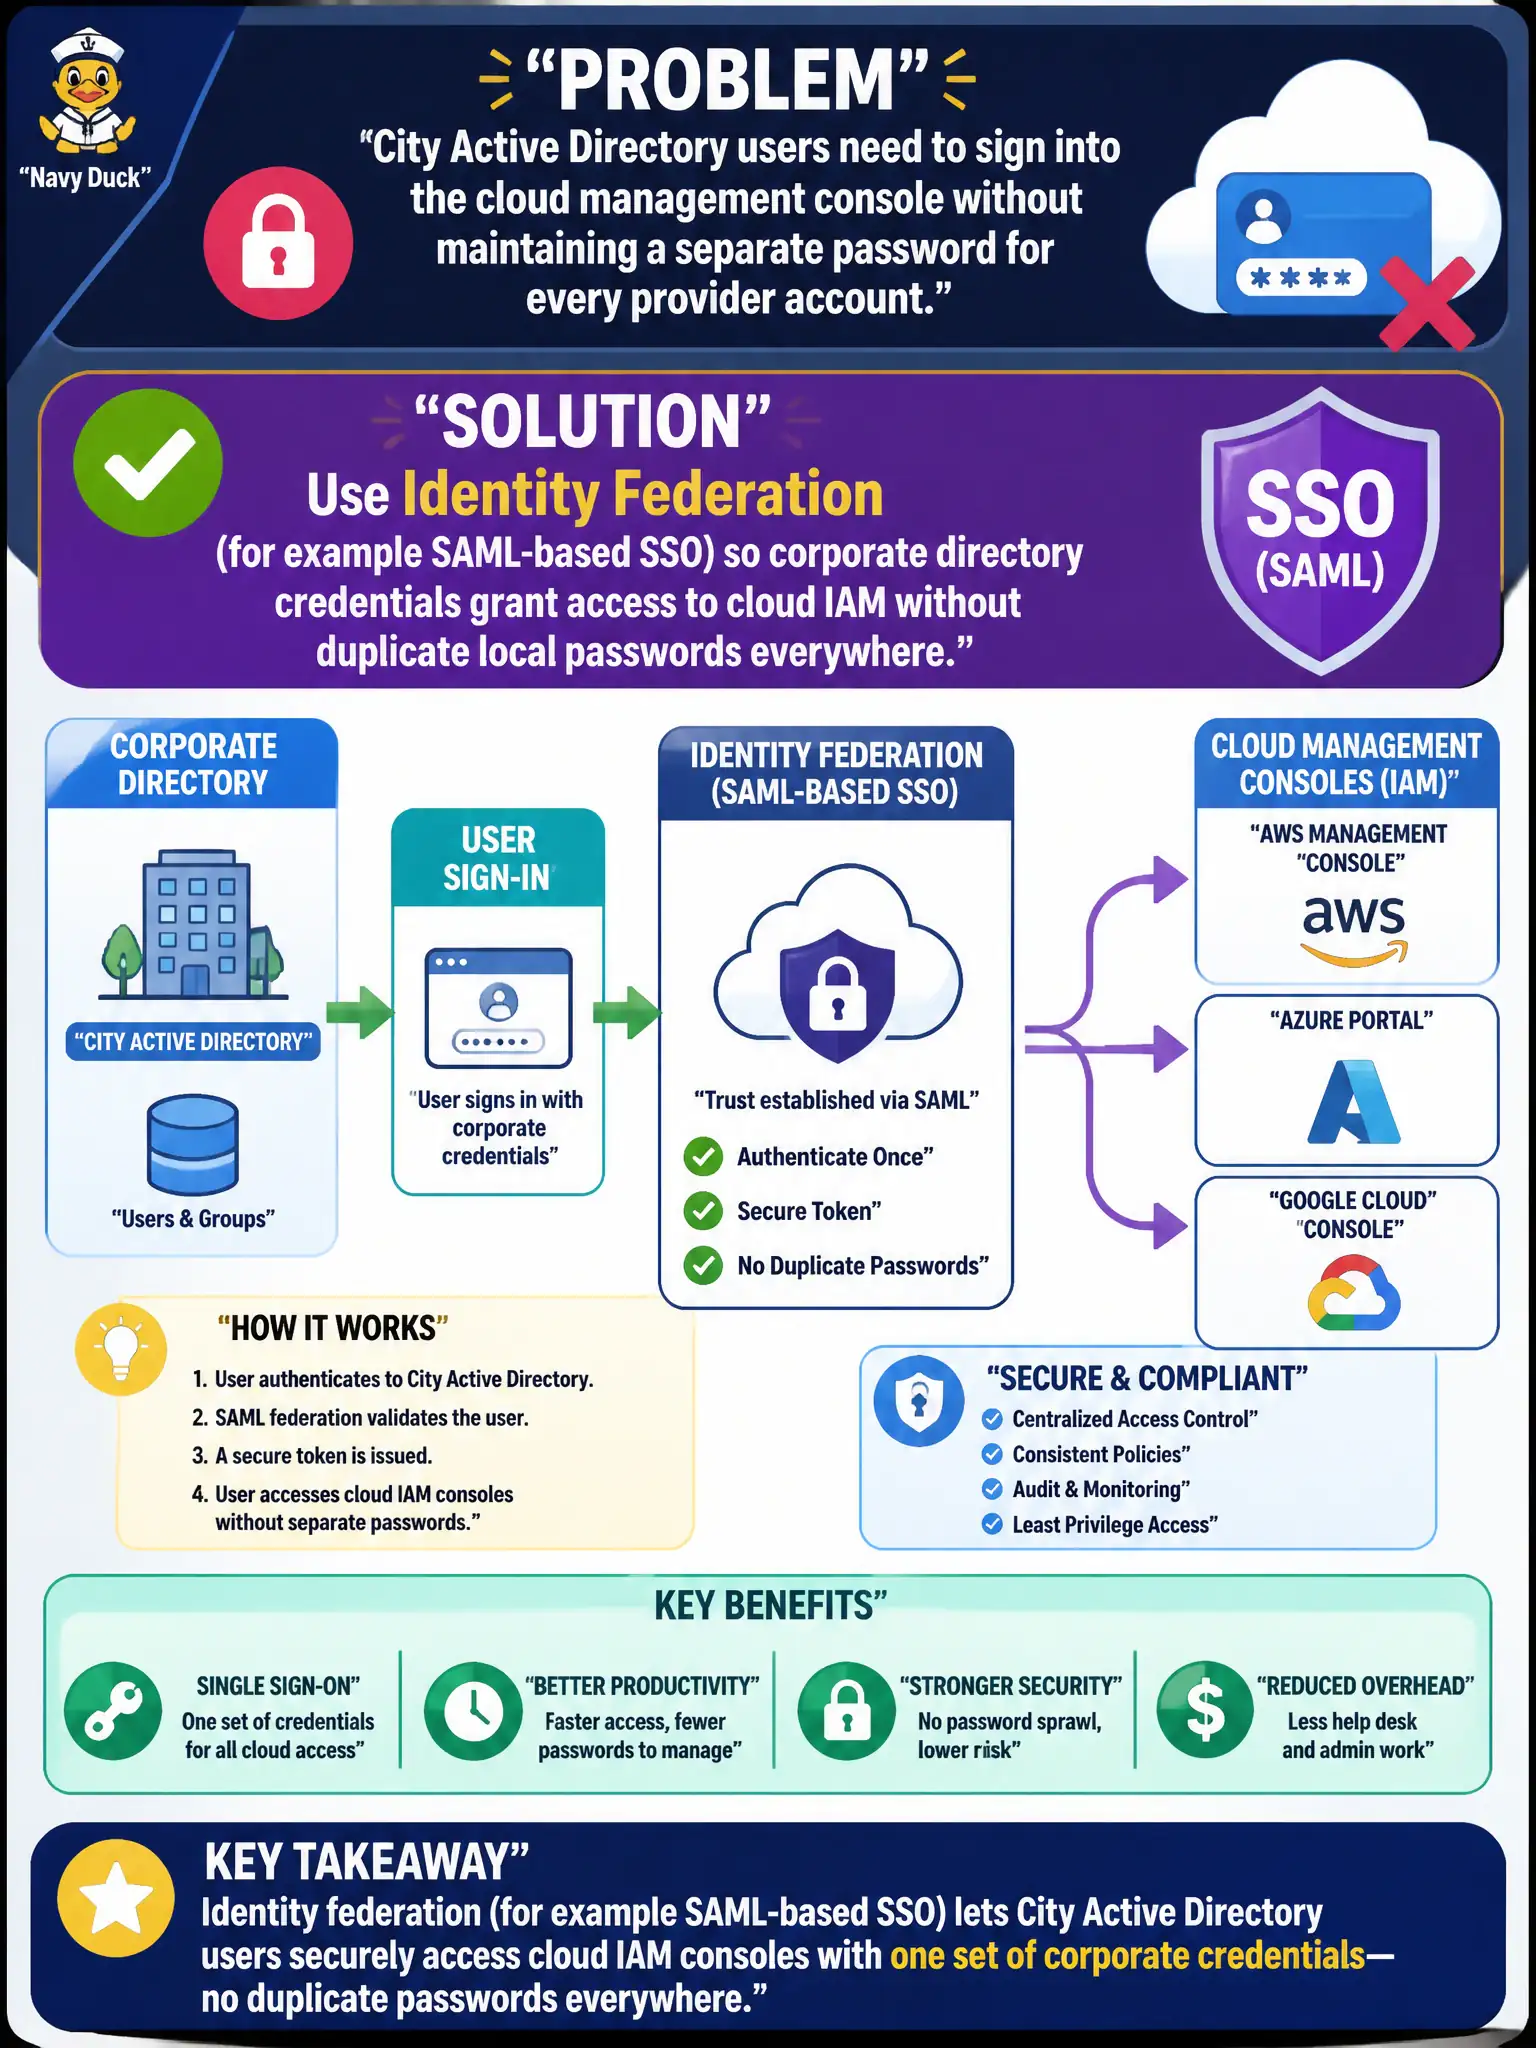
City Active Directory users need to sign into the cloud management console without maintaining a separate password for every provider account. What IAM approach enables that?
Select an answer to reveal the explanation.
Short Explanation
Federation is the city badge that also opens the cloud lobby—SAML SSO lets AD users in without yet another sticky-note password. Shared whiteboard passwords and open consoles are not SSO.
Full Explanation
Identity federation (commonly SAML or OIDC-based SSO) lets city Active Directory (or other corporate IdP) credentials grant access to cloud IAM without maintaining a separate password for every provider account. Users sign into the management console via the directory relationship, improving UX and centralizing disablement when staff leave municipal employment.
Creating identical local passwords on every cloud user and writing them on shared whiteboards multiplies credential risk. Disabling authentication so the console is open to anonymous visitors removes security entirely. Requiring a new unique cloud-only password daily with no directory integration increases fatigue without solving lifecycle joiners/movers/leavers cleanly.
Exam caveat: federation maps IdP groups/roles to cloud roles; MFA may still be required at IdP or cloud. Federation is about authentication/identity source, not a replacement for least-privilege authorization design.
Operational check: configure the IdP application and cloud IAM identity provider trust, map AD groups to cloud roles, test console login for a standard user and an admin, disable a test user in AD and confirm cloud access stops, and document the federation runbook for the city’s identity team.