
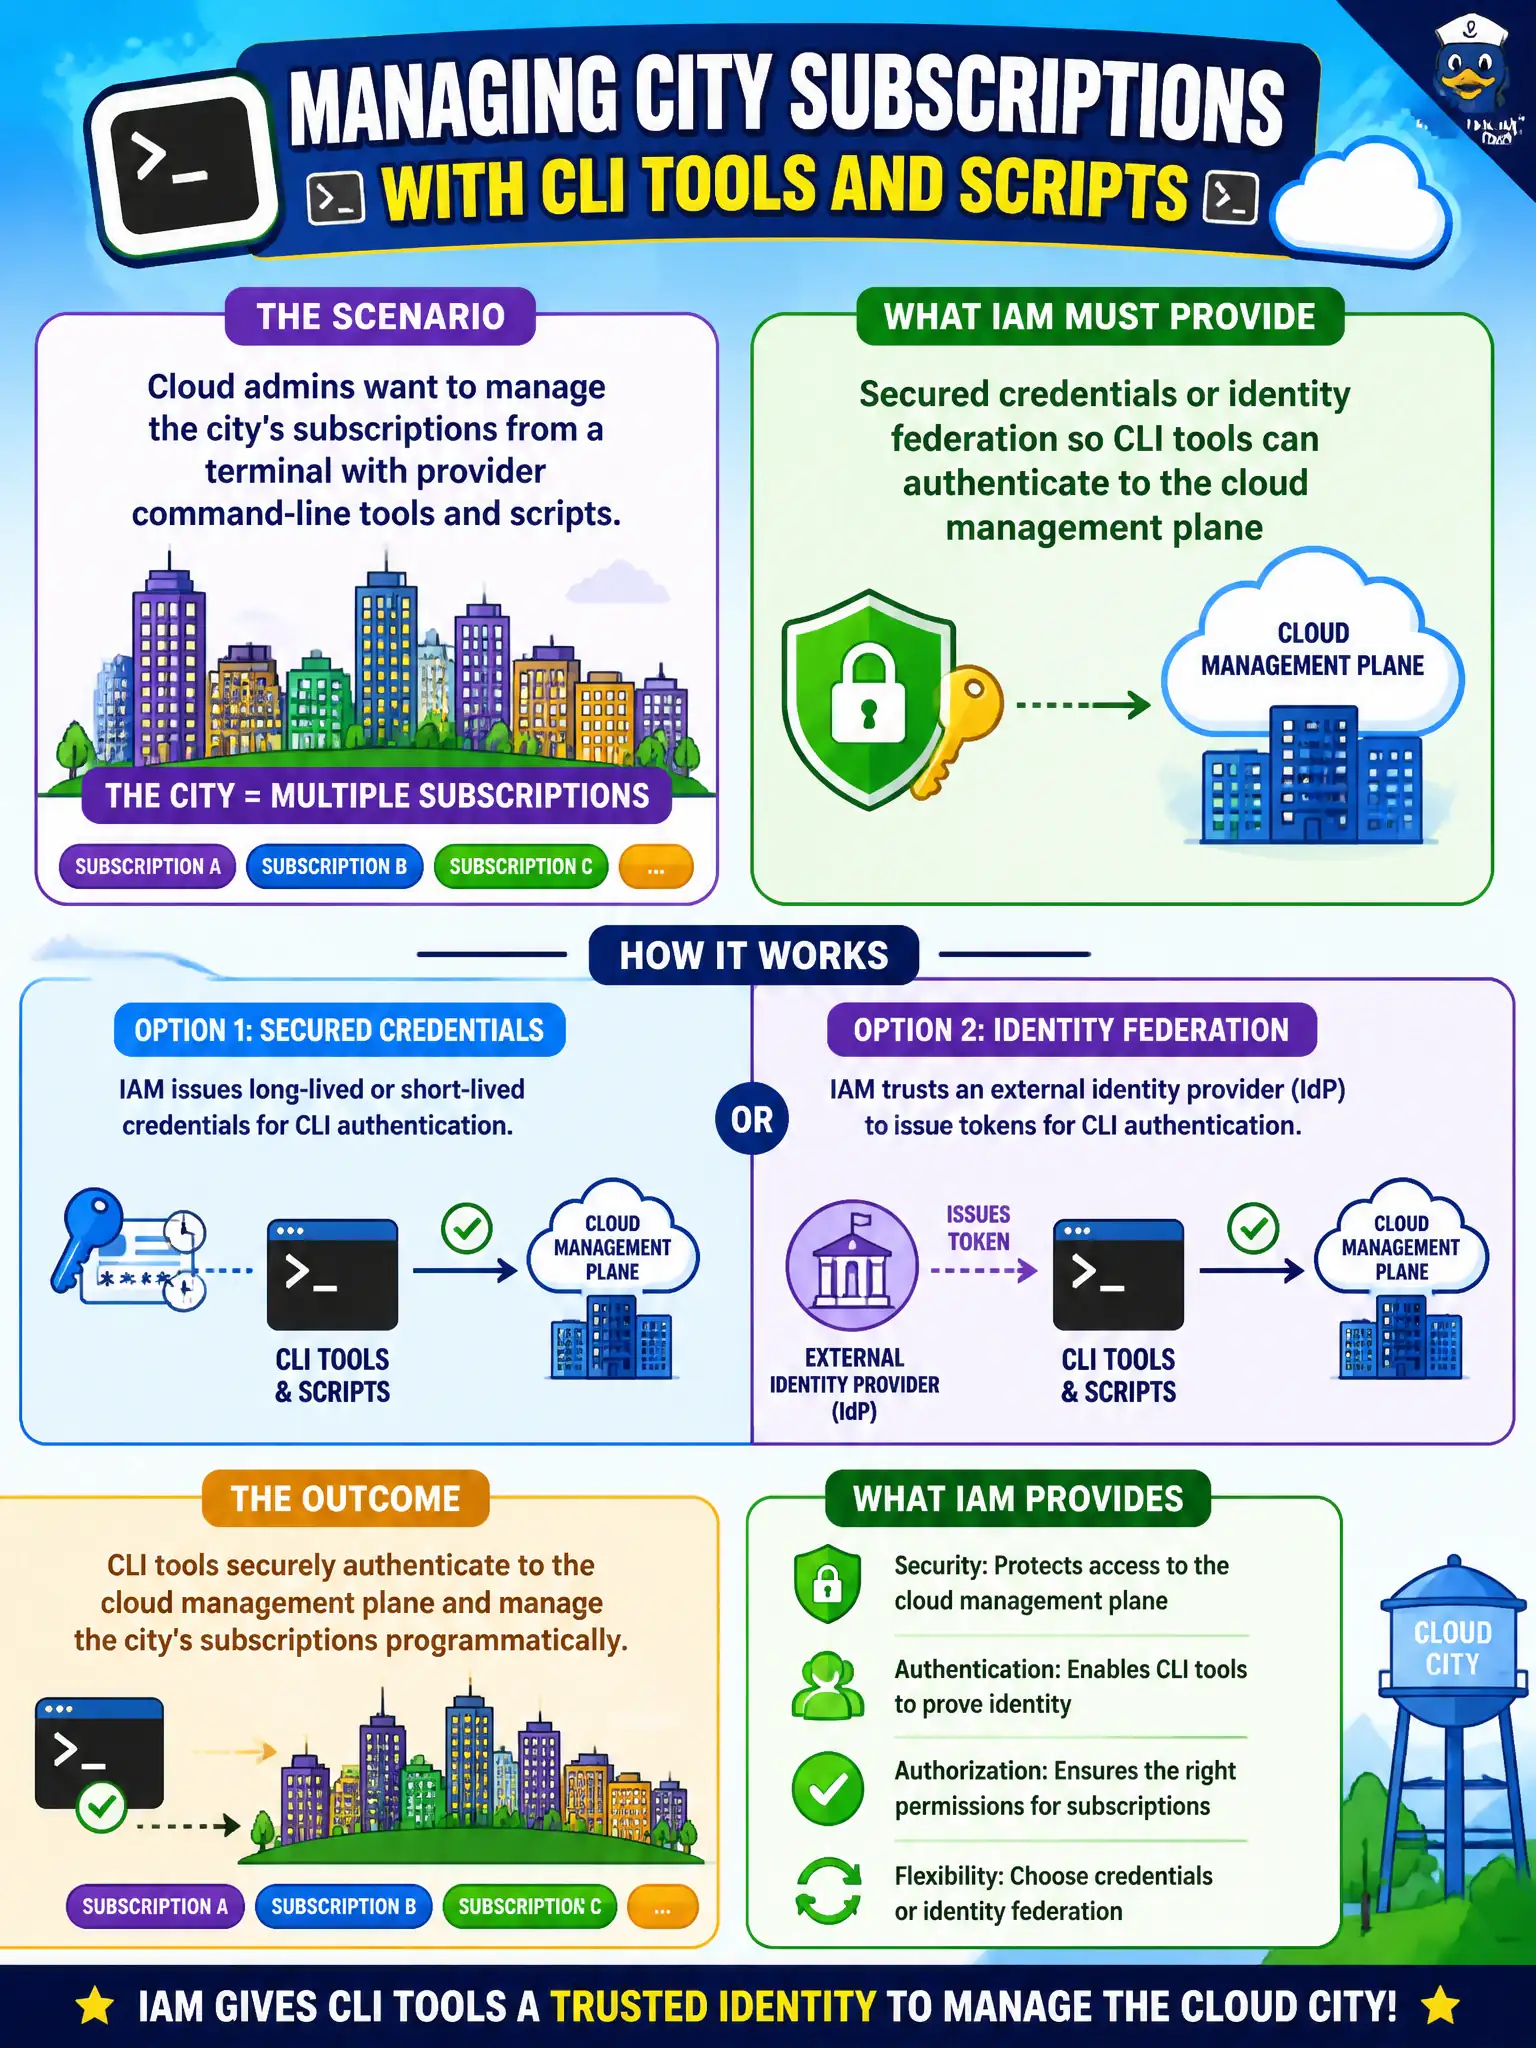
Cloud admins want to manage the city's subscriptions from a terminal with provider command-line tools and scripts. What must IAM provide?
Select an answer to reveal the explanation.
Short Explanation
The CLI is just another front door to the control plane—it still needs a badge. Wire up secured credentials or federation (and keep logging) so terminal scripts are authenticated, not anonymous.
Full Explanation
CLI tools and scripts need secured credentials or identity federation to authenticate to the cloud management plane just as the console does. Providing those IAM authentication methods lets city admins manage subscriptions from a terminal without resorting to anonymous or unlogged access. Secure CLI access is part of normal cloud operations hygiene.
Unrestricted anonymous CLI access from any IP without credentials is indefensible. Removing all audit logging when CLI is enabled blinds investigations. Requiring that CLI users never use MFA even if policy demands it weakens a control the console may already enforce.
Exam caveat: CLI, SDK, and console are different clients of the same IAM system—controls should be consistent. Federation and MFA for privileged CLI use are common hardening expectations.
Operational check: configure CLI profiles with federation or vaulted credentials, enforce MFA where supported for human operators, restrict source IPs if policy requires, and verify CloudTrail/activity logs capture CLI API calls. Train admins not to share access keys in chat.
Ban shared CLI access keys in team password managers when individual federation is available, and periodically attest that every active municipal admin profile uses unique identity with MFA aligned to console policy.