
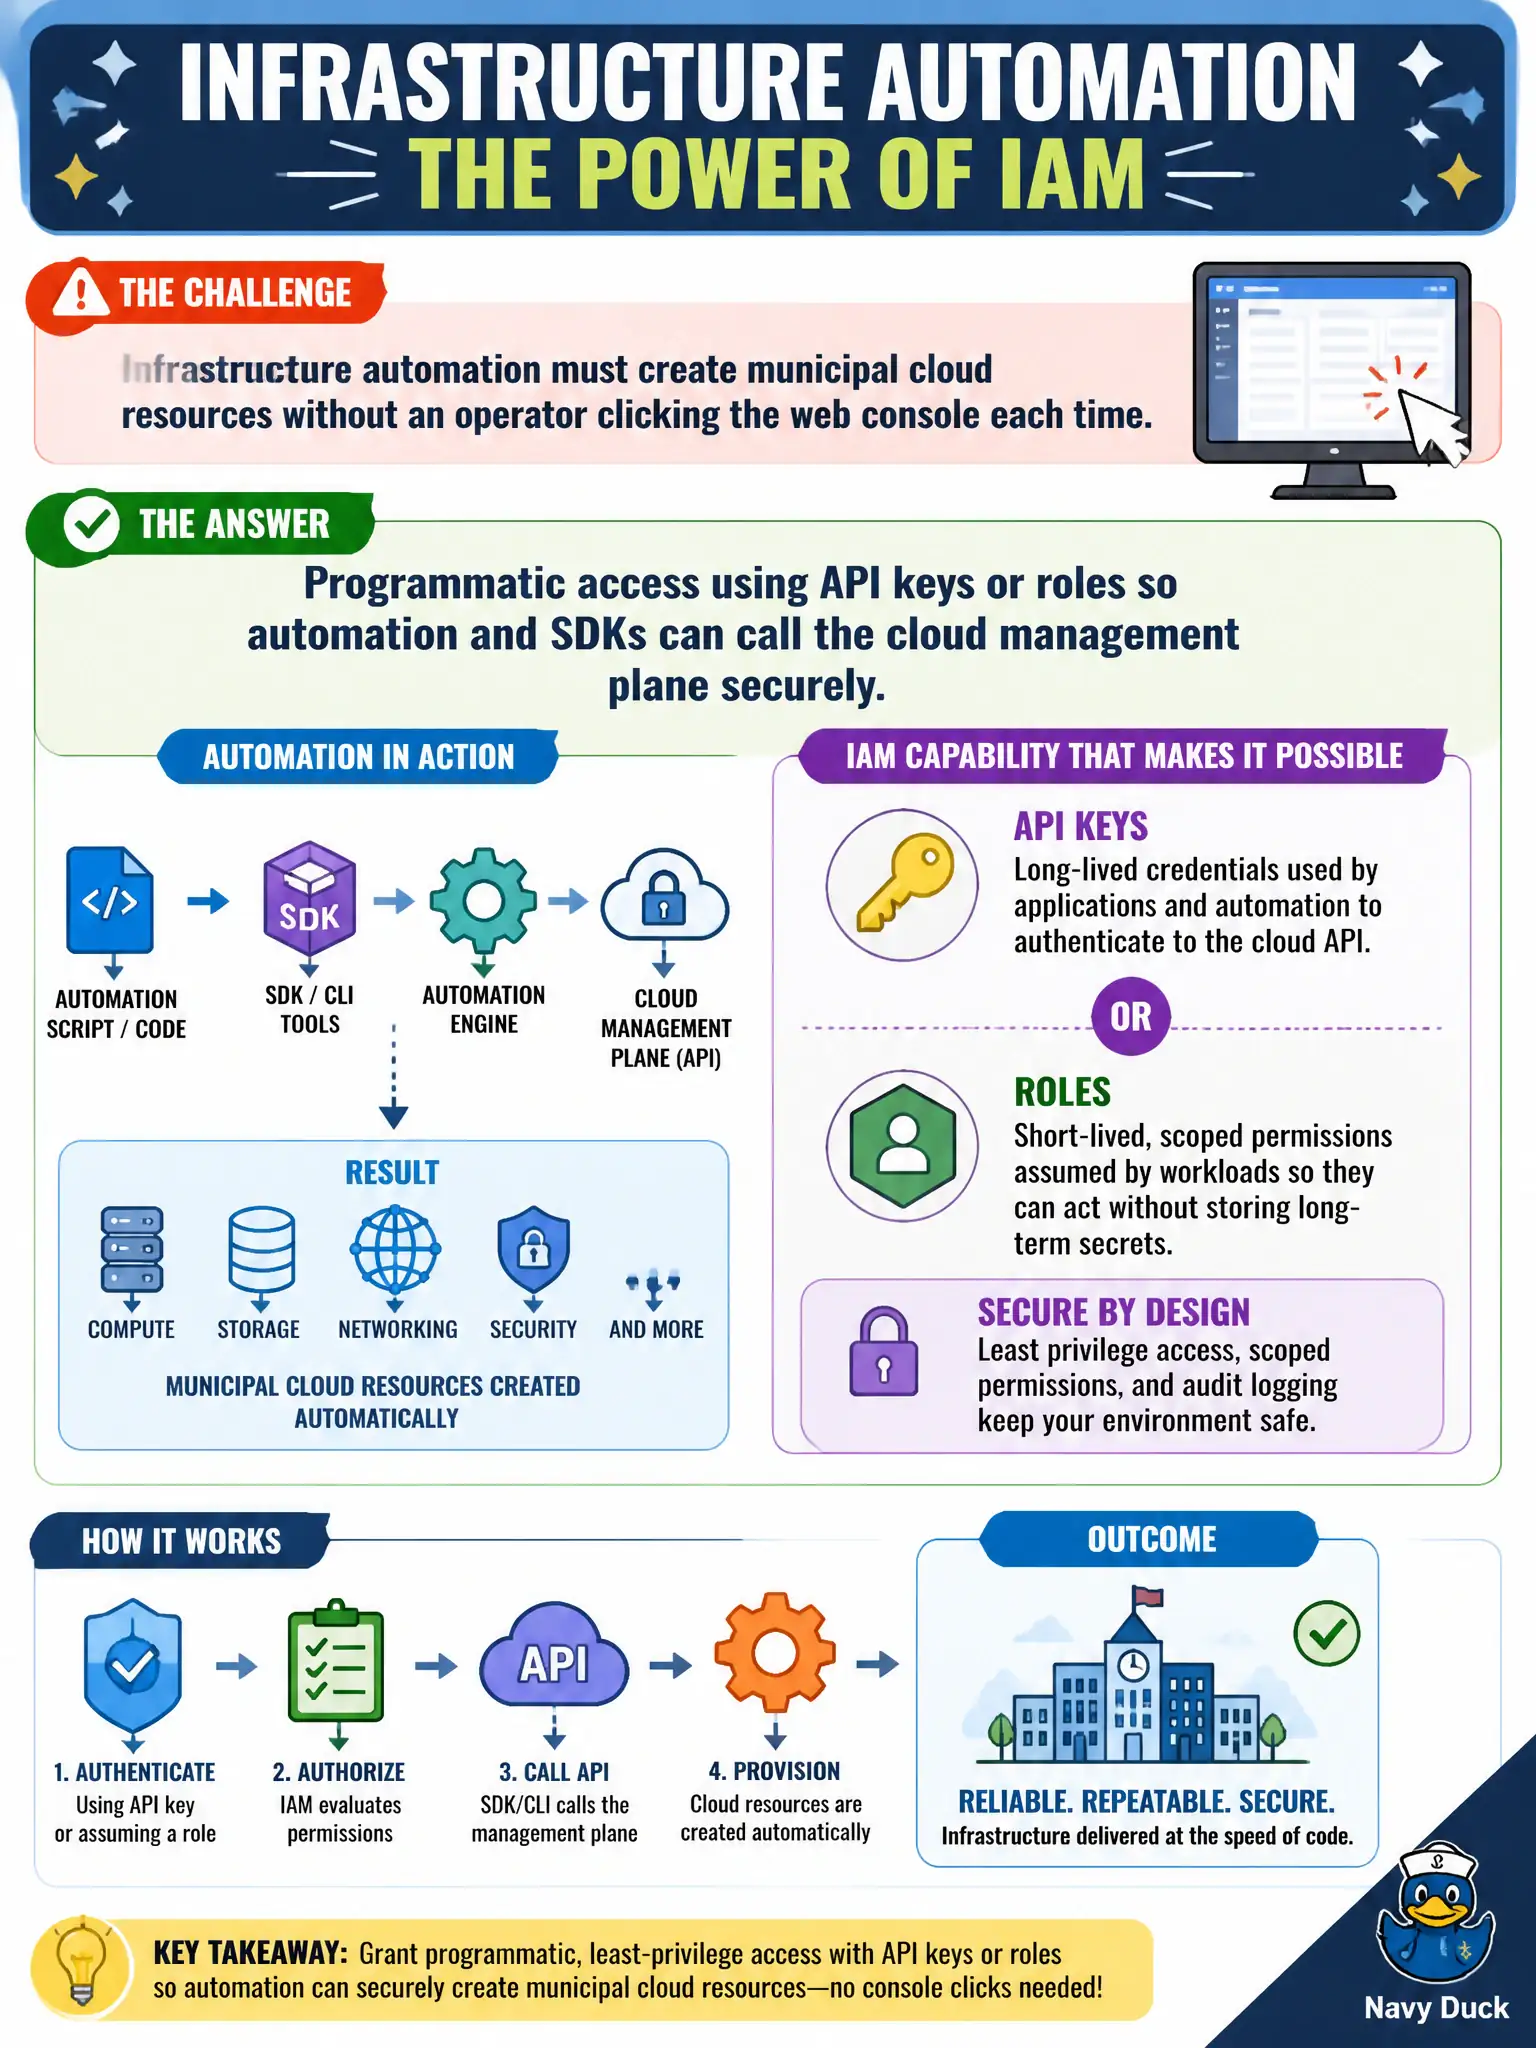
Infrastructure automation must create municipal cloud resources without an operator clicking the web console each time. What IAM capability enables that?
Select an answer to reveal the explanation.
Short Explanation
Bots do not click buttons—they call APIs. Give automation scoped API keys or roles so it can create resources on the management plane without a human in the portal every time.
Full Explanation
Infrastructure automation needs programmatic access to the cloud management plane via API keys, instance/service roles, or similar IAM-issued credentials so SDKs and pipelines can create municipal resources without an operator clicking the web console each time. That capability is what allows repeatable, audited infrastructure-as-code for city platforms.
Paper change forms faxed to the provider each hour are not cloud IAM programmatic access. Disabling all APIs so only mouse clicks work blocks automation. Sharing one interactive desktop session among all scripts is insecure and unscalable.
Exam caveat: prefer short-lived roles/federation over long-lived static keys when possible; still, the core concept is programmatic API access under IAM. Never embed keys in public repos.
Operational check: create a dedicated automation identity with least privilege, store credentials in a secrets manager or use OIDC/role federation from CI, run a pipeline that creates a tagged test resource, and audit API calls. Rotate keys and review role policies quarterly for the municipal landing zone.
Prefer workload identity or OIDC federation from the CI system into cloud roles when the provider supports it, reducing long-lived key sprawl while still delivering the programmatic access automation requires for municipal landing zones.