
A public-archive retrieval team handles sealed personnel files and wants stronger GenAI privacy and security controls for test tasks. Which pair of complementary mitigations best fits the syllabus guidance?
Select an answer to reveal the explanation.
Short Explanation
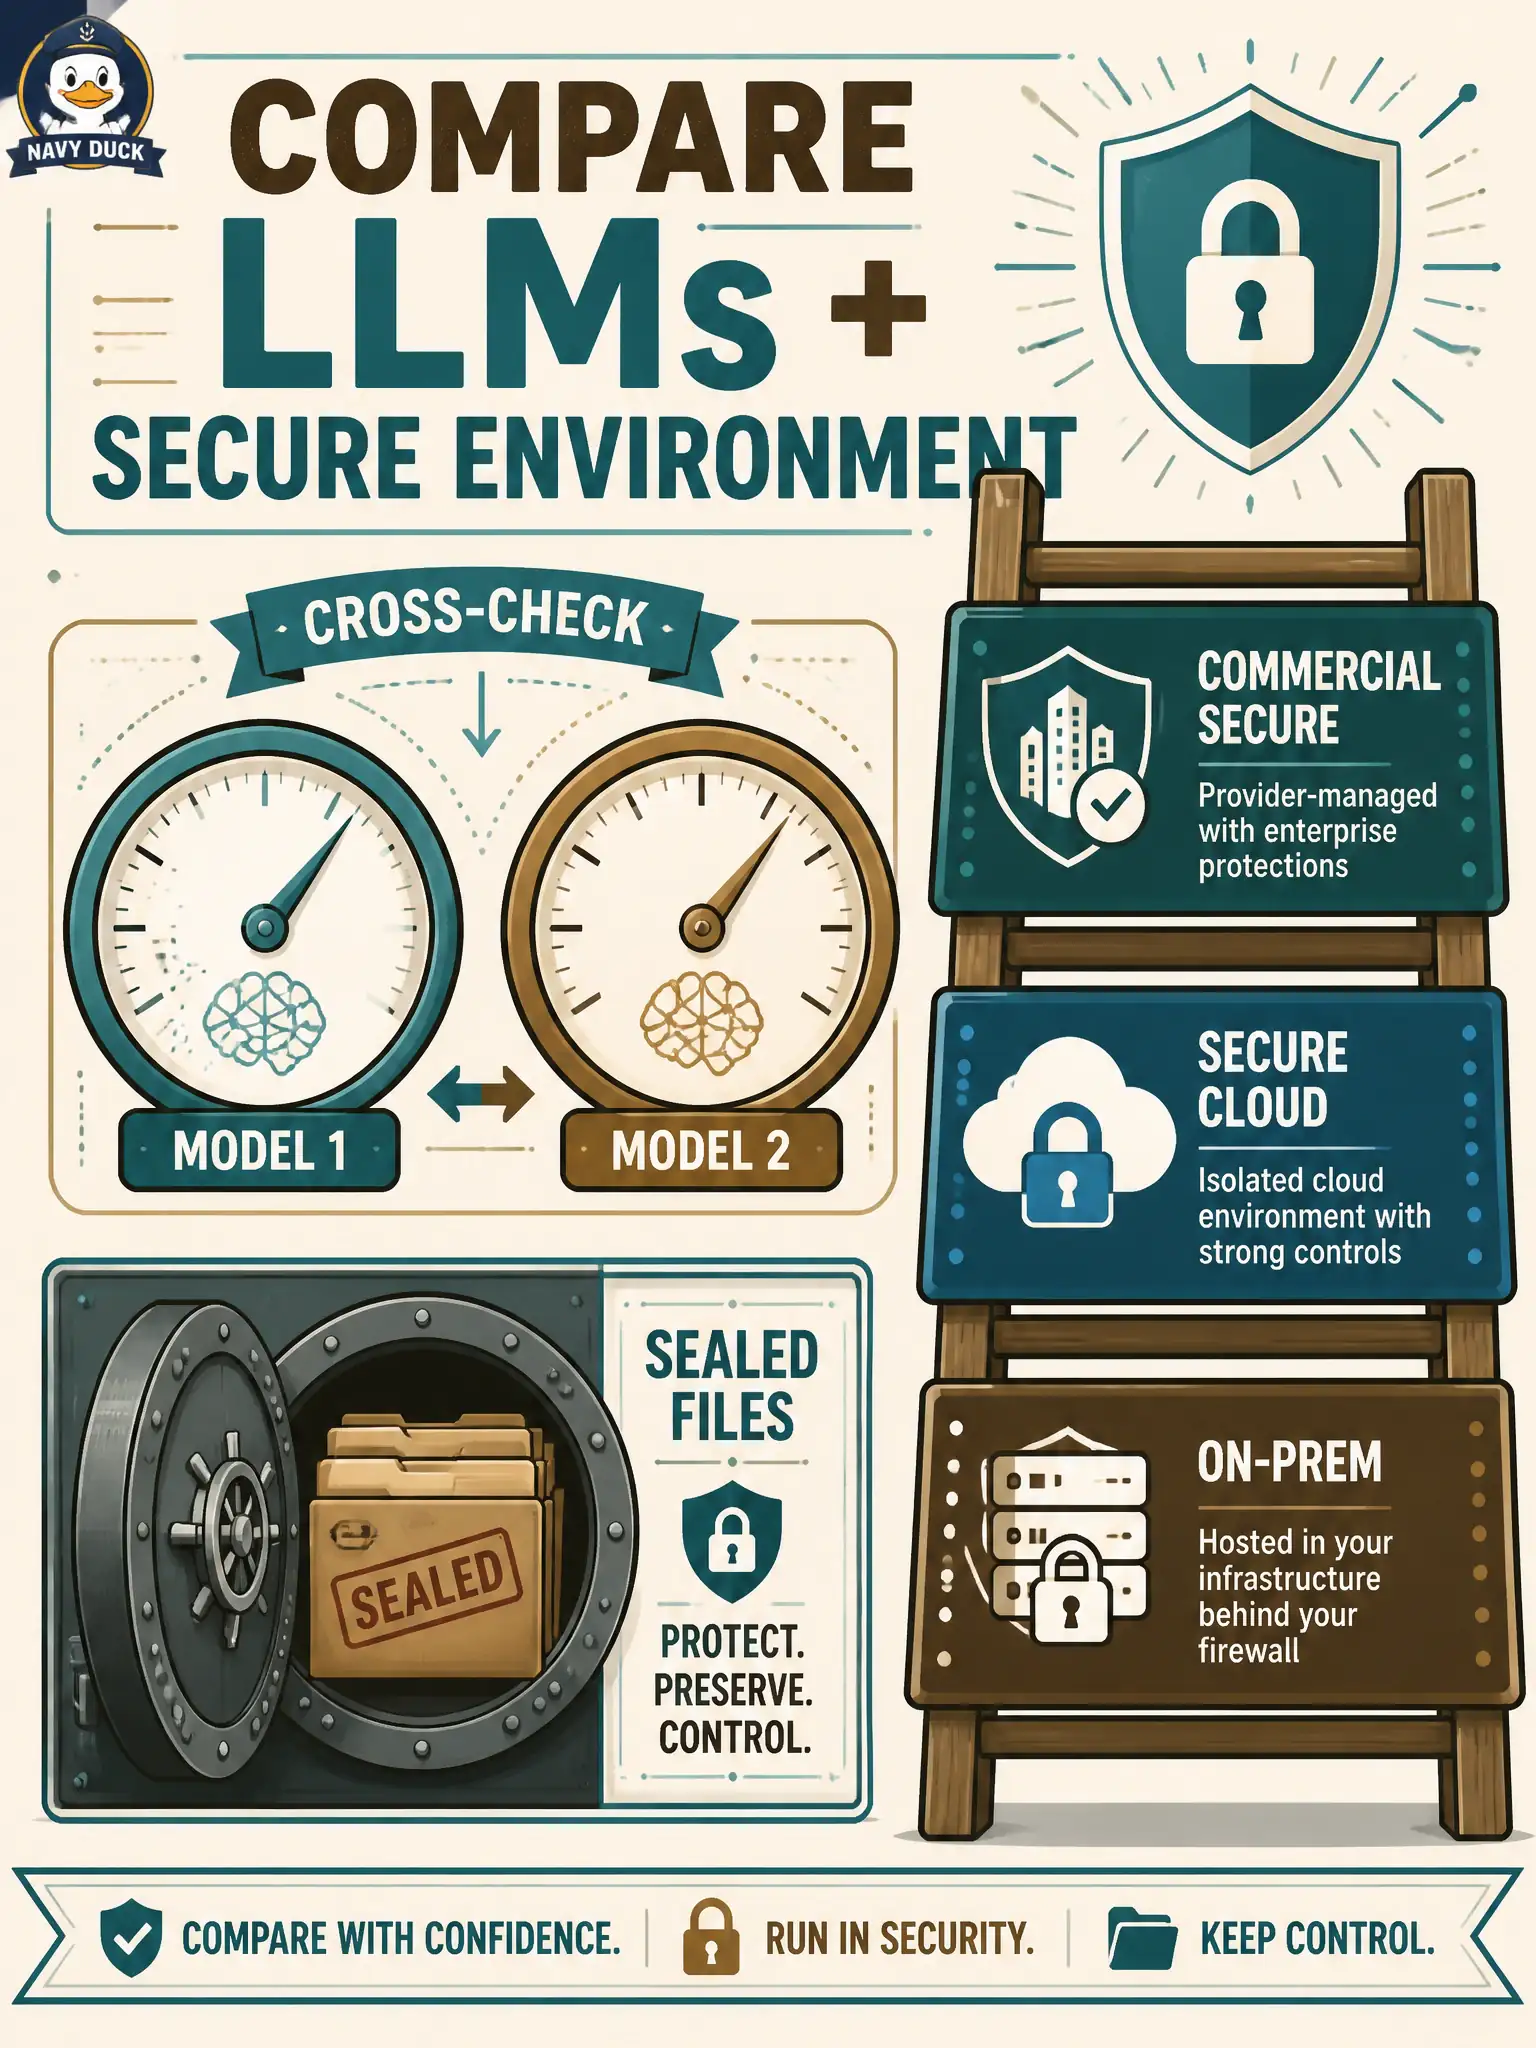
Sealed personnel files deserve both a second opinion and a locked workshop. Comparing outputs across LLMs and picking a secure operating environment—commercial secure offering, secure cloud, or on-prem install—fit the confidentiality bar. RAG recipes and prompt styles do not replace that pair.
Full Explanation
Public-archive teams handling sealed personnel files need stronger GenAI privacy and security controls. The syllabus pair that best fits is evaluate by comparison with another LLM, and choose a secure operational environment matched to confidentiality—commercial secure offering, secure cloud, or on-prem—as complementary mitigations.
Adopting RAG first then fine-tuning on sealed files fails by concept: architecture recipes do not replace secure environment choice and can worsen exposure if misapplied to sealed content. Relying on GDPR alone and skipping environment or comparison choices fails because legal compliance and technical/process mitigations both matter. Using only zero-shot prompts so sealed content never needs custody controls fails: prompt style is not a custody program.
Exam caveat: comparison across models helps detection; secure environment choice addresses custody—together they match high-confidentiality civic archives better than prompt tricks alone.
Operational check: keep sealed-file GenAI work in an approved secure enclave; compare critical outputs across models or reviewers; forbid public chatbots; log access; involve records/legal officers before any sealed series enters a prompt.