
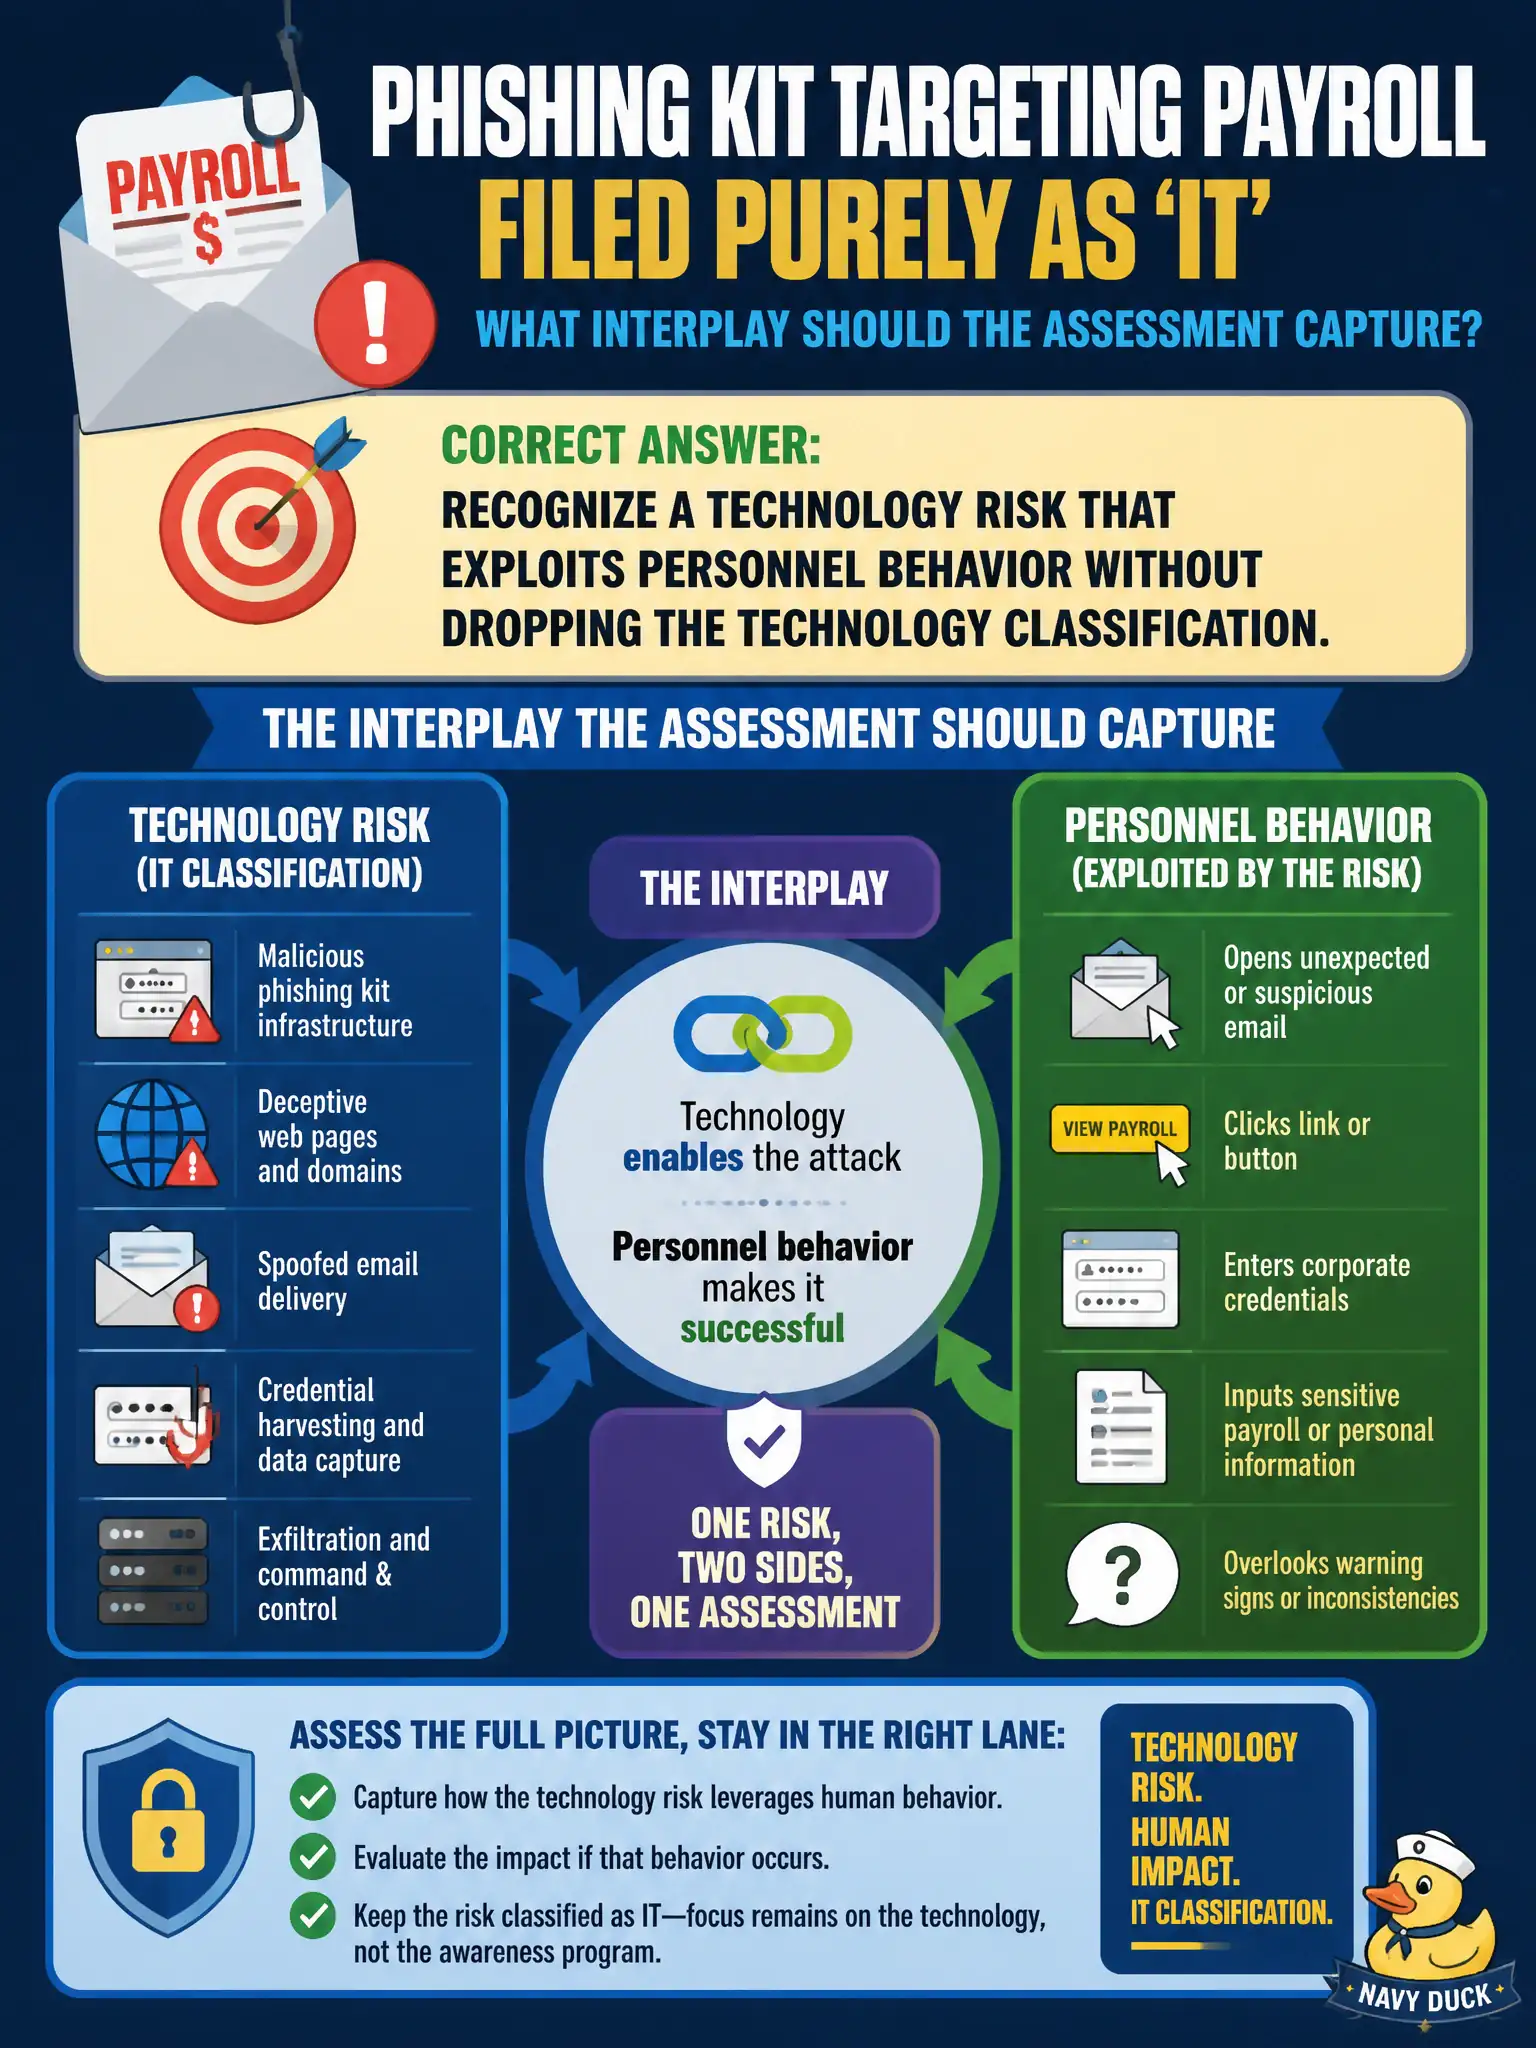
A phishing kit targeting payroll is filed purely as 'IT' with no personnel-awareness angle. What interplay should the assessment capture?
Select an answer to reveal the explanation.
Short Explanation
Phishing hits both the inbox tech and the human who clicks. Keep it as technology risk, but do not pretend awareness training is optional wallpaper.
Full Explanation
A phishing kit targeting payroll should be assessed as a technology risk that exploits personnel behavior—without dropping the technology classification or ignoring awareness controls. Ignoring technology entirely and treating phishing only as HR wellness is incomplete. Classifying phishing as environmental due to server heat is nonsensical. Moving it to supplier risk because the kit vendor is unknown misuses supplier categories. Exam caveat: many cyber risks are socio-technical; keep the primary technology class and address people controls as treatments. Operational check: maintain a technology-risk register entry for payroll phishing, pair it with MFA, email filtering, and targeted awareness for payroll staff, and measure click/report rates after simulations. Involve HR for training delivery while IT/security retains risk ownership for the civic payroll systems. In municipal practice, record the rationale in the risk procedure or committee minutes so future staff apply the same rule under budget pressure. Re-validate after the next seasonal peak or org-chart change to confirm the civic control still holds as designed for residents and staff. In municipal practice, record the rationale in the risk procedure or committee minutes so future staff apply the same rule under budget pressure. Re-validate after the next seasonal peak or org-chart change to confirm the civic control still holds as designed for residents and staff.