
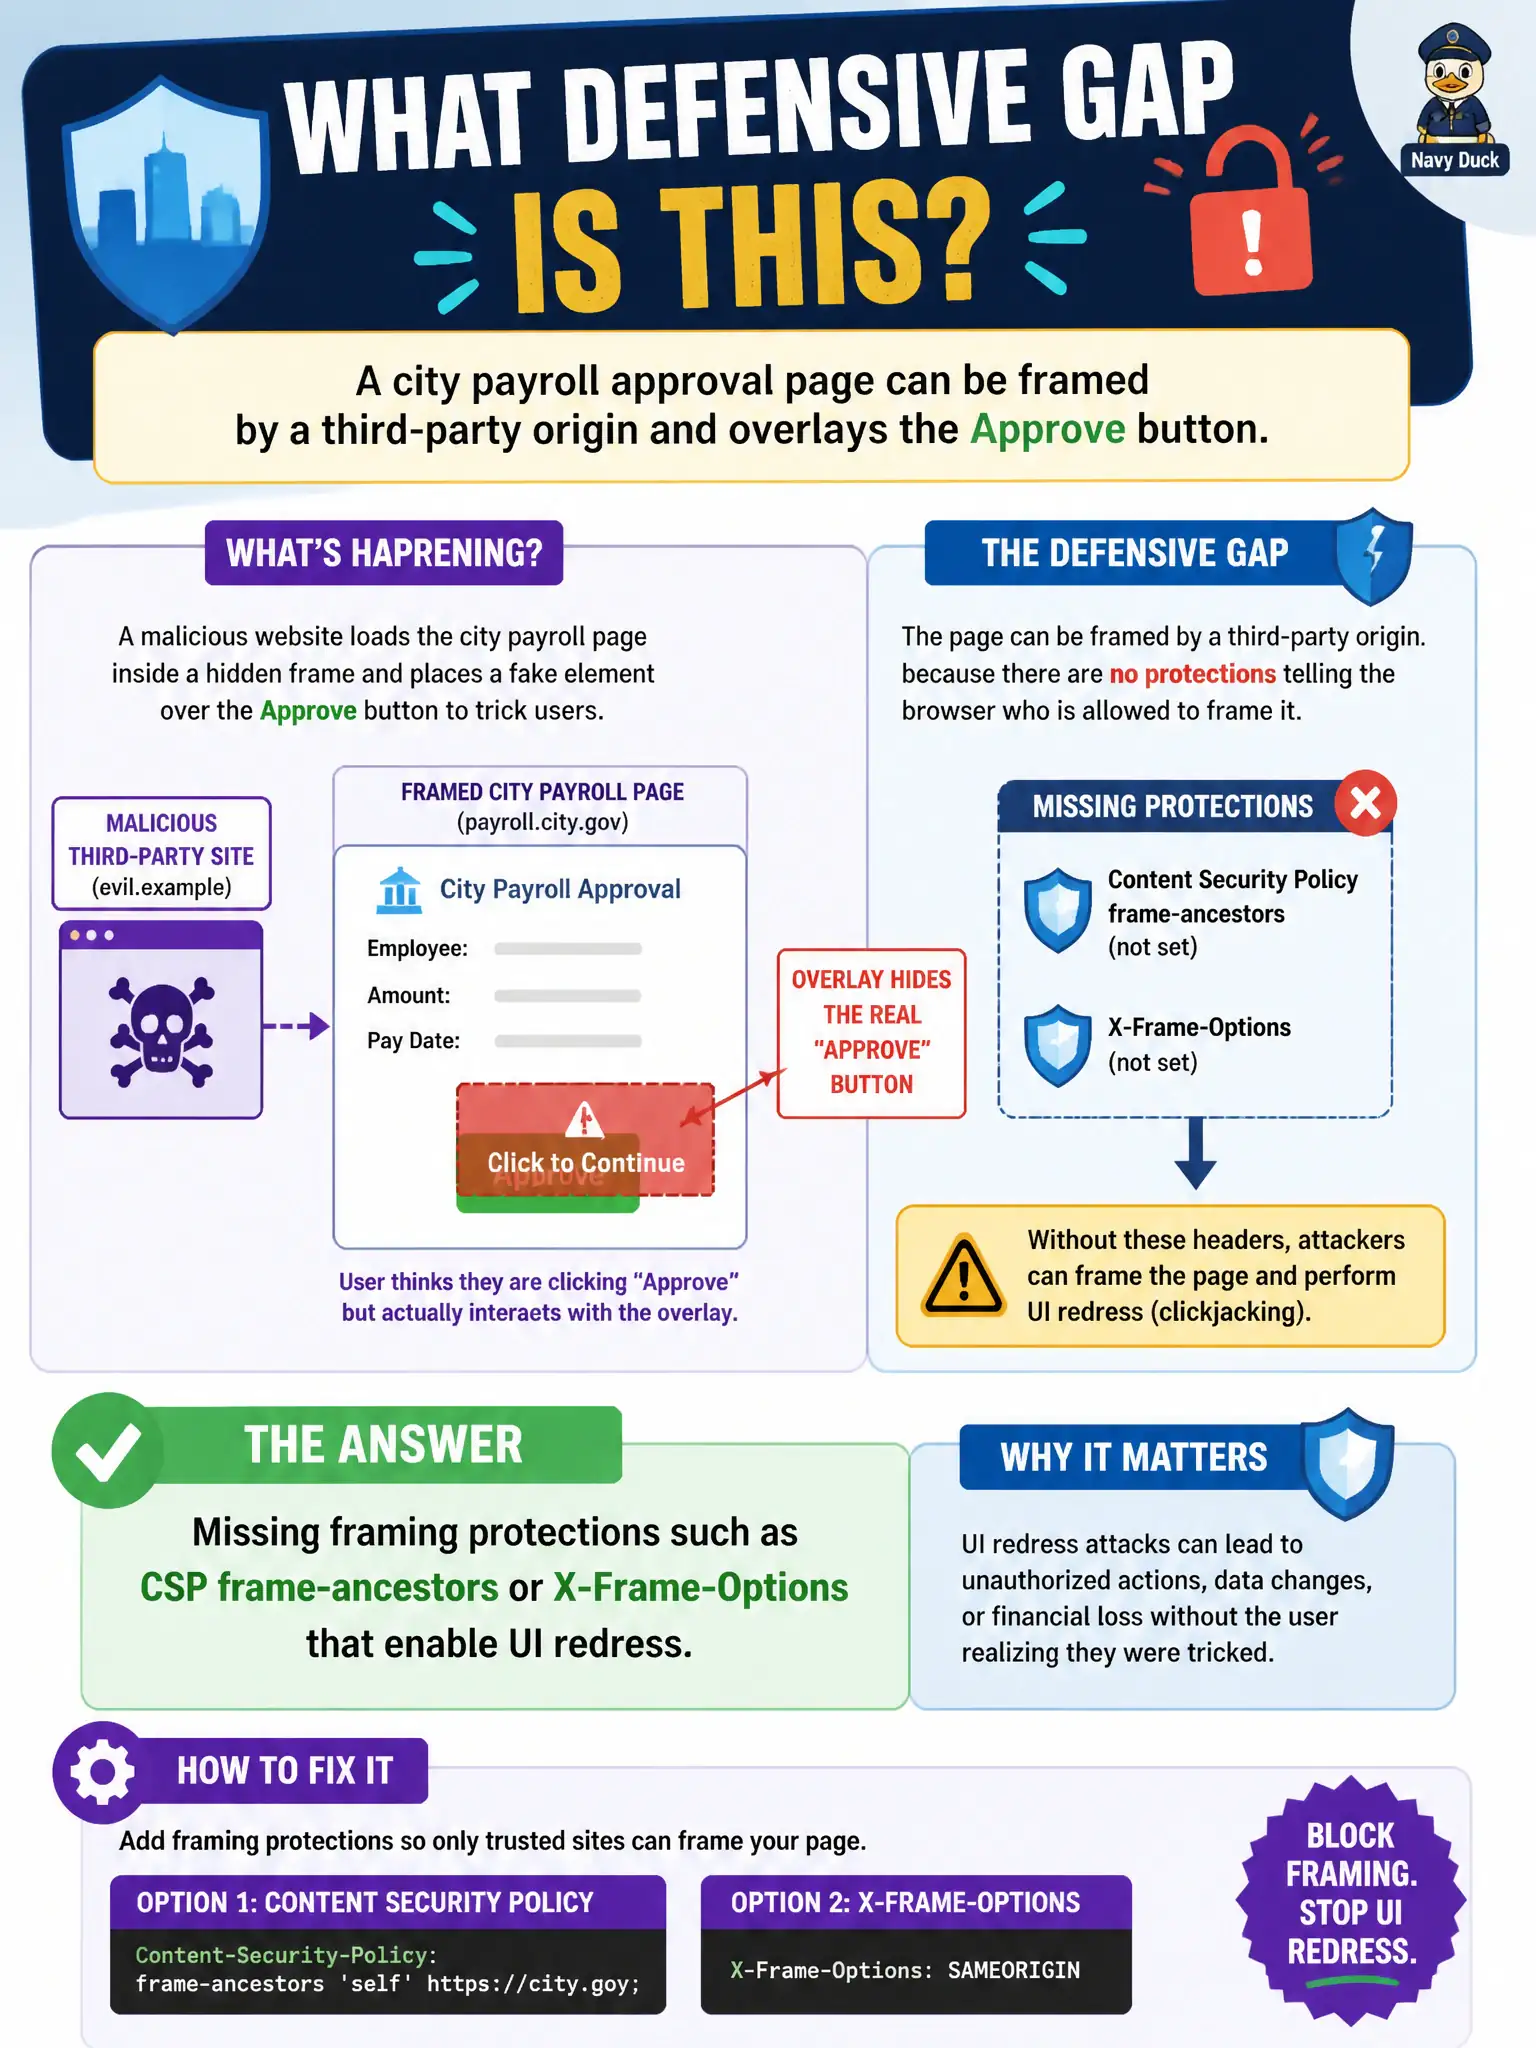
A city payroll approval page can be framed by a third-party origin and overlays the Approve button. What defensive gap does this primarily indicate?
Select an answer to reveal the explanation.
Short Explanation
If a stranger can put a fake glass over your Approve button, you have a clickjacking problem. Missing frame-ancestors or X-Frame-Options is the usual gap. BGP, SMB signing, and newsletter DKIM are different neighborhoods.
Full Explanation
A city payroll approval page that can be framed by a third-party origin so an overlay hijacks the Approve control primarily indicates missing framing protections—CSP frame-ancestors and/or X-Frame-Options—enabling UI redress (clickjacking) against privileged municipal actions.
BGP authentication on border routers is unrelated to browser framing. SMB signing on HR file shares is a file-service integrity control, not a web UI defense. DKIM on a newsletter subdomain addresses email authenticity, not iframe embedding of payroll pages.
Exam caveat: SameSite cookies and UX changes may reduce some risks but do not replace explicit frame-ancestors policy for sensitive approval UIs.
Operational check: attempt to embed the payroll approval page in a cross-origin iframe under authorization, observe whether framing succeeds, and capture evidence. Recommend enforcing CSP frame-ancestors 'self' (or tighter) and verify X-Frame-Options consistency for civic admin workflows. In municipal operations, record the rationale in the engagement notes so future assessors know which control was chosen and which failure modes the rejected options would create for city services. Re-validate after the next release window that the same control still holds under the application's current auth model.