
A county tester has proven a reliable path to local SYSTEM on one Windows host and the next objective involves Active Directory. What distinction must remain clear?
Select an answer to reveal the explanation.
Short Explanation
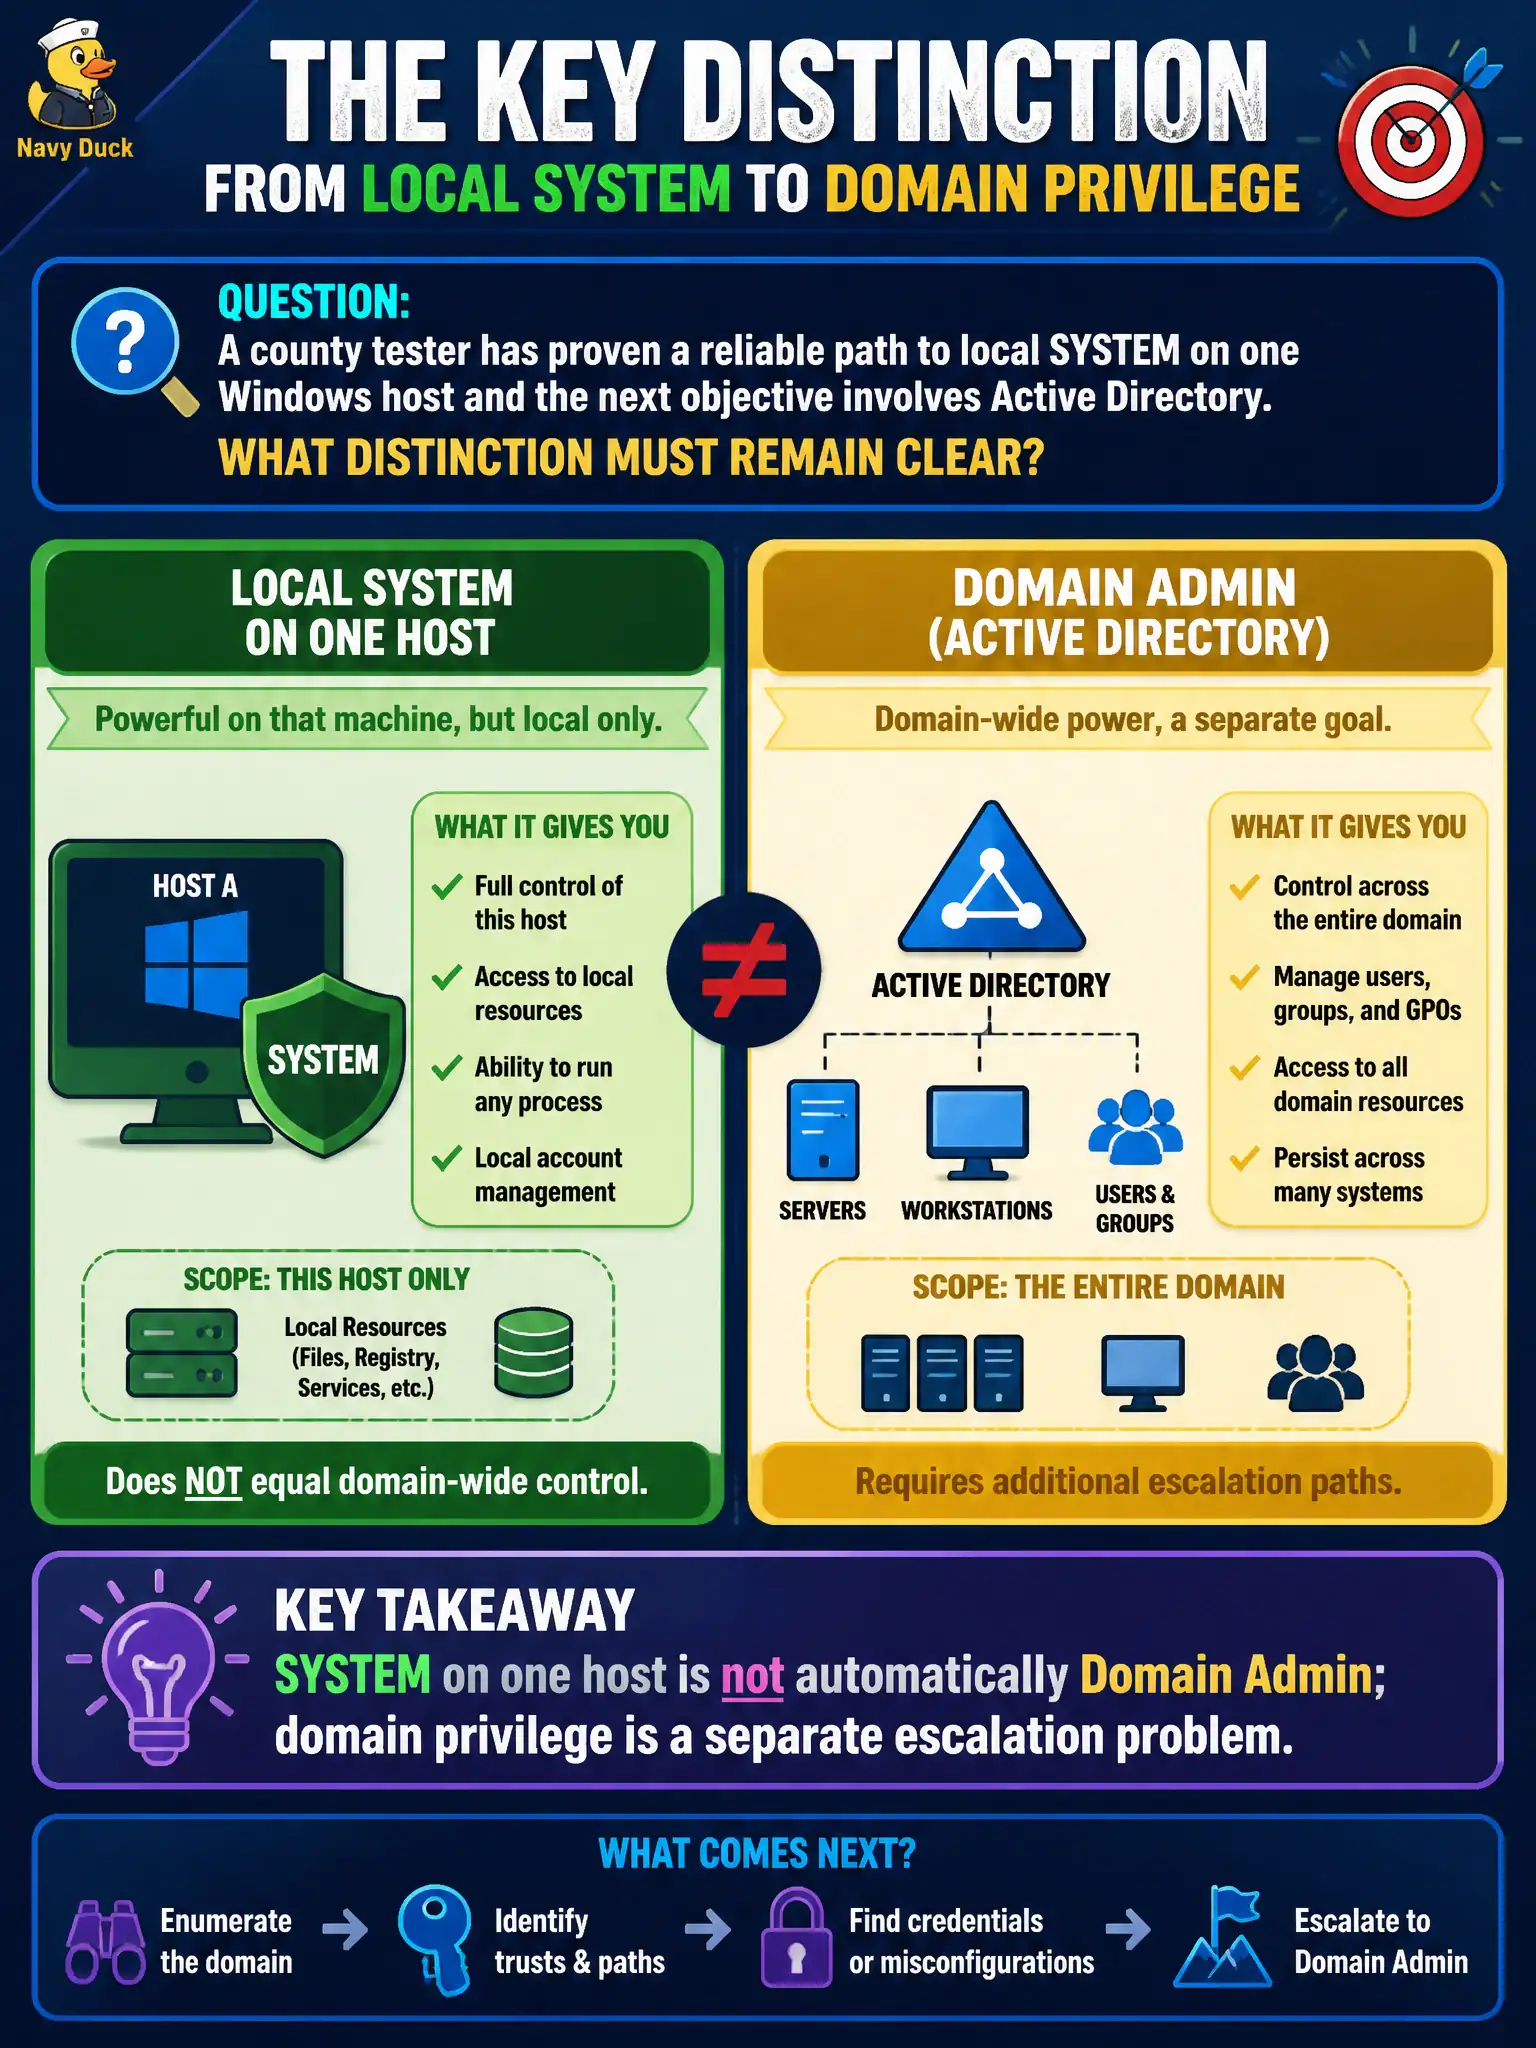
SYSTEM is king of that one castle, not automatically emperor of the whole Active Directory kingdom. You still need a path from that host into domain privilege. Celebrate local SYSTEM, then keep working the AD problem separately.
Full Explanation
After proving a reliable path to local SYSTEM on one county Windows host, Active Directory objectives remain a separate escalation problem: SYSTEM on a member server is not automatically Domain Admin. Keep local host privilege and domain privilege clearly distinguished in planning and reporting.
Local SYSTEM does not include Enterprise Admin rights in every forest by design. Achieving SYSTEM does not end the engagement with guaranteed domain rights. Active Directory privileges are not identical to local Administrators on a workgroup laptop only.
Exam caveat: SYSTEM may unlock host secrets useful for domain attacks, but those are follow-on steps with their own scope and evidence needs.
Operational check: document local SYSTEM proof, then begin domain-oriented enumeration (user context, trusts, delegation themes) without assuming forest control. State residual domain risk separately for county stakeholders. In municipal operations, record the rationale in the engagement notes so future assessors know which control was chosen and which failure modes the rejected options would create for city services. Re-validate after the next maintenance window that the same finding class still applies under the estate's current patch and configuration baseline.