
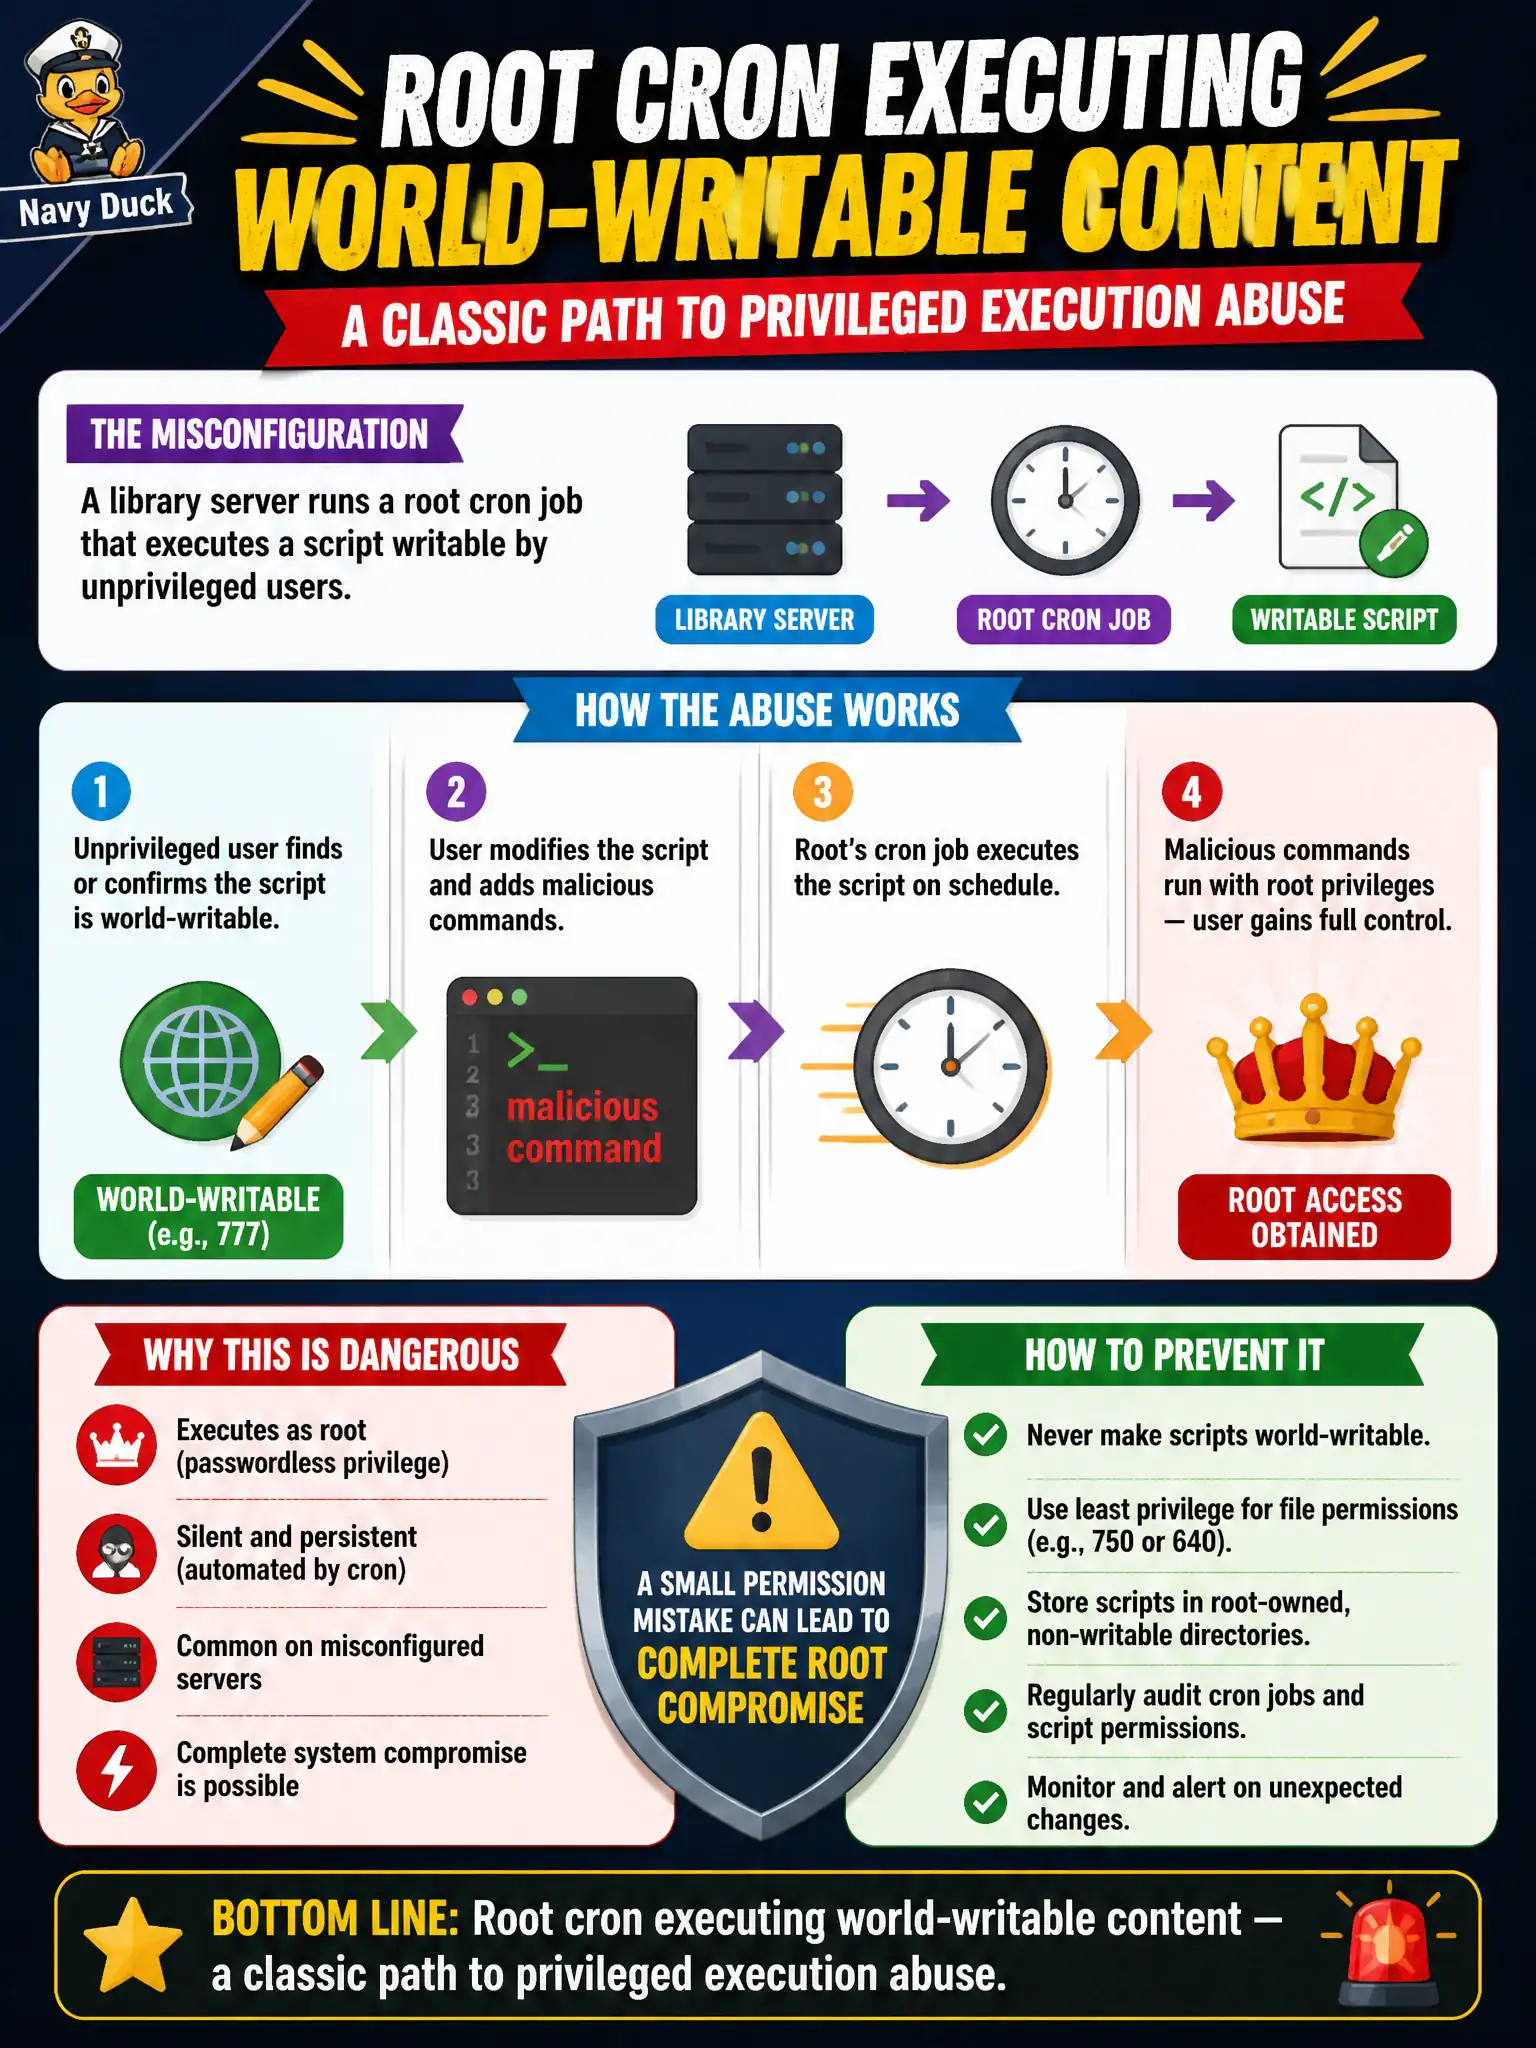
A library server runs a root cron job that executes a script writable by unprivileged users. What misconfiguration class is this?
Select an answer to reveal the explanation.
Short Explanation
If root's nightly chores run a script anyone can rewrite, that is a loaded gift. Writable cron content plus root execution is a textbook Linux misconfig class. Cron absolutely cares who owns and can edit what it runs.
Full Explanation
A library server whose root cron job executes a script writable by unprivileged users presents a classic privileged-execution abuse class: whatever the low-privilege user writes becomes root's next scheduled command stream. This is a permissions and scheduling integrity failure, not a cosmetic preference.
It is not a harmless scheduling preference unrelated to privilege boundaries. Cron on Linux servers does not only run as the invoking desktop user when jobs are defined for root. File permissions are not ignored merely because a job appears in /etc/crontab.
Exam caveat: check both the cron entry and the full writable path chain (script, includes, directories).
Operational check: identify root cron jobs, verify ownership and write ACLs on invoked scripts, and demonstrate unauthorized writability within RoE without deploying destructive payloads. Recommend root-owned, non-group/world-writable maintenance scripts for library systems. In municipal operations, record the rationale in the engagement notes so future assessors know which control was chosen and which failure modes the rejected options would create for city services. Re-validate after the next maintenance window that the same finding class still applies under the estate's current patch and configuration baseline.