
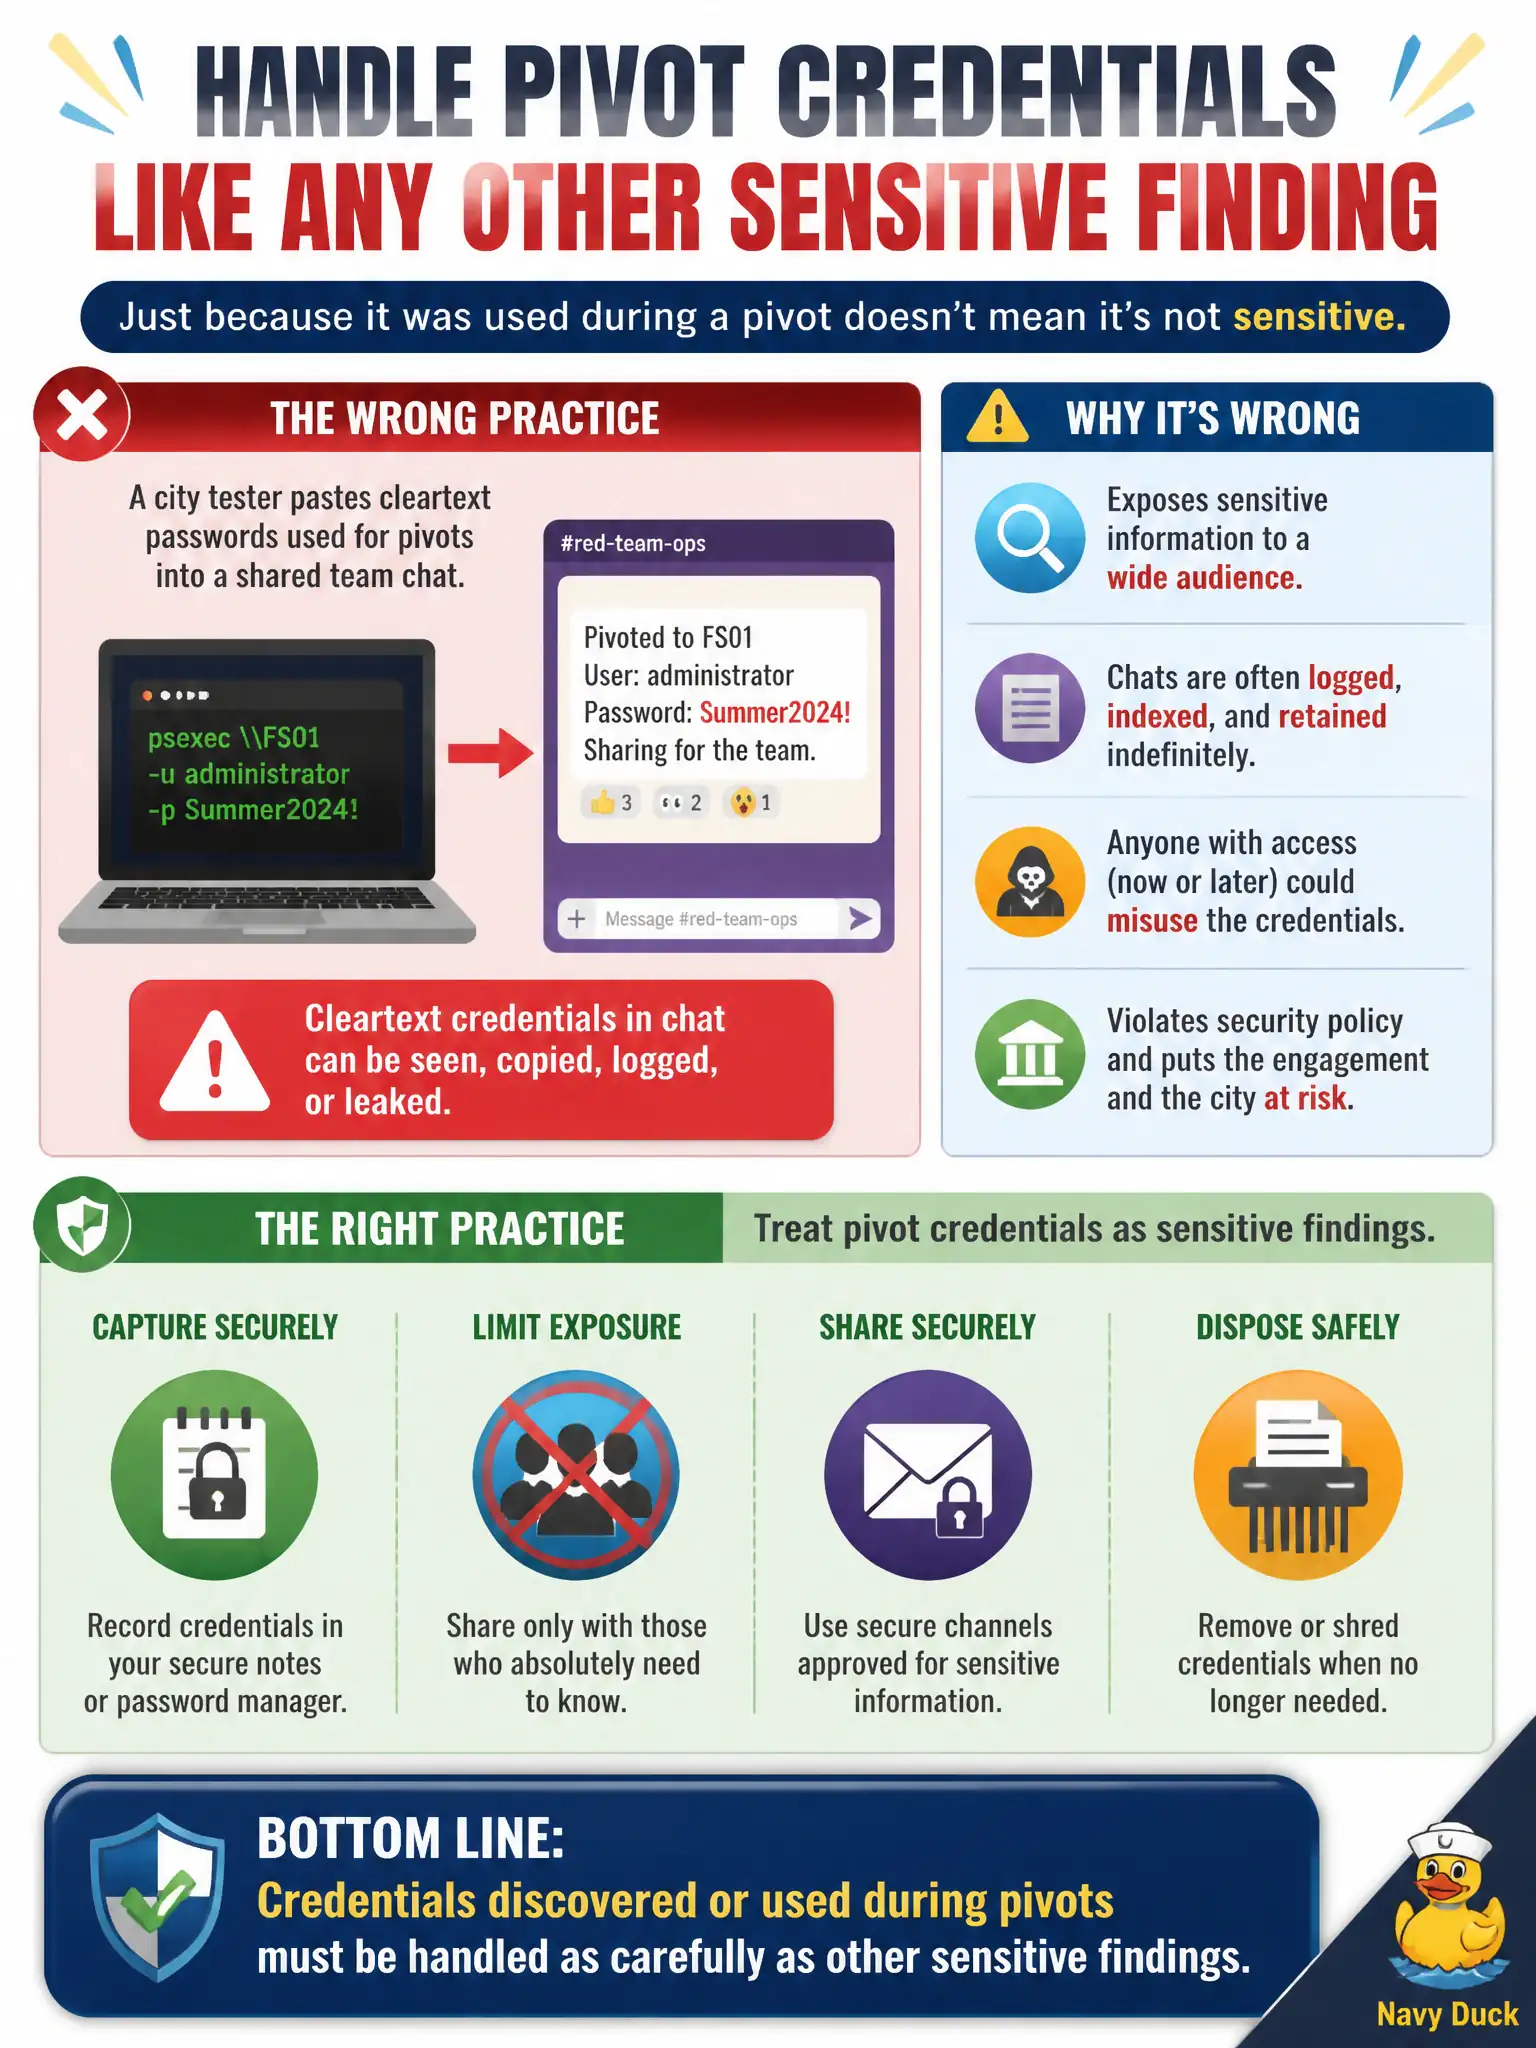
A city tester pastes cleartext passwords used for pivots into a shared team chat. What is wrong with that practice?
Select an answer to reveal the explanation.
Short Explanation
Passwords are not hallway gossip. Dumping cleartext pivot creds into shared chat is like taping the master key to the break-room fridge. Treat those secrets with the same care you would give anything that lands in the final report.
Full Explanation
Pasting cleartext passwords used for pivots into a shared city team chat is wrong because credentials discovered or used during pivots must be handled as carefully as other sensitive findings. Shared chat is not the required vault for engagement secrets. Cleartext pivot passwords in chat do not “improve SOC detection by design”; they create insider and log-retention exposure. Mid-pivot credentials do not deserve less protection than final report secrets—they often enable the same blast radius. Exam caveat: secret handling applies throughout the engagement lifecycle. Operational check: move pivot secrets into the approved password vault or encrypted appendix workflow, redact chat if exposure already occurred, rotate affected municipal credentials when required, and brief the team on the handling rule. In municipal operations, record the rationale in the engagement notes so future testers and city defenders understand which approach was chosen and which failure modes the rejected options would create for civic services. Re-validate the same judgment after the next change window so the control still holds under the city’s current tooling, identity posture, and RoE amendments. Keep secret material and session artifacts in the approved vaulted workflow rather than chat paste or unprotected tickets used by mixed municipal teams.