
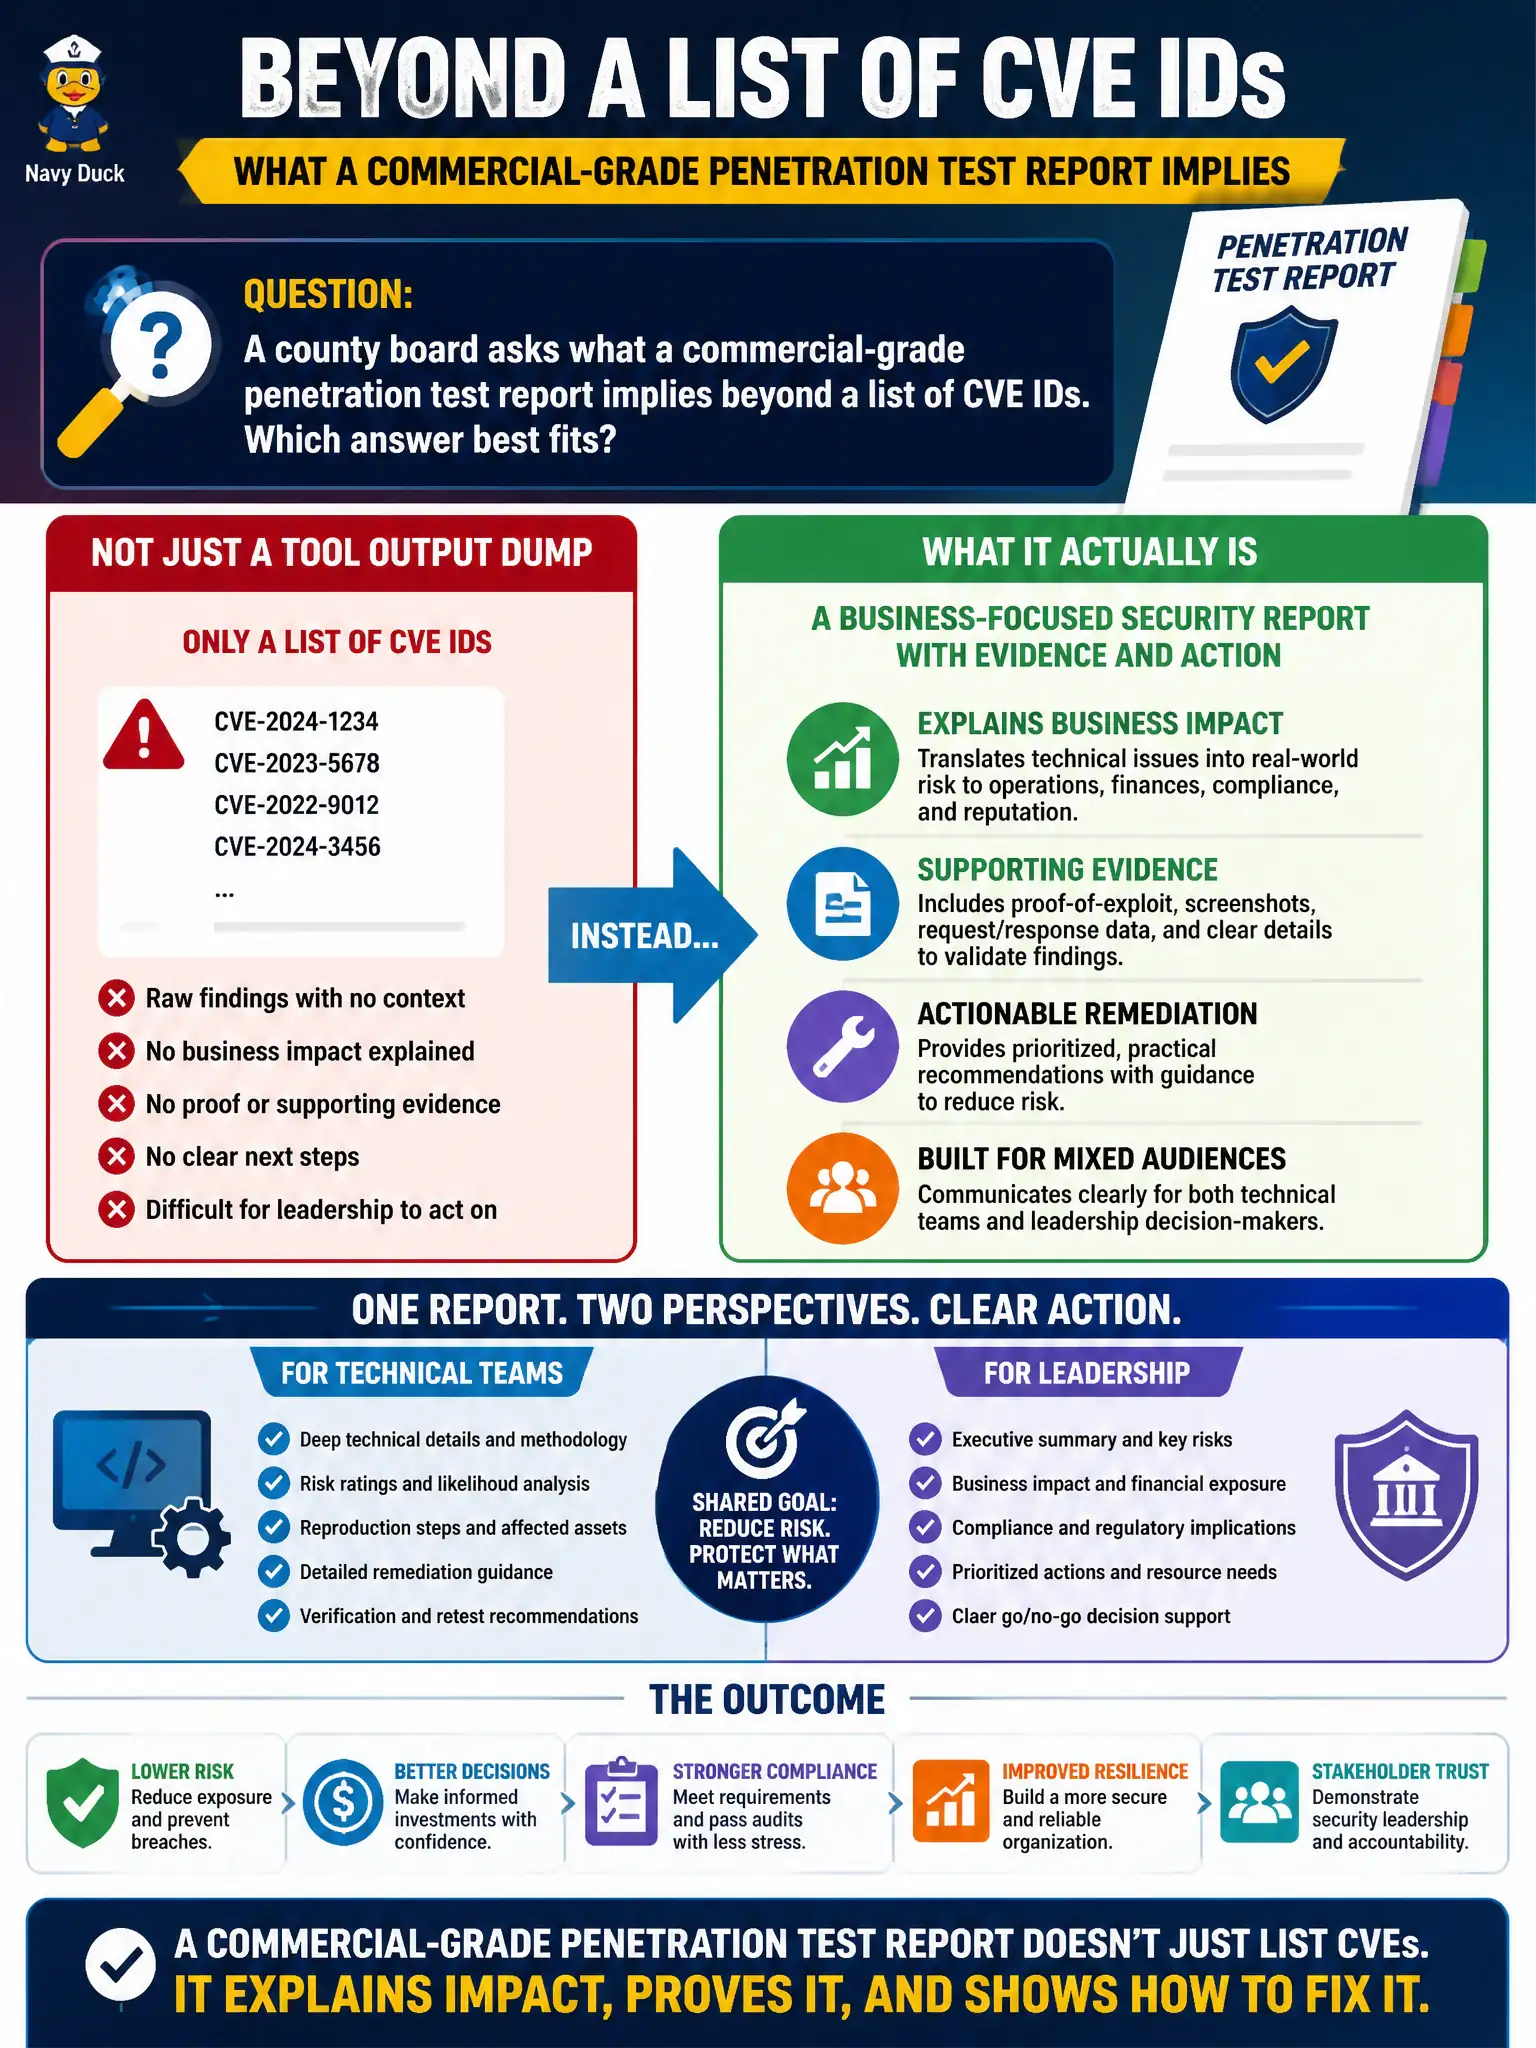
A county board asks what a commercial-grade penetration test report implies beyond a list of CVE IDs. Which answer best fits?
Select an answer to reveal the explanation.
Short Explanation
A CVE laundry list is a receipt; a commercial report is the full trip summary. Leaders need impact and next steps, not just IDs from a tool. Evidence plus clear fixes is what 'commercial-grade' really means.
Full Explanation
A commercial-grade penetration test report for a county board implies more than a list of CVE IDs. It explains business impact with supporting evidence and actionable remediation for mixed technical and leadership audiences—not only a tool output dump. Pasting raw scanner exports without narrative or fix guidance is unfinished work. Omitting remediation forces administrators to invent unrelated projects. Listing only CVE numbers because 'executives refuse context' fails board-level decision needs and under-serves system owners. Exam caveat: severity should reflect municipal asset criticality and exposure, not scanner defaults alone. Operational check: ensure each confirmed finding includes affected civic asset, evidence, impact narrative, likelihood/severity rationale, and concrete remediation or compensating controls suitable for both engineers and county leadership. Document the rationale in the municipal engagement notes so later civic responders know which boundary was honored and which failure modes the rejected options would create for public services. Document the rationale in the municipal engagement notes so later civic responders know which boundary was honored and which failure modes the rejected options would create for public services.