
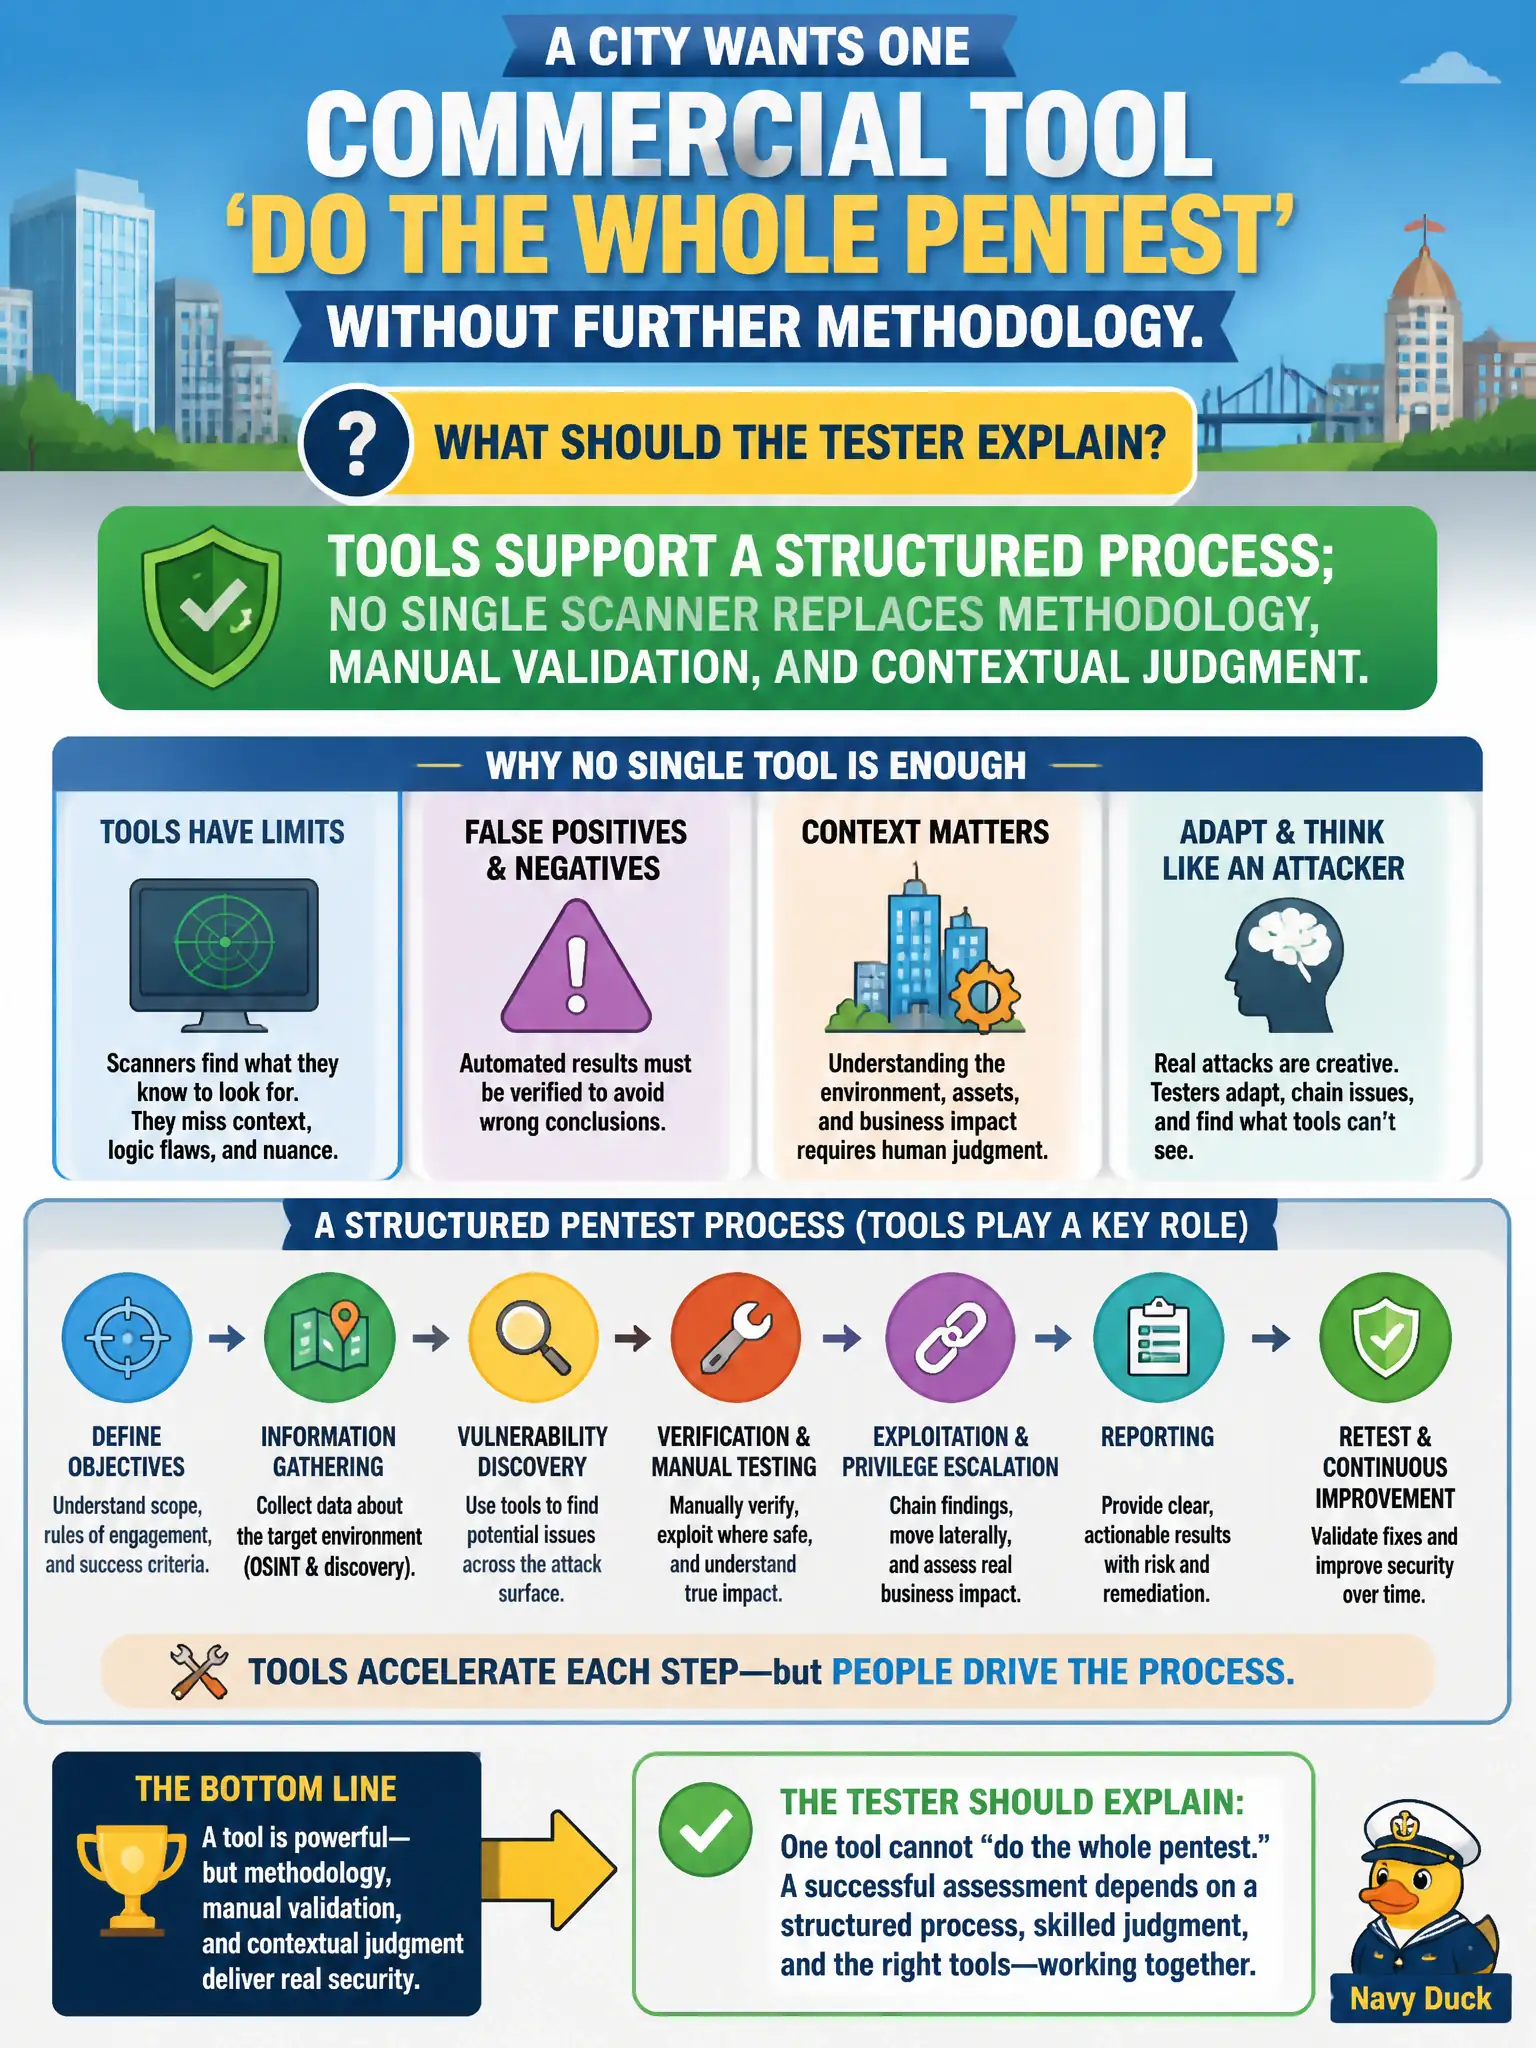
A city wants one commercial tool that will 'do the whole pentest' without further methodology. What should the tester explain?
Select an answer to reveal the explanation.
Short Explanation
A scanner is a metal detector, not the whole security team. It helps, but someone still has to think, validate, and follow a process. There is no magic 'pentest complete' button.
Full Explanation
A city wanting one commercial tool to 'do the whole pentest' needs a clear explanation: tools support a structured process, but no single scanner replaces methodology, manual validation, and contextual judgment. An executive PDF export from an automated license tier is still a vulnerability-assessment-style output unless humans validate exploitability and business impact. Marketing an AI button does not make methodology obsolete. Manual validation is not discouraged for procurement speed; it is how false positives are removed and chained risks are proven on municipal systems. Exam caveat: CPTS emphasizes process over tool worship—know why a finding matters, not only which plugin fired. Operational check: map tool outputs into a testing workflow that includes scoping, enumeration, manual verification, authorized exploitation where allowed, and narrative reporting tied to city assets and owners. Document the rationale in the municipal engagement notes so later civic responders know which boundary was honored and which failure modes the rejected options would create for public services. Document the rationale in the municipal engagement notes so later civic responders know which boundary was honored and which failure modes the rejected options would create for public services.