
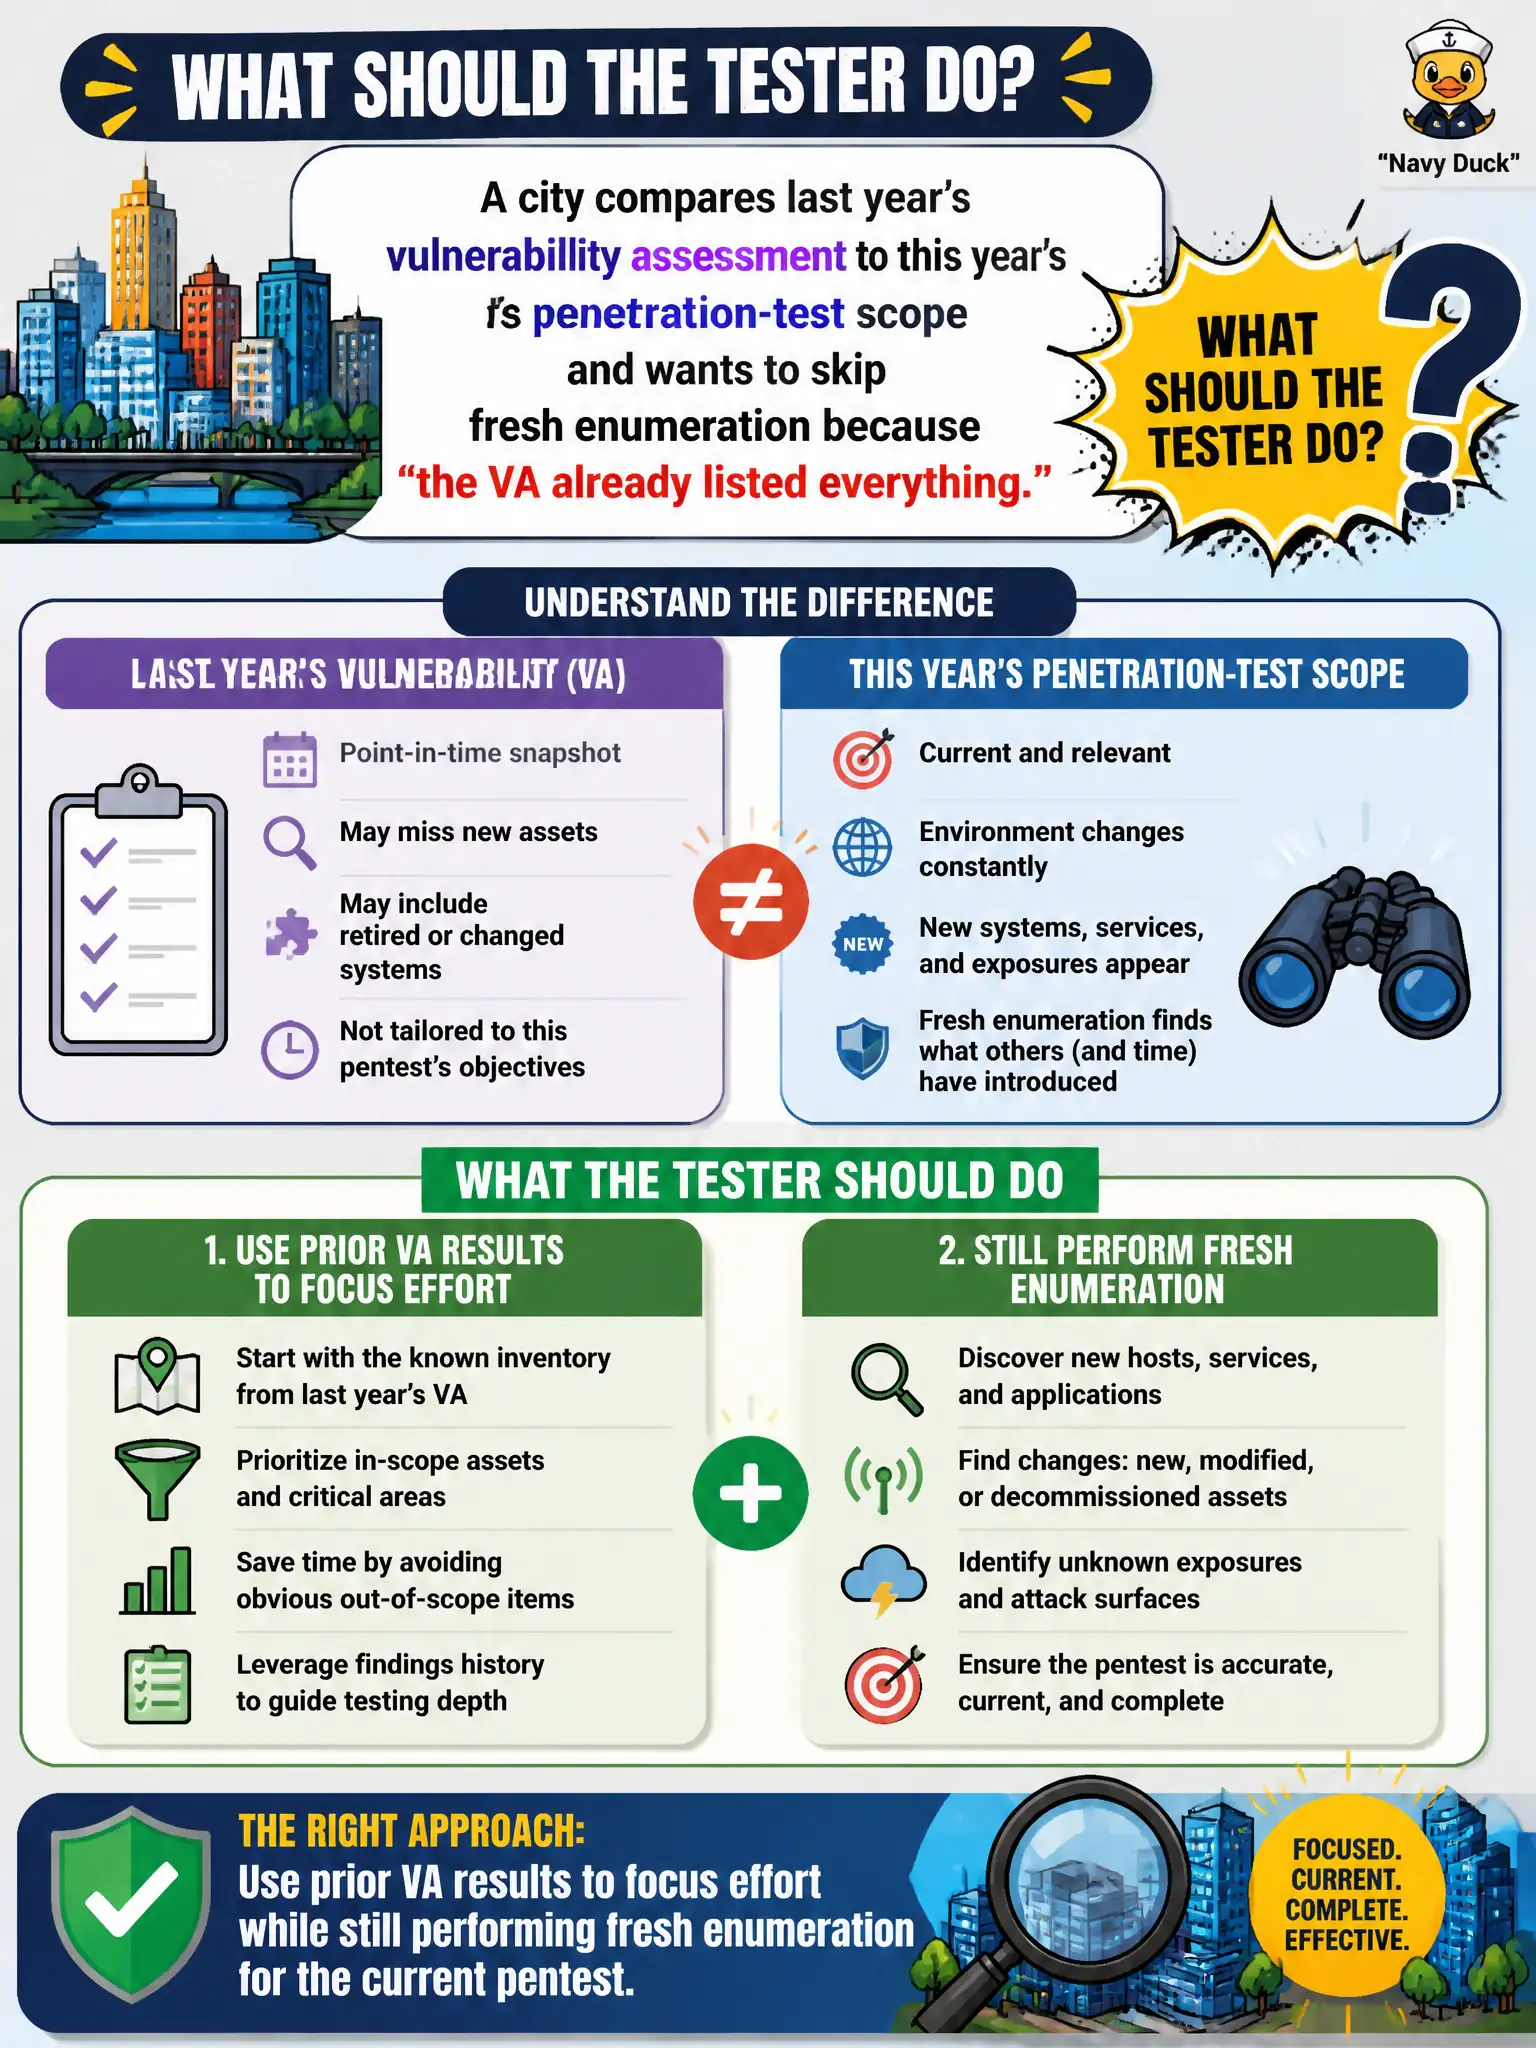
A city compares last year's vulnerability assessment to this year's penetration-test scope and wants to skip fresh enumeration because "the VA already listed everything." What should the tester do?
Select an answer to reveal the explanation.
Short Explanation
Old VA notes are a helpful trail map, not a reason to leave the binoculars at home. Networks change—look again, then lean harder where last year already hurt.
Full Explanation
If a city wants to skip fresh enumeration because last year's VA 'already listed everything,' the tester should use prior VA results to focus effort while still performing fresh enumeration for the current pentest. Reusing last year's VA verbatim as the only attack map misses drift. Destroying the prior VA wastes useful context. Limiting the pentest to informational findings from the old report alone under-scopes current risk. Exam caveat: prior reports may contain outdated severity or fixed issues—re-validate before relying on them. Operational check: import prior high-value leads, re-discover live hosts and services, note changes since last year, and build the current attack plan from fresh municipal enumeration plus focused follow-up on historical hotspots. Document the rationale in the municipal engagement notes so later civic responders know which boundary was honored and which failure modes the rejected options would create for public services. Document the rationale in the municipal engagement notes so later civic responders know which boundary was honored and which failure modes the rejected options would create for public services. Document the rationale in the municipal engagement notes so later civic responders know which boundary was honored and which failure modes the rejected options would create for public services.