
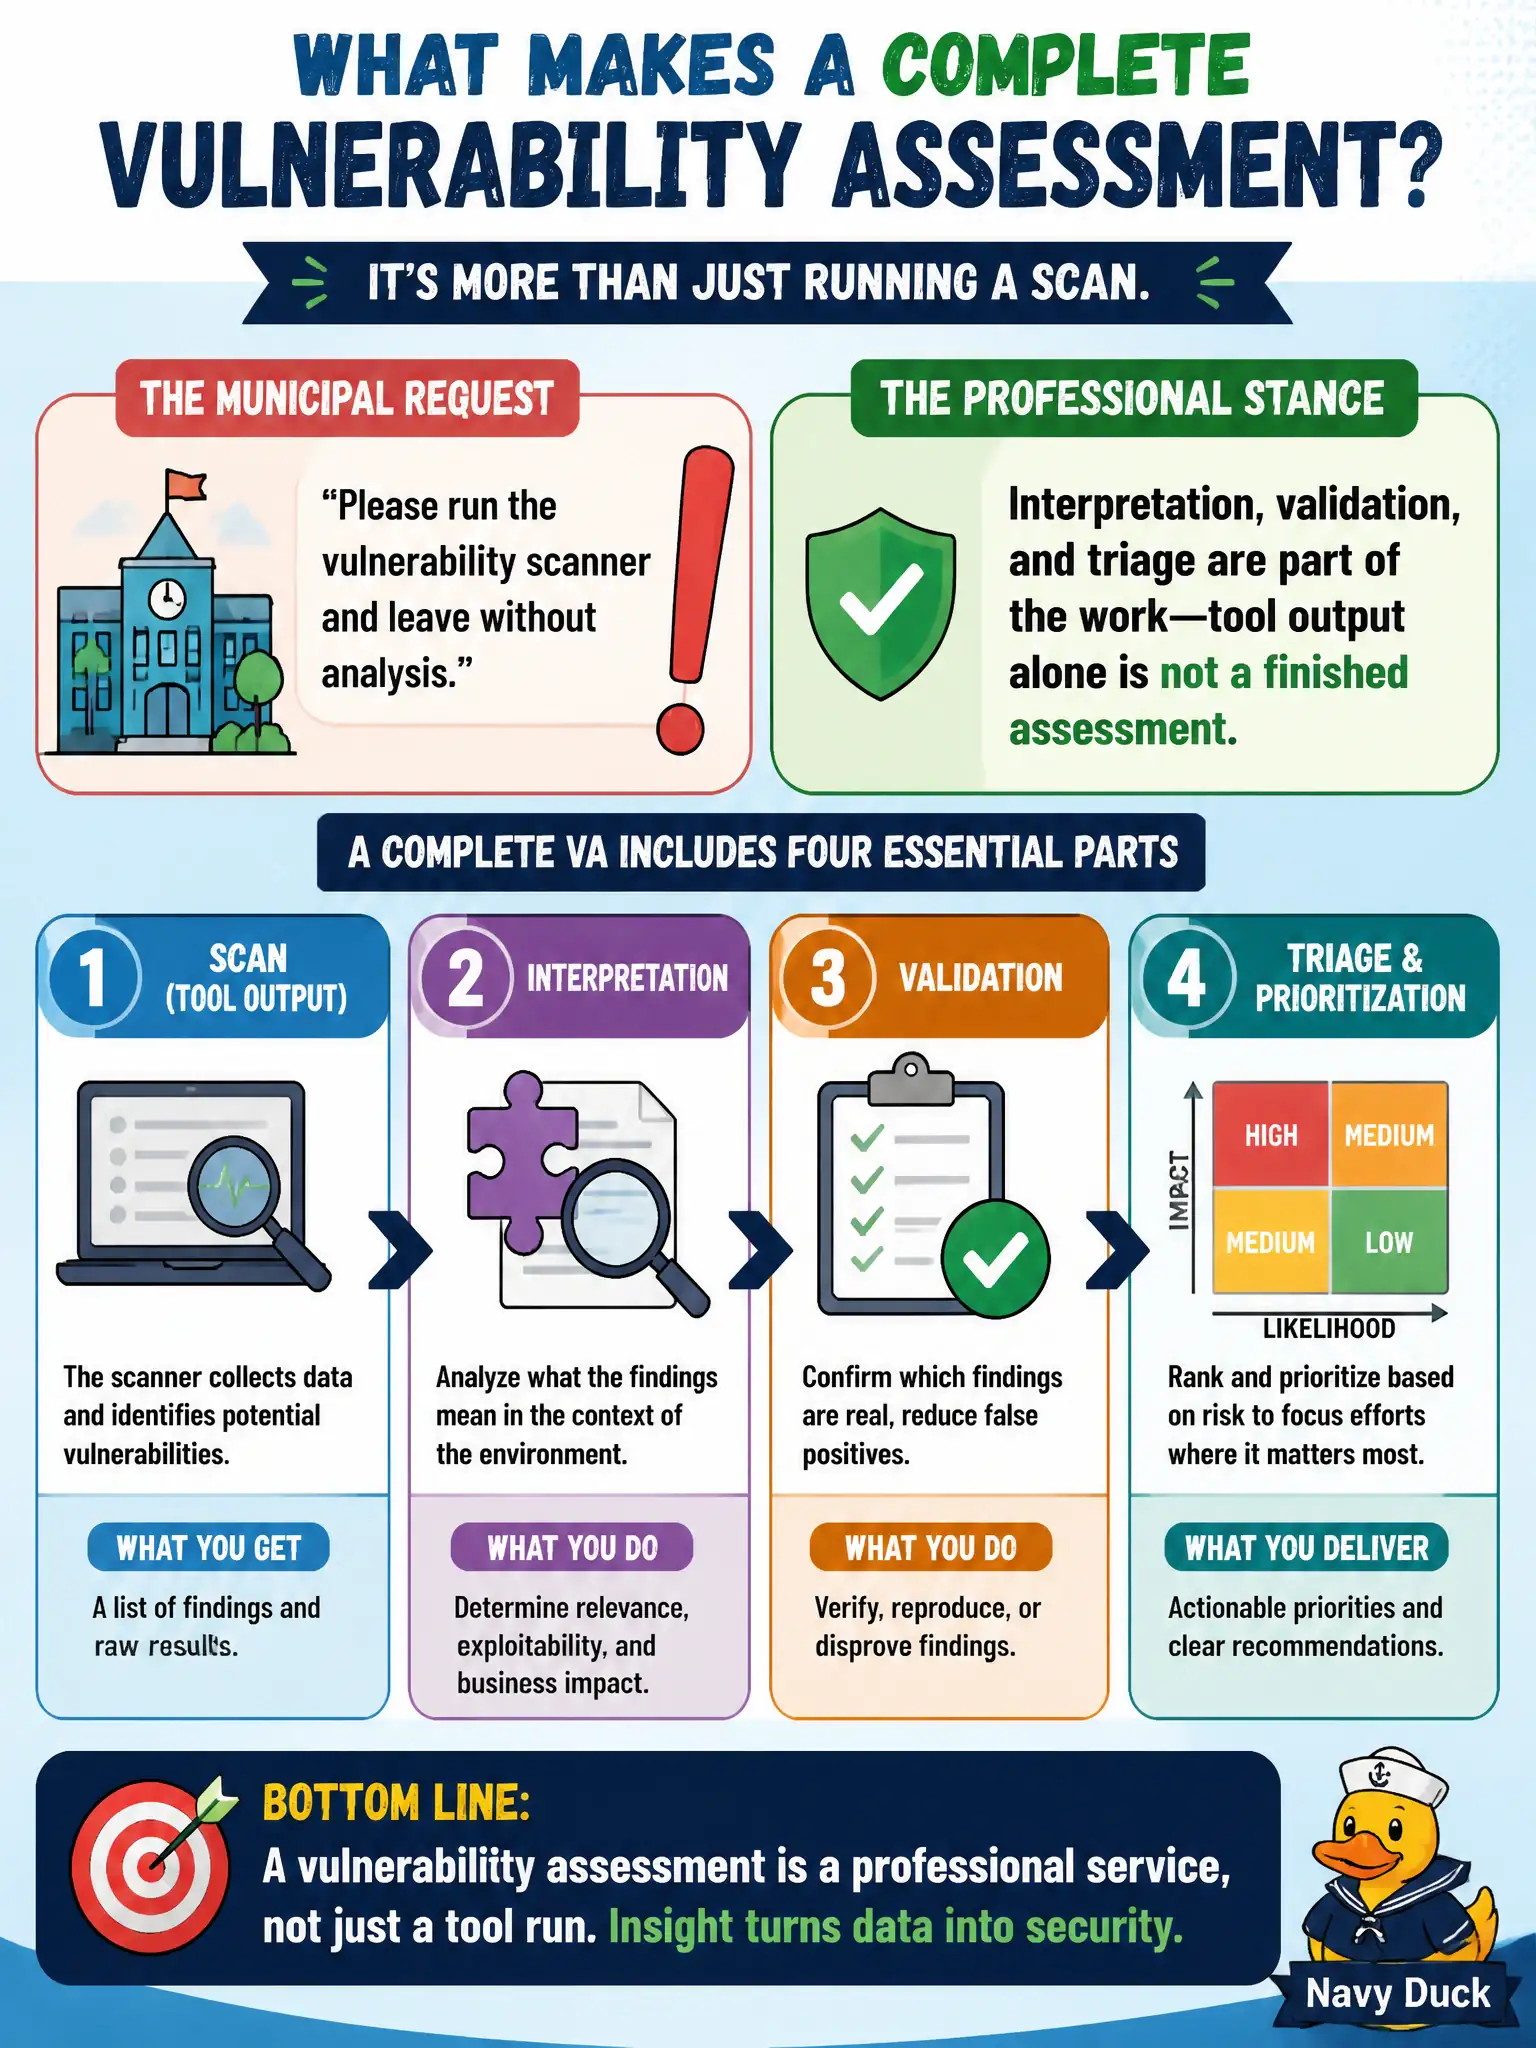
A municipal team asks the tester to run the vulnerability scanner and leave without analysis. What professional stance fits a complete VA?
Select an answer to reveal the explanation.
Short Explanation
Hitting "scan" and walking out is like dumping a blood panel on the desk with no doctor. Someone still has to read it, toss the false alarms, and say what matters.
Full Explanation
When a municipal team asks the tester to run the vulnerability scanner and leave without analysis, the professional stance for a complete VA is that interpretation, validation, and triage are part of the work—tool output alone is not a finished assessment. Dumping raw XML and calling analysis solely the client's problem abdicates the service. Refusing all scanning and delivering an empty report helps no one. Encrypting results and withholding them until a second contract is signed is an unfair bait-and-switch if analysis was in scope. Exam caveat: state clearly in the SOW what validation depth is included. Operational check: validate high-impact findings, remove or mark false positives, triage by civic business risk, and deliver a narrative VA report—not only scanner files—to the municipality. Document the rationale in the municipal engagement notes so later civic responders know which boundary was honored and which failure modes the rejected options would create for public services. Document the rationale in the municipal engagement notes so later civic responders know which boundary was honored and which failure modes the rejected options would create for public services. Document the rationale in the municipal engagement notes so later civic responders know which boundary was honored and which failure modes the rejected options would create for public services.