
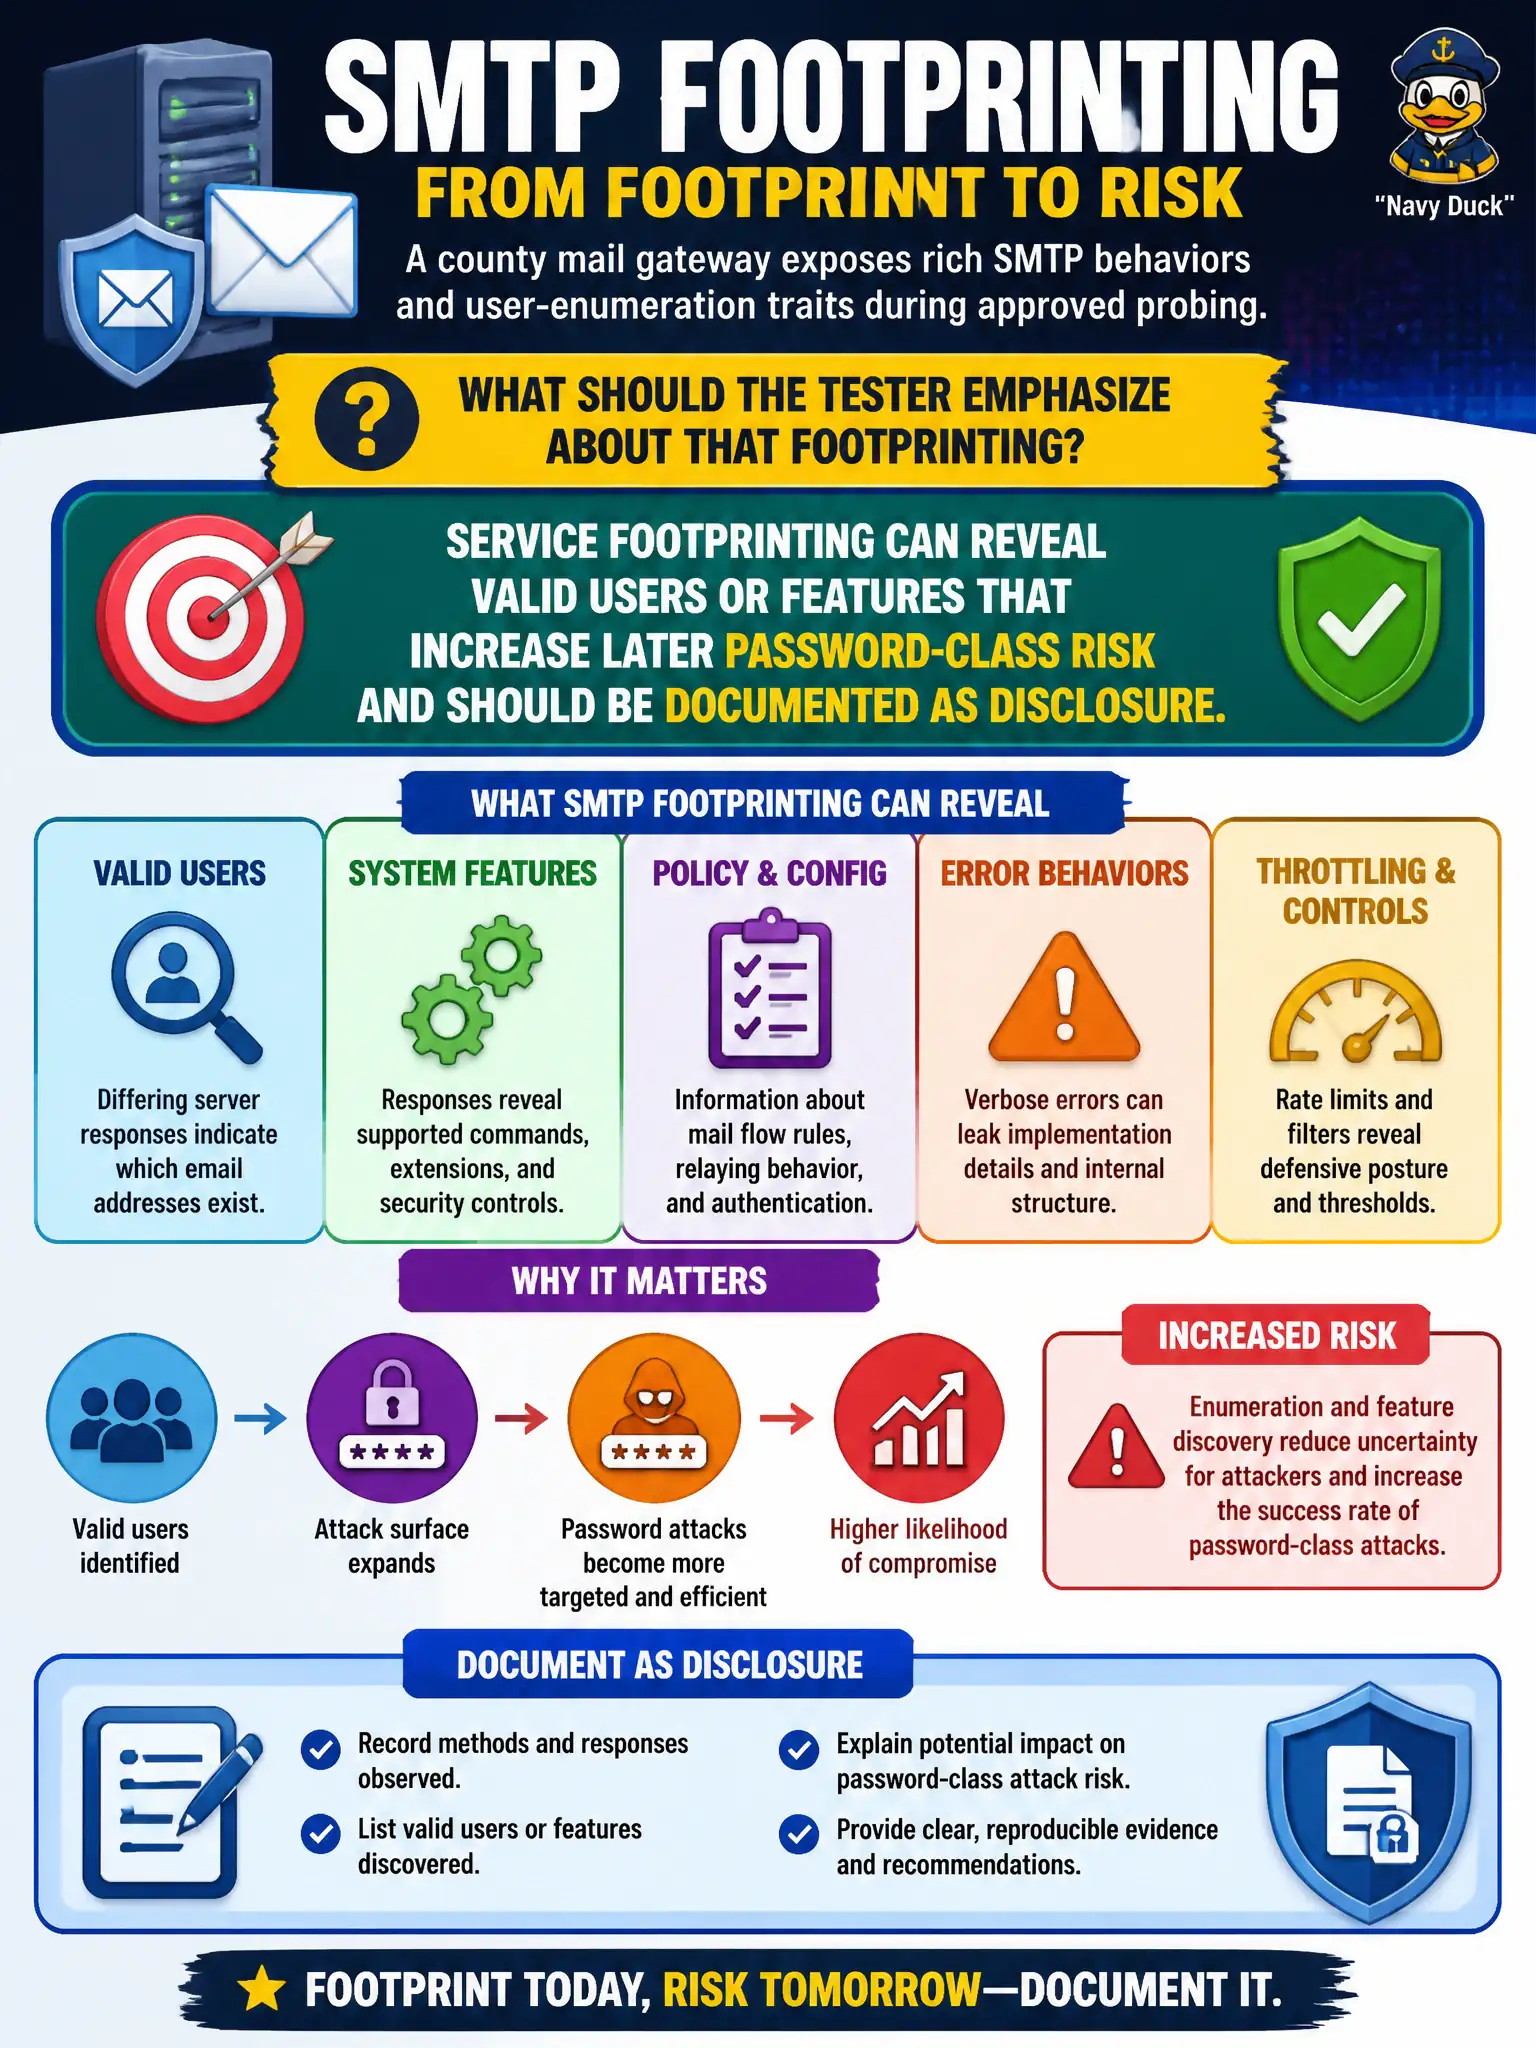
A county mail gateway exposes rich SMTP behaviors and user-enumeration traits during approved probing. What should the tester emphasize about that footprinting?
Select an answer to reveal the explanation.
Short Explanation
A chatty mail gateway is like a receptionist who confirms which names are real. That helps later password guessing far more than people admit. Write it up as disclosure — you do not need a stolen inbox to prove the risk exists.
Full Explanation
When a county mail gateway exposes rich SMTP behaviors and user-enumeration traits during approved probing, service footprinting can reveal valid users or features that increase later password-class risk and should be documented as disclosure. Behavioral clues remain relevant even without a full mailbox dump in the same session. User-enumeration traits on mail services should not be ignored; email remains part of modern attack surface for municipalities. Immediate ransomware deployment is never an appropriate validation step. Exam caveat: some RoEs limit authentication testing—report enumeration even if password attacks are deferred or forbidden. Operational check: record SMTP verbs, response codes, and enumeration evidence; assess exposure of civic user naming patterns; notify contacts if the finding enables targeted attacks against county staff. Document the rationale in the municipal engagement notes so later civic responders know which boundary was honored and which failure modes the rejected options would create for public services. Document the rationale in the municipal engagement notes so later civic responders know which boundary was honored and which failure modes the rejected options would create for public services.