
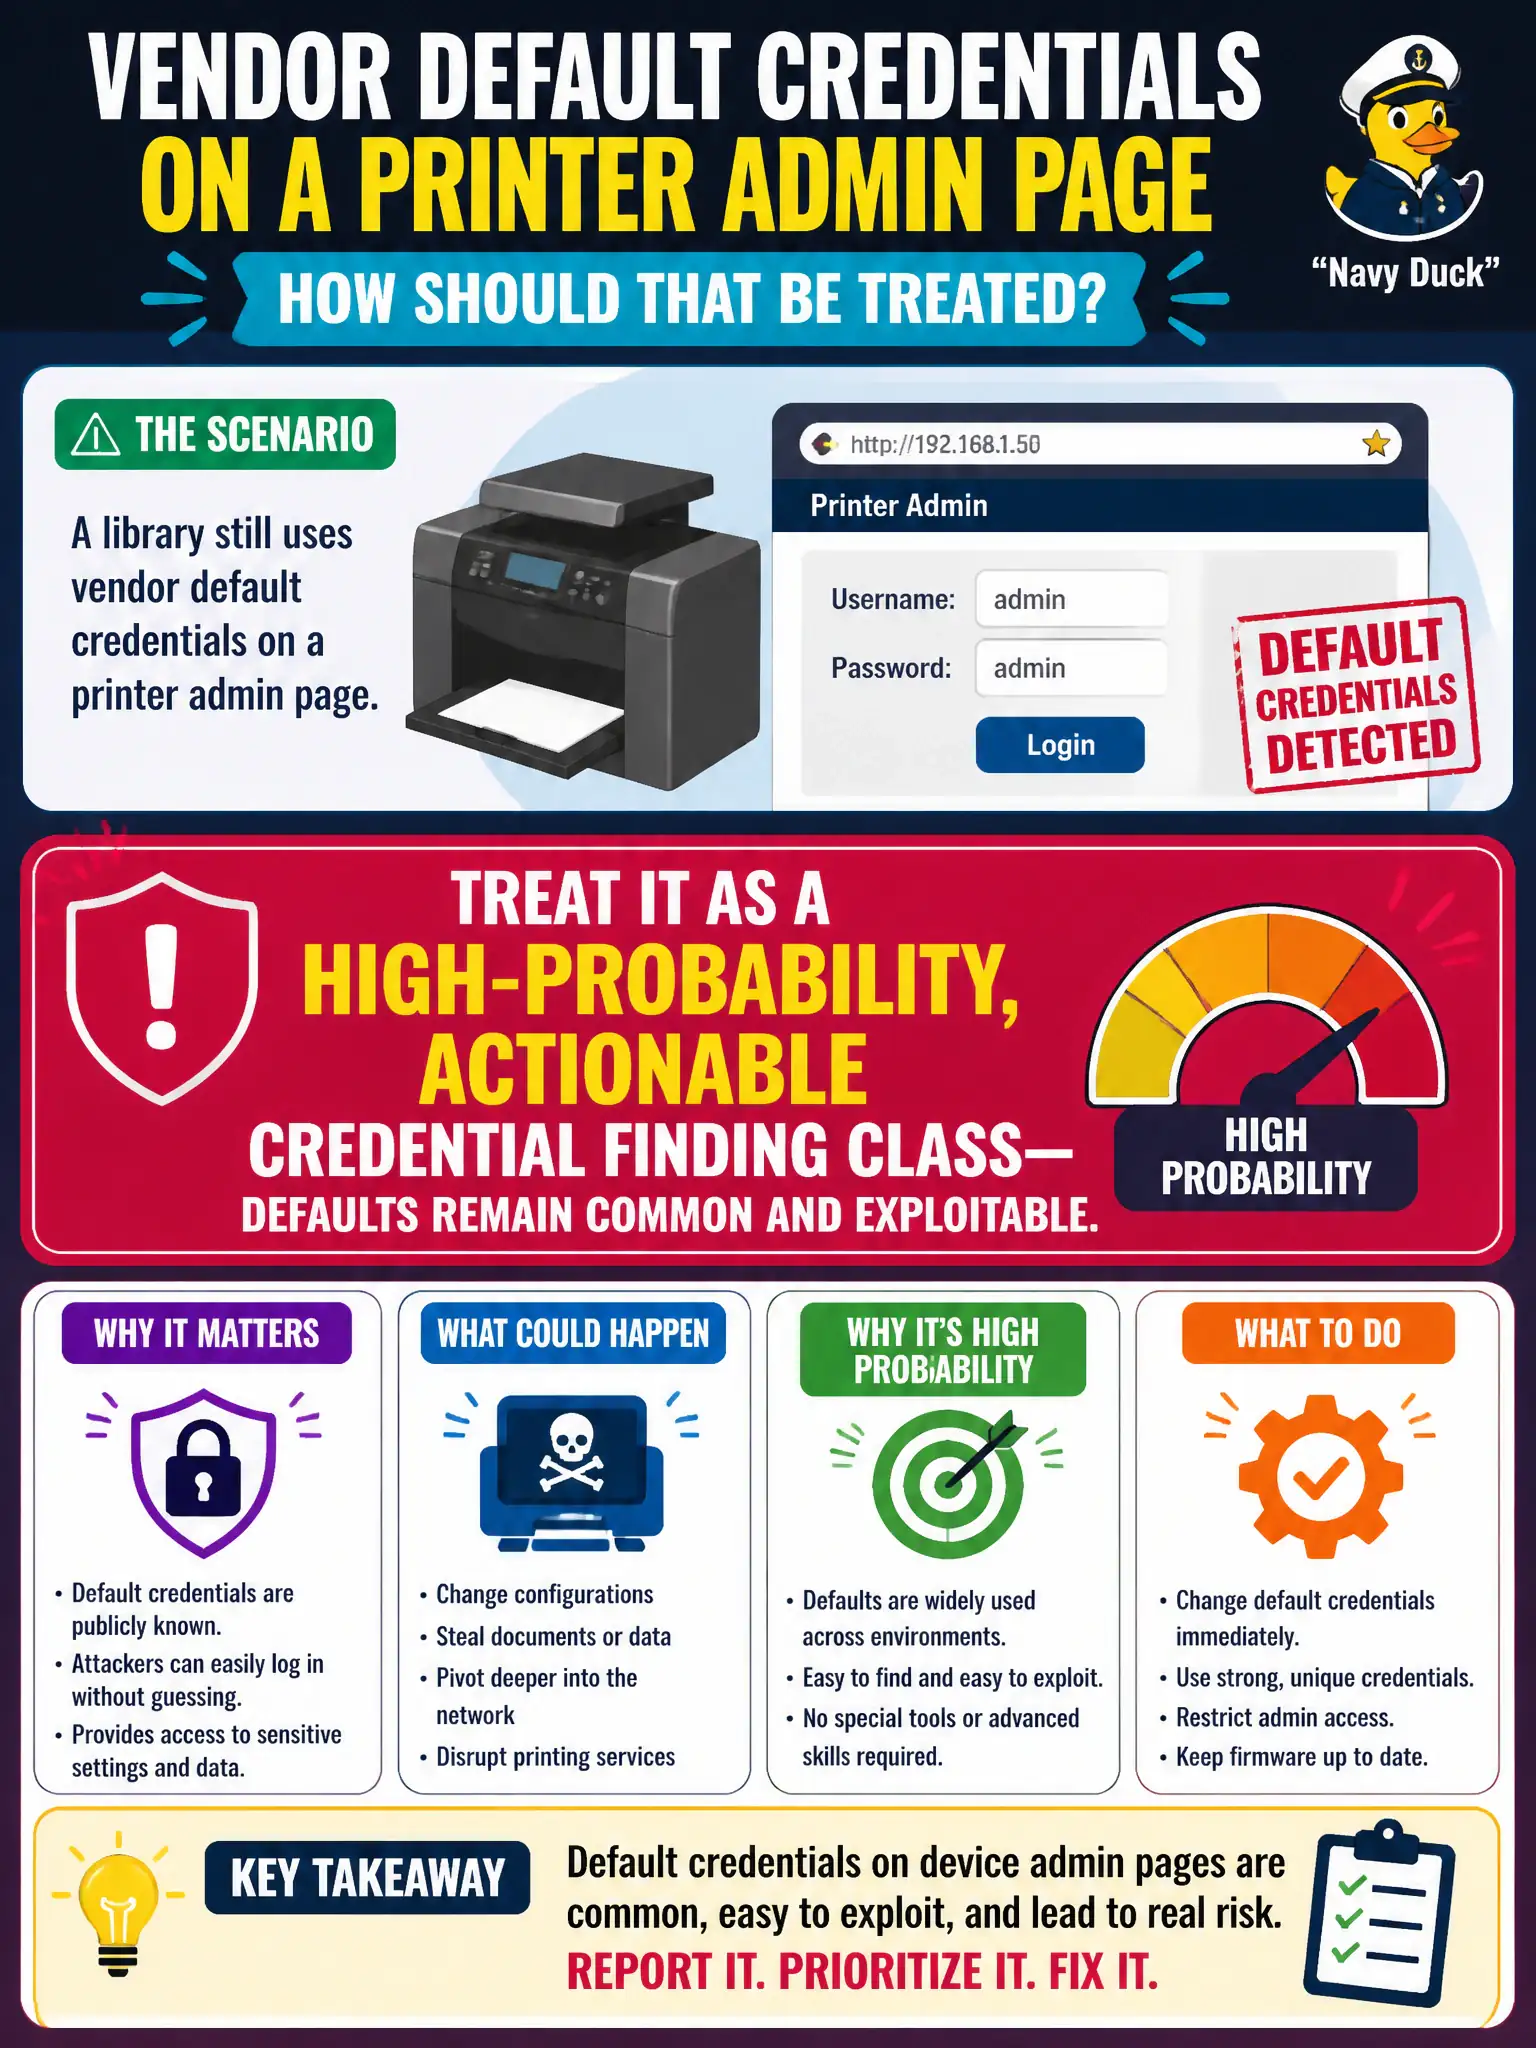
A library still uses vendor default credentials on a printer admin page. How should that be treated?
Select an answer to reveal the explanation.
Short Explanation
Default passwords are the spare key left under the mat—everyone who reads the manual knows where it is. On printers and appliances they show up constantly and they matter. Call it out clearly; don’t shrug it off as ‘just a printer.’
Full Explanation
Vendor default credentials on a library printer admin page should be reported as a high-probability, actionable credential finding class—defaults remain common and exploitable on appliances that cities often forget after install. Ignoring printers because they are supposedly out of scope for credential findings invents a carve-out that RoE rarely states and leaves an easy foothold on the user VLAN. Treating defaults as informational only unless full domain compromise follows underrates standalone risk: printer admin access can expose scans, stored jobs, and lateral paths without needing Domain Admin first. Requiring proof that the vendor still ships those passwords this year before reporting adds an unnecessary research gate; the live system accepted the defaults, which is enough for a municipal finding. Exam caveat: severity still depends on exposure and privilege of the interface, but the finding class itself is classic and reportable. Operational check: document the interface URL or path, show successful auth with the default under RoE, note network exposure relative to staff VLANs, and recommend unique credentials plus management-plane isolation. In municipal operations, record the rationale in the engagement notes so future testers and city defenders understand which approach was chosen and which failure modes the rejected options would create for civic services.