
After cracking one standard user hash, a municipal stakeholder asks whether that automatically equals Domain Admin. What is the correct response?
Select an answer to reveal the explanation.
Short Explanation
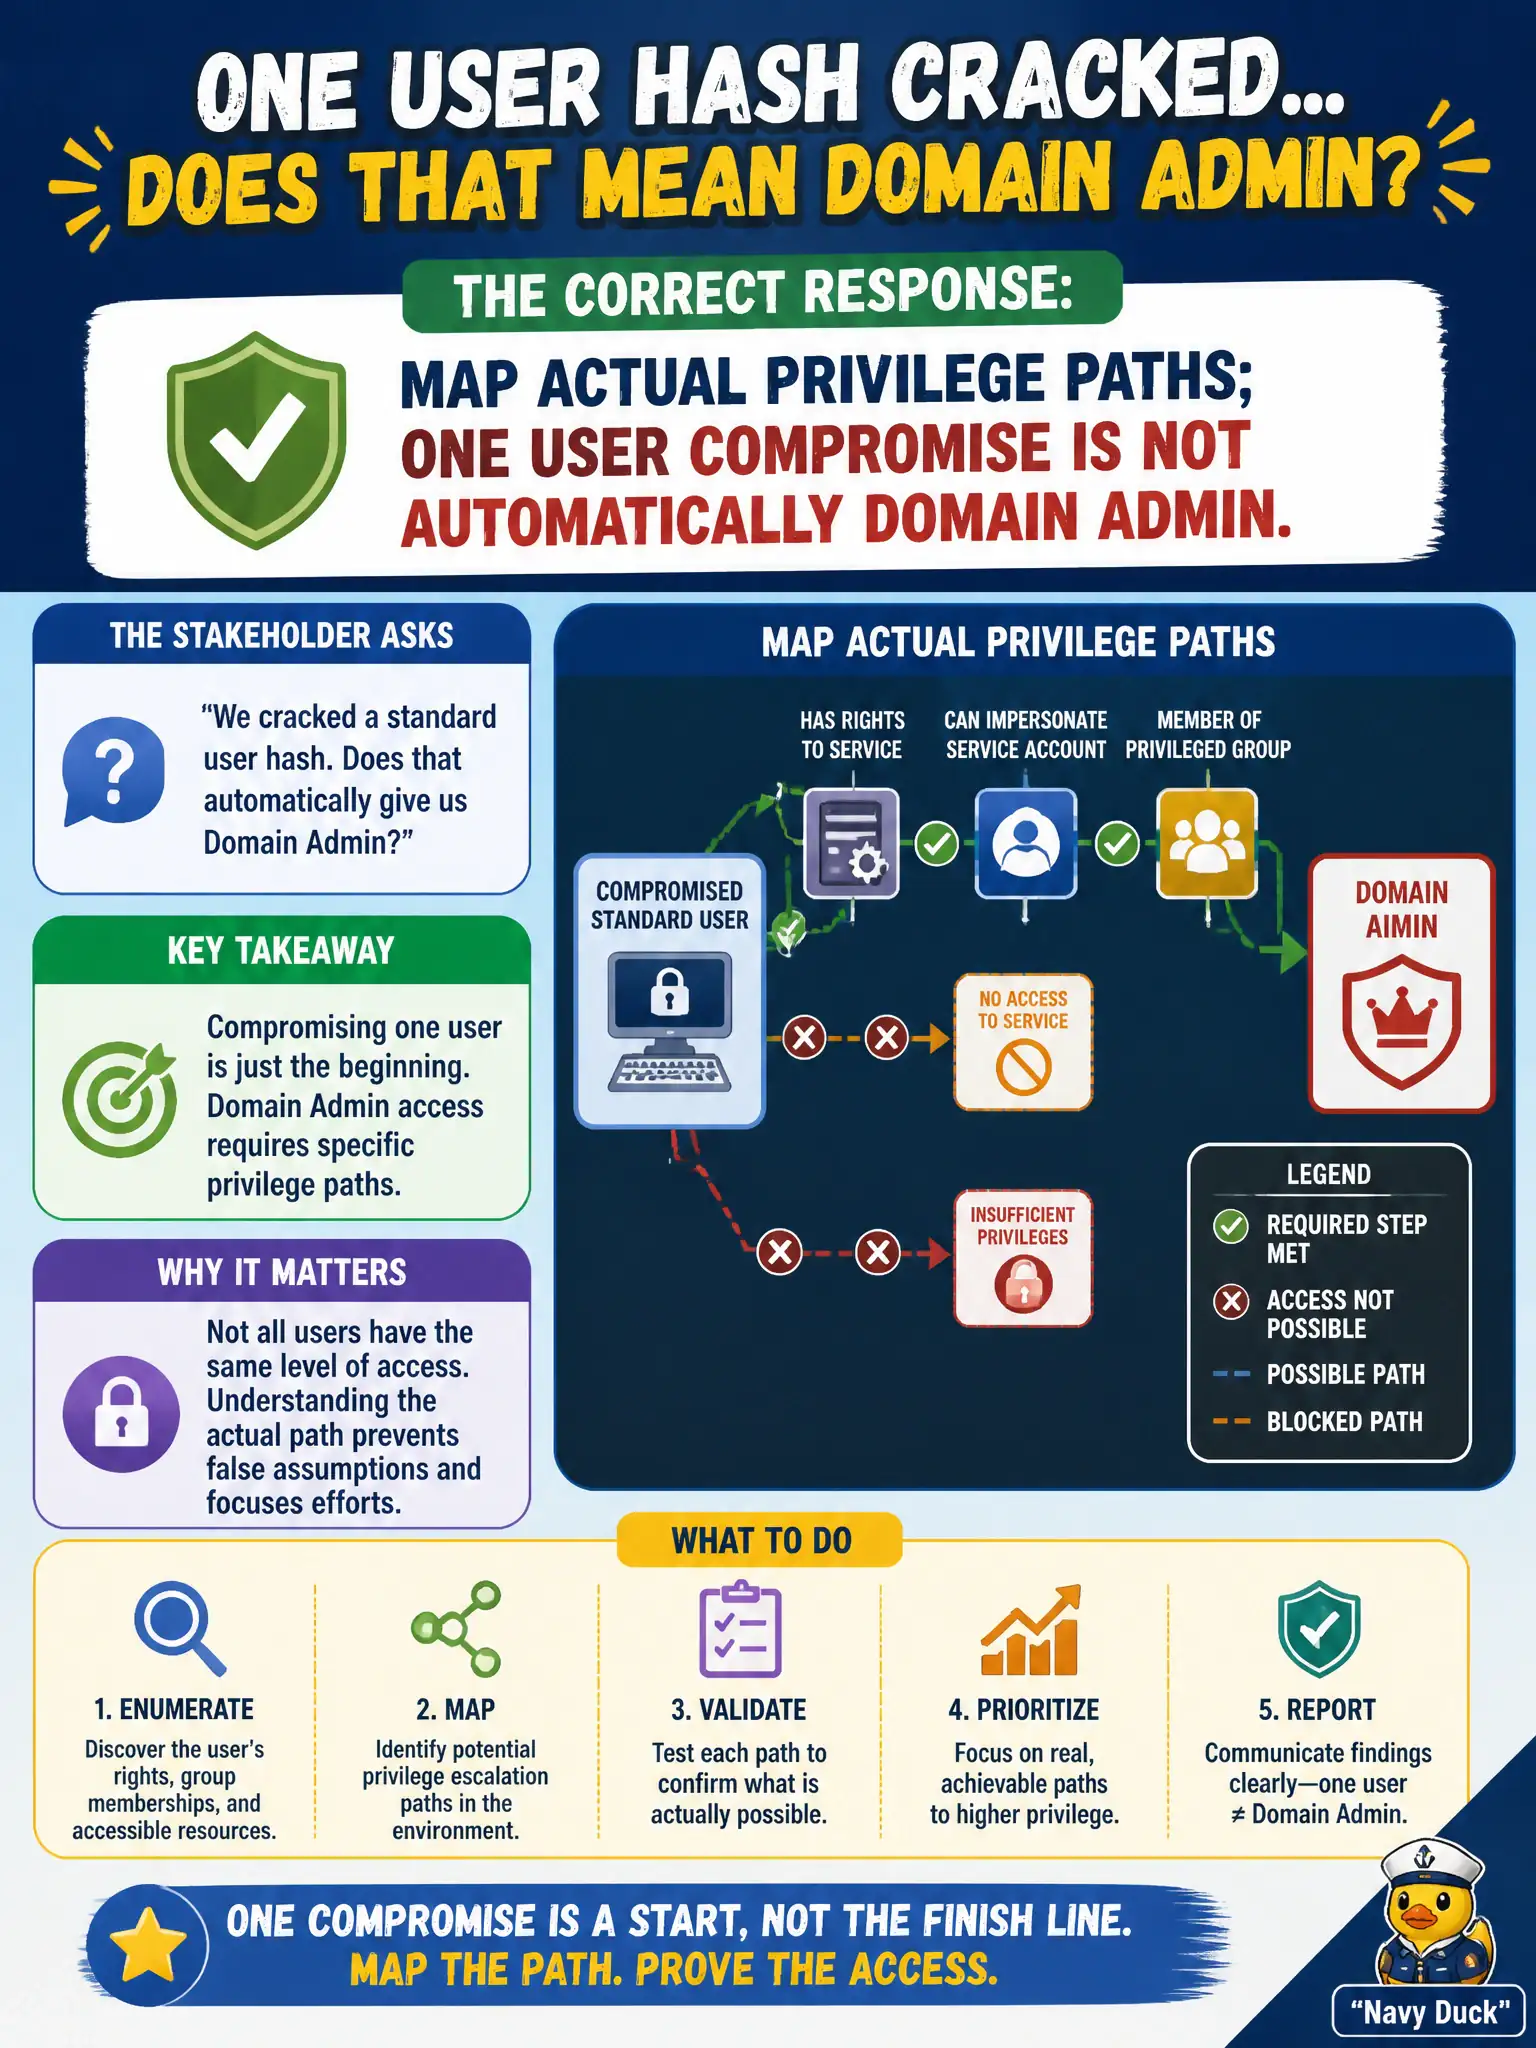
One cracked badge gets you into the lobby — not automatically into the CEO suite. Domain Admin is a path question: groups, ACLs, and hops still matter. Keep mapping instead of assuming the finish line.
Full Explanation
Cracking one standard user hash is progress, not Domain Admin by default. Municipal stakeholders need the accurate methodology answer: map actual privilege paths—group membership, ACLs, delegation, local admin reuse, and trust edges—because one user compromise becomes Domain Admin only when a viable escalation chain exists. CPTS-style engagements prove impact through paths, not through assumptions.
Kerberos design does not grant forest-wide Domain Admin from any cracked user hash. Ending the engagement because a hash cracked abandons path mapping that defines residual risk for city systems. Standard user hashes can absolutely participate in further AD attack paths when those users hold local admin, ACL write, or other footholds—dismissing them is incorrect.
Exam caveat: distinguish credential access from privilege escalation outcomes; report what the account can reach next. Avoid both under-claiming (“users never matter”) and over-claiming (“any hash equals DA”).
Operational check: from the cracked civic user context, enumerate effective group membership and interesting ACLs, document whether a DA path exists, and stop at objective-proven impact rather than dumping unnecessary secrets.