
A retailer must isolate its cardholder data environment from the rest of the network. An assessor warns that with VLANs on shared switches, a single switch misconfiguration could bridge the zones. Management requires isolation that does not depend on the configuration of shared network devices, regardless of cost. Which approach meets this requirement?
Select an answer to reveal the explanation.
Short Explanation
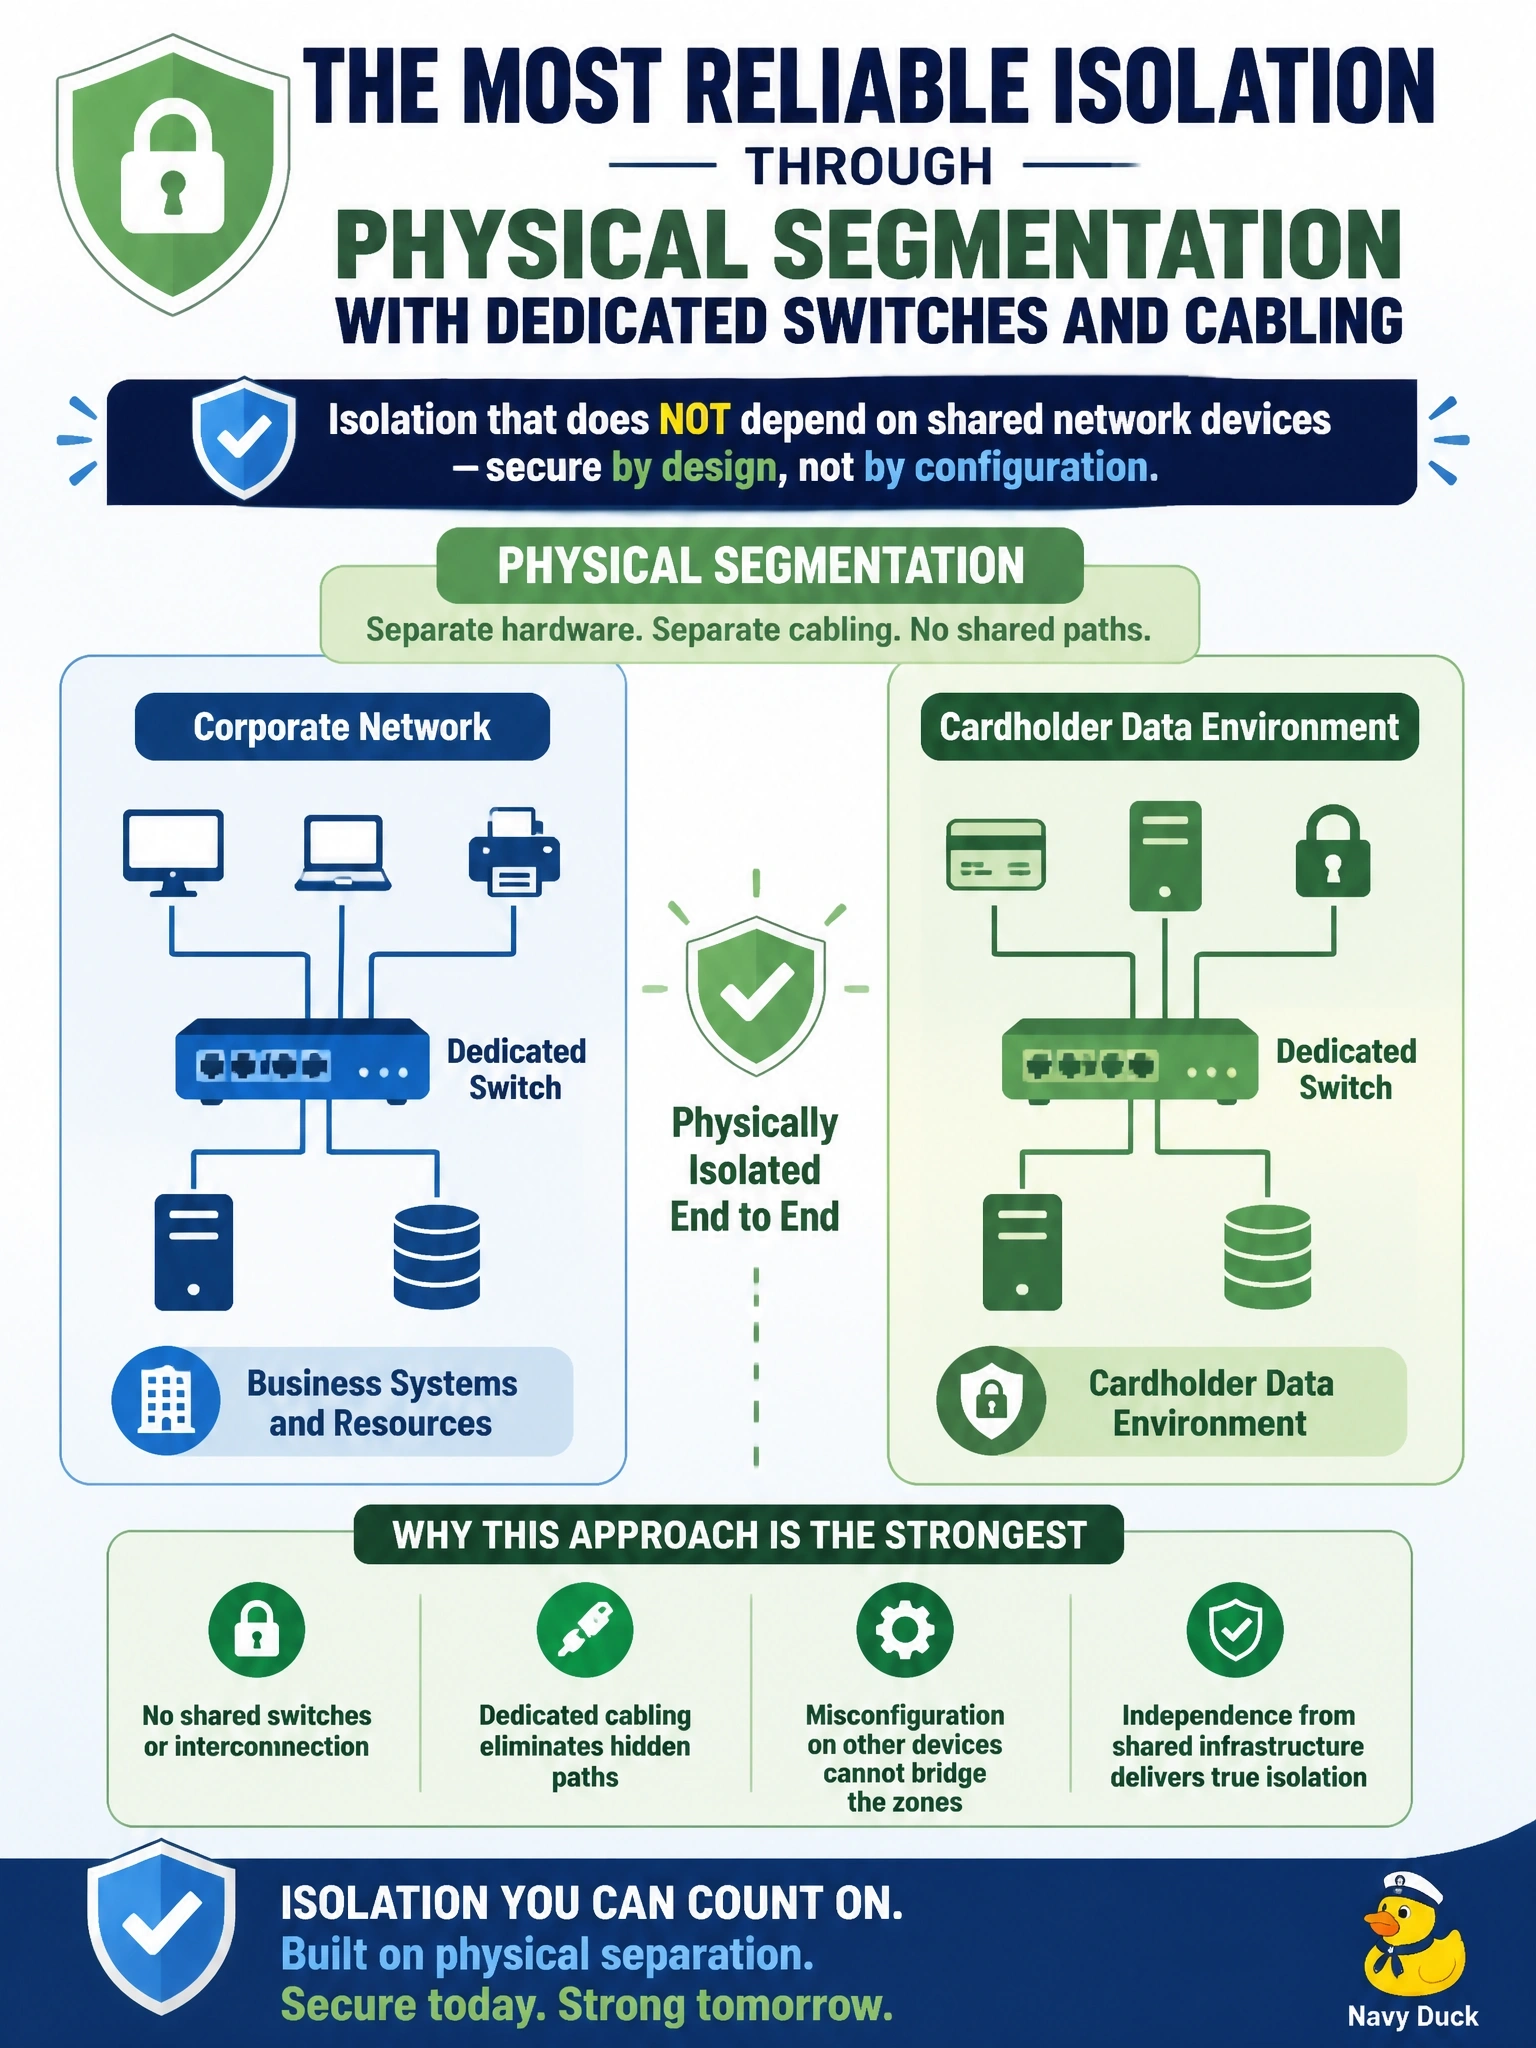
VLANs are like painted lines in a shared parking lot; one wrong paint job and the lines move. If you need separation that doesn't rely on shared gear being configured right, you give the zone its own switches and cables. Don't pick ACLs; they're still riding on the same shared boxes.
Full Explanation
Physical segmentation separates networks using distinct hardware, such as dedicated switches, cabling, and interfaces, so that traffic in one zone cannot reach another unless it passes through a deliberately placed control point like a firewall. Because there is no shared switching fabric, an error in another zone's switch configuration cannot bridge the cardholder data environment to the corporate network. It costs more, which the stem explicitly accepts. Logical segmentation with VLANs on shared switches is effective and widely used, but its isolation depends entirely on correct switch configuration, which is precisely the dependency management wants to eliminate. Access control lists between VLANs add filtering, yet they still run on the same shared devices, so a misconfiguration of those devices remains a single point of failure for the separation. Host-based firewalls on servers sharing one VLAN provide defense in depth on each host, but they leave the zones on a common broadcast domain and rely on every host's configuration rather than network separation. Exam caveat: logical segmentation is usually the practical choice, and physical segmentation wins only when the scenario explicitly prioritizes independence from shared device configuration over cost and flexibility. Operational check: document the dedicated hardware, verify that the only path into the zone is through the firewall, and test segmentation from outside.