
Network engineers at a retailer must authenticate to the routers, and the router must authorize each configuration command. Which service fits that device administration?
Select an answer to reveal the explanation.
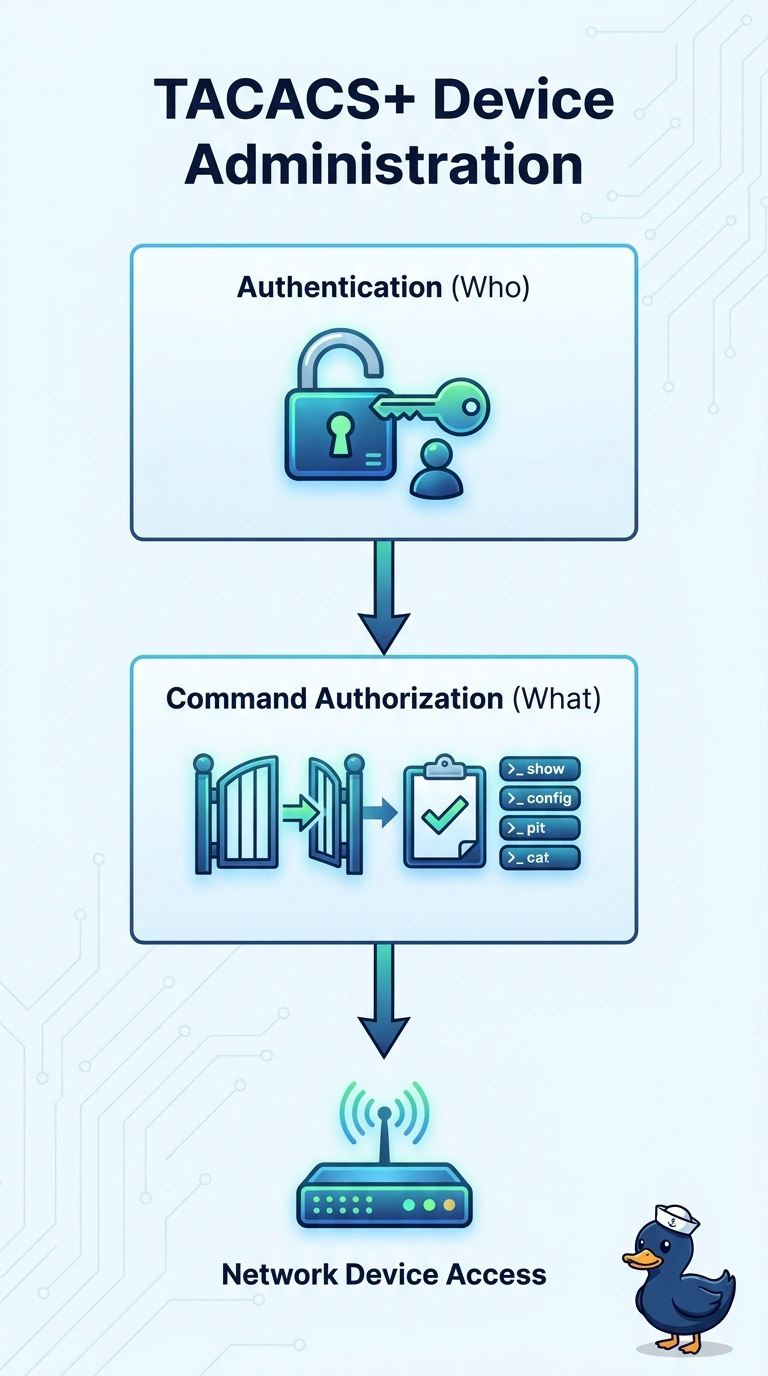
Short Explanation
You are not asking who may join the wireless network. You are asking who may type a command on the router and whether that command is allowed, and that device-administration split is TACACS+. A wireless logon service, a DNS signature, and a drawing of the cables do not authorize the command.
Full Explanation
TACACS+ is the AAA protocol typically used for administrative access to network devices. It can authenticate the engineer and authorize individual commands separately, which matches a retailer that wants both the login and a per-command decision. RADIUS is the AAA protocol typically used for network access, such as wireless or VPN logon. It can authenticate a device admin in some designs, and it is not the protocol this exam associates with separating command authorization. DNSSEC signs DNS records so a resolver can detect tampering. It does not authorize a command typed at a router prompt. A cable diagram documents physical runs. It does not list or enforce command privileges. Exam caveat: the routers still need a fallback local account for the moment the AAA server is unreachable, or you can lock yourself out. Operational check: log in through TACACS+, attempt a command the role should deny, and confirm the router refuses it while an allowed command succeeds. Try the denied command from a second engineer in a different role so you know the authorization is per command and not a dead server.