
Users on a Windows domain connect to a database server with integrated authentication. The security team wants clients to authenticate with time-limited tickets from the domain's key distribution center, with mutual authentication of the server and no password sent to it. Which protocol should be in use?
Select an answer to reveal the explanation.
Short Explanation
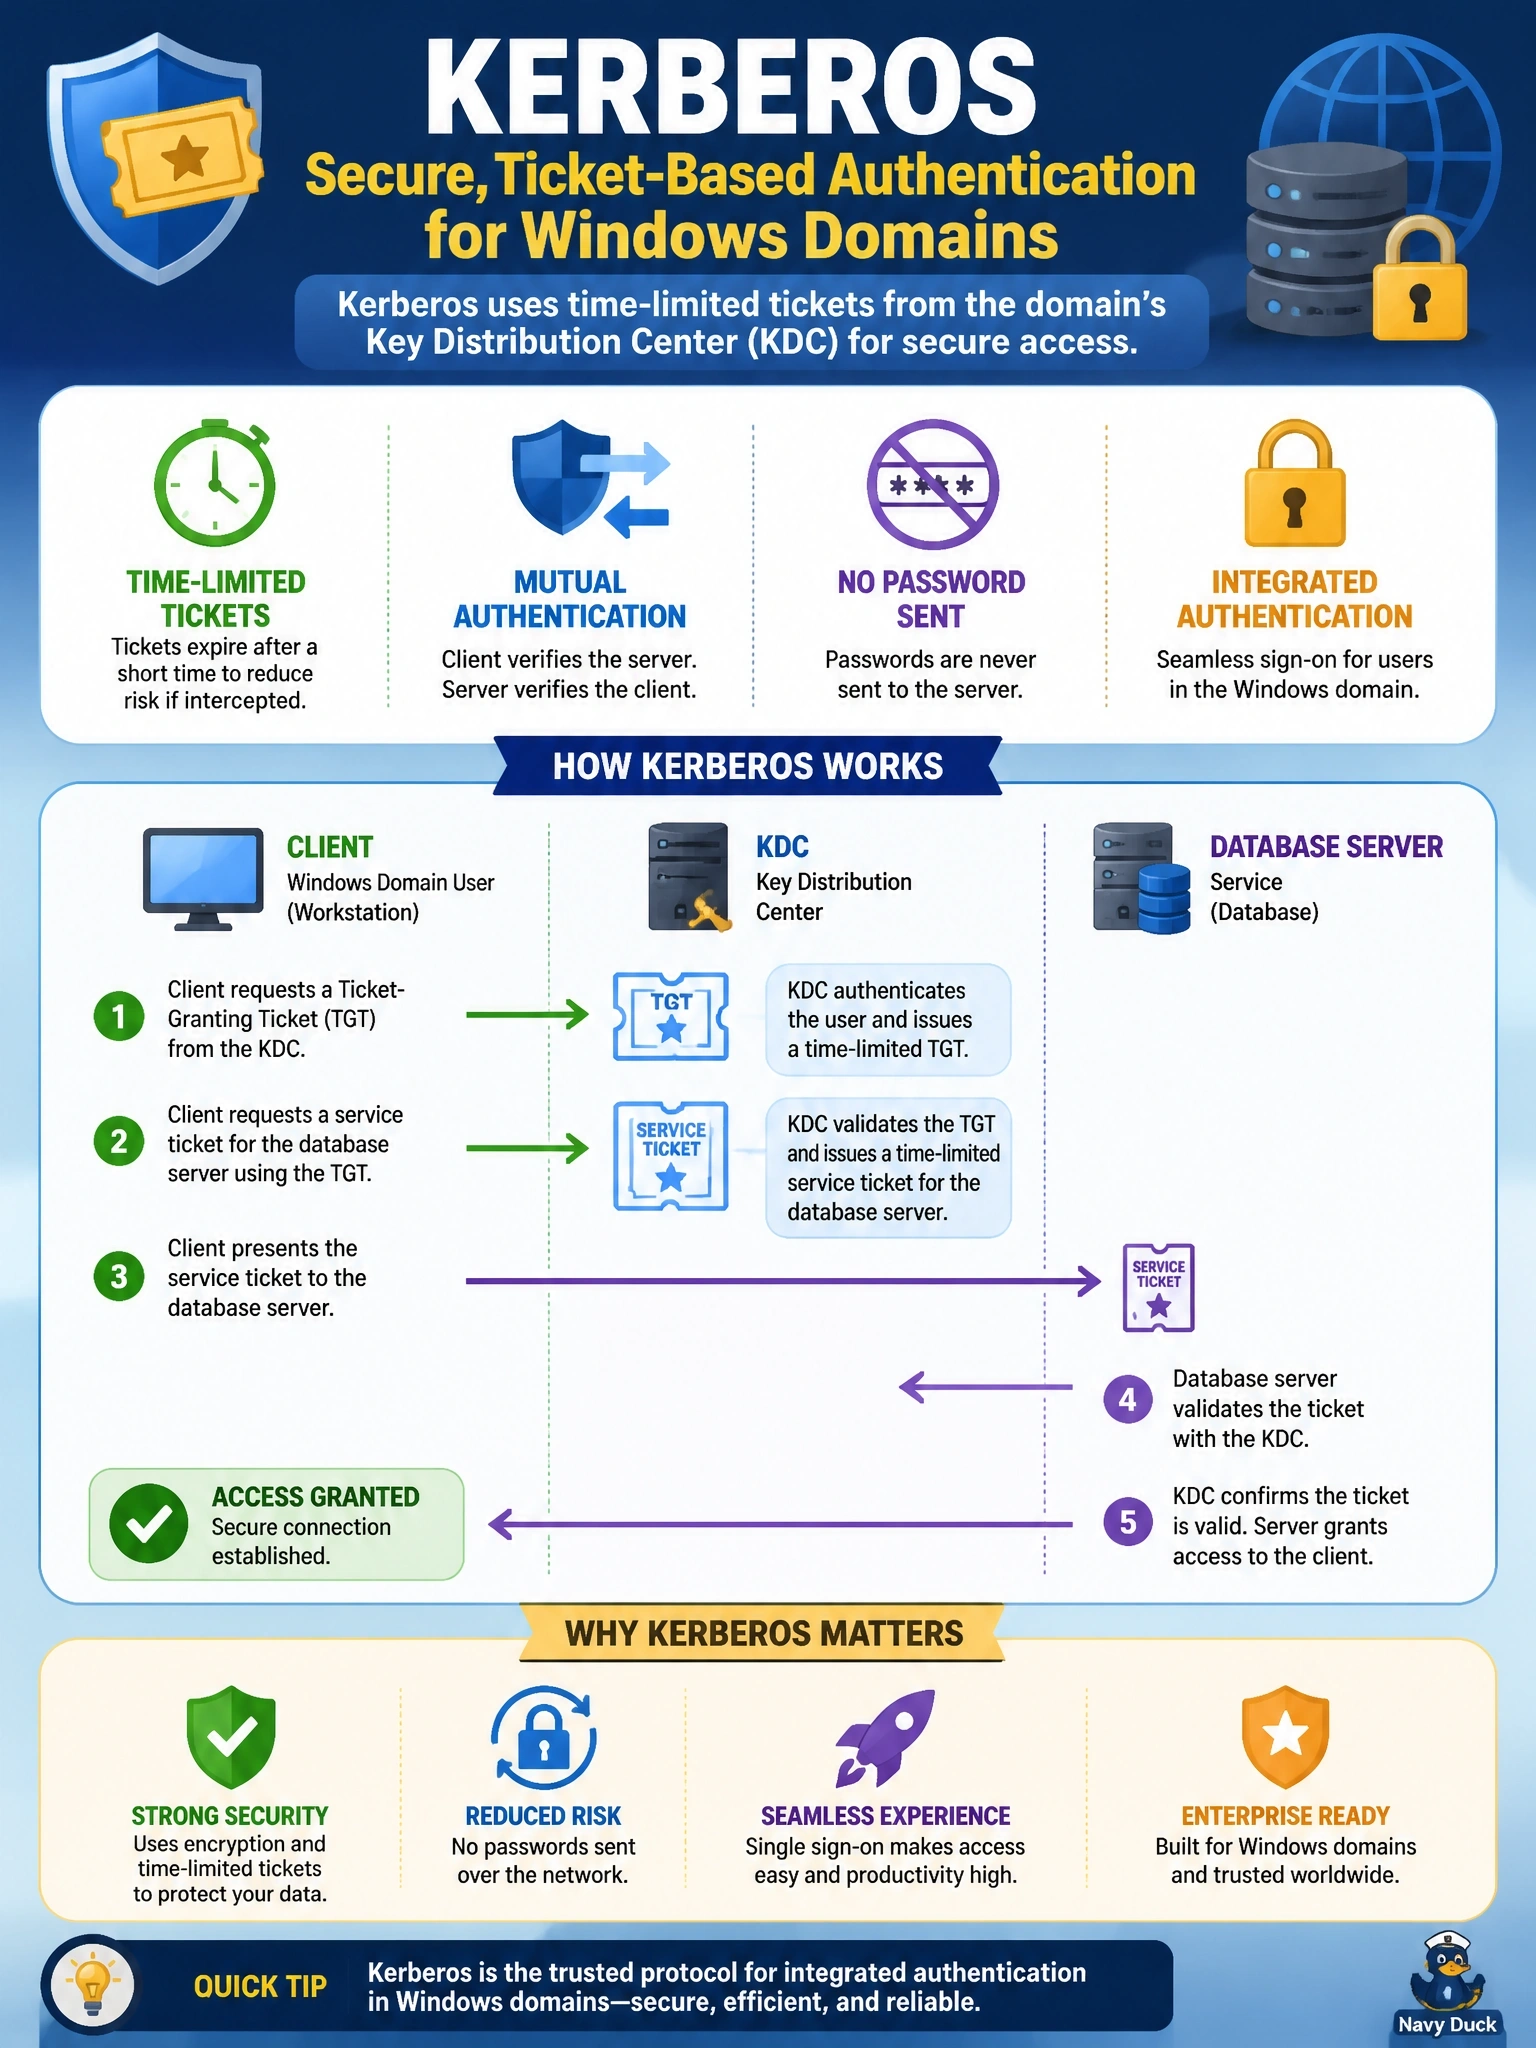
Kerberos works like a theme park ticket booth: you prove who you are once at the booth, get a ticket, and show the ticket at each ride. The database checks the ticket, and your password never travels to it. NTLM is the trap; it's also integrated, but it's challenge-response with no tickets and no mutual authentication.
Full Explanation
Kerberos is a ticket-based authentication protocol. A user authenticates to the key distribution center, which in a Windows domain runs on the domain controllers, and receives a ticket-granting ticket. When connecting to the database, the client presents that to obtain a service ticket for the database's service principal name, then presents the service ticket to the server. Tickets are time-limited and encrypted, the password itself is never sent to the database server, and the protocol supports mutual authentication so the client can verify it is talking to the genuine service, as well as delegation. NTLM is also used for integrated authentication but relies on challenge-response between client and server, has no tickets, lacks mutual authentication and is considered weaker; it is the fallback when Kerberos cannot be used. RADIUS is a protocol for centralized authentication, typically for network access such as VPN and wireless, not domain database logins. An LDAP simple bind sends credentials to a directory server, and without TLS sends them in clear text, which is the opposite of the stated requirement. Exam caveat: Kerberos depends on correct SPN registration and synchronized clocks, and failures there commonly cause silent fallback to NTLM. Operational check: query the server's connection information to confirm sessions report Kerberos as the authentication scheme.