
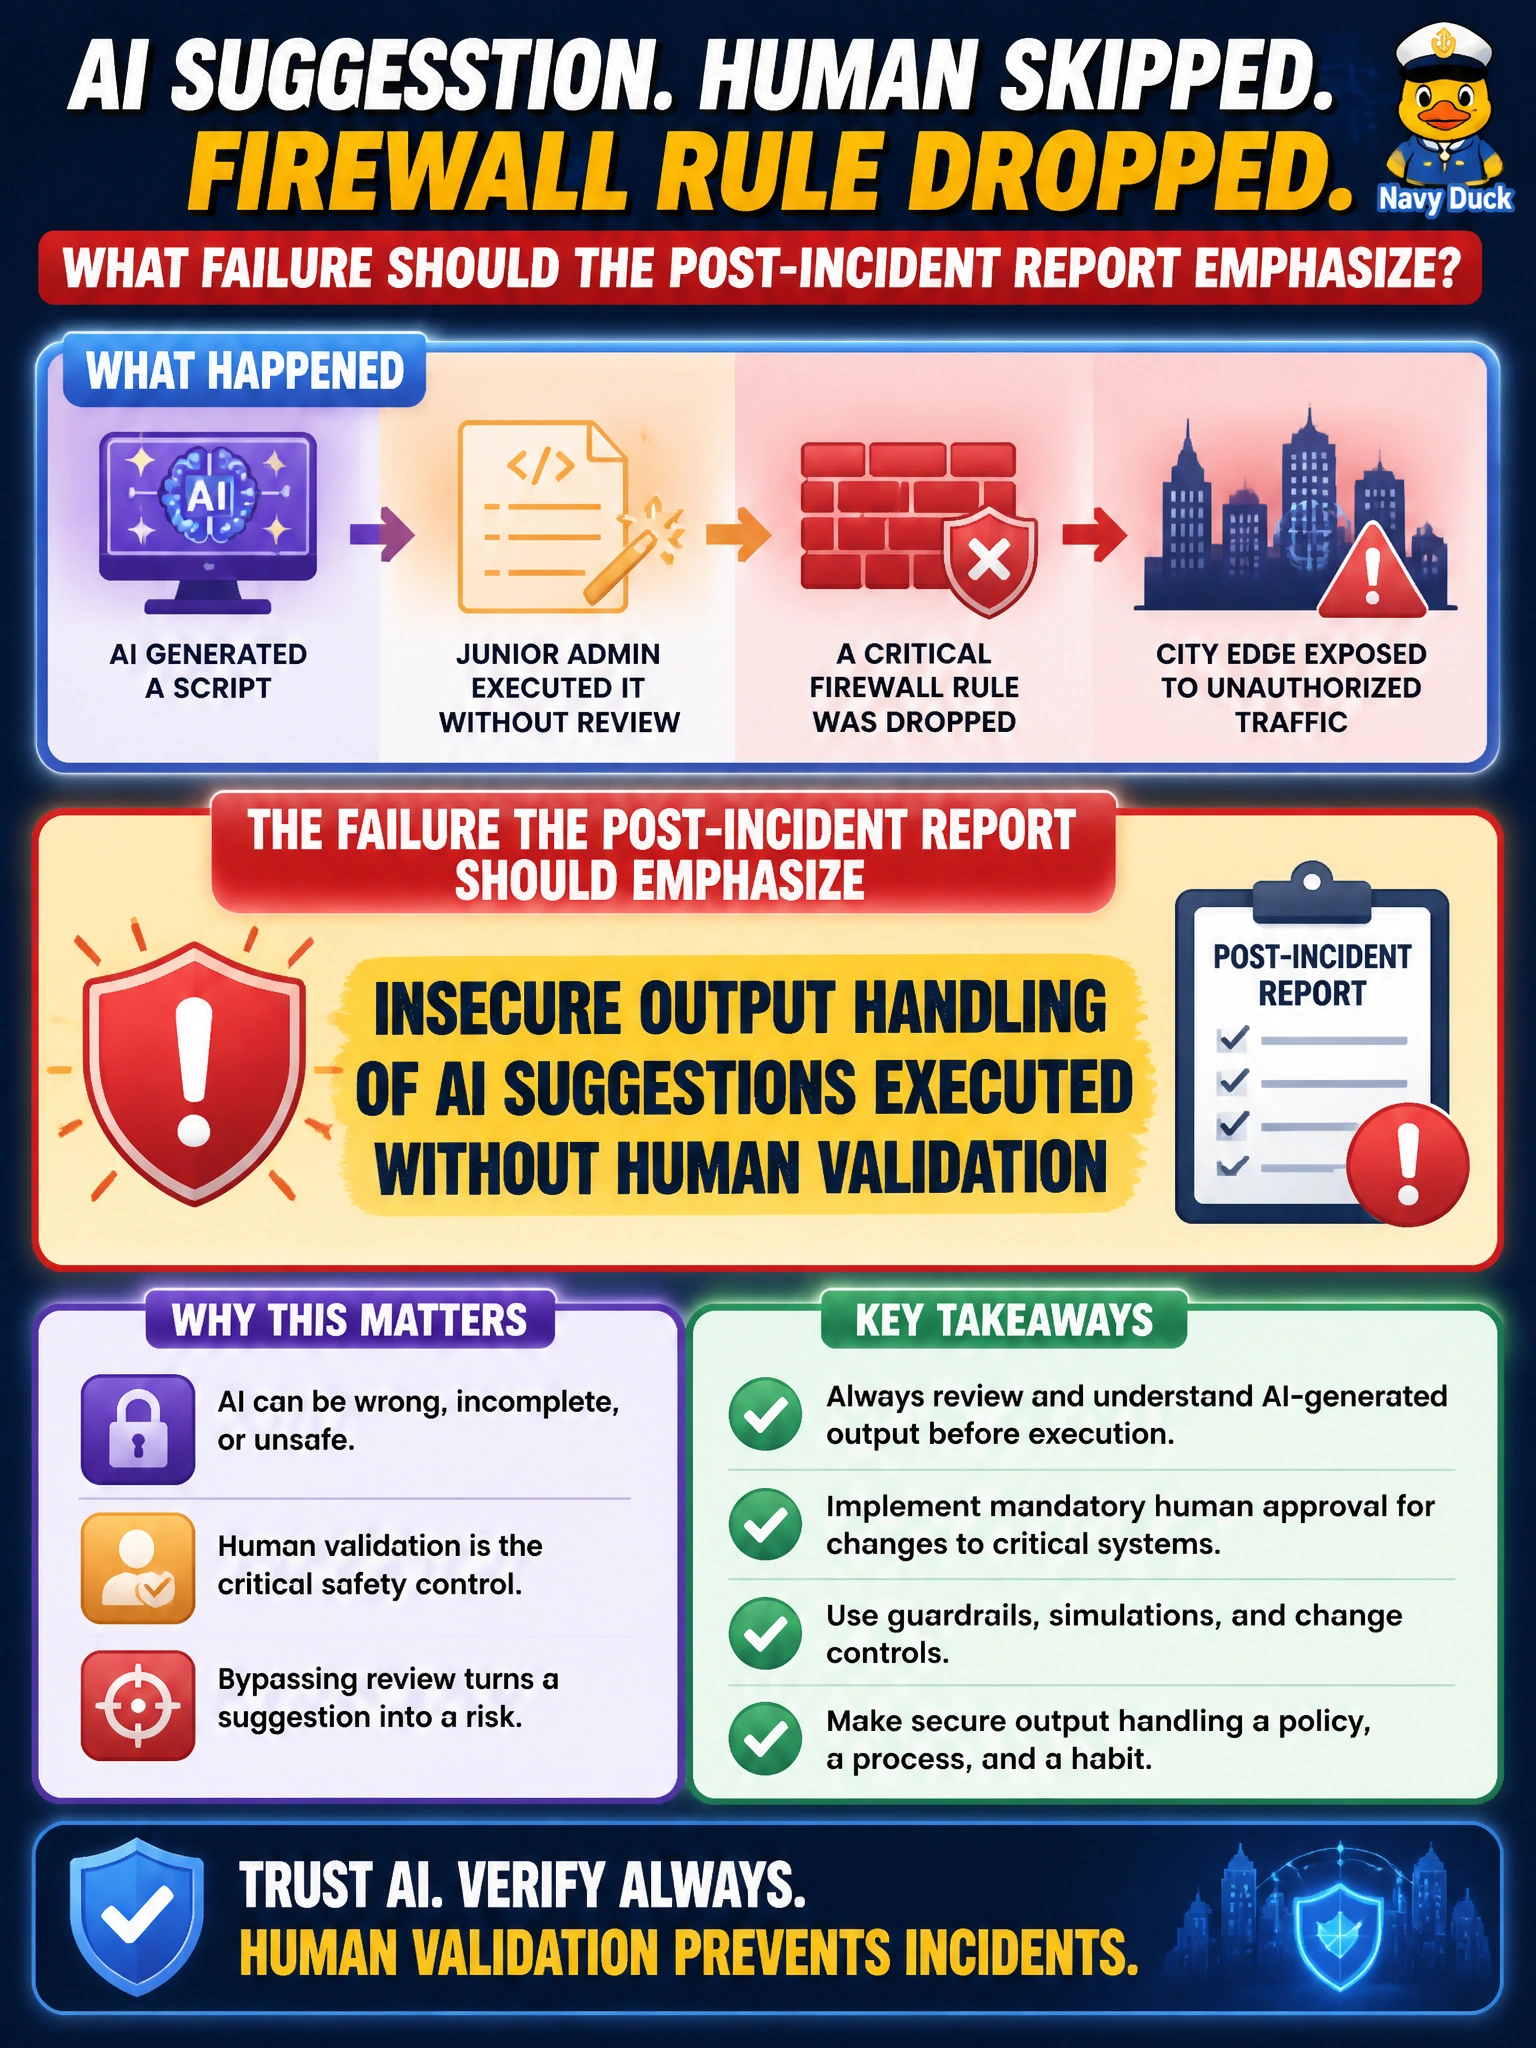
A junior admin executes an AI-generated script without review and drops a critical firewall rule on the city edge. What failure should the post-incident report emphasize?
Select an answer to reveal the explanation.
Short Explanation
Blindly running the bot’s script and nuking a firewall rule is insecure output handling—treat AI text like untrusted code. No autonomous agent pushed the change for you, nothing shows prompt injection altered the suggestion, and trusting a summary didn't make you run it. Require review before apply.
Full Explanation
Emphasizing insecure output handling when a junior admin executes an AI-generated script without review and drops a critical city-edge firewall rule is correct because AI suggestions were treated as trusted executable truth. Insecure output handling is the failure mode where generated text, code, or commands enter production actions without validation, testing, or change control. Municipal network edges are high-impact; one unreviewed apply can expose services citywide.
Excessive AI agent agency that pushed firewall changes without human validation fails as the emphasized root failure because no autonomous agent pushed the change — the junior admin manually executed the script, so the failure was unvalidated output entering production. Prompt injection that altered AI firewall suggestions without human validation fails as the emphasized root cause because there is no evidence of manipulated input, and validation is still required before applying any AI-generated commands to the edge firewall. Overreliance on AI incident summarization accepted without human validation fails as the emphasized root failure because summarization affects post-incident understanding, not the original decision to run an unreviewed script that dropped the rule.
Exam caveat: “human in the loop” is insufficient if the human rubber-stamps; review must include understanding side effects, diff against intended policy, and staged apply—not mere presence of an approver checkbox. Operational check: forbid direct paste-and-run of assistant-generated network changes, require peer review and change tickets for firewall edits, run AI-proposed scripts in a non-production parser/linter first, and log the assistant prompt/output alongside the change record for after-action review.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.