
RAG documents for the clerk bot should only be retrievable by roles allowed for each sensitivity level. Which control enables that?
Select an answer to reveal the explanation.
Short Explanation
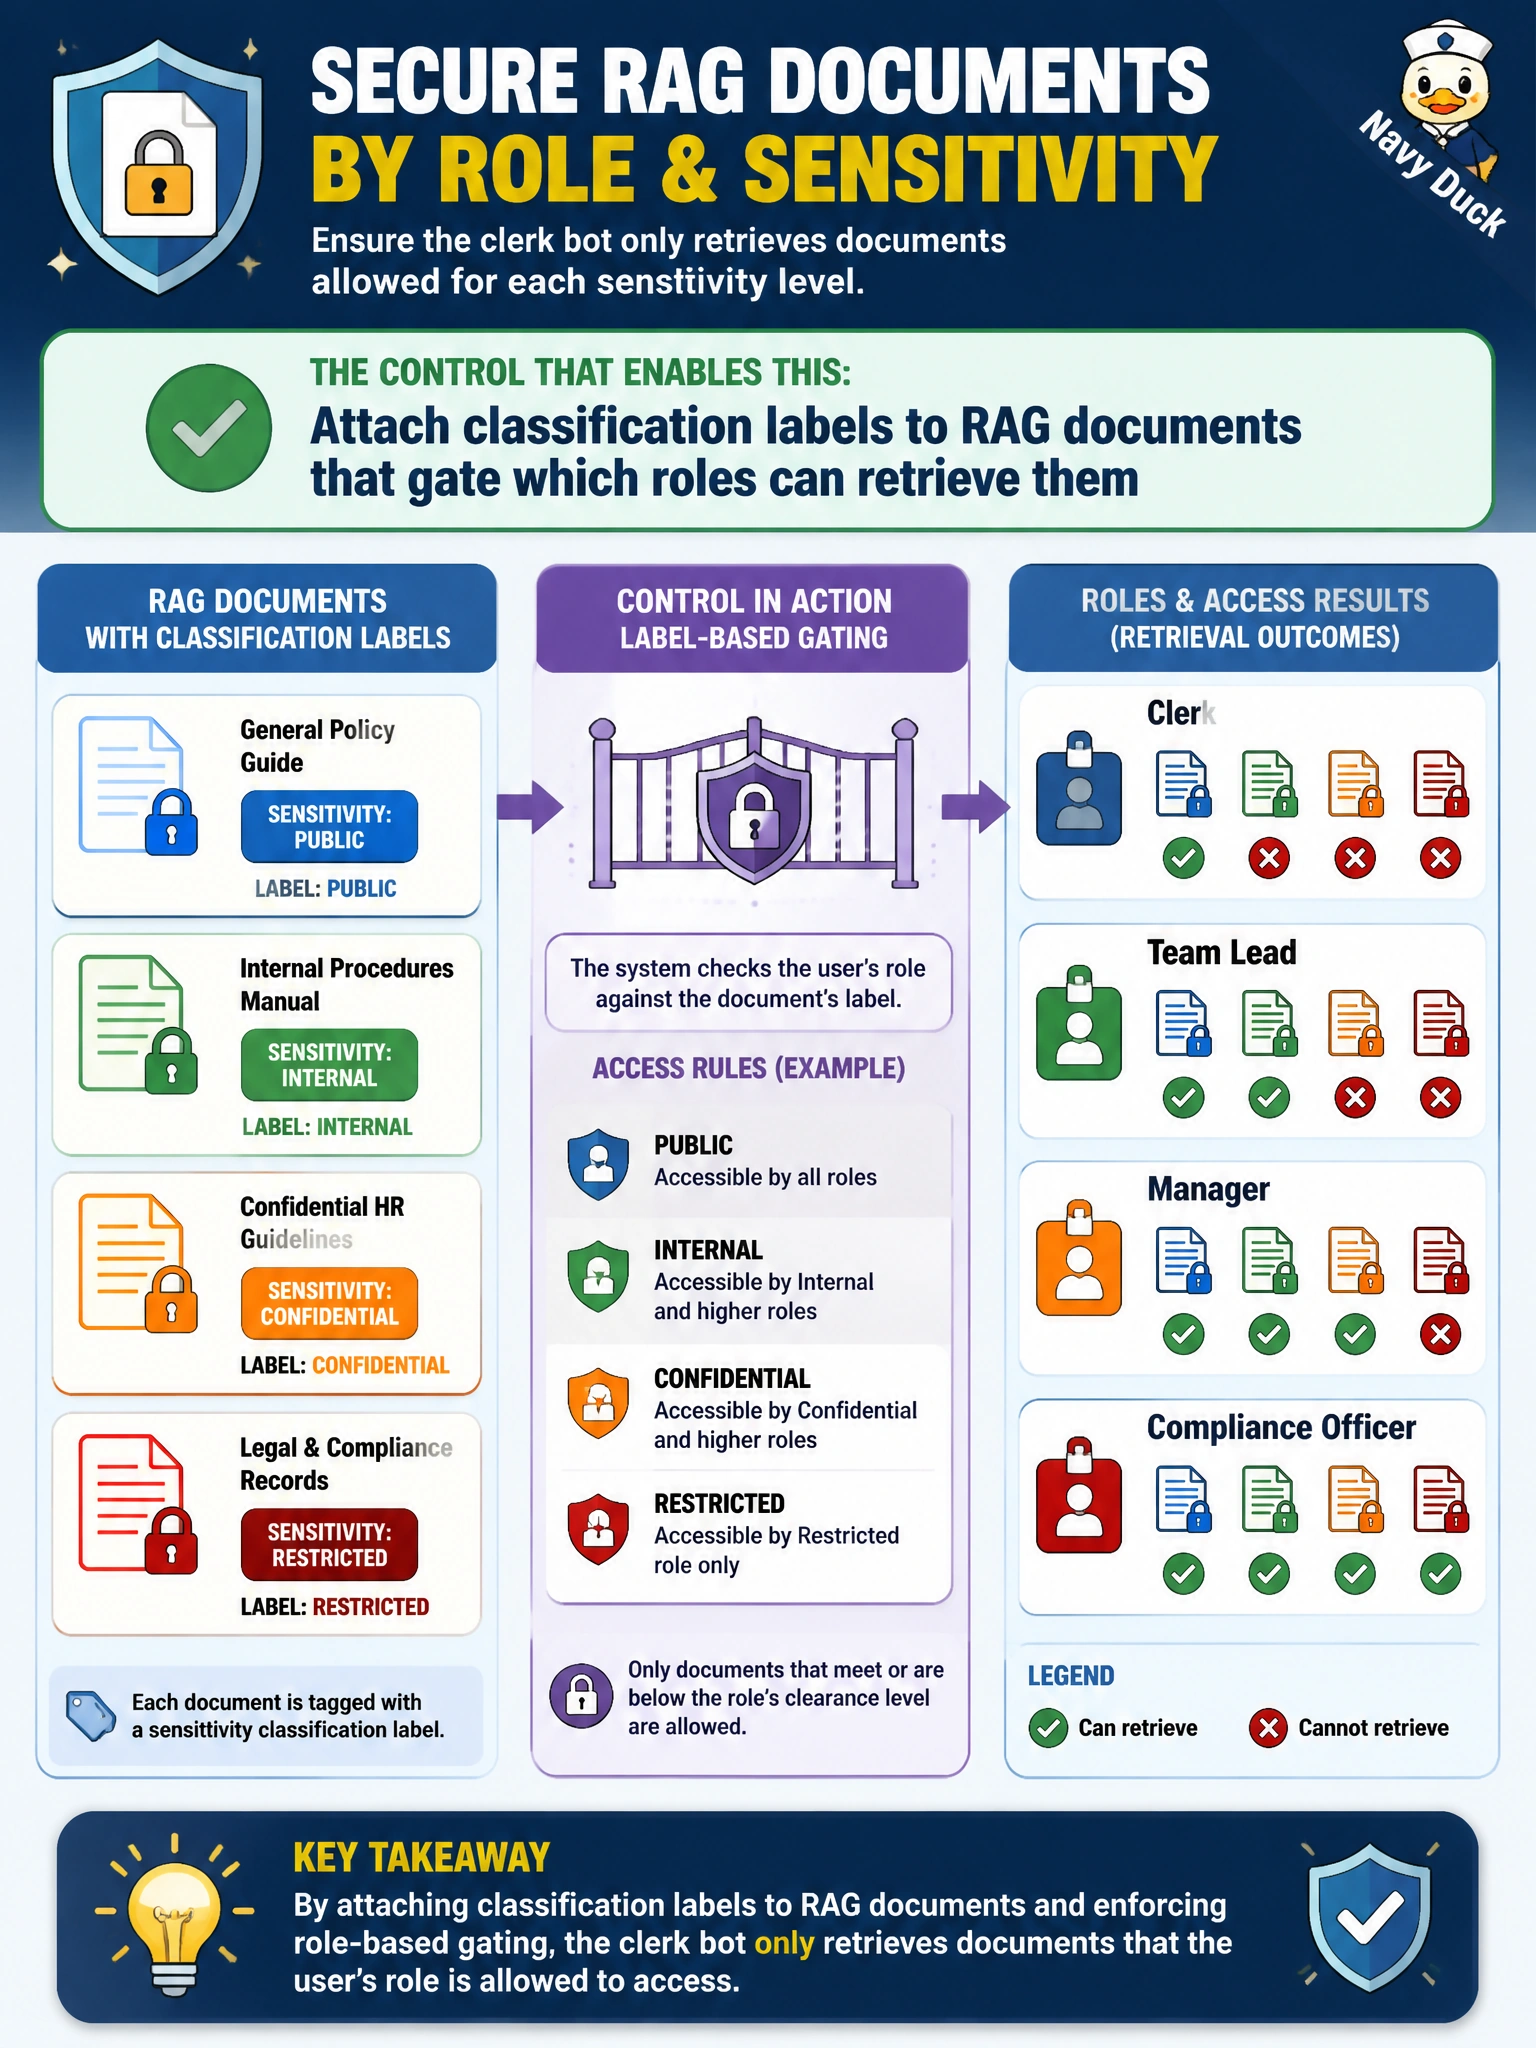
Labels on files are like clearance stickers on folders. Classification labels on RAG documents decide which roles can pull them into the clerk bot. If you'll only label queries, responses, or chat histories, you're not stopping uncleared roles from pulling files into the bot, so it's like you've got no sticker at all.
Full Explanation
Attaching classification labels to RAG documents that gate which roles can retrieve them is the control that enables sensitivity-aware retrieval for the clerk bot. Labels tag municipal documents with sensitivity levels; authorization uses those labels so only roles cleared for a given level can pull matching chunks into the RAG context. That pattern keeps confidential counsel or higher-sensitivity clerk materials from being retrieved by lower-privilege roles while still serving appropriately labeled content.
Attaching classification labels to RAG queries that gate which roles can retrieve them fails because it labels the request rather than the source documents — without sensitivity tags on the documents themselves, the retriever cannot block an uncleared role from pulling confidential clerk chunks into context. Attaching classification labels to RAG responses that gate which roles can retrieve them fails because it labels the output after retrieval has already happened — it does not prevent an uncleared role from pulling sensitive documents into the RAG context in the first place. Attaching classification labels to RAG chat histories that gate which roles can retrieve them fails because it labels prior conversation rather than the retrievable corpus — history tags cannot enforce per-level sensitivity when the retriever selects municipal documents for the clerk bot.
Exam caveat: Classification-driven RAG access depends on labels on RAG documents that are actually enforced against the retrieval path itself, not labels on RAG queries, RAG responses, or RAG chat histories that gate which roles can retrieve them. A label that nothing checks is not a control.
Operational check: Label clerk RAG documents by sensitivity, map retrieval permissions to roles, attempt retrieval of a confidential memo with a low-privilege clerk role (denied), confirm the retrieval path enforces document labels, and verify that labeling only RAG queries, RAG responses, or RAG chat histories still lets an uncleared role pull the sensitive document.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.