
Departing employees must lose model API access automatically when they leave city SSO groups. Which design best achieves that?
Select an answer to reveal the explanation.
Short Explanation
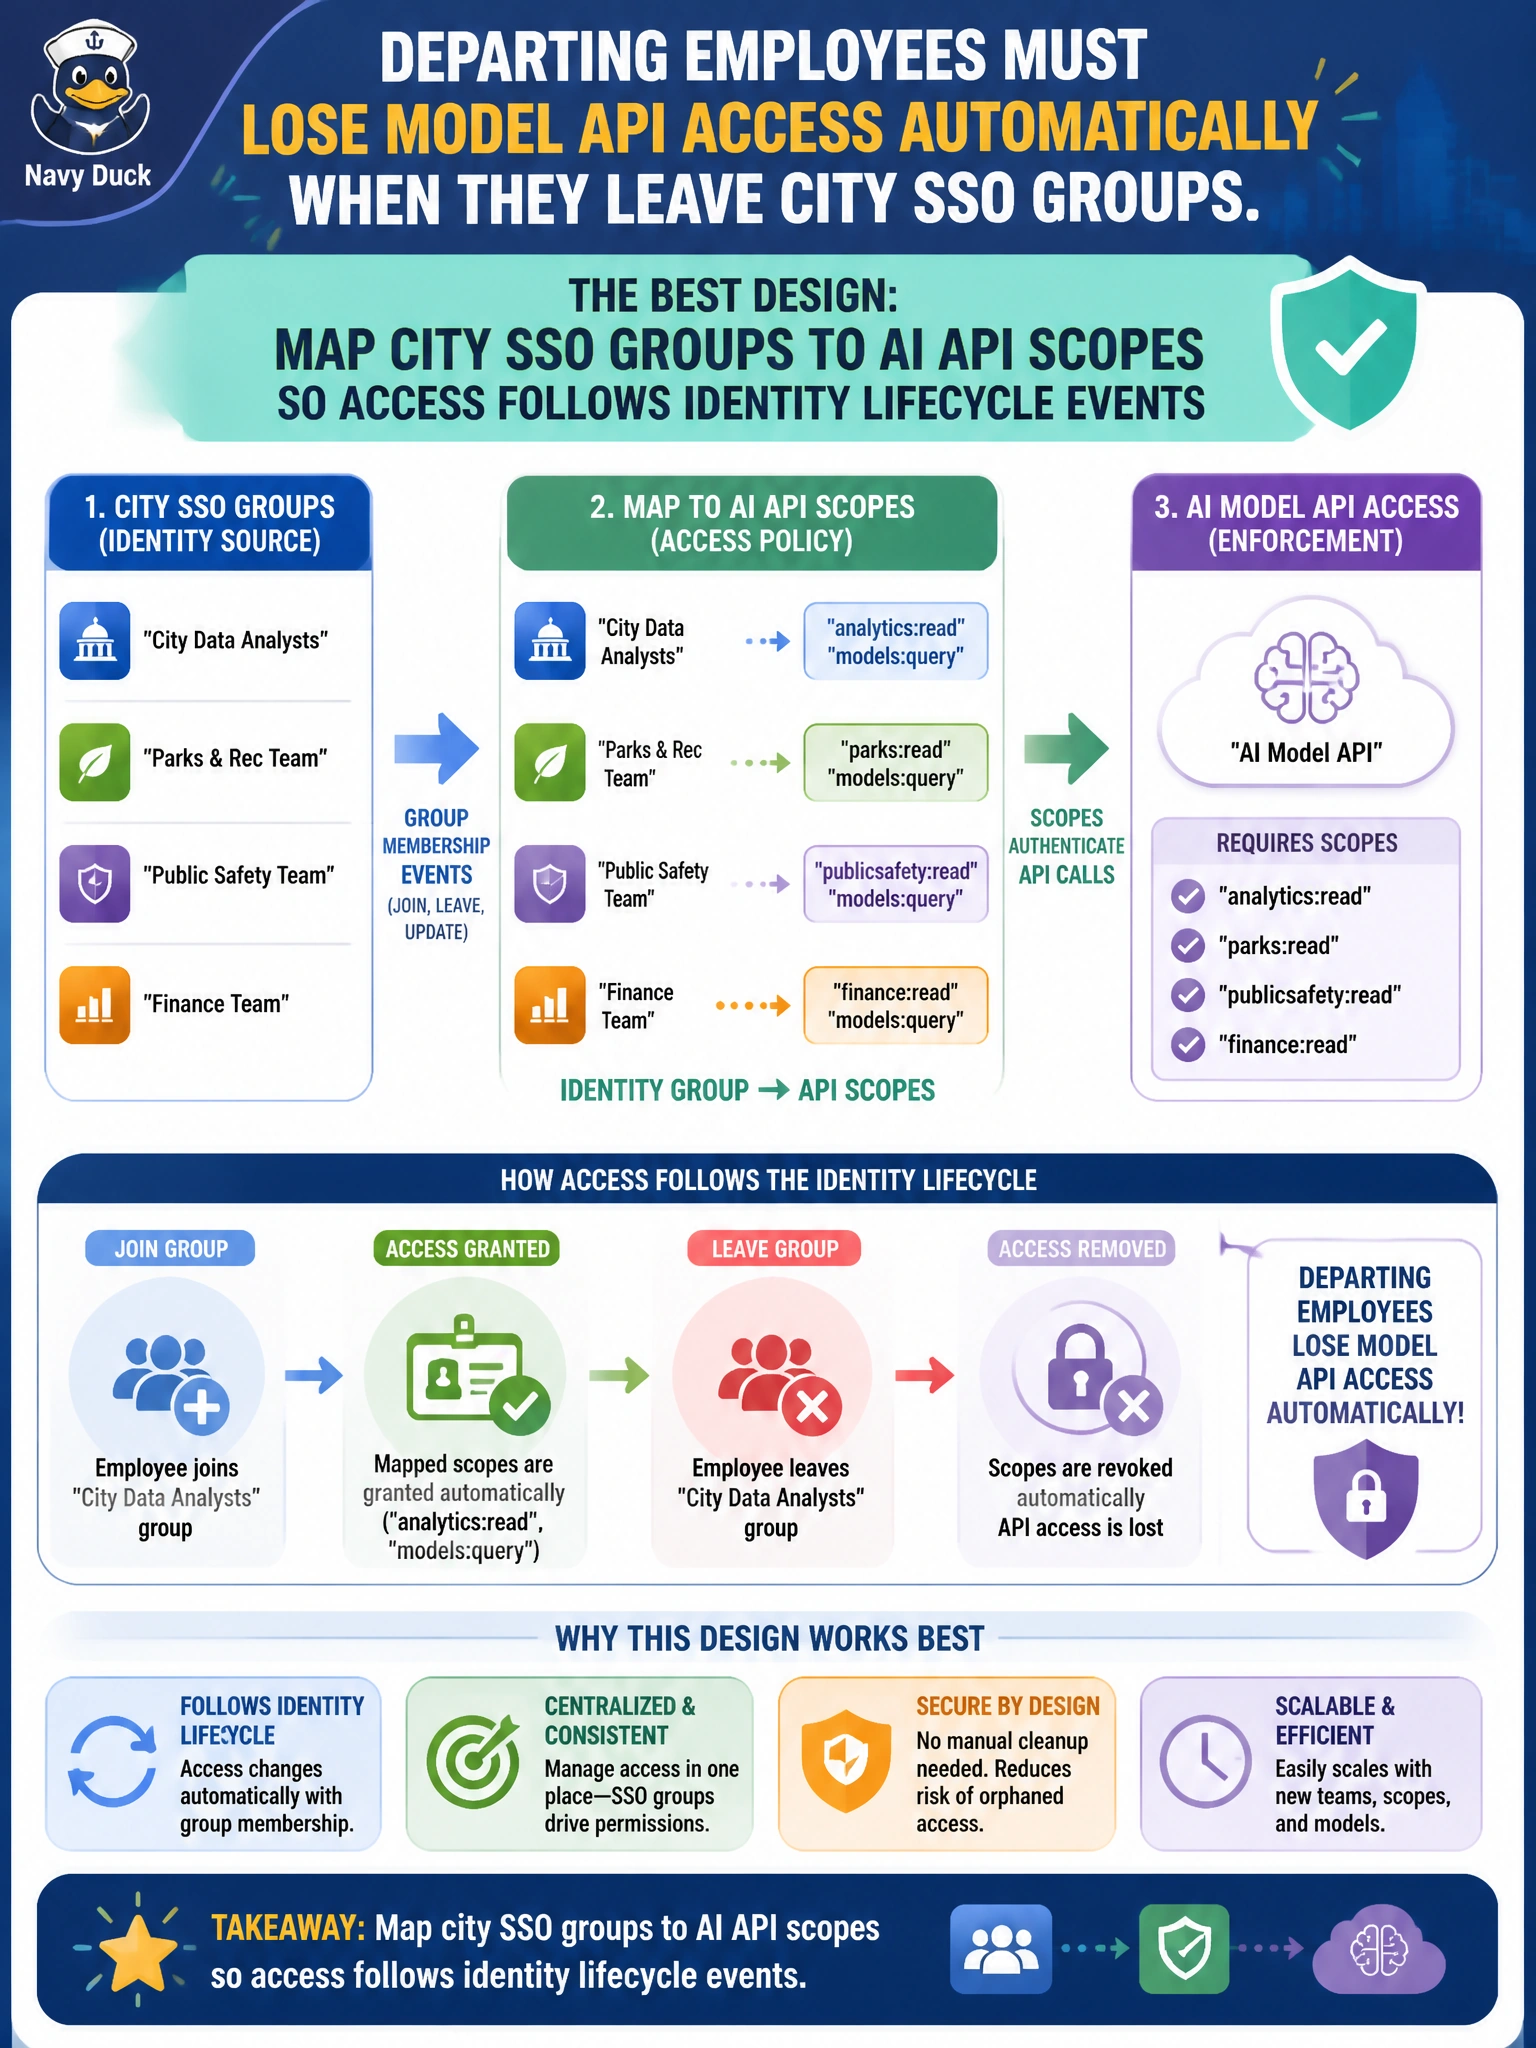
When someone leaves the org chart, the model door should close with them. Tie AI API scopes to city SSO groups so lifecycle events revoke access automatically. If you wait for scheduled batch reconciliation to catch up, or trust a gateway cache that lags behind real membership, you'll keep the door open too long.
Full Explanation
Mapping city SSO groups to AI API scopes so access follows identity lifecycle events is the design that automatically removes model API access when departing employees leave those groups. IdP-tied authorization means joiners gain scopes when added to groups and leavers lose scopes when removed—without relying on manual key cleanup. For municipal AI APIs, binding scopes to city SSO groups aligns model access with HR and identity offboarding. Enforcing model API calls with short-lived OAuth tokens bound to SSO session lifetime fails by concept because tokens bound to the session are not automatically revoked the instant SSO group membership changes, so a departed employee can keep using a valid token until it expires. Caching city SSO group lookups at the gateway to authorize AI API scopes at runtime fails because cached lookups can be stale; a removed employee may still appear in the cache until it refreshes, so access is not revoked at departure. Syncing city SSO group changes to AI API scopes through scheduled batch reconciliation jobs fails because reconciliation only runs on a schedule, so a removed employee keeps access until the next batch runs instead of losing it automatically at departure. Exam caveat: Prefer IdP/group-mapped API authorization that reacts automatically to lifecycle events over scheduled batch reconciliation jobs that leave access in place until the next run or cached group lookups that can be stale between syncs. Operational check: Map AI API scopes to SSO groups, add a test user and confirm model access, remove the user from the group (or disable the account) and confirm access ends without waiting for a scheduled batch reconciliation job, and confirm scopes stay current without depending on a gateway-cached group lookup.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.