
A SOC analyst sees an EDR alert showing a Windows server beaconing to an unknown external IP every 30 seconds. The host is suspected compromised, but the analyst needs to keep EDR agent management and remote forensic access while blocking adversary network traffic. Which containment action best meets these requirements?
Select an answer to reveal the explanation.
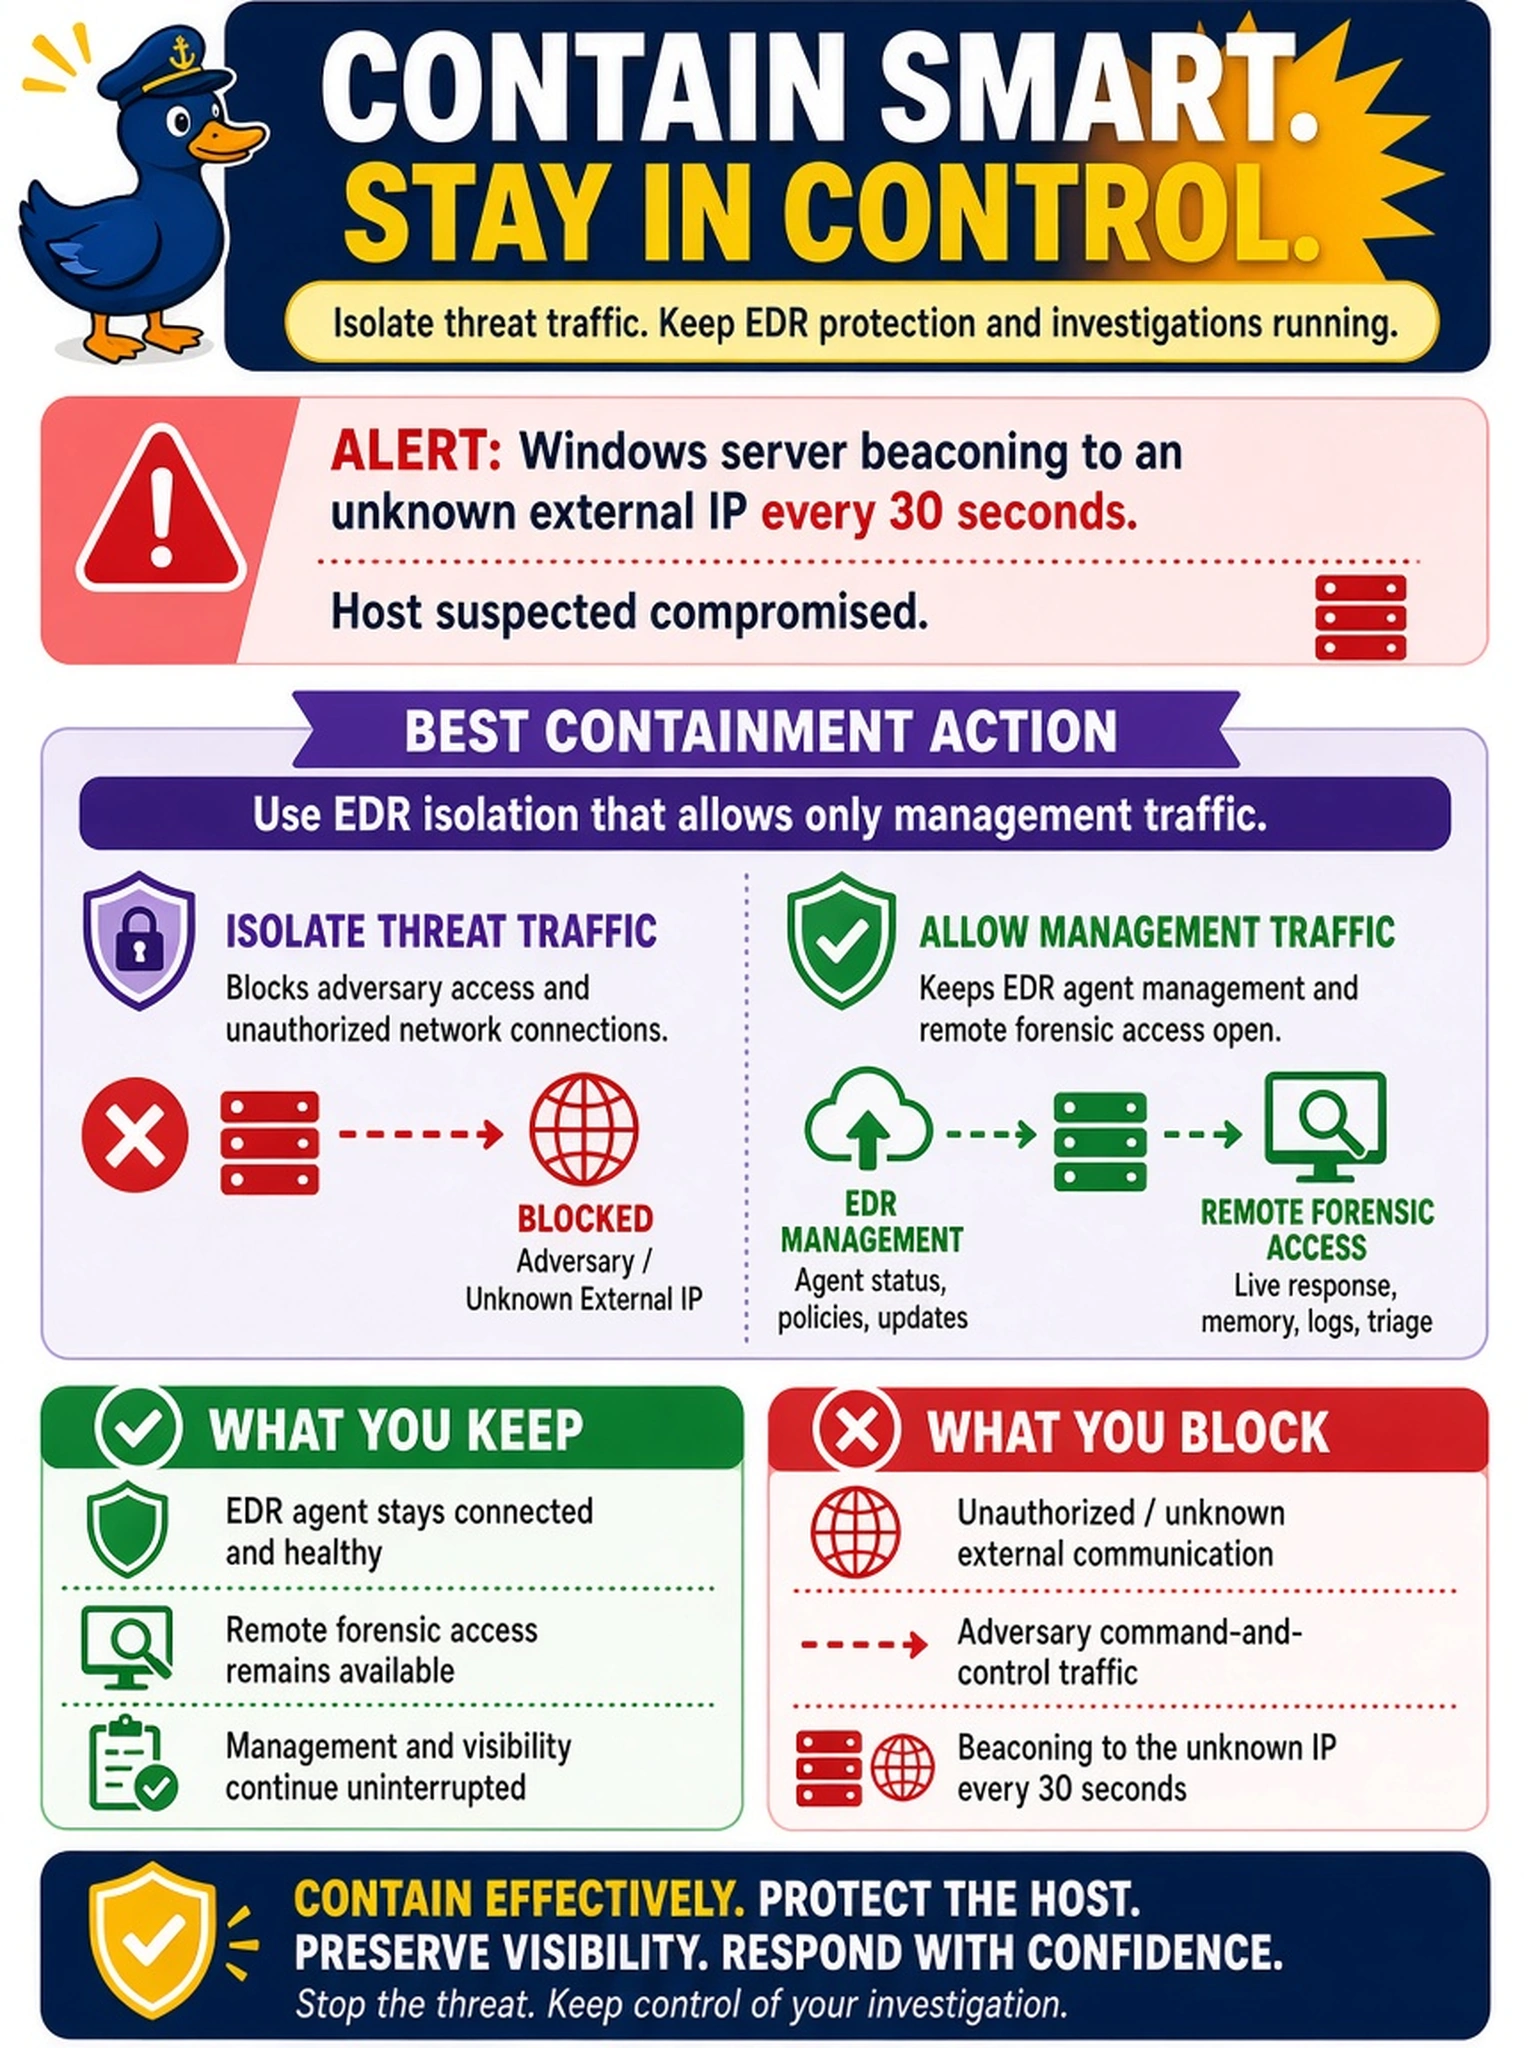
Short Explanation
Think of EDR isolation like a one-way glass: you keep the analyst’s remote view alive while the infected host can’t talk to its handler. If you yank the NIC or firewall-block everything, you also blind your own containment tool. The right move is isolation that allows only management traffic.
Full Explanation
EDR network isolation is a containment control because it applies a host-level policy that denies adversary command-and-control paths while preserving the agent’s authenticated channel to the management plane. This lets the analyst query telemetry, collect memory and disk artifacts, and run commands without letting the compromised process continue beaconing or move laterally. Blocking all outbound traffic at the perimeter firewall can stop the beacon, but it is a broad network control that may also sever the EDR agent’s management connection, leaving the host unreachable for live containment and forensics. Disabling the operating system network adapter is more destructive: it removes all connectivity, including the management channel, and can alert the adversary through lost heartbeats. Quarantining an alert in the SIEM and disabling an Active Directory account affects alert workflow and authentication, not the host’s active network session or malware process; it neither isolates traffic nor guarantees forensic access. Exam caveat: CompTIA expects you to distinguish containment that preserves investigative access from blunt shutdown or network cutoff methods. Operational check: Before isolation, confirm the EDR management endpoint IP or URL is in the isolation allow list, then verify the host remains online and the beaconing destination is blocked.