
Your SOC needs to exchange indicators, campaigns, and actor data with partner CERTs and threat intel platforms in a machine-readable, automated way. Which standards should you require?
Select an answer to reveal the explanation.
Short Explanation
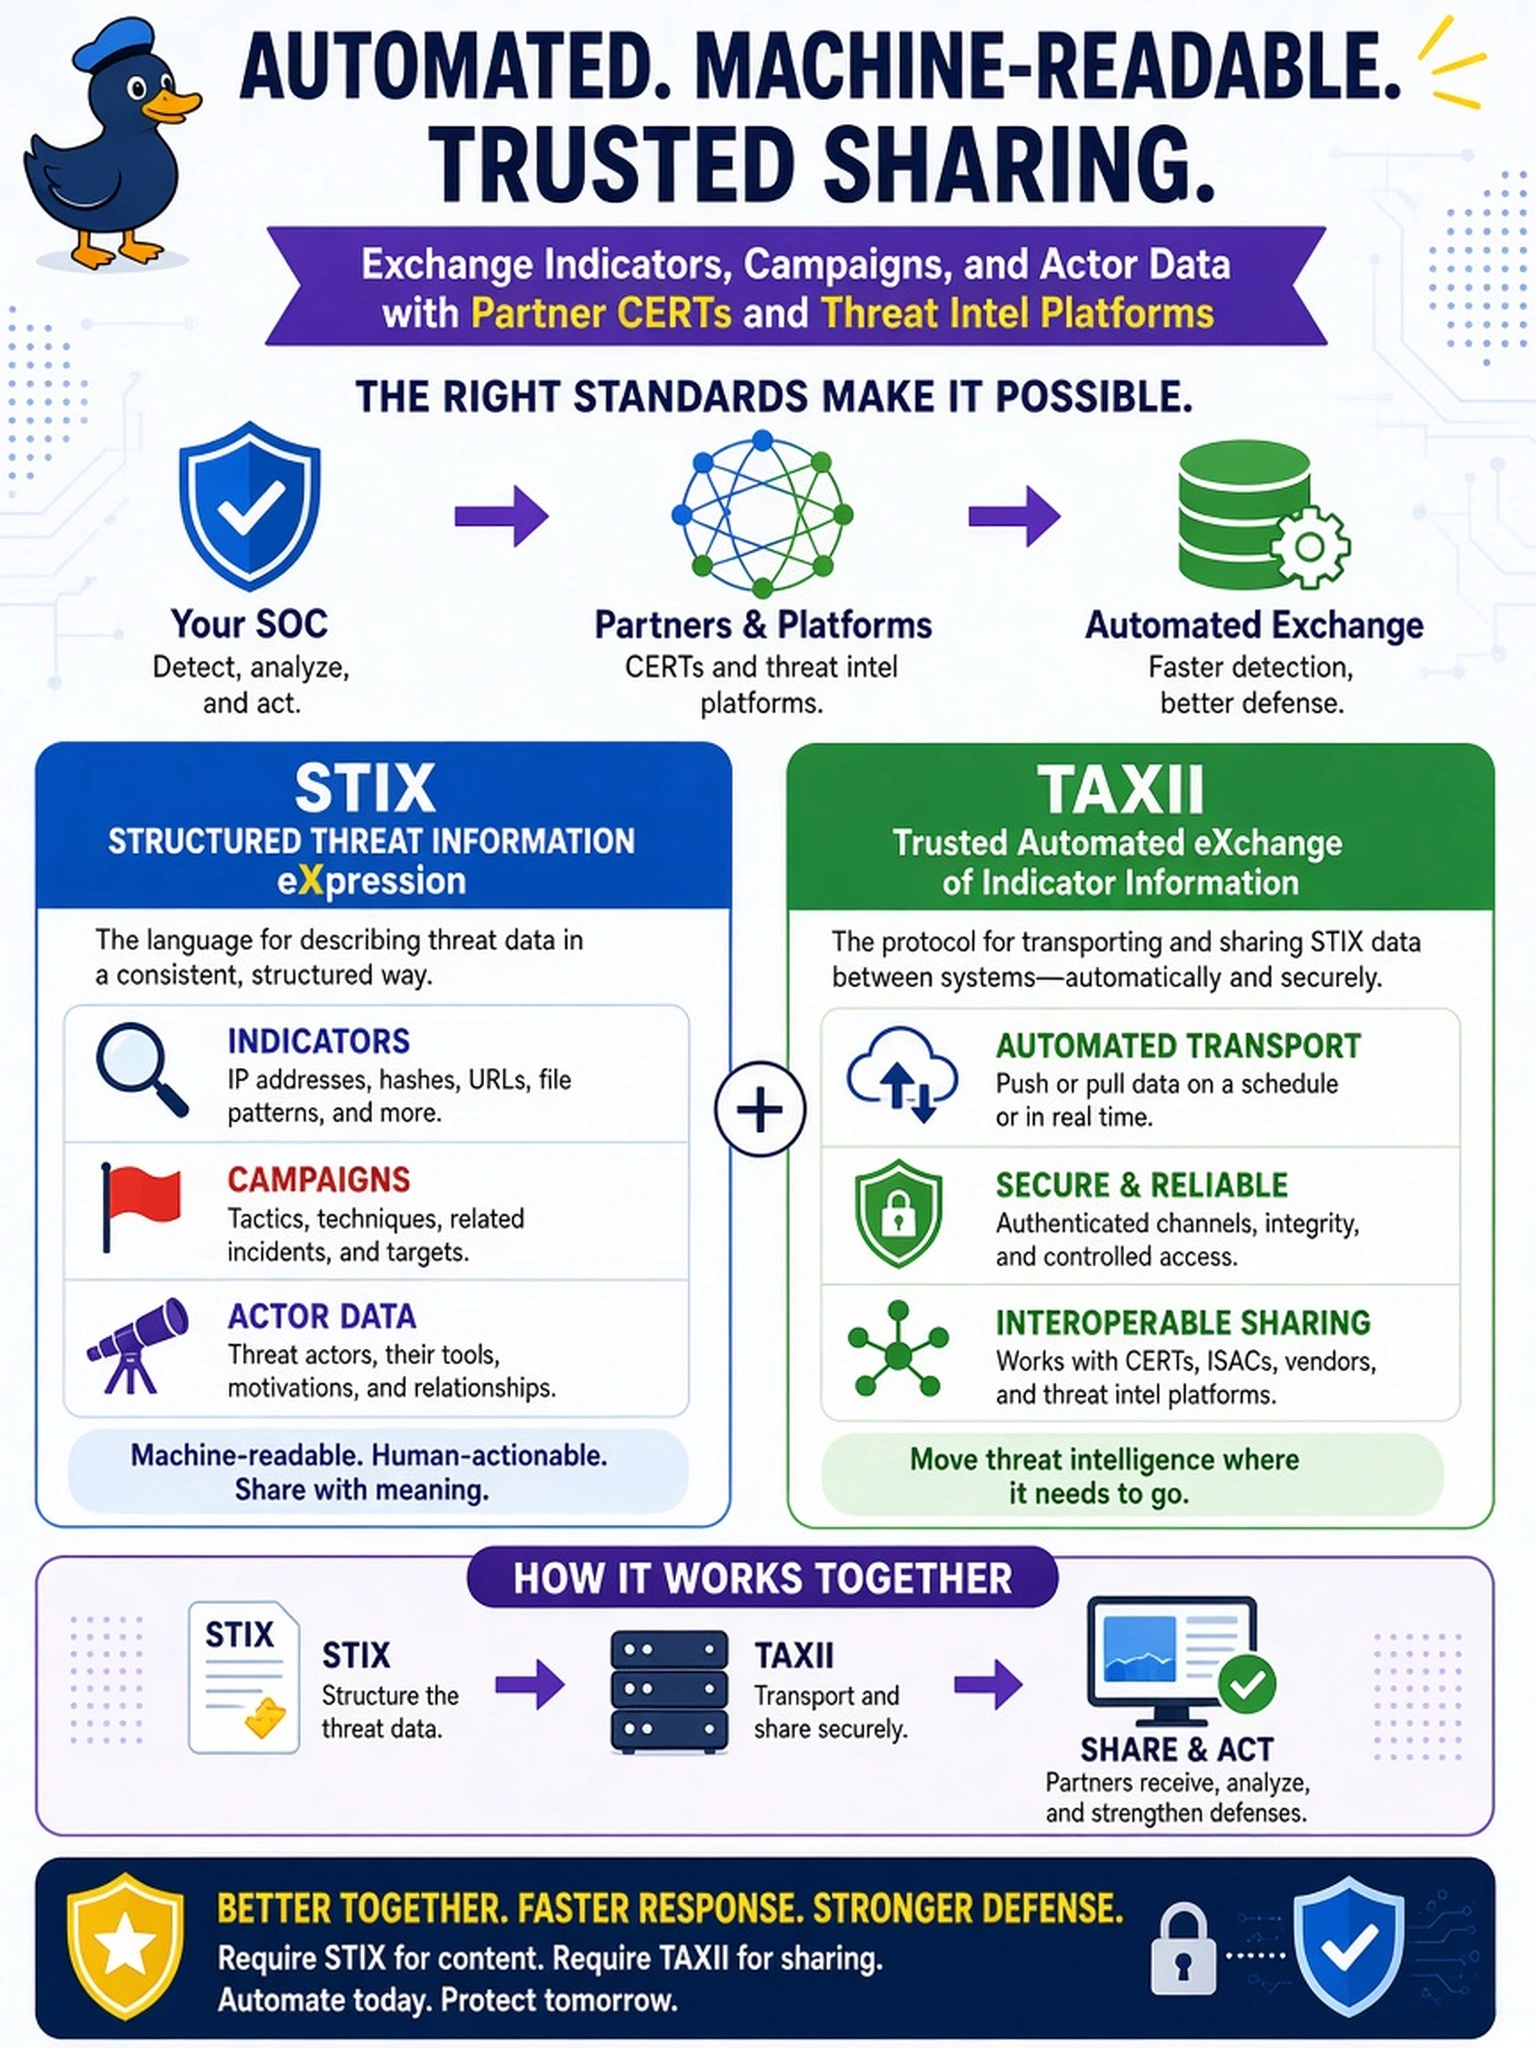
Think of threat intel like shipping: STIX is the crate and labeling, TAXII is the truck route. You want a standard that both sides can load, unload, and automate. The trap is picking a detection framework or log protocol just because it sounds security-ish, so don't be fooled.
Full Explanation
STIX is a structured language for representing cyber threat intelligence, including indicators, campaigns, actors, and relationships. TAXII provides transport mechanisms for sharing those STIX packages between trusted systems. Together they allow a SOC to exchange machine-readable indicators with partners, threat intel platforms, and automated enrichment workflows. Syslog is wrong because it is a log transport and event collection protocol, not a threat intelligence data model or exchange standard for indicators. MITRE ATT&CK is wrong because it is a taxonomy and knowledge base for adversary tactics, techniques, and procedures, useful for detection coverage and mapping, not for transmitting indicator objects. OpenIOC is wrong because it is an older indicator format and not the standardized exchange pair expected for structured sharing between modern threat intelligence systems. Exam caveat: Do not confuse threat intelligence exchange standards with detection frameworks or log transport protocols. Operational check: Confirm the integration uses STIX/TAXII with authentication, current version support, and a validation step for imported indicators.