
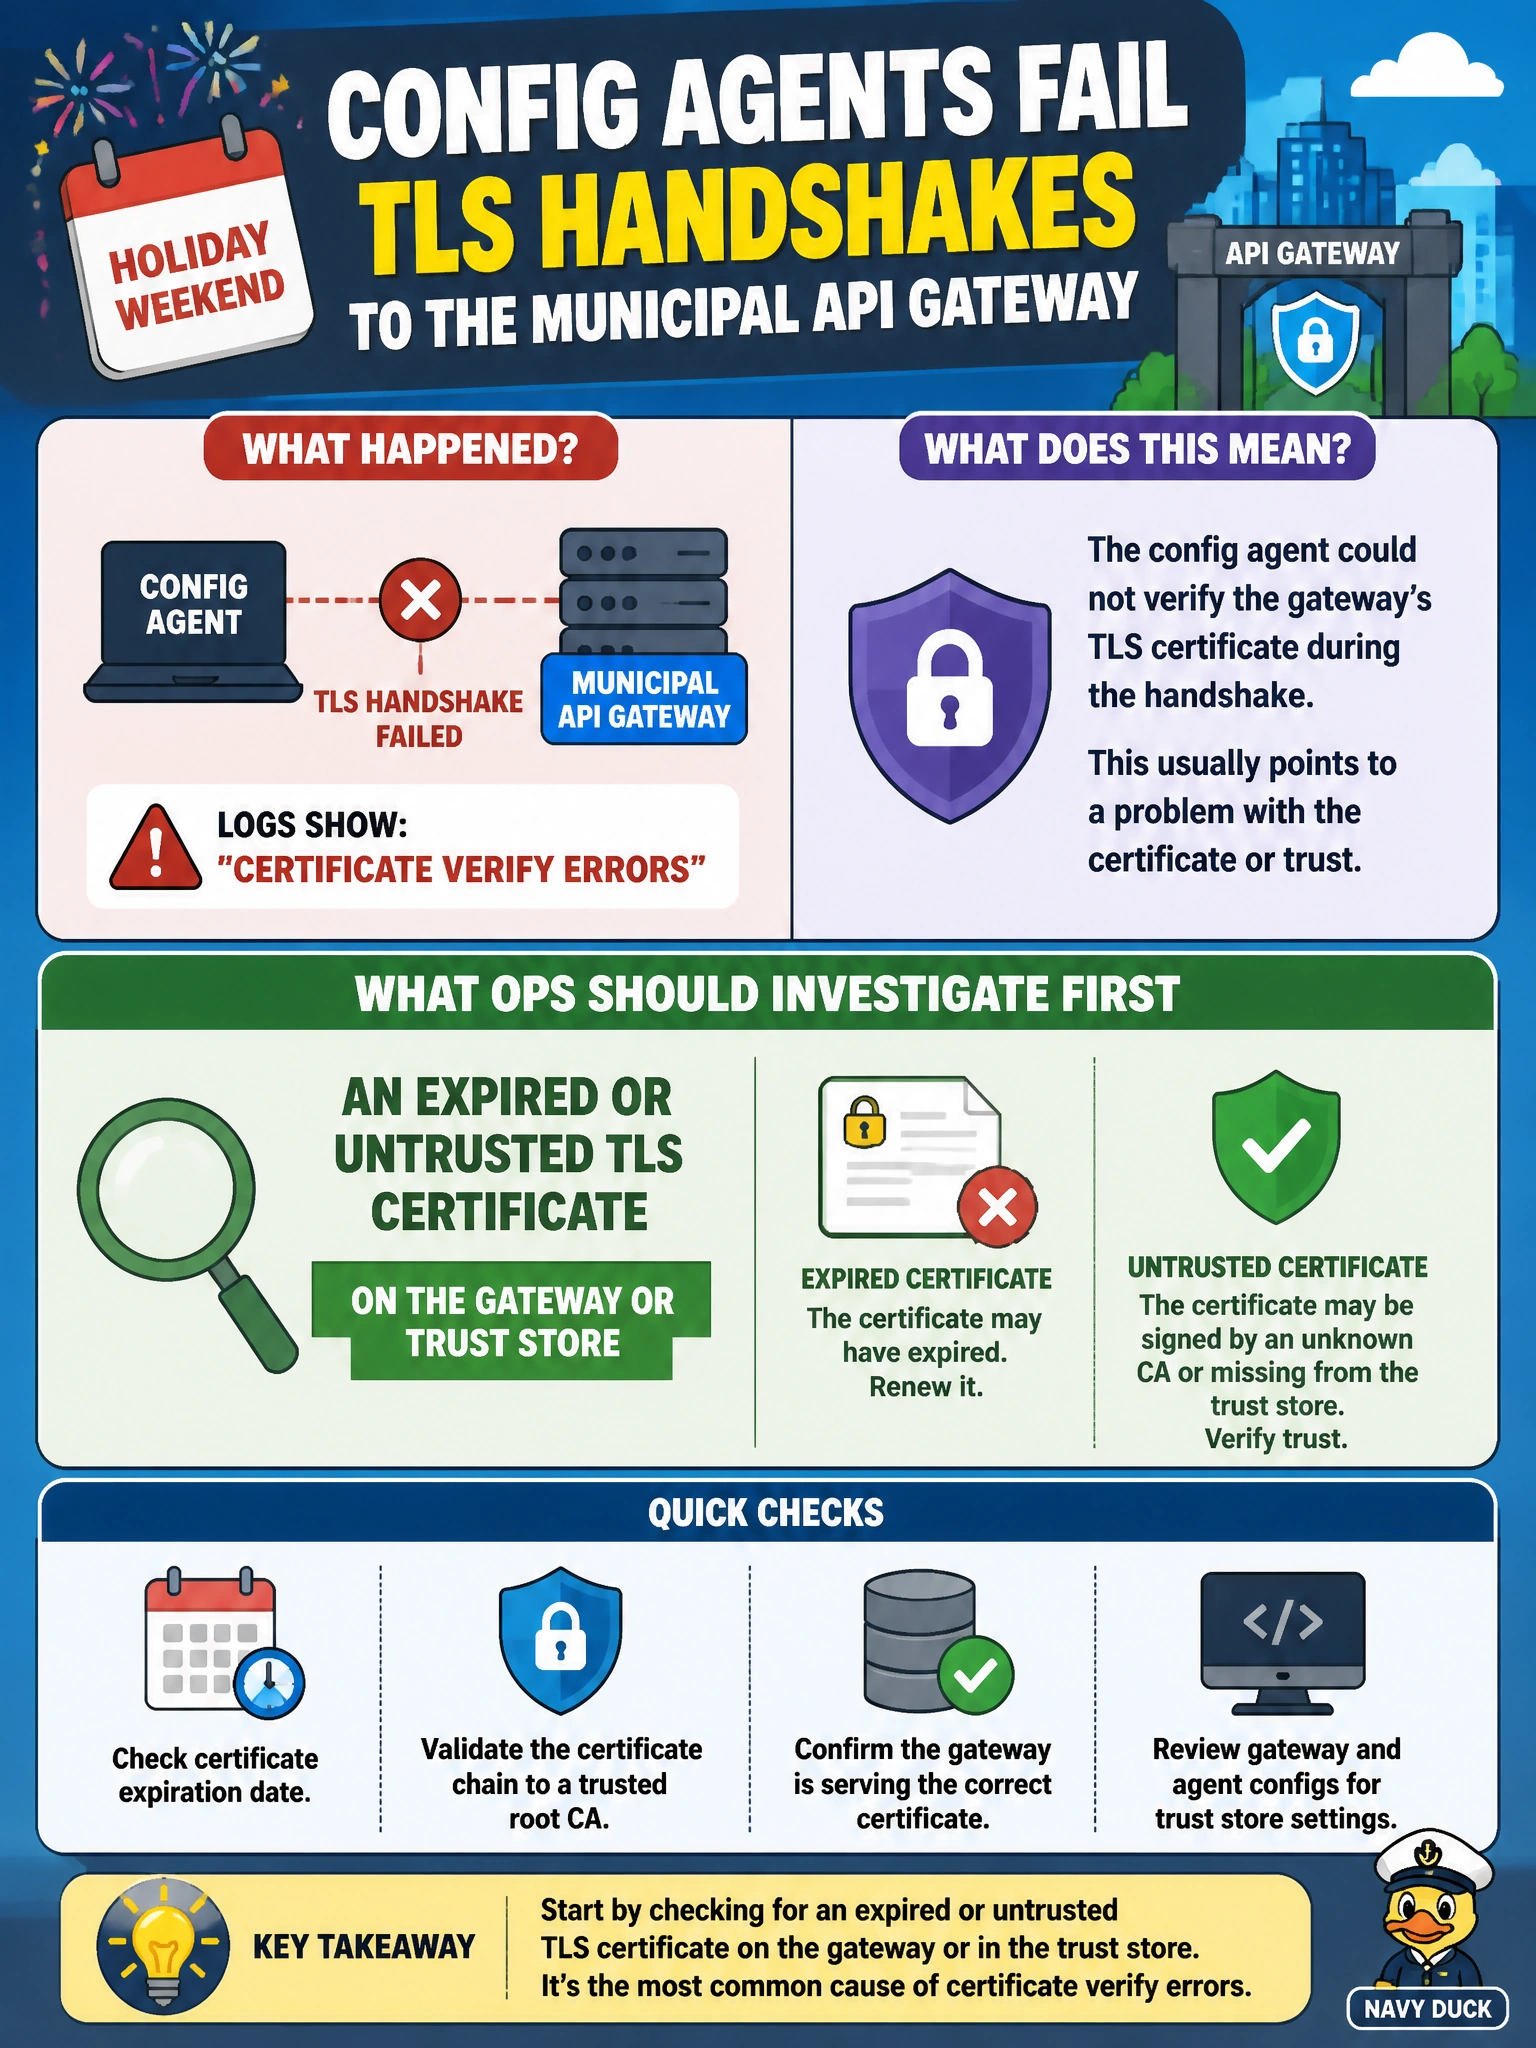
Config agents fail TLS handshakes to the municipal API gateway after a holiday weekend. Logs show certificate verify errors. What should ops investigate first?
Select an answer to reveal the explanation.
Short Explanation
Handshake verify errors are usually a bad or expired badge at the door—renew or trust the right cert. Turning off HTTPS is not the municipal fix. YAML indents do not renew TLS.
Full Explanation
Config agents that fail TLS handshakes to the municipal API gateway with certificate verify errors should prompt ops to investigate an expired or untrusted TLS certificate on the gateway or in the agents’ trust store first. Verify failures mean the client cannot validate the server certificate chain—common after holiday weekends when certificates expire unnoticed, intermediate chains change, or trust bundles on agents drift. Restoring a valid gateway certificate and ensuring municipal agents trust the issuing CA repairs the handshake so configuration pulls resume over HTTPS.
Disabling HTTPS for permanent cleartext HTTP fails by concept: it removes confidentiality and integrity for config traffic and is not an acceptable municipal remediation for verify errors. Claiming HTTP 201 responses somehow invalidate client certificates fails because 201 is an application success status after TLS is already established; it does not revoke or invalidate certificates. Increasing YAML indentation depth fails because playbook whitespace has no relationship to renewing or trusting TLS certificates.
Exam caveat: verify errors can be server cert expiry, missing intermediate, hostname mismatch, or outdated client trust store—investigate those before blaming application payloads. Do not confuse mutual-TLS client-cert failures with server-cert verify errors, though both are certificate problems; the stem points at verify errors typical of server/trust-store issues.
Operational check: inspect gateway certificate notAfter and chain in a browser or openssl s_client from an agent host, renew/replace the cert if expired, update agent CA bundles if the issuer changed, alert on cert expiry with lead time covering holidays, and confirm handshakes succeed before declaring the configuration channel healthy.