
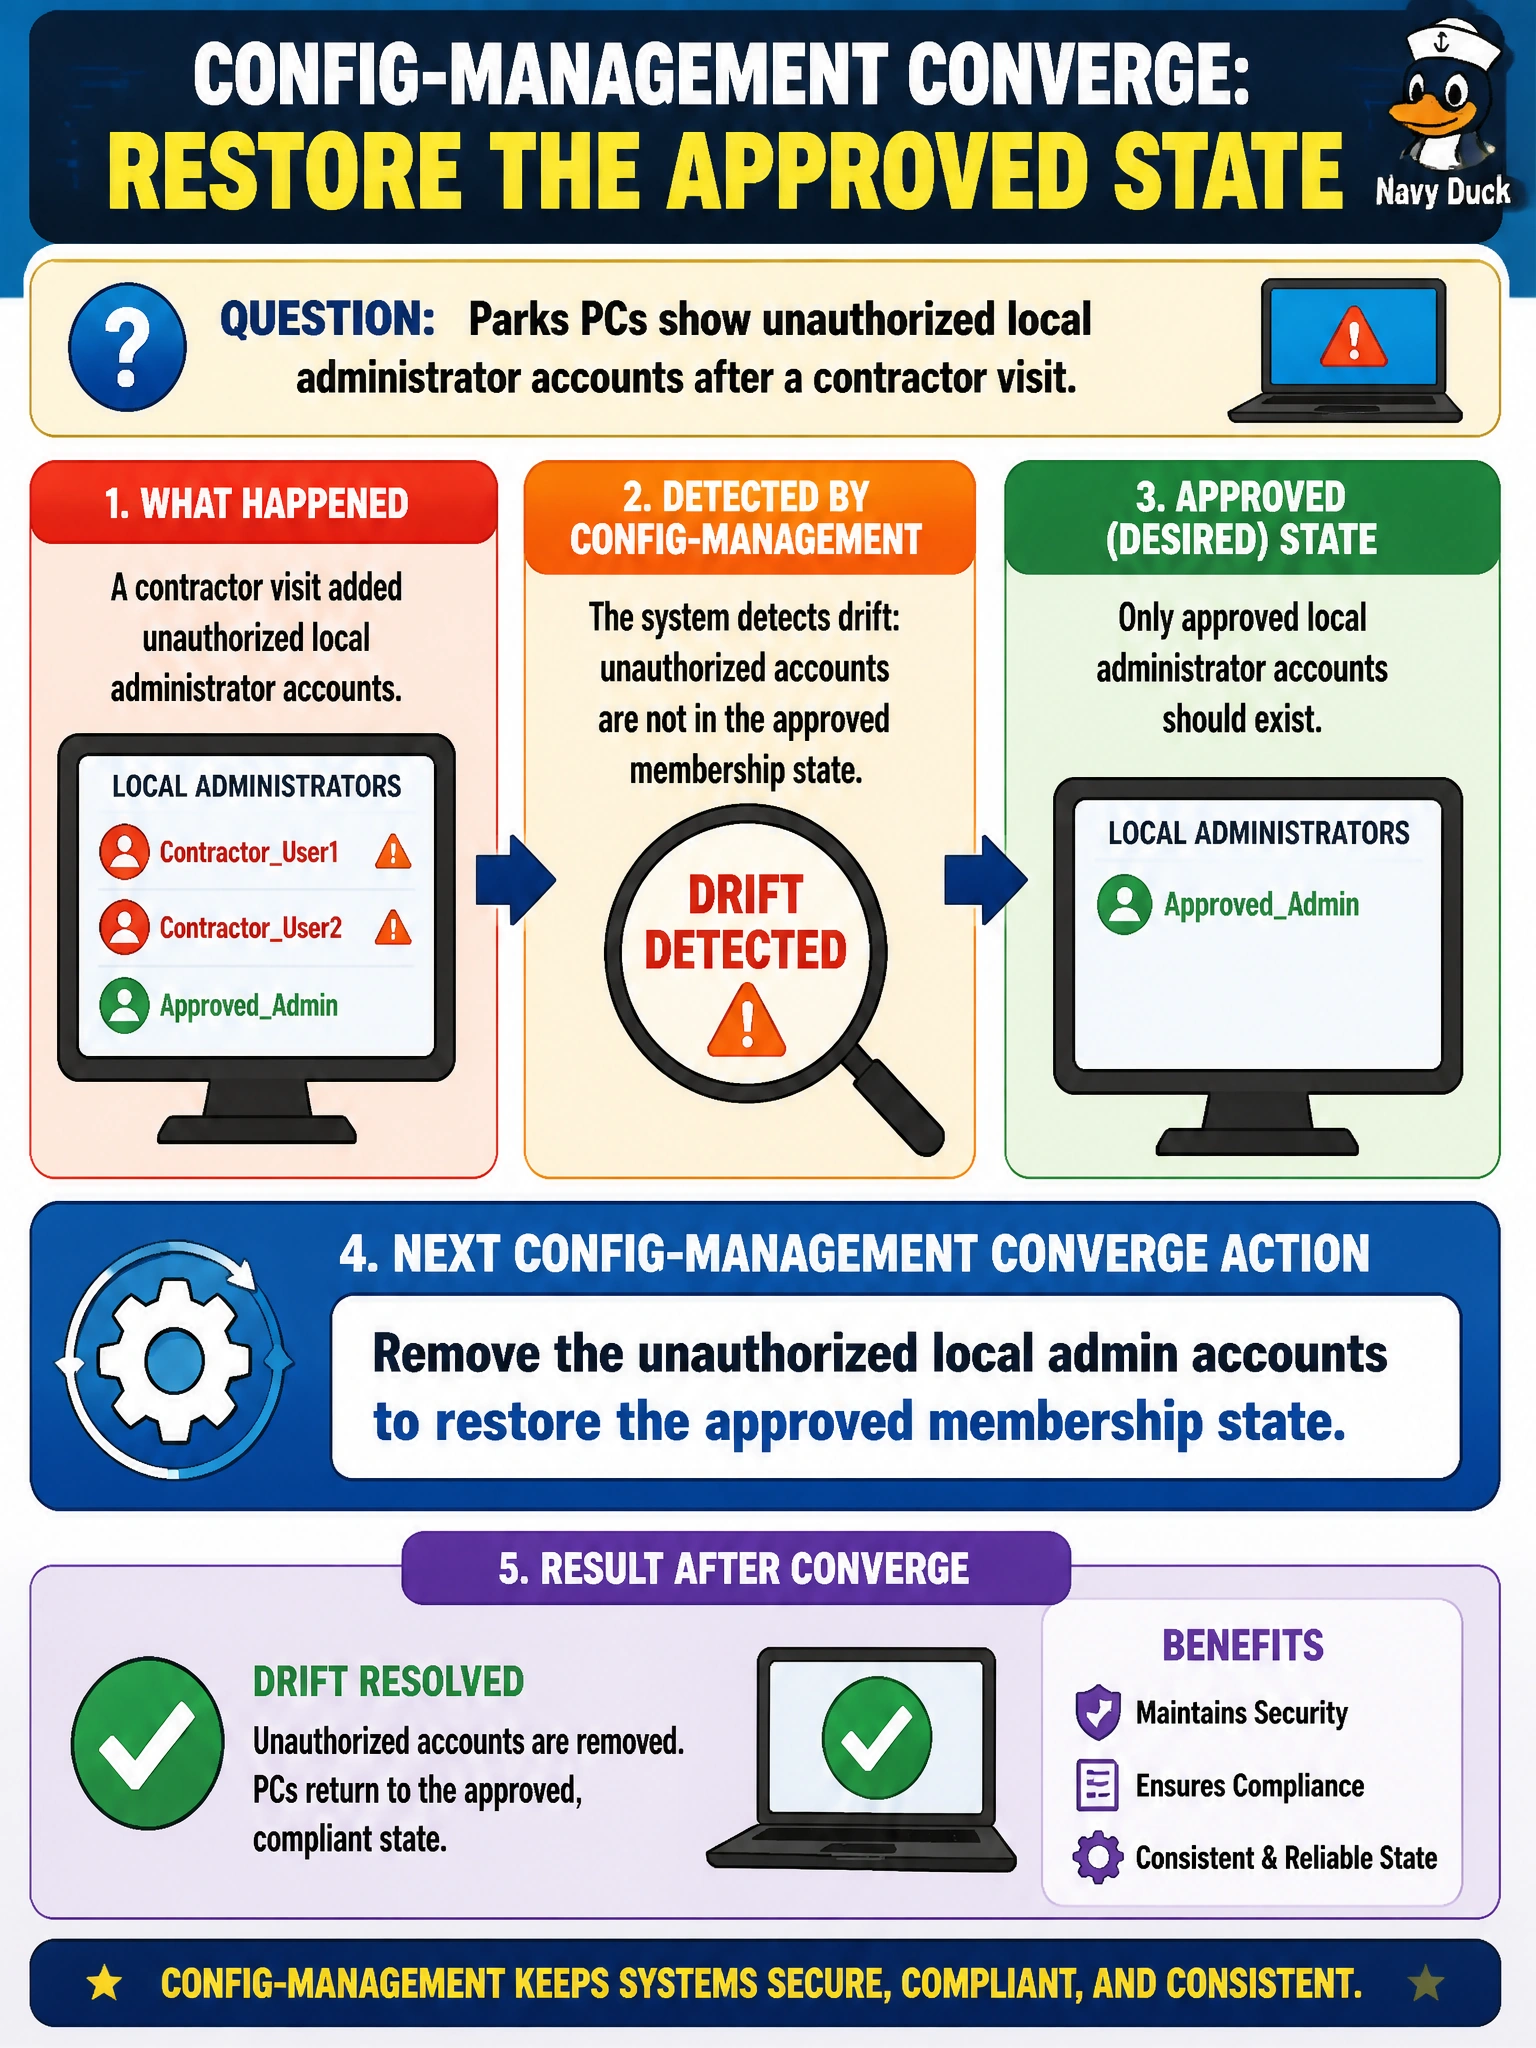
Parks PCs show unauthorized local administrator accounts after a contractor visit. What should the next config-management converge do?
Select an answer to reveal the explanation.
Short Explanation
You can think of unauthorized local admins as extra keys left under the mat after the contractor leaves. The next converge should restore the approved membership by removing those accounts; making the contractor a permanent admin spreads the risk, while disabling converge or granting Domain Admins kiosk login does not fix the unauthorized membership.
Full Explanation
When parks PCs show unauthorized local administrator accounts after a contractor visit, the next config-management converge should remove those accounts and restore the approved membership state. Desired-state enforcement for local groups lets municipal endpoints recover from temporary vendor access that was not meant to persist. Adding the contractor’s account as a permanent local administrator on every PC expands standing privilege beyond the visit and creates a risk from persistent, widely distributed access. Disabling converge jobs so local admins can never be changed again freezes drift in place and removes the control needed to correct the unauthorized membership. Granting Domain Admins interactive login on public-facing kiosks greatly increases the potential blast radius and does not address the local accounts. Exam caveat: remediation should follow the approved break-glass process; do not preserve unauthorized access merely because it may have been used for support. Operational check: inventory local Administrators group membership on the affected parks PCs, run converge, confirm the unauthorized accounts are gone and required support accounts remain in line with the approved baseline, then check for renewed membership drift after future contractor visits.