
A municipal IT board wants IAM users who still sign in with passwords to meet stronger authentication rules for length, complexity, and change cadence. Which IAM feature addresses that requirement at Cloud Practitioner depth?
Select an answer to reveal the explanation.
Short Explanation
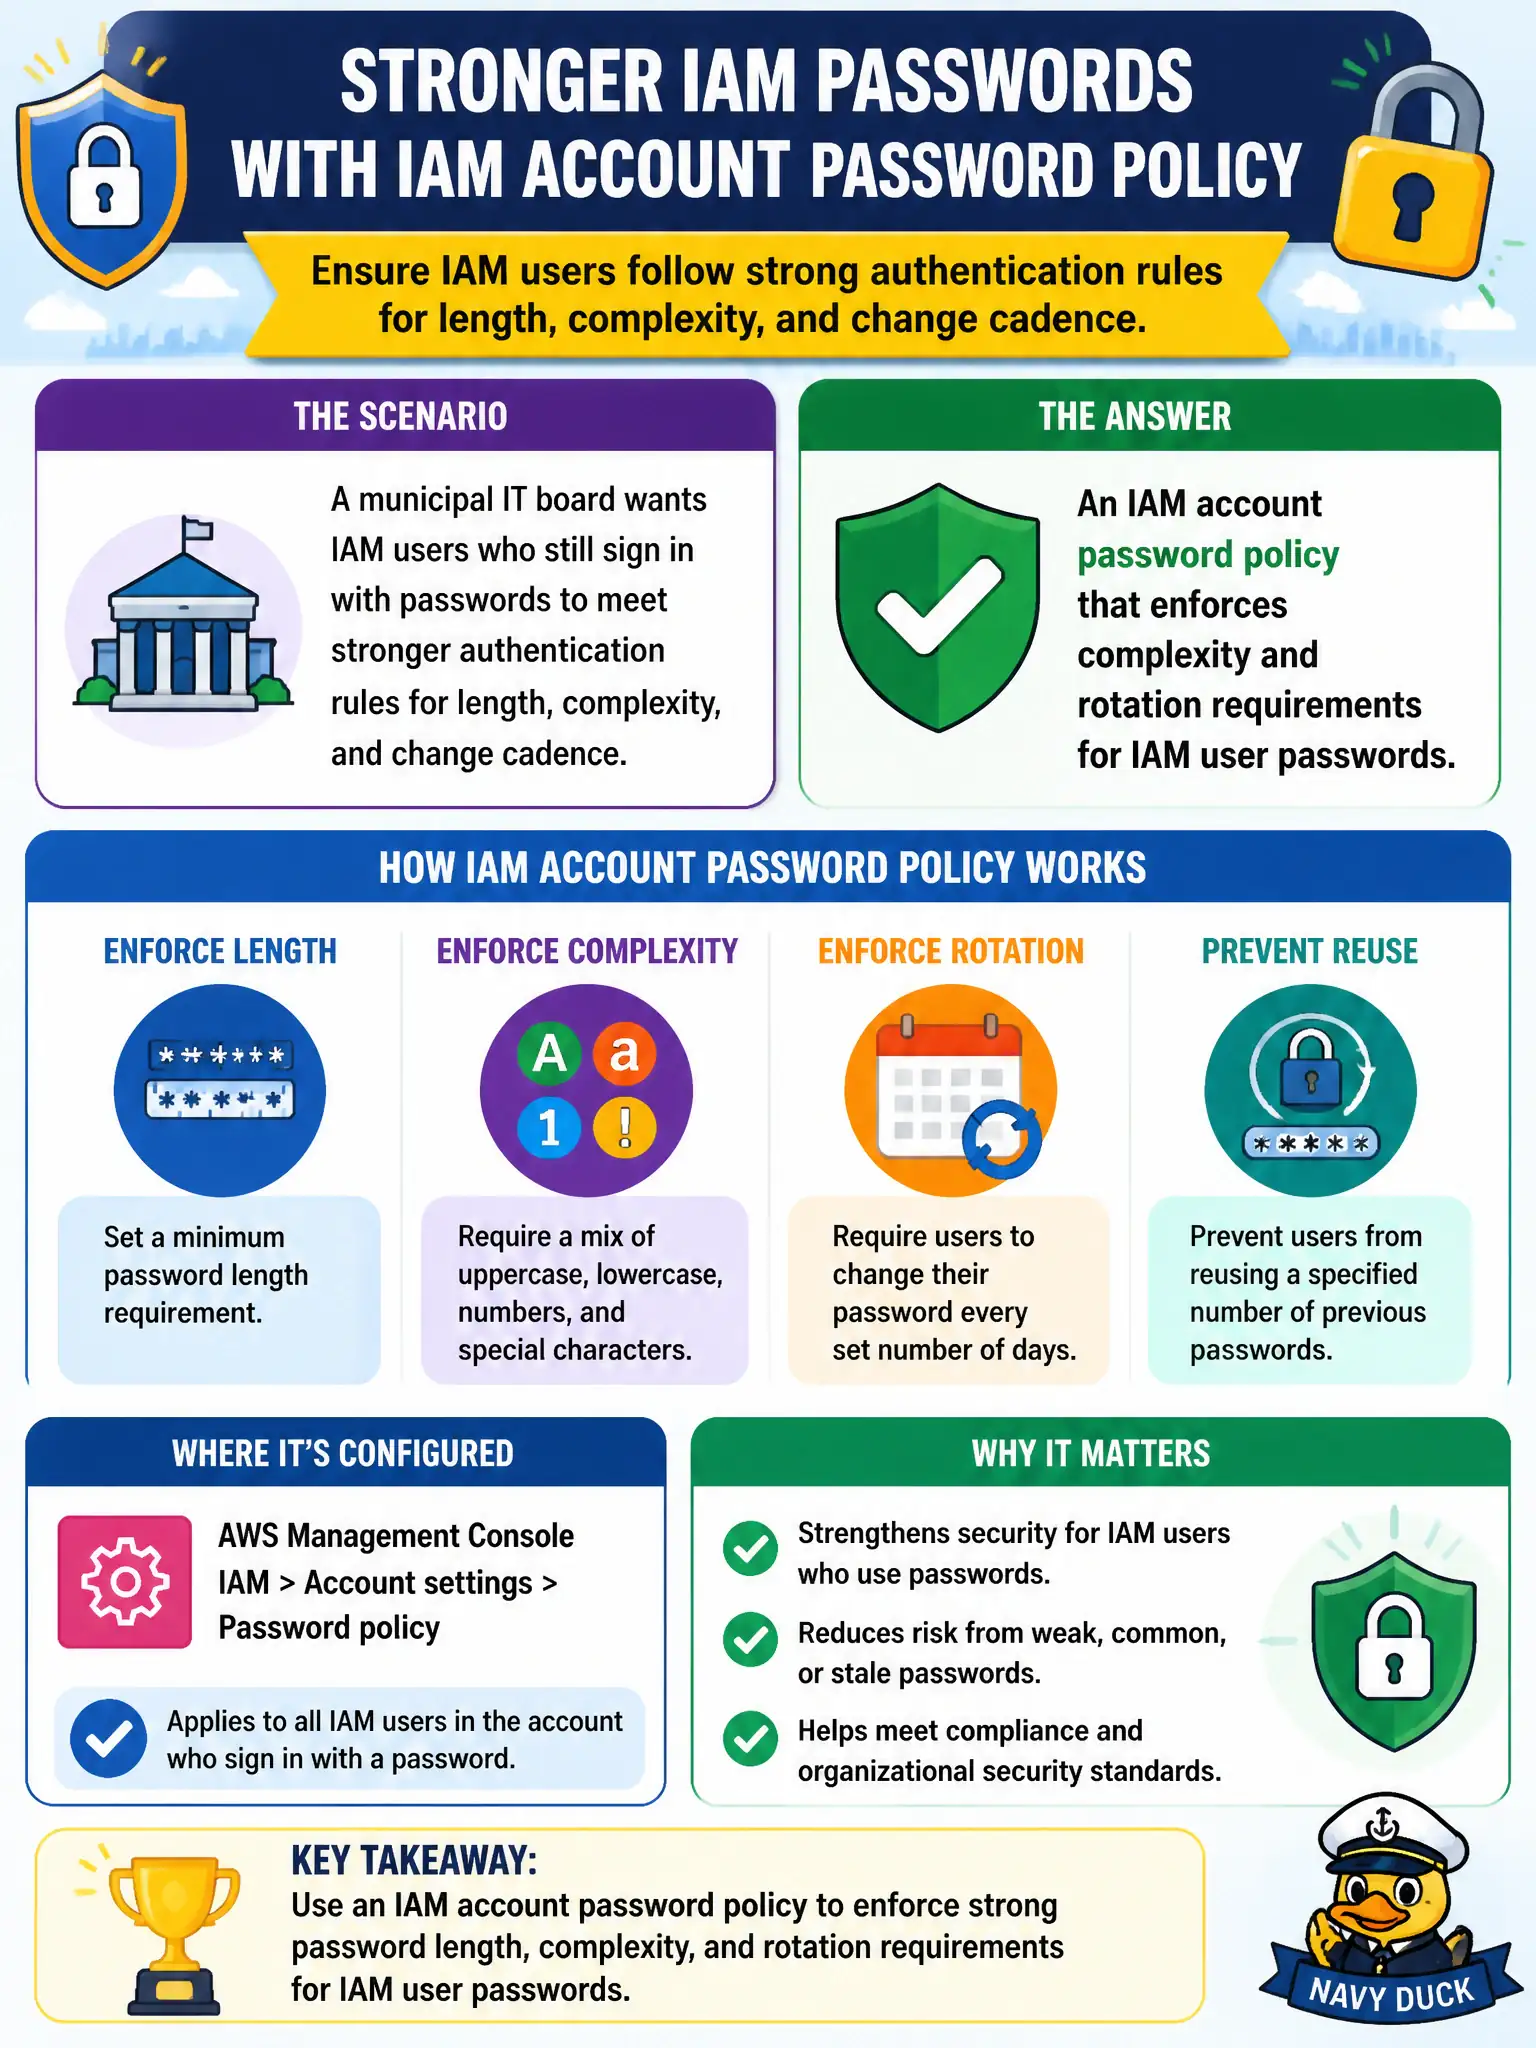
Password policy is the account's rulebook for how strong IAM user passwords must be — think minimum length, symbols, and how often they expire. Flip those knobs once at the account level and every IAM user password has to live up to them.
Full Explanation
An IAM account password policy enforces complexity and rotation requirements for IAM user passwords, which is what a municipal IT board wants when human users still sign in with passwords that must meet stronger length, complexity, and change cadence rules. Password policy is the account's rulebook — flip those knobs once and IAM user passwords must live up to them. VPC Flow Logs record network traffic metadata, not a password-complexity engine. S3 bucket versioning versions objects; it is not how IAM credential files are governed. AWS WAF rate rules protect web applications; applying them to "the IAM console URL" is not the Cloud Practitioner answer for IAM password strength. Distractors fail by pointing at networking logs, object versioning, and WAF instead of the IAM password policy feature. Exam caveat: password policy hardens password-based sign-in but should be paired with MFA; many organizations further prefer federation so fewer long-lived IAM passwords exist. Operational check: set minimum length and complexity, enable expiration per policy, prevent reuse as required, communicate changes to finance and admin users, and verify new passwords meet the policy during next login cycles.