
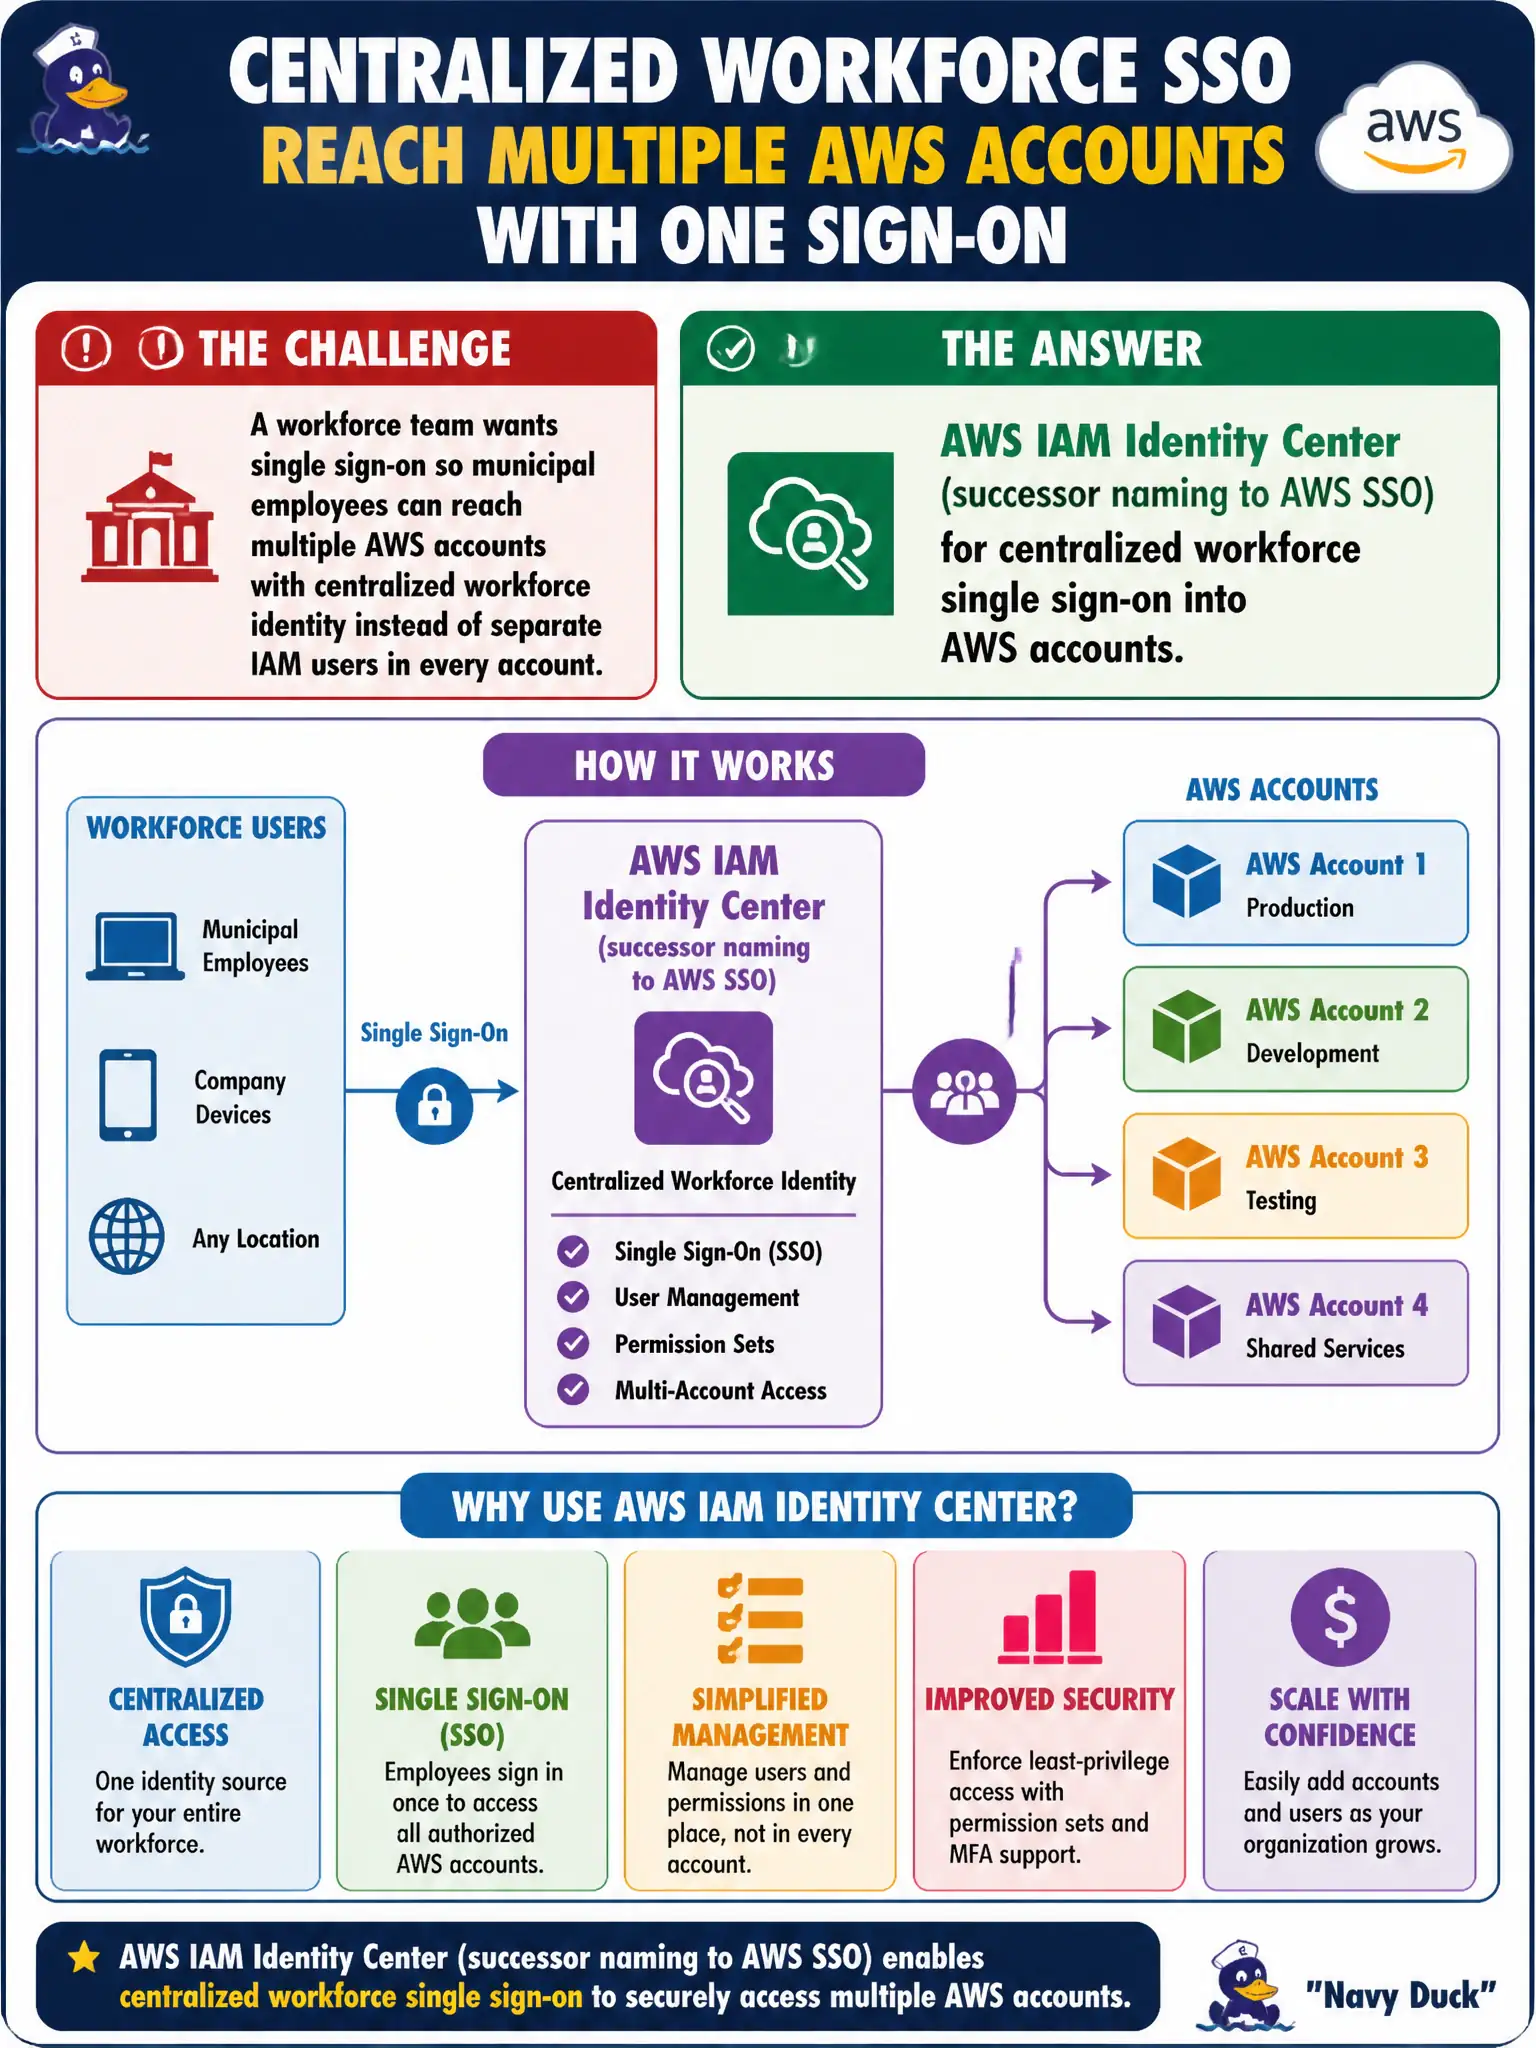
A workforce team wants single sign-on so municipal employees can reach multiple AWS accounts with centralized workforce identity instead of separate IAM users in every account. Which AWS capability is intended for that workforce SSO pattern?
Select an answer to reveal the explanation.
Short Explanation
IAM Identity Center is the front desk badge system for the workforce — one SSO experience into many AWS accounts instead of breeding IAM users everywhere. S3 websites, Snowcone devices, and Instance Connect solve hosting, edge compute/storage, and instance SSH access — not workforce SSO.
Full Explanation
AWS IAM Identity Center (successor naming associated with AWS SSO) is intended for centralized workforce single sign-on into AWS accounts so municipal employees can reach multiple accounts without separate IAM users everywhere. It is the front desk badge system for the workforce. Amazon S3 static website hosting is not an identity provider for all accounts. AWS Snowcone is a rugged edge device, not a requirement to federate browser logins. Amazon EC2 Instance Connect helps with instance SSH access patterns; it is not the only supported multi-account workforce SSO service. Distractors fail by confusing hosting, edge hardware, and instance connectivity with workforce SSO. Exam caveat: Identity Center still requires careful permission set design and joiner-mover-leaver processes tied to the city's identity source. Operational check: connect the corporate IdP, define permission sets per job function, assign users or groups to accounts, enforce MFA, review assignments quarterly, and retire standing IAM users that duplicated the same workforce access pattern. In practice, map AD or IdP groups to Identity Center permission sets by department, then retire duplicate IAM users once SSO logins are proven for each civic team.