
A new hire describes AWS Security Hub as a packet-filtering firewall that should replace security groups for a library website. What is the more accurate purpose of Security Hub?
Select an answer to reveal the explanation.
Short Explanation
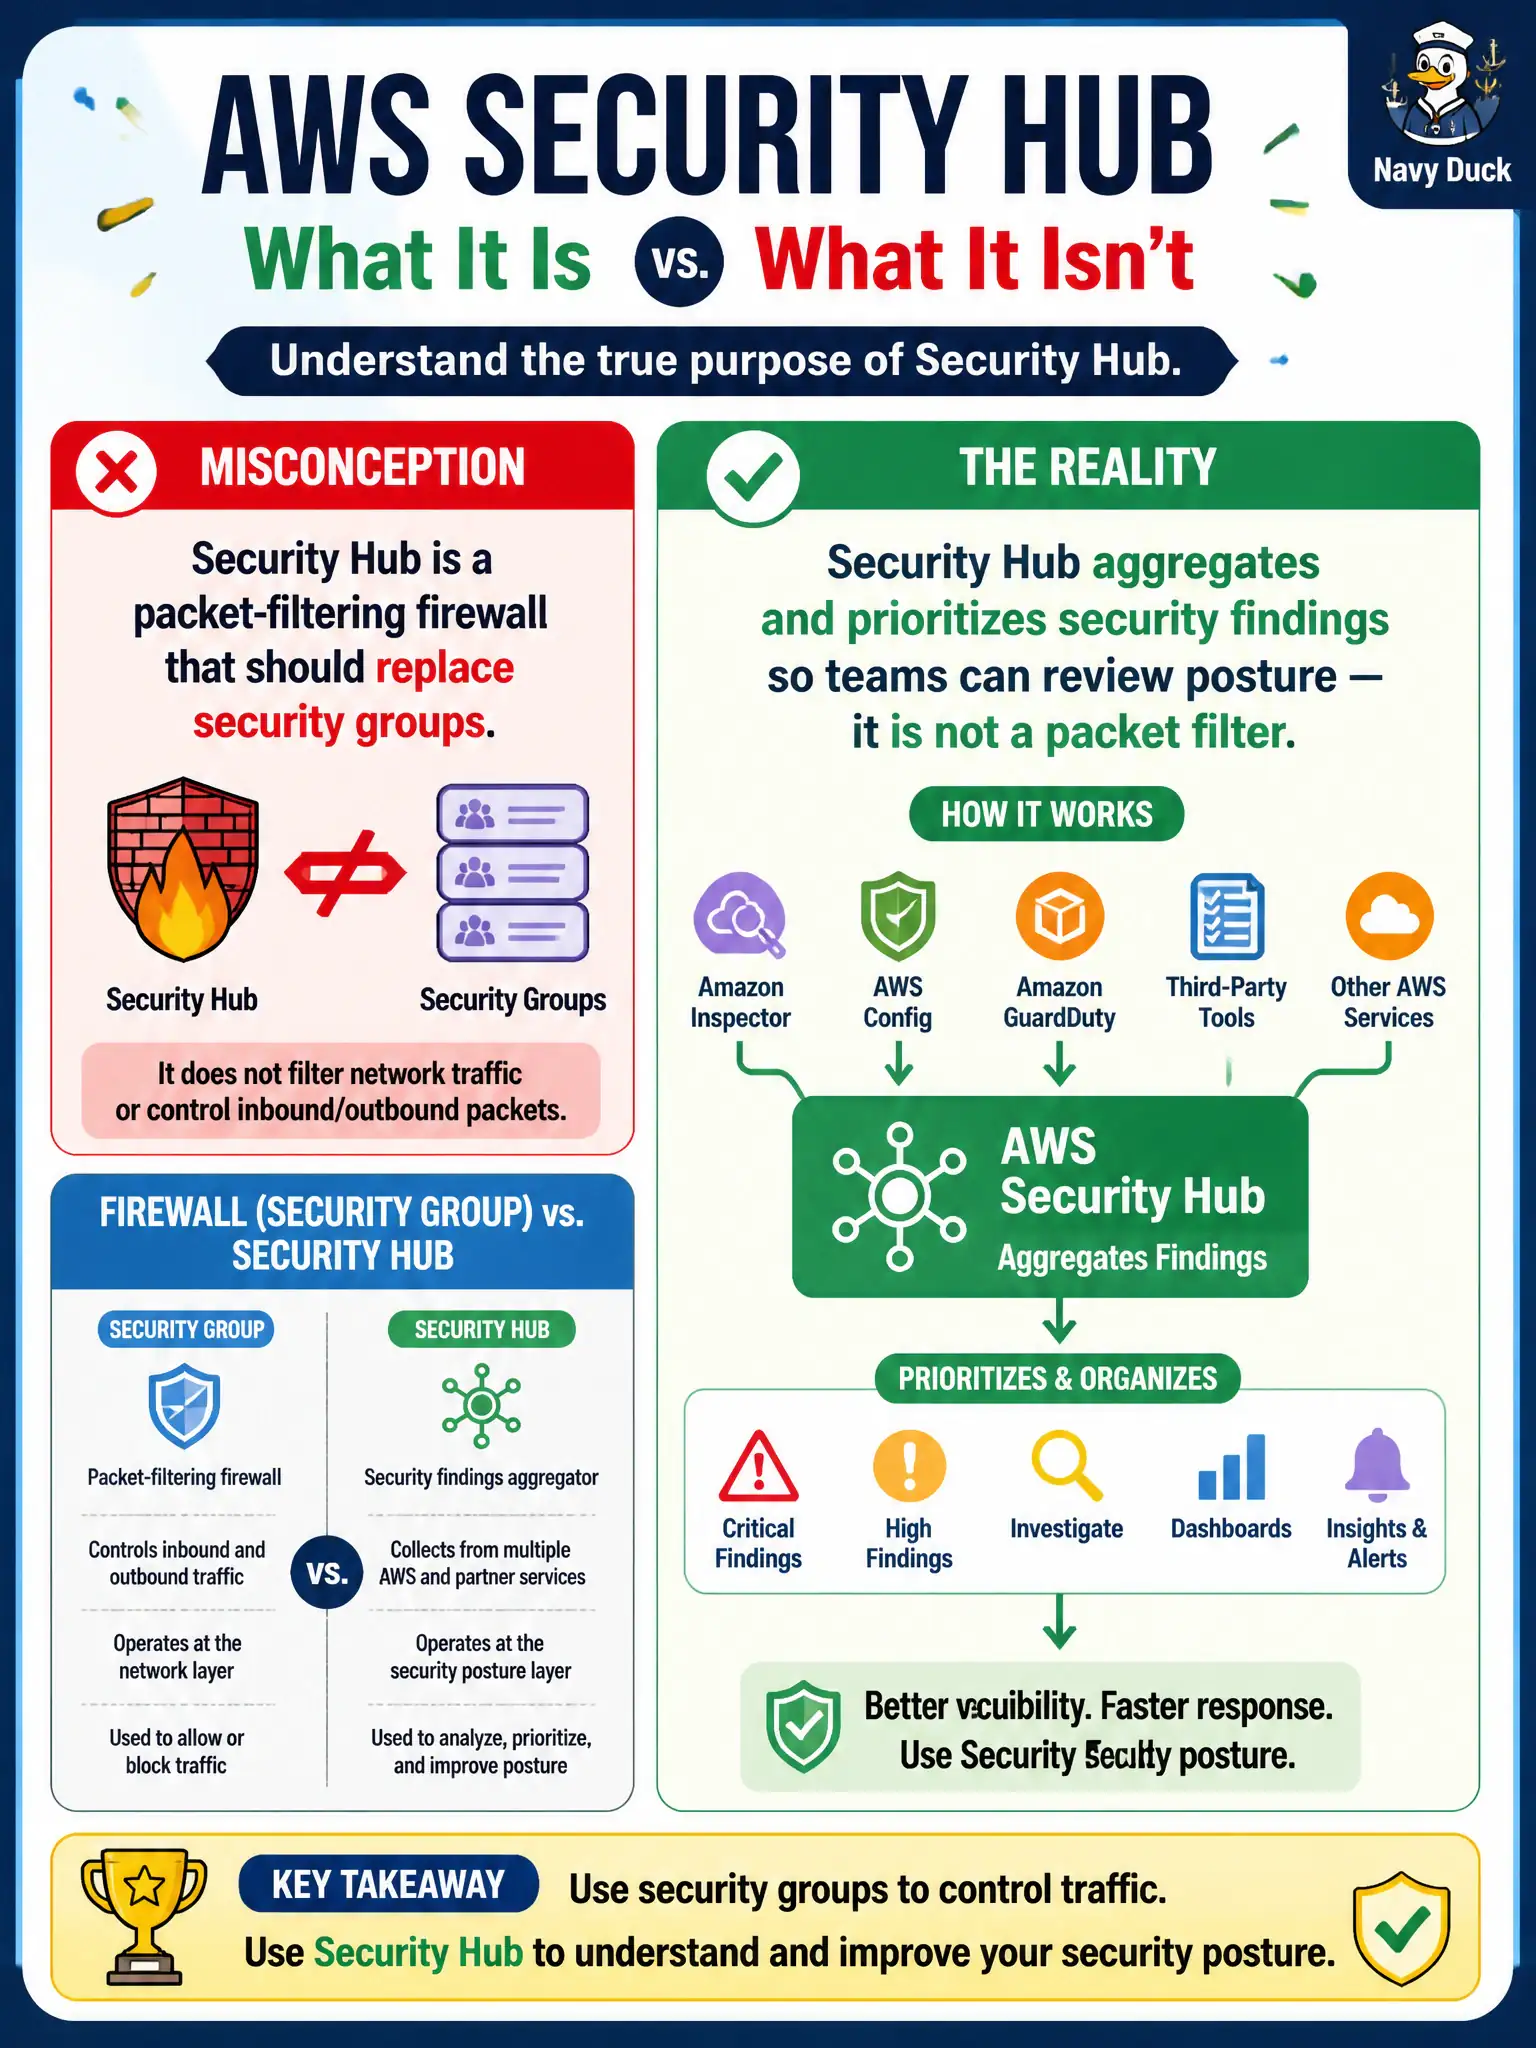
Security Hub is the findings inbox and priority board, not the door lock on each VPC. Security groups and NACLs still handle packet filtering; Hub helps you see and prioritize what GuardDuty, Inspector, and friends reported. Calling Hub a firewall mixes the aggregator with the filter.
Full Explanation
AWS Security Hub aggregates and prioritizes security findings so teams can review posture — it is not a packet filter on each VPC. Security Hub is the findings inbox and priority board for municipal security operations, while security groups and network ACLs remain the instance- and subnet-level traffic filters that actually allow or deny packets for permitting and utility systems. Descriptions that cast Security Hub as replacing security groups, as scrubbing DDoS floods, or as automatically rewriting every firewall rule misunderstand the service and create false comfort in architecture reviews. Exam caveat: aggregation without assigned owners produces dashboards that never clear; Hub complements preventive network and IAM controls rather than deleting the need for them under shared responsibility. Operational check: enable Security Hub and integrated providers in organization accounts, map finding types to accountable teams (IAM, network, vulnerability), track remediation SLAs for high-priority items affecting resident data systems, keep security group reviews on a monthly cadence, and use Hub insights in leadership reporting without claiming Hub itself blocks packets at the elastic network interface.