
A county IT lead confuses Amazon Inspector with AWS Shield while planning controls for web apps and compute. Which statement correctly separates their purposes?
Select an answer to reveal the explanation.
Short Explanation
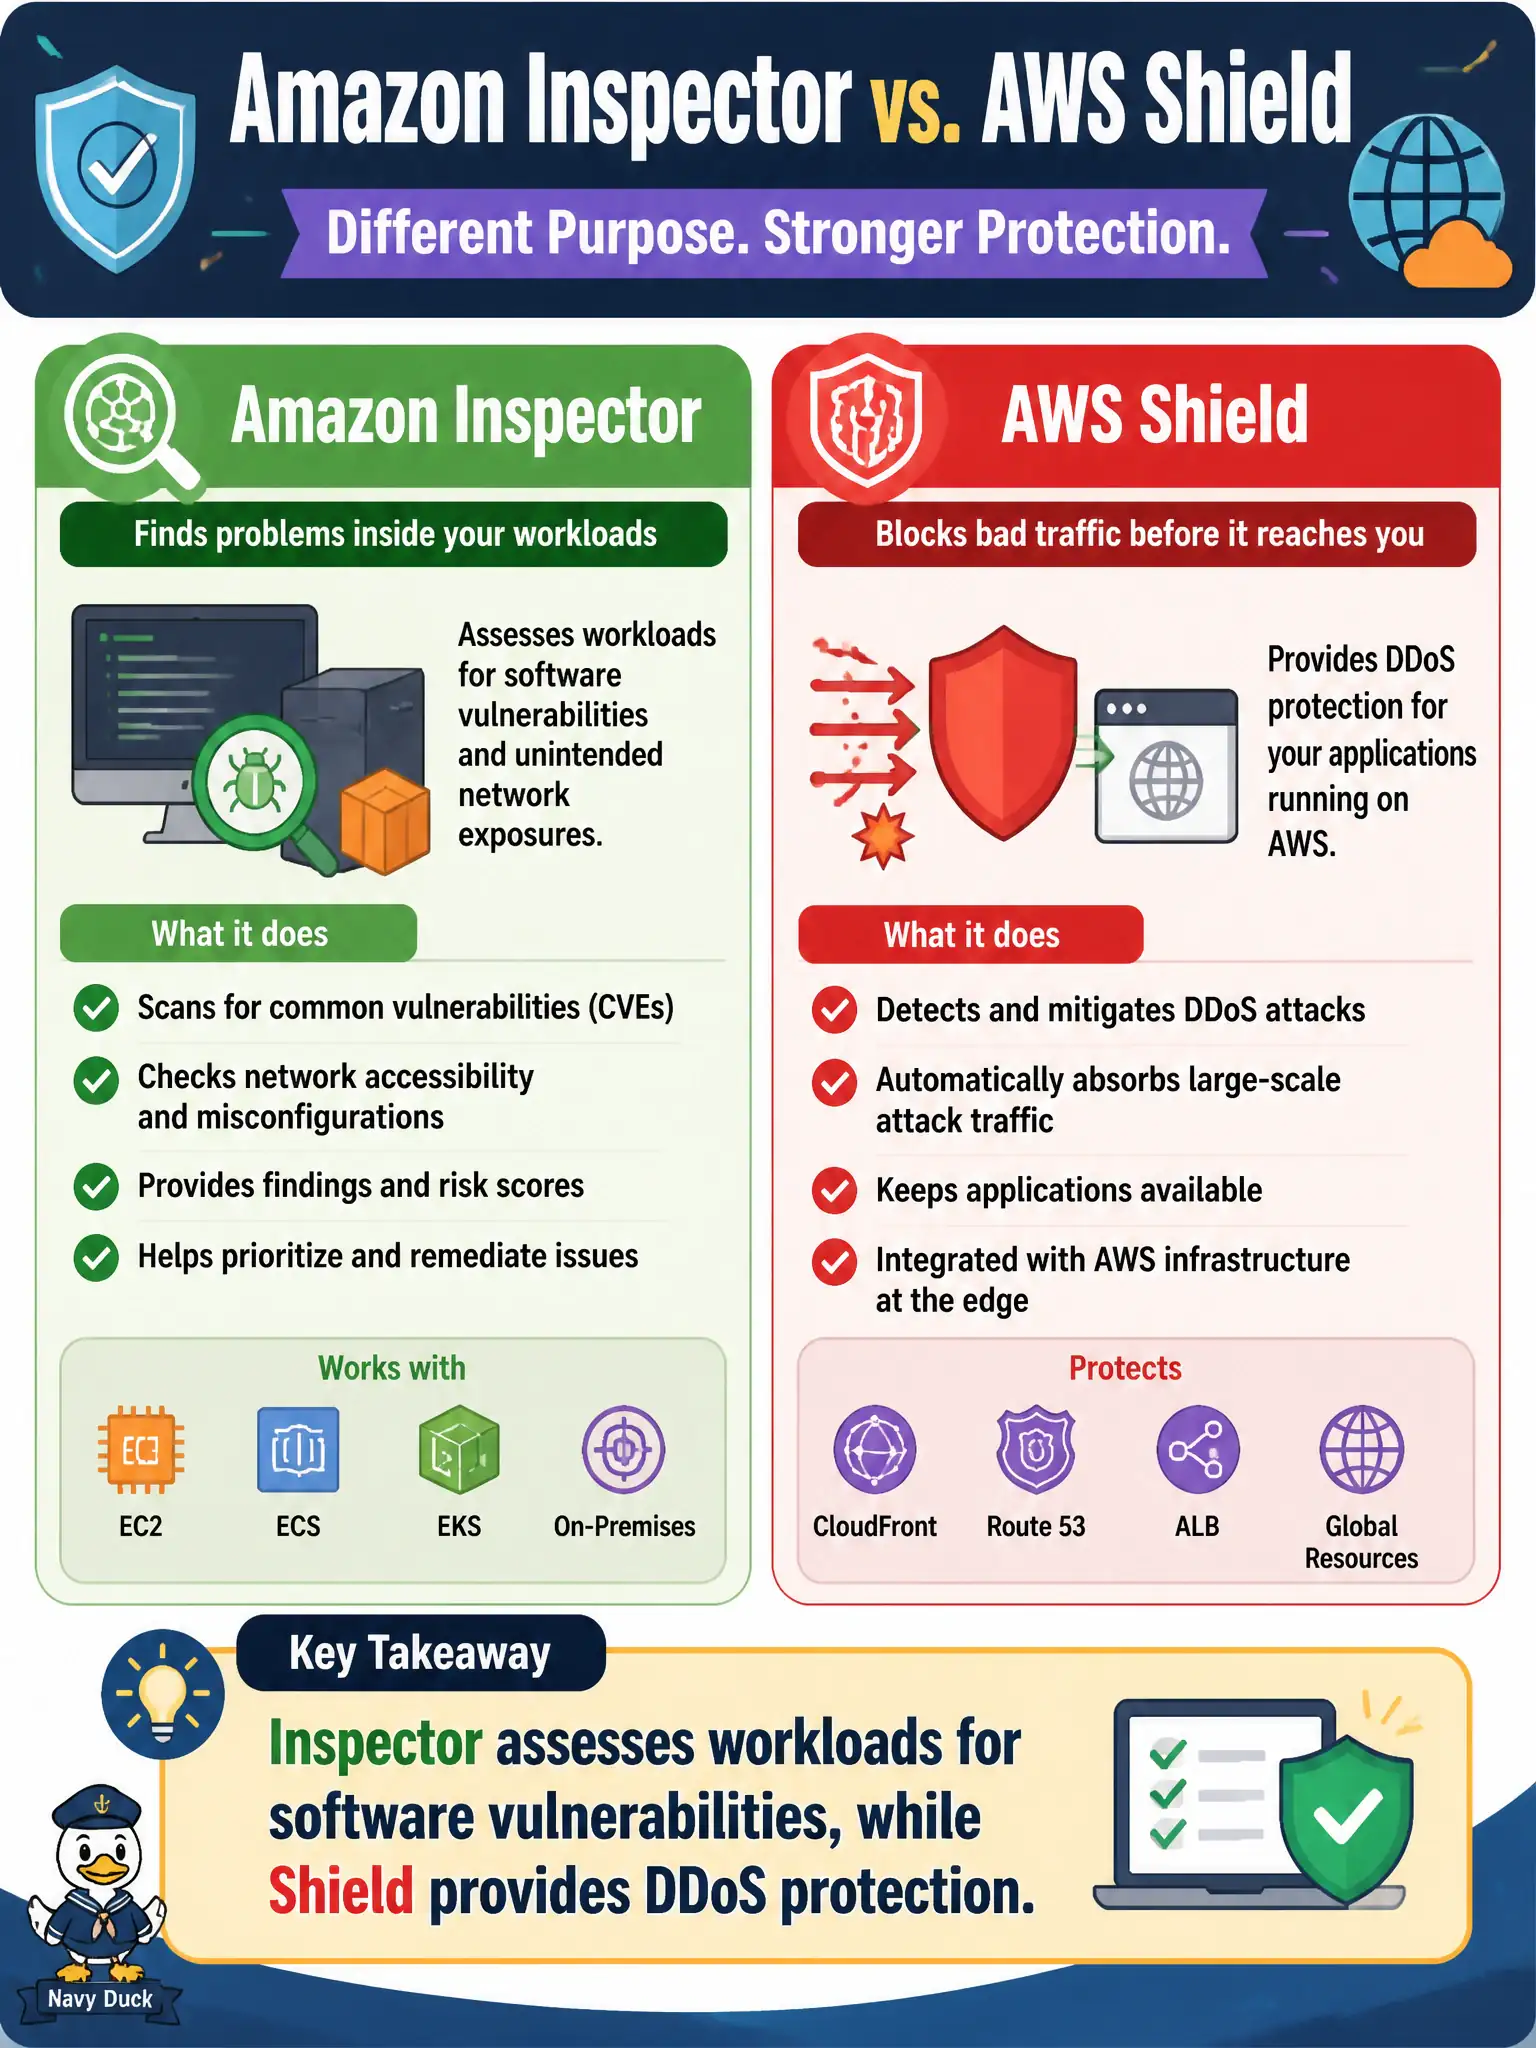
Inspector is the building inspector looking for weak locks and cracked windows on your workloads; Shield is the berm against a flood of junk traffic. Swap those jobs in your head and you pick the wrong tool every time.
Full Explanation
Amazon Inspector assesses workloads for software vulnerabilities, while AWS Shield provides DDoS protection. Inspector is the building inspector looking for weak locks and cracked windows on EC2 and related workloads; Shield is the berm against a flood of unwanted traffic aiming at public citizen portals. Swapping those missions on an exam — treating Inspector as the DDoS service or Shield as the CVE scanner — is a classic trap. Pairings that assign vulnerability assessment to Artifact PDFs or DDoS mitigation to Config drift rules similarly mismatch purposes and waste precious exam minutes. Exam caveat: vulnerability management and availability protection are complementary under shared responsibility; patching guests does not absorb volumetric floods, and Shield does not patch outdated packages on city instances. Operational check: schedule Inspector assessments on fleets processing sensitive data or facing the internet, drive patch SLAs from findings with clear owners, architect public apps to benefit from Shield, rehearse DDoS contacts separately from vuln patch windows, and document separate escalation paths so tickets do not bounce between network and platform teams during an incident.