
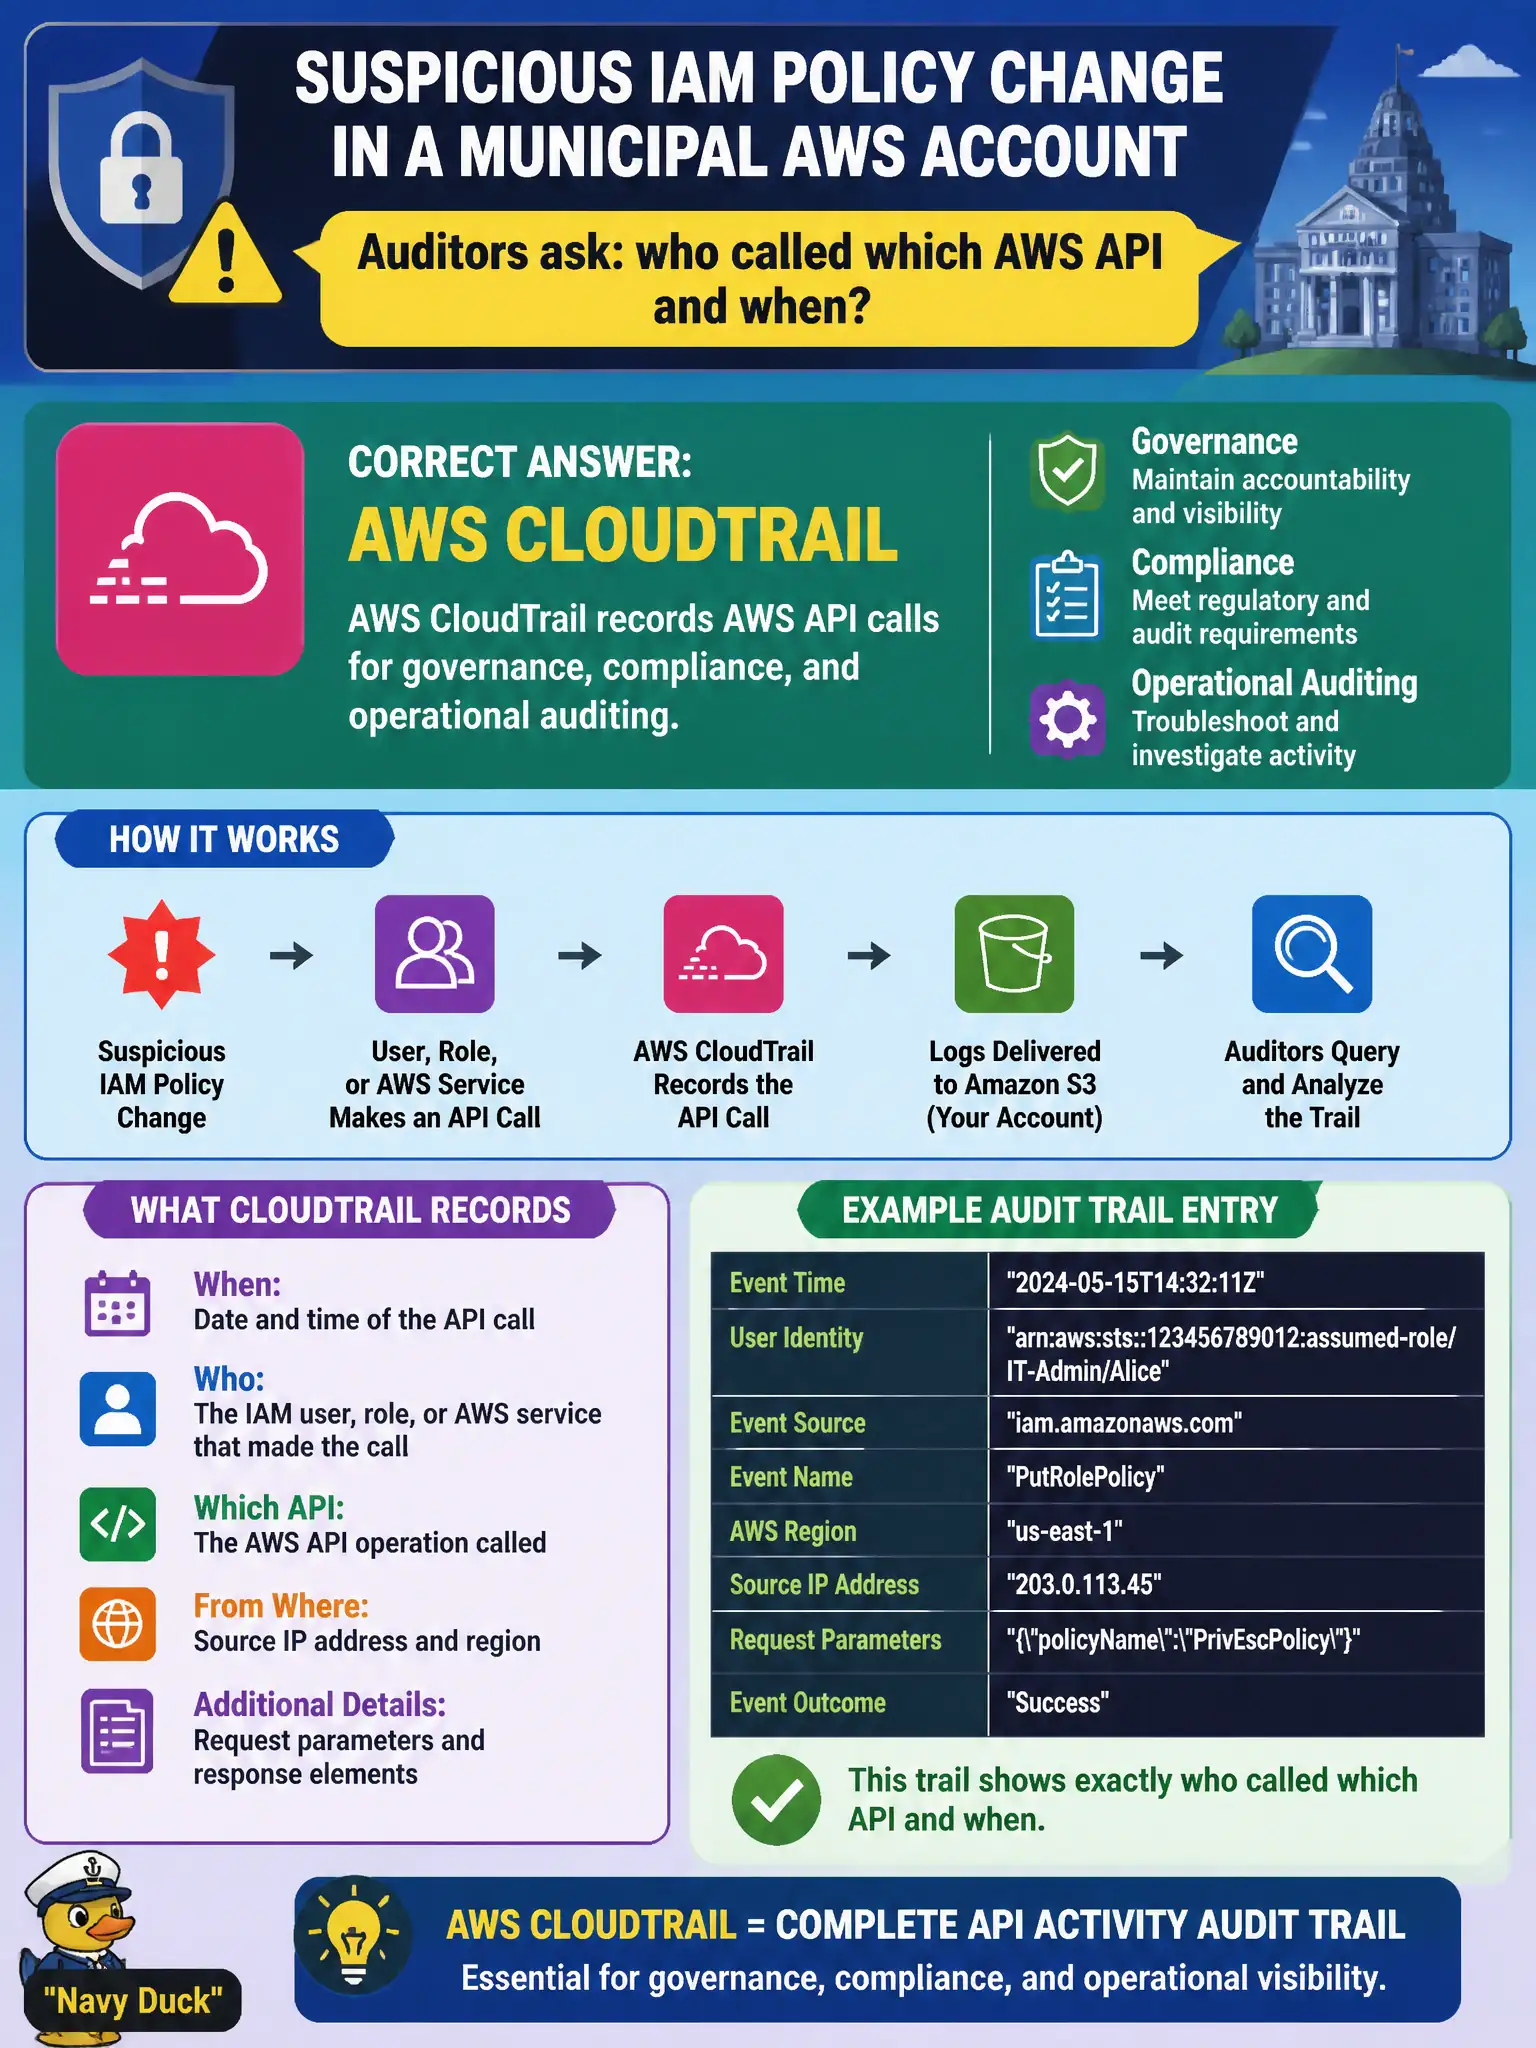
After a suspicious IAM policy change in a municipal AWS account, auditors ask who called which AWS API and when. Which service provides that account API activity audit trail?
Select an answer to reveal the explanation.
Short Explanation
When someone rearranges the keys in city hall overnight, you want the visitor log — CloudTrail is that visitor log for AWS API calls. CloudWatch alarms watch health; Inspector looks for vulnerabilities; Shield fights floods. For who-did-what on the control plane, start with CloudTrail.
Full Explanation
AWS CloudTrail records AWS API calls for governance, compliance, and operational auditing, which is what auditors need after a suspicious IAM policy change when they ask who called which API and when. CloudTrail is the visitor log for control-plane activity in a municipal account. Amazon CloudWatch Alarms watch health thresholds; they do not store every signed API request as immutable evidence by default in place of CloudTrail. AWS Shield Standard addresses DDoS protection and does not log every console click as a DDoS event for IAM forensics. Amazon Inspector assesses workloads for vulnerabilities; it is not the primary source of who-changed-what API history. Distractors fail by swapping monitoring alarms, DDoS protection, and vulnerability assessment for an API activity audit trail. Exam caveat: enable trails broadly across accounts and Regions that matter, protect log storage from tampering or deletion, and remember that logging without review still leaves investigative gaps. Operational check: verify organization-wide or multi-account trail coverage, send logs to a restricted durable bucket, enable log file validation where appropriate, alert on CloudTrail configuration stops, and practice retrieving events around IAM policy modifications that affect civic identity boundaries.