
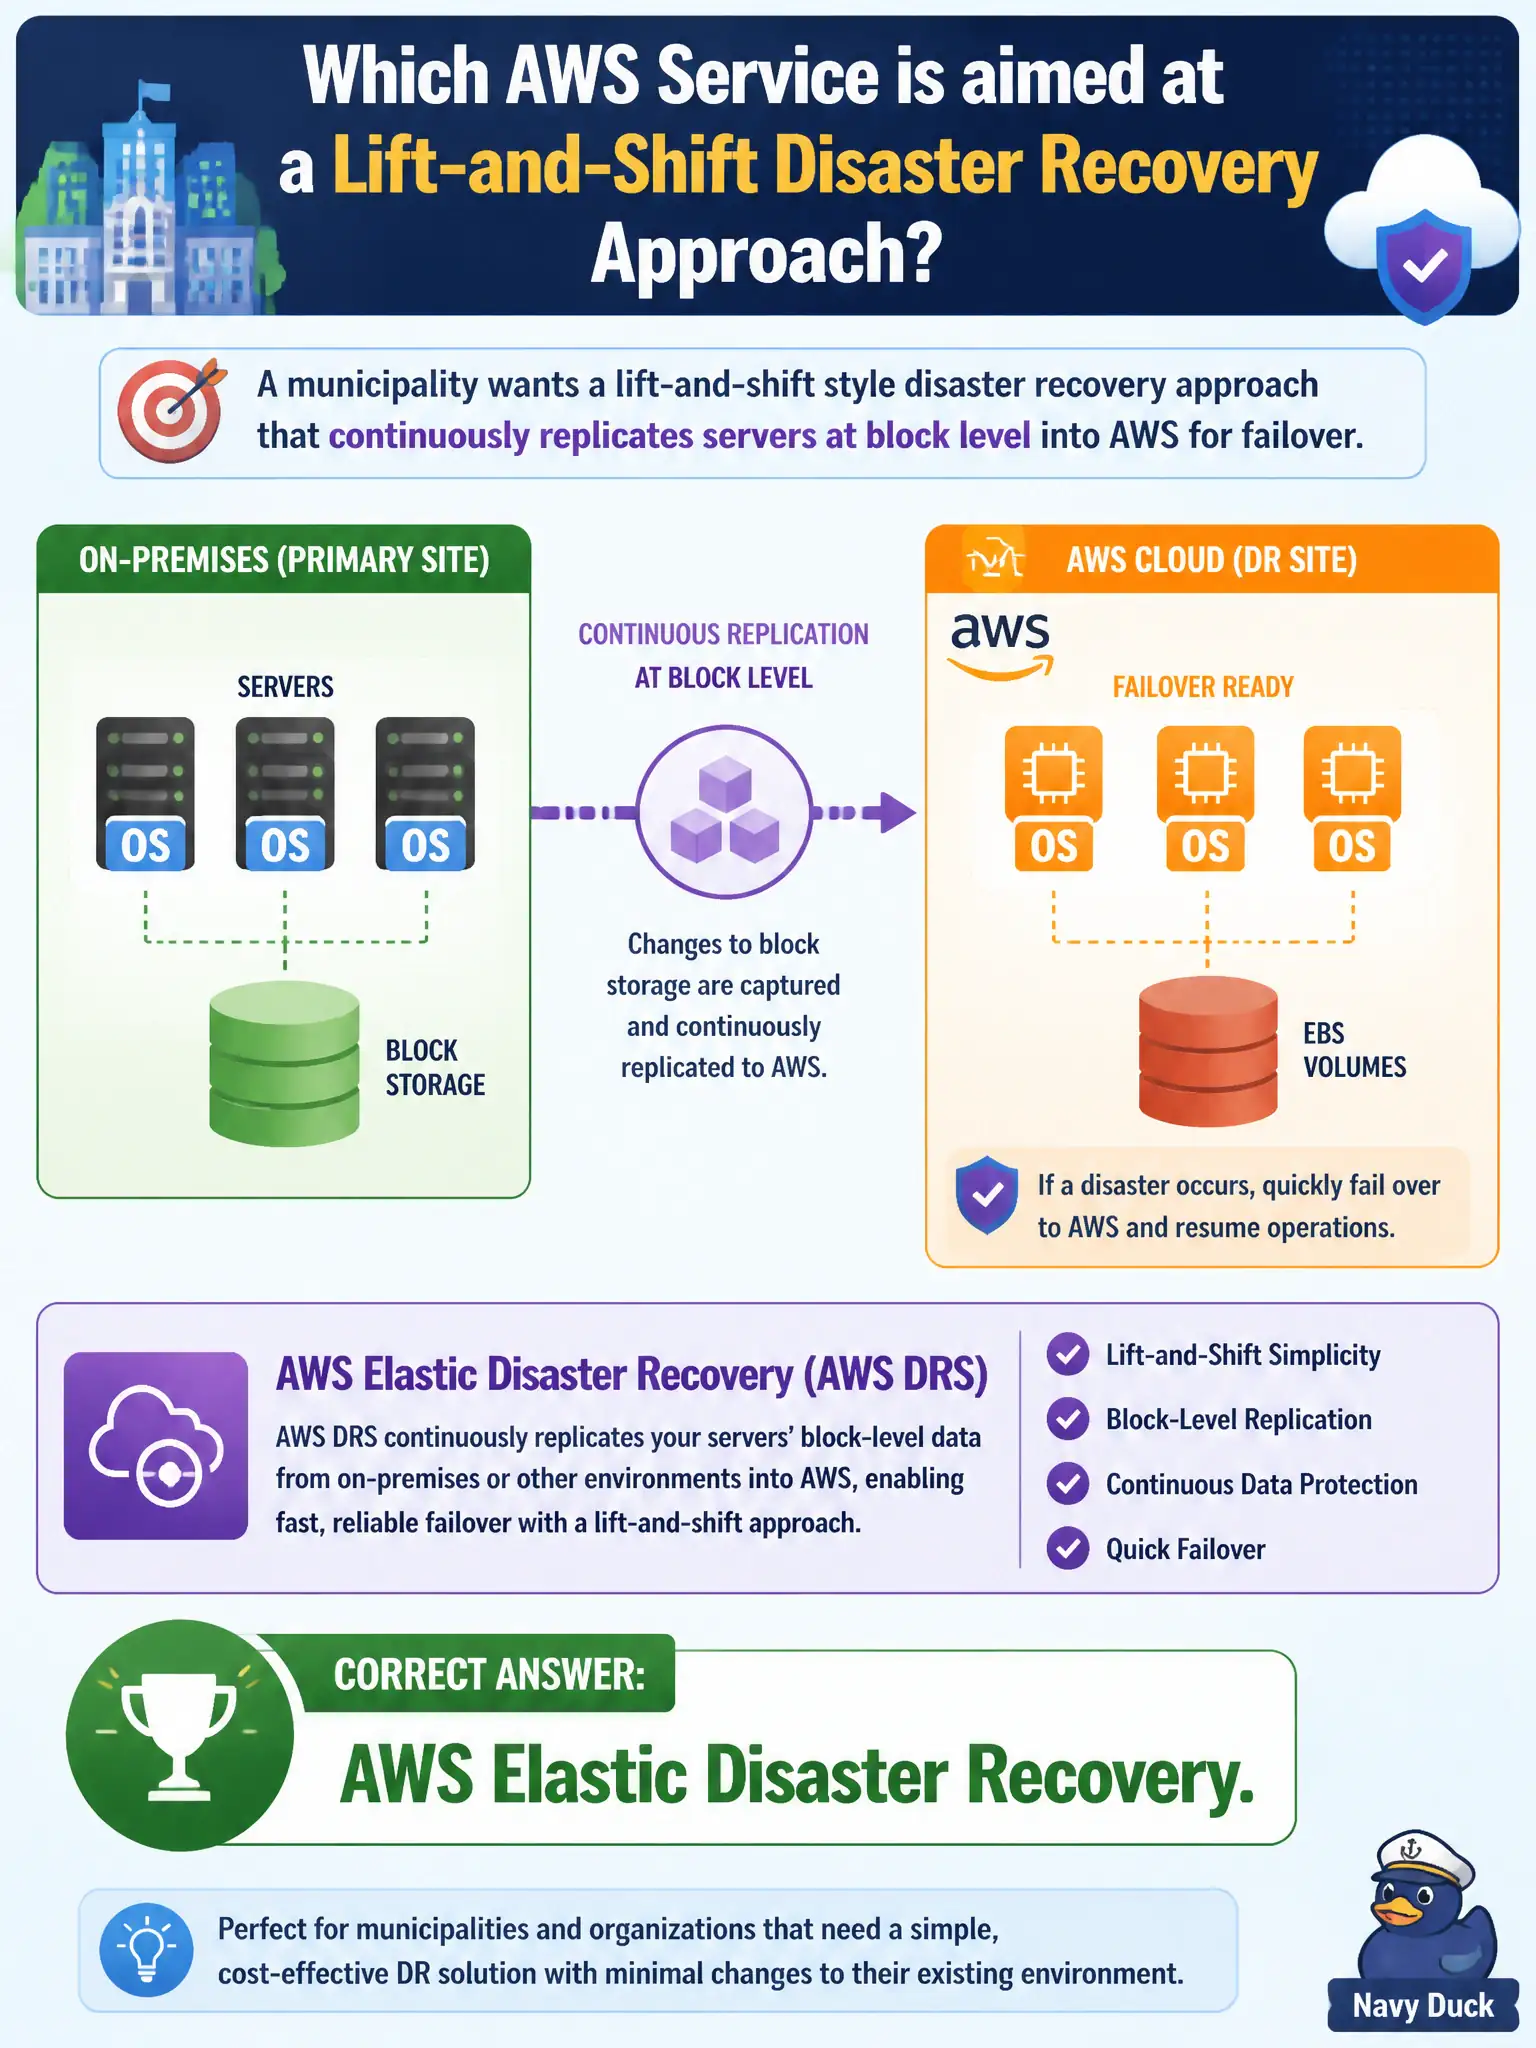
A municipality wants a lift-and-shift style disaster recovery approach that continuously replicates servers at block level into AWS for failover. Which AWS service is aimed at that DR pattern?
Select an answer to reveal the explanation.
Short Explanation
Block-level lift-and-shift DR is the "keep a warm twin in AWS" story. AWS Elastic Disaster Recovery is the service aimed at continuous replication and failover for that pattern—identify it when the brief says replicate servers for disaster recovery, not when you only need a dashboard or a budget alert.
Full Explanation
Municipalities seeking a lift-and-shift style disaster recovery approach that continuously replicates servers at block level into AWS for failover should identify AWS Elastic Disaster Recovery. That service is aimed at continuous block-level replication of source servers into a staging area in AWS and enabling failover when a disaster or drill requires cutting over. It matches civic DR briefs that say "replicate our servers into AWS and be ready to fail over" rather than rebuilding only from nightly file copies without a dedicated DR replication control plane.
Amazon QuickSight SPICE capacity is for BI in-memory acceleration, not server replication DR. AWS Budgets anomaly detection watches cost patterns, not block-level failover. Amazon Polly neural voices can narrate runbooks but do not replicate disks. These distractors sit in analytics, cost, and speech domains unrelated to continuous server replication DR.
Exam caveat: Distinguish Elastic Disaster Recovery (block-level replication/failover) from AWS Backup (backup/restore policies), from pilot-light/warm-standby architecture patterns described in whitepapers, and from database-native replication features. CLF asks you to identify the service name for the lift-and-shift continuous replication DR pattern.
Operational check for the municipality: inventory critical on-premises or source servers, install replication agents per AWS guidance, validate continuous replication health, run a failover drill into AWS with DNS or routing cutover procedures, measure RPO/RTO against policy, and document failback. Ensure network connectivity and IAM permissions for the DR account are ready before an actual civic emergency.