
A policy should restrict only egress and leave ingress unspecified intentionally. What must be set so egress rules are honored as intended?
Select an answer to reveal the explanation.
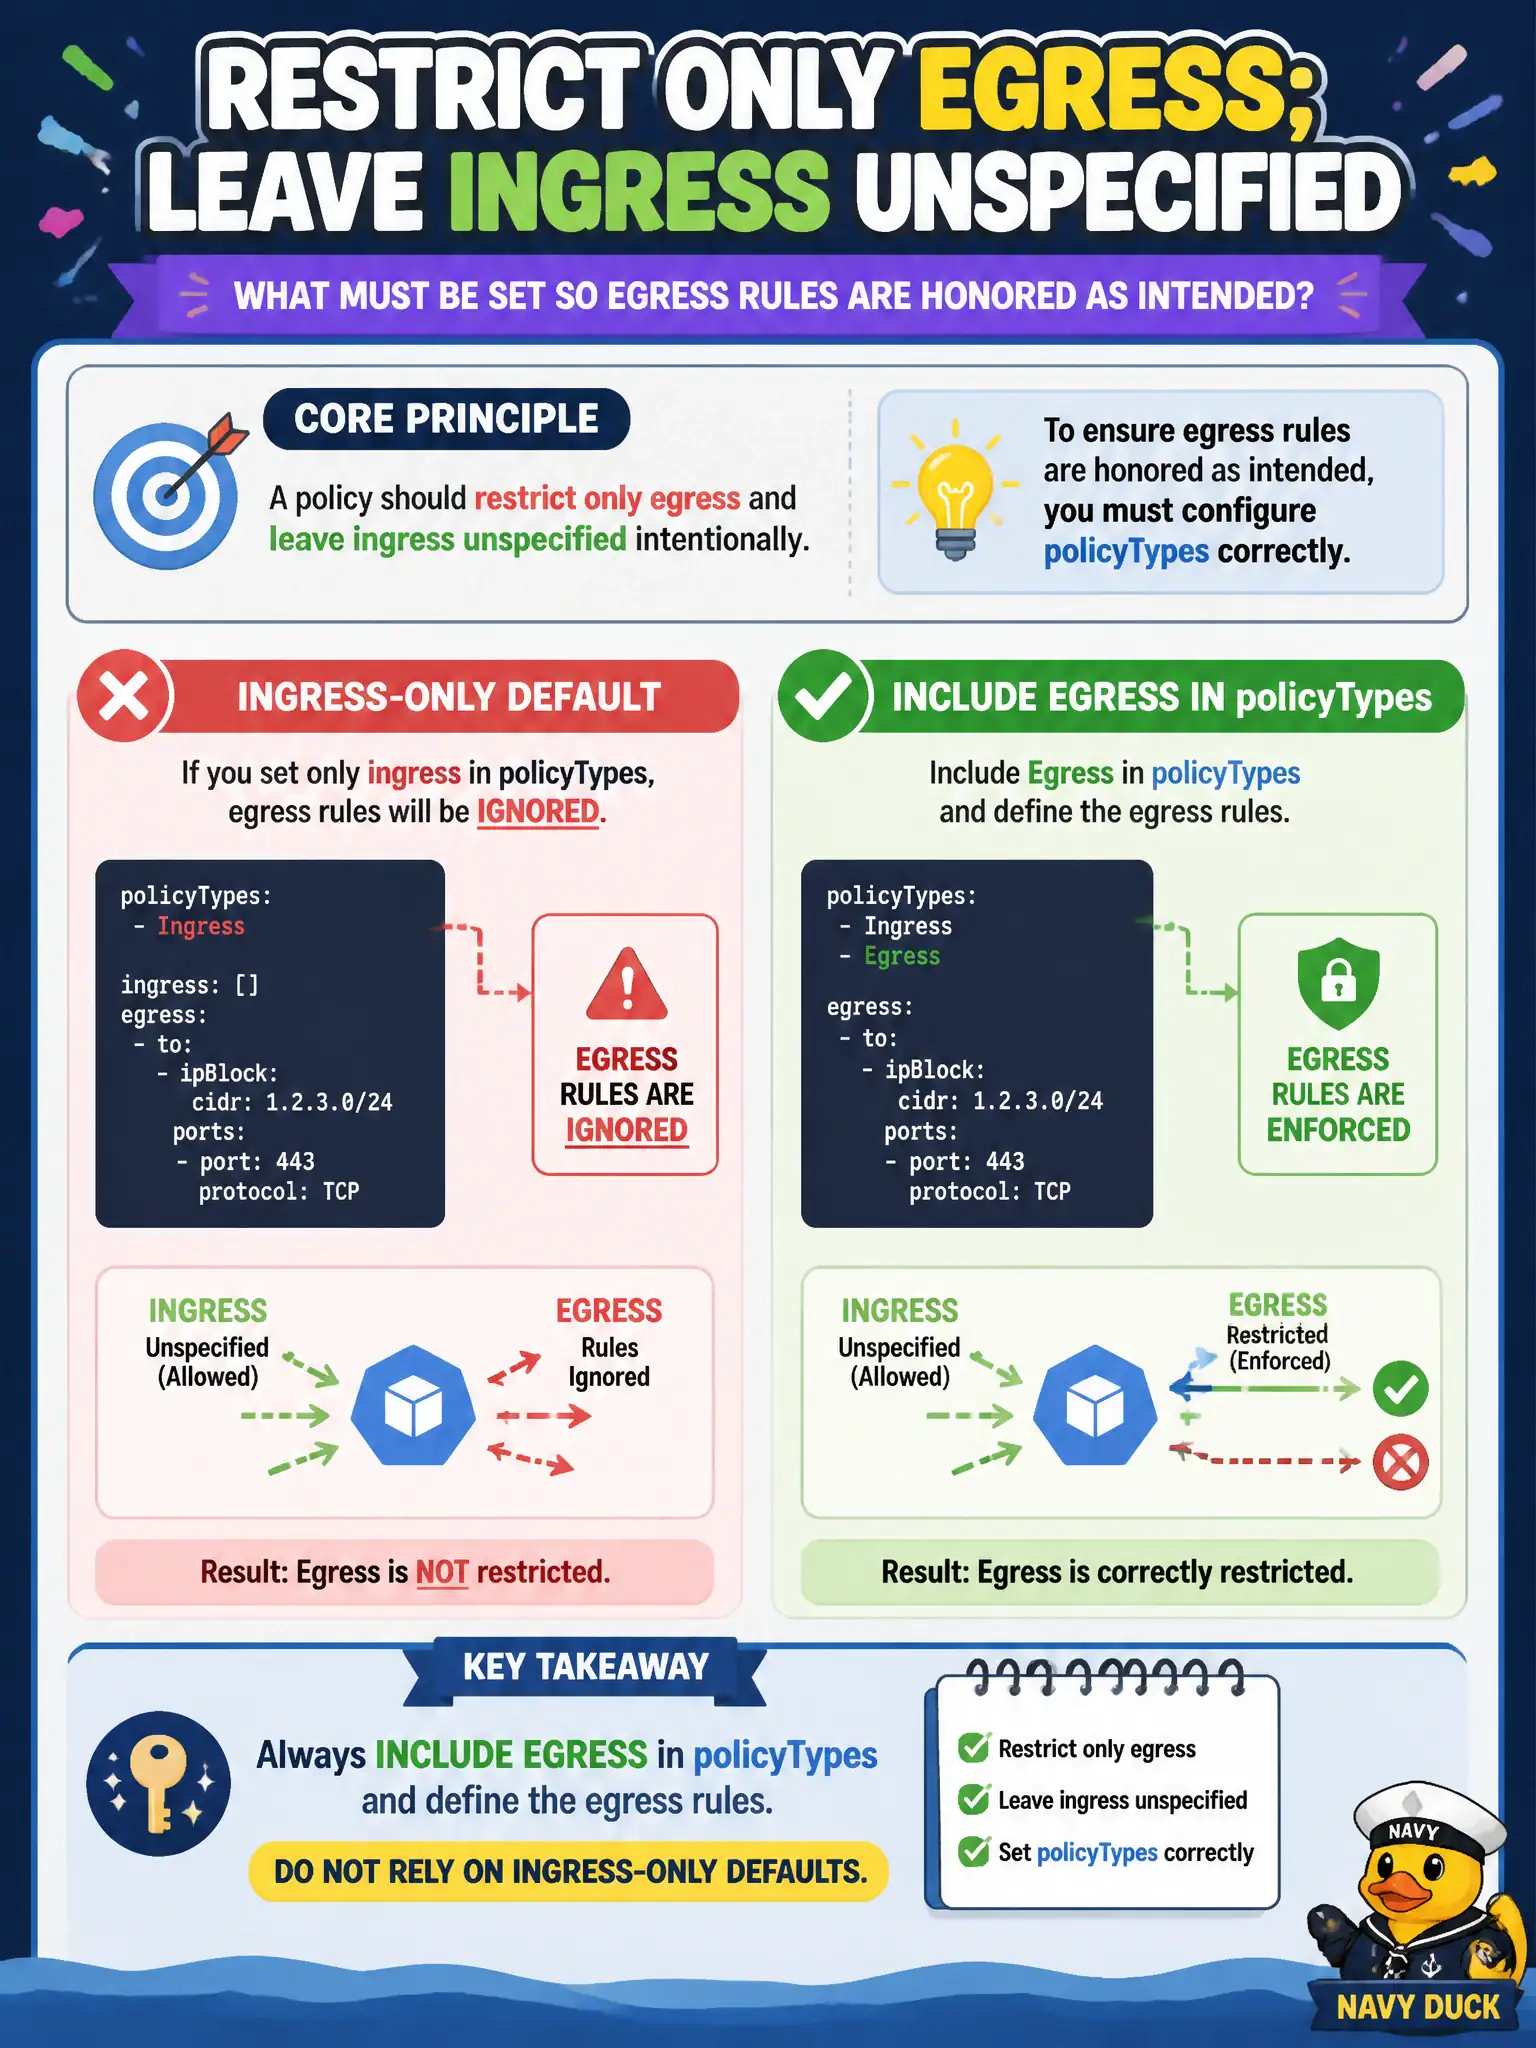
Short Explanation
policyTypes is the label on the jar that says what's inside—if you mean egress, list Egress. Don't hide egress rules under an Ingress-only jar or on Service externalIPs.
Full Explanation
policyTypes declares which traffic directions a NetworkPolicy intends to govern. If a policy should restrict only egress and leave ingress unspecified intentionally, include Egress in policyTypes and define the egress rules. Do not rely on ingress-only defaults or on hiding egress intent in the wrong field. policyTypes is the label on the jar that says what is inside—if you mean egress, list Egress so implementations honor the egress rules as intended.
Omitting policyTypes entirely and listing only ingress rules does not force an egress deny. Setting policyTypes to Ingress only while putting rules under the egress field mismatches the declared direction and can leave egress unenforced relative to your intent. Putting egress CIDRs in the Service externalIPs field is unrelated to NetworkPolicy policyTypes and does not implement Pod egress filtering.
Exam caveat: for egress-only or ingress-only policies, set policyTypes explicitly to avoid cross-implementation ambiguity on exams and in production. Operational check: kubectl get networkpolicy -o yaml and verify policyTypes includes Egress when egress rules are present; from the selected Pod, test outbound connects to allowed versus denied destinations for the municipal workload; keep both results with the change record so reviewers see that egress enforcement matches the YAML.