
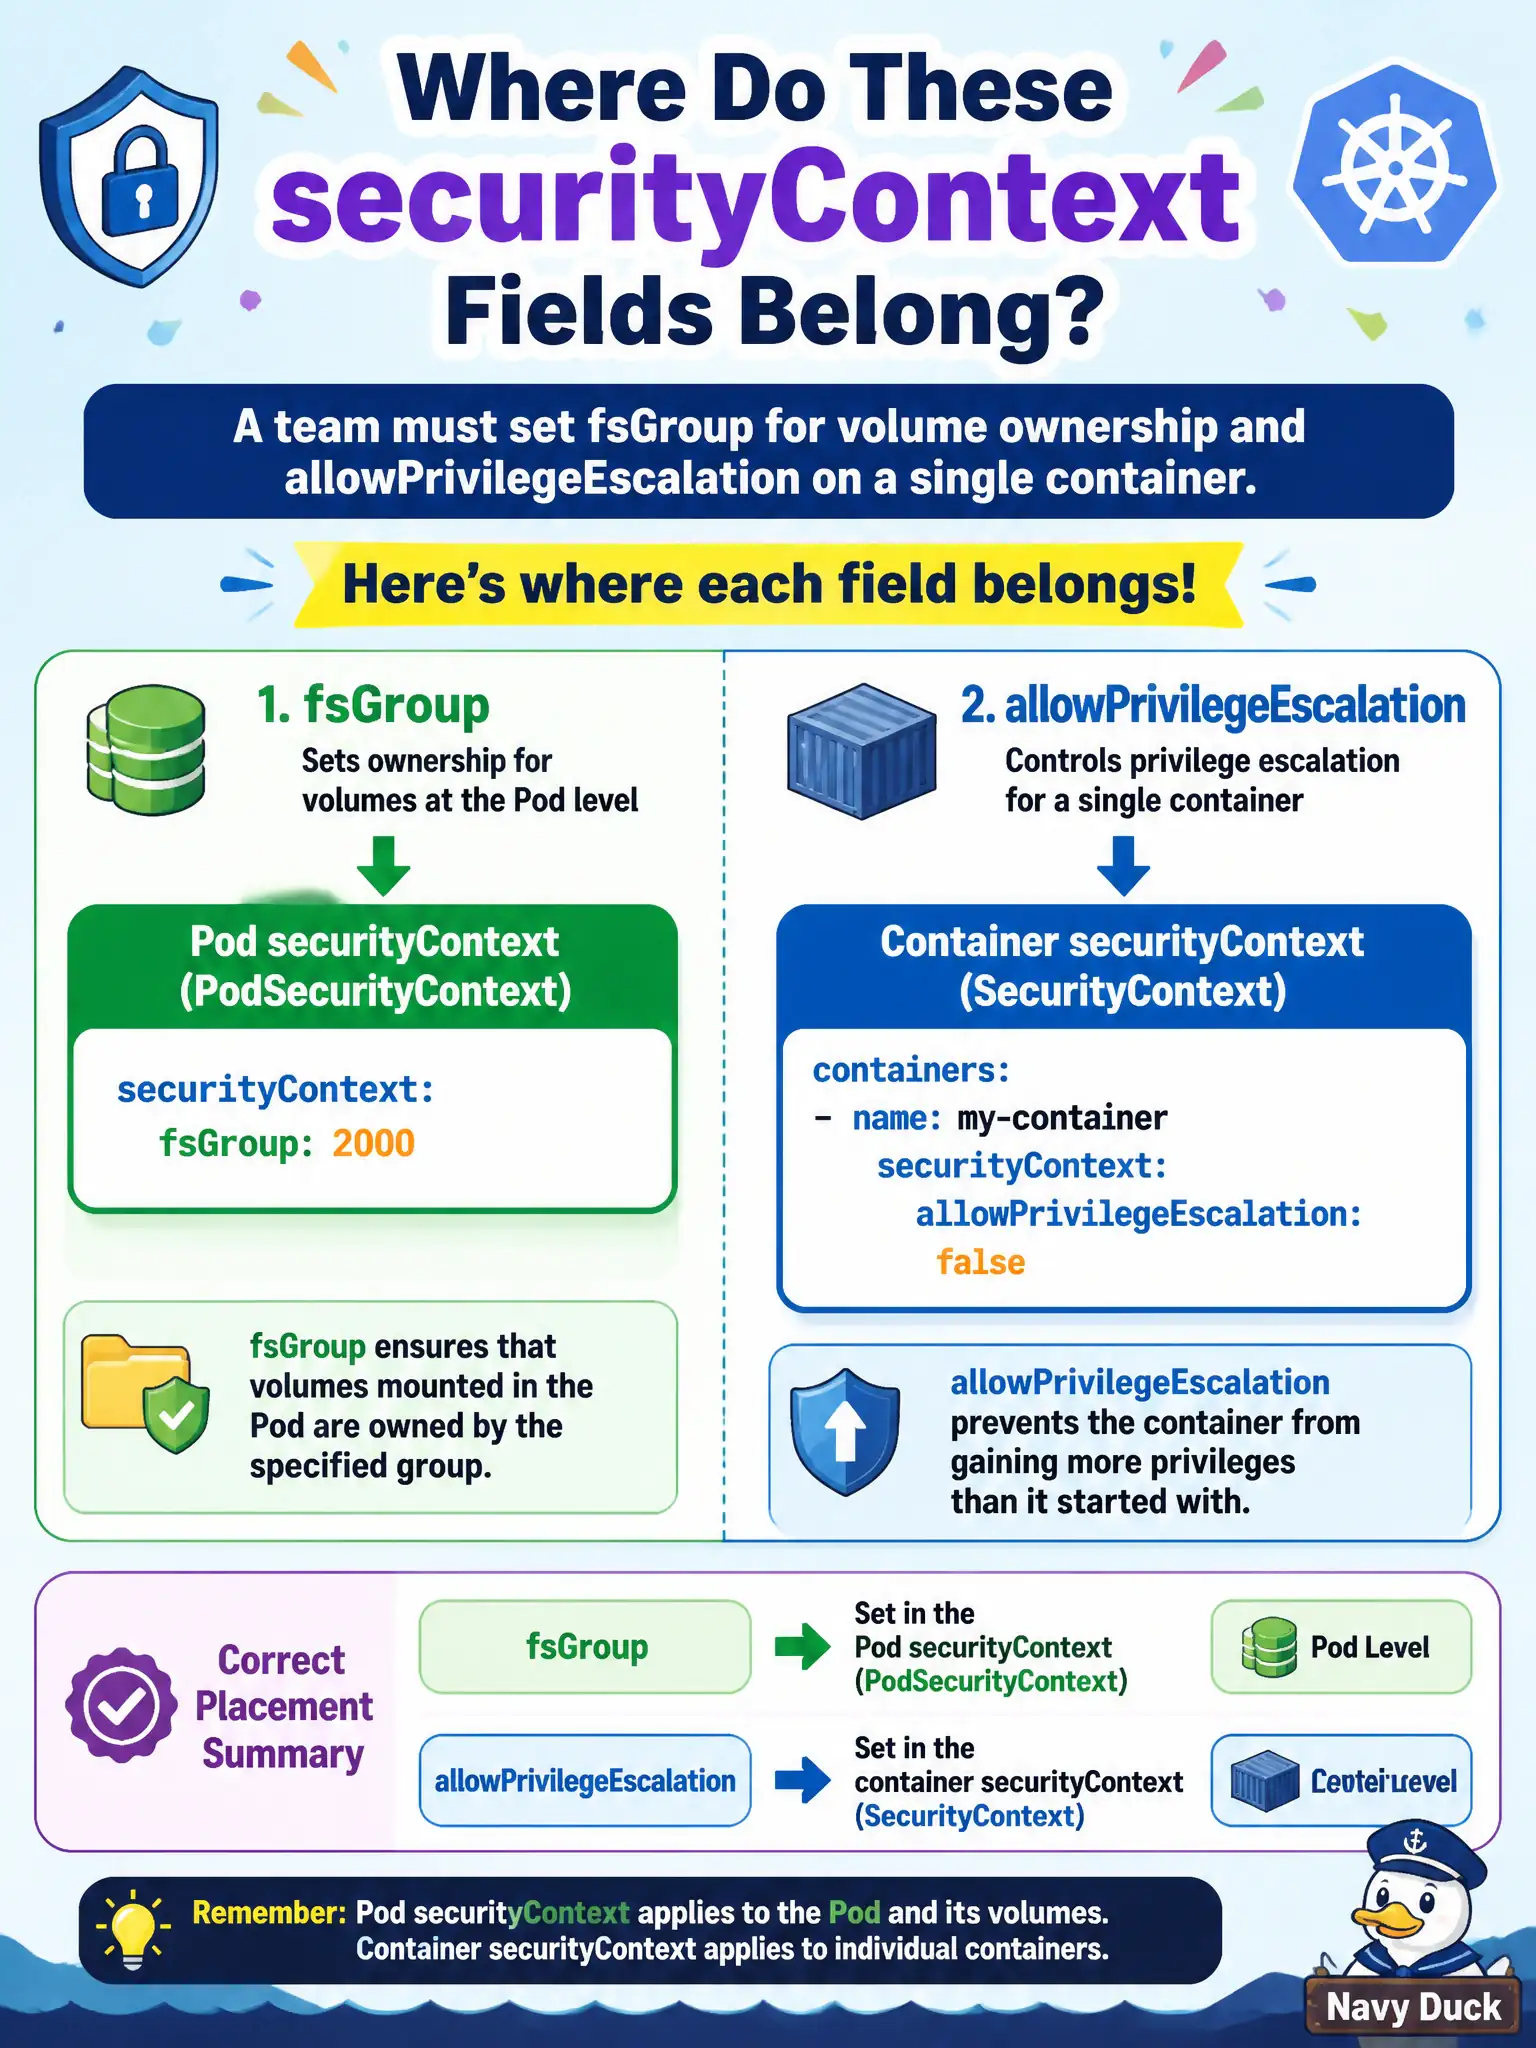
A team must set fsGroup for volume ownership and allowPrivilegeEscalation on a single container. Where do these securityContext fields belong?
Select an answer to reveal the explanation.
Short Explanation
Pod-level context is the shared apartment rules (like fsGroup for volumes); container-level is each roommate's personal locks (like allowPrivilegeEscalation). Put each field where the API actually defines it—not on Services or Ingress.
Full Explanation
Kubernetes splits security settings between PodSecurityContext and per-container securityContext. fsGroup is a Pod-level field: it belongs under spec.securityContext on the Pod (PodSecurityContext) so volume ownership/group permissions apply to the Pod’s mounts for processes sharing that supplemental group. allowPrivilegeEscalation is a container-level field: it belongs under each container’s securityContext because privilege escalation policy is evaluated per container. For a municipal app that must set both, place fsGroup on the Pod securityContext and allowPrivilegeEscalation on the container securityContext.
Putting both fields only under the container securityContext fails for fsGroup—the API does not treat fsGroup as a container field in the way candidates often assume. Putting both only under the Pod securityContext fails for allowPrivilegeEscalation, which is not a PodSecurityContext field containers somehow inherit as an override ban in that simplified way. Placing fsGroup on a Service or allowPrivilegeEscalation on an Ingress is nonsensical: those objects do not define Pod process security contexts.
Exam caveat: memorize which fields are Pod-scoped (fsGroup, supplementalGroups, runAsUser defaults, seccompProfile at Pod level) versus container-scoped (allowPrivilegeEscalation, capabilities, readOnlyRootFilesystem, privileged). Operational check: kubectl explain pod.spec.securityContext and kubectl explain pod.spec.containers.securityContext to confirm field homes; apply a Pod with fsGroup at Pod level and allowPrivilegeEscalation false at container level; describe the running Pod and verify volume group access works for the city app’s mounted volumes while privilege escalation remains disabled.