
A civic HTTPS reverse-proxy container only needs to bind privileged ports. How should Linux capabilities be configured for least privilege?
Select an answer to reveal the explanation.
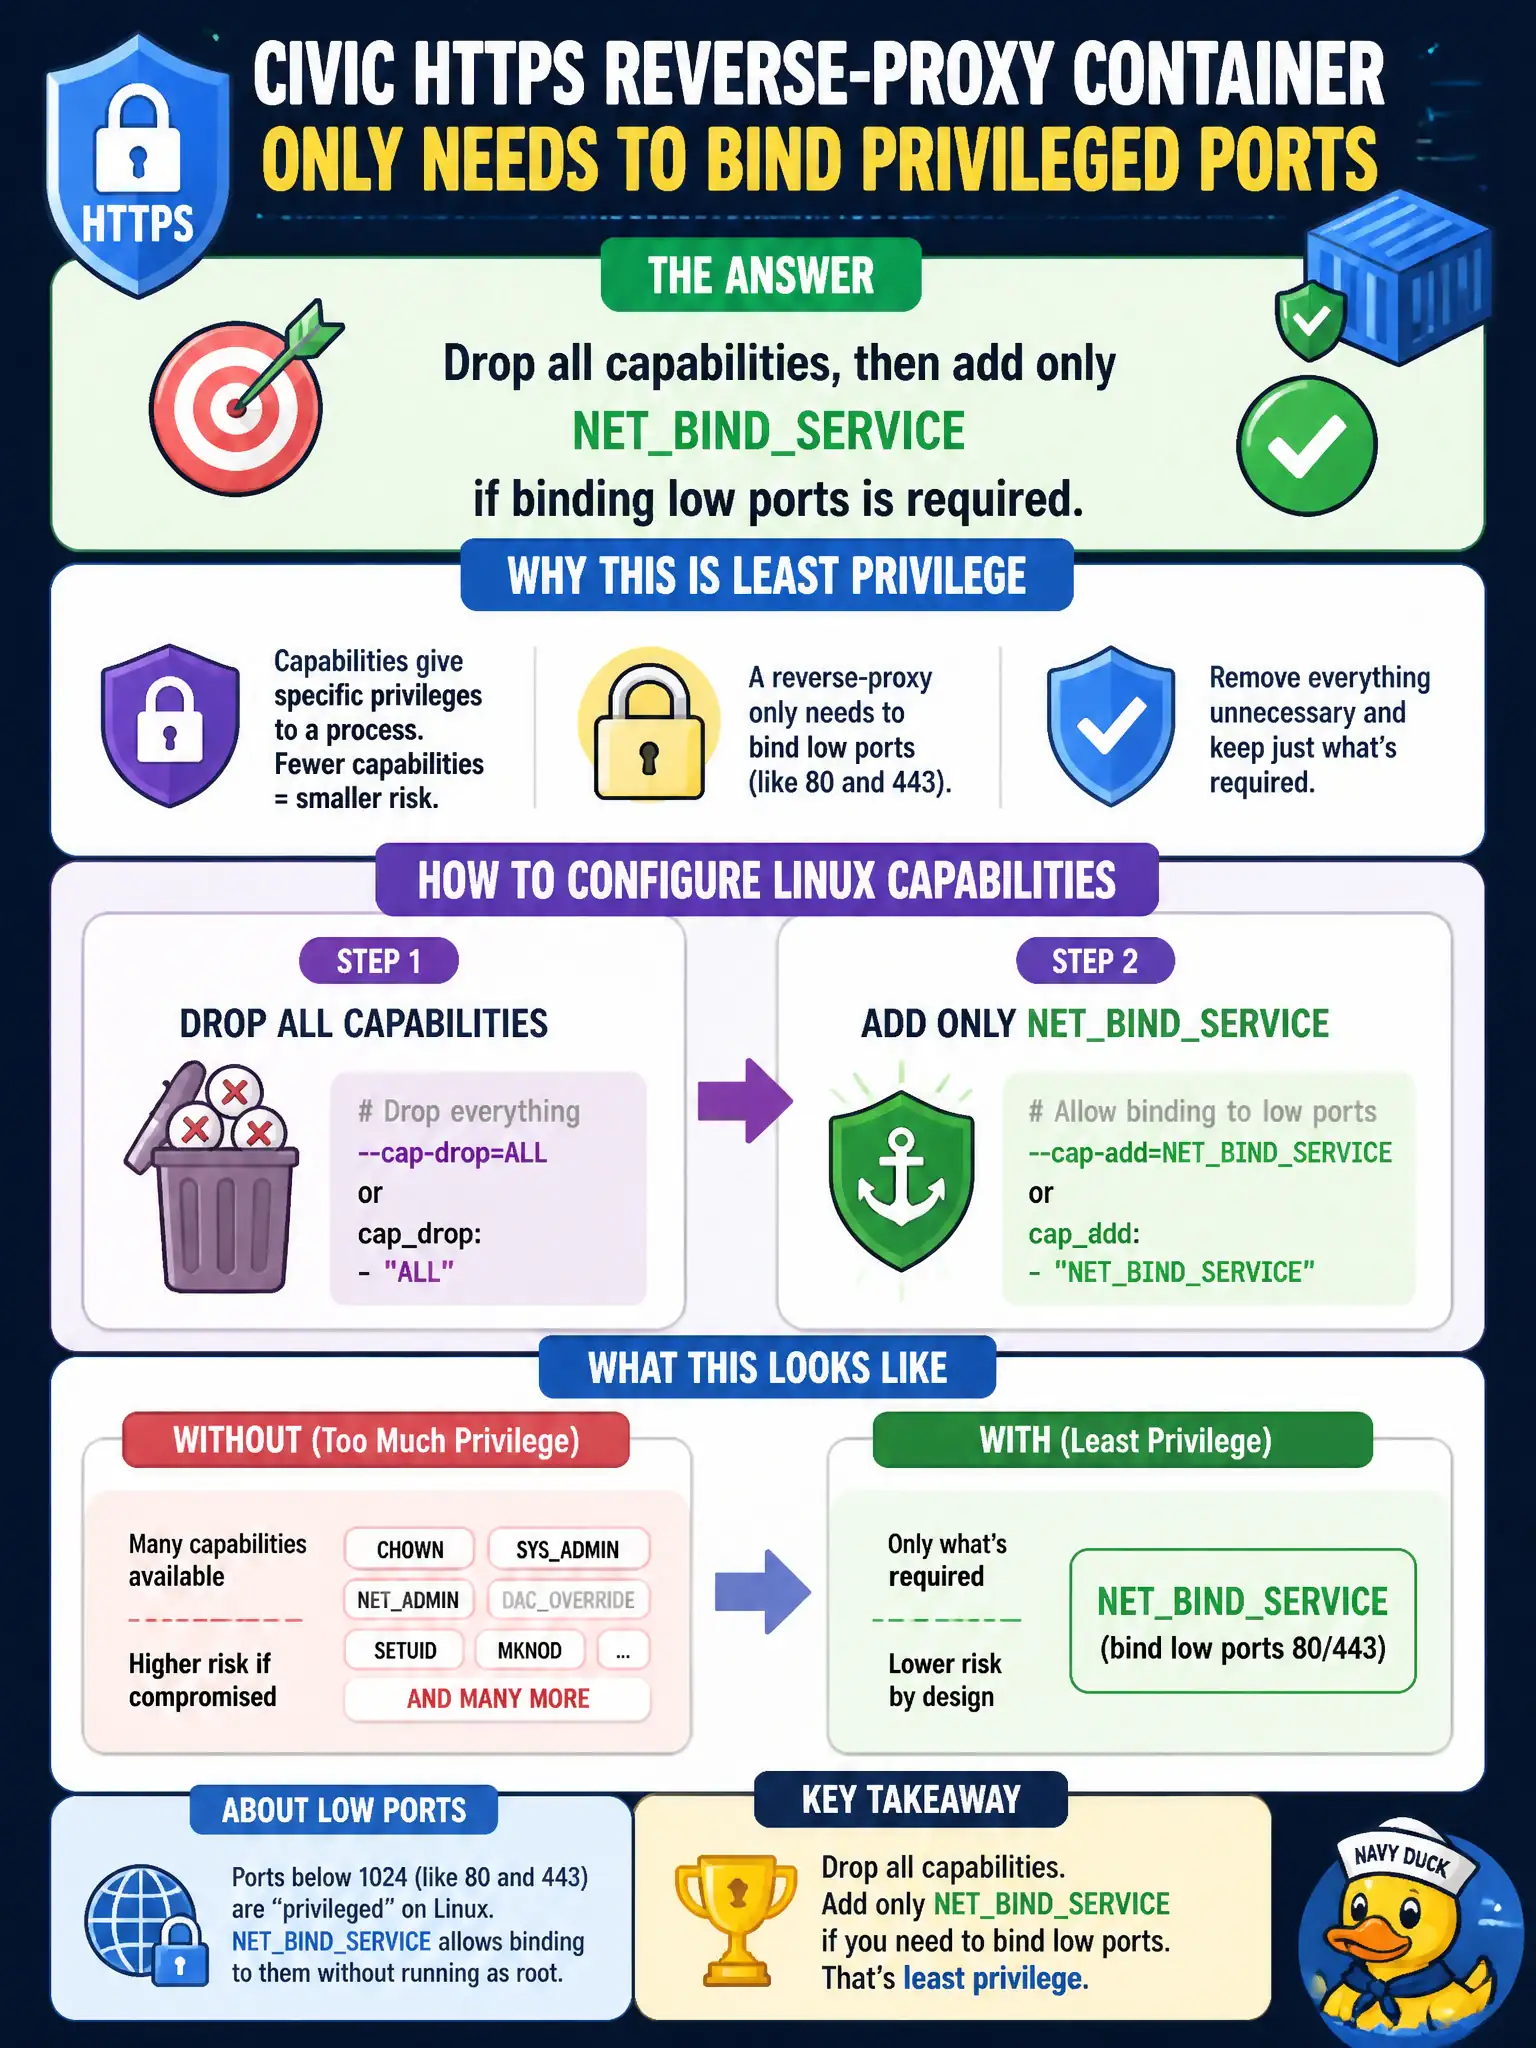
Short Explanation
Capabilities are like individual power tools—don't hand over the whole workshop. Drop ALL, then add back only NET_BIND_SERVICE if the proxy must bind low ports. Privileged or SYS_ADMIN is a sledgehammer for a thumbtack job.
Full Explanation
Linux capabilities are fine-grained privileges. For a civic HTTPS reverse-proxy that only needs to bind privileged ports (below 1024), least privilege means dropping everything and adding back only what is required. The standard pattern is capabilities.drop: ["ALL"] and then capabilities.add: ["NET_BIND_SERVICE"] when binding low ports is truly needed. That gives the proxy the one power tool required for low-port binds without handing over the entire workshop of host-affecting capabilities.
privileged: true effectively opens nearly all capabilities and demolishes isolation; it is not an acceptable shortcut “so you do not have to list capabilities.” Adding CAP_SYS_ADMIN and CAP_NET_ADMIN by default for any network-facing Pod massively overscopes routine proxies—those capabilities enable broad administrative actions far beyond bind-to-low-port. Omitting capabilities settings and relying only on the image USER directive does not drop ambient capability sets the runtime may still grant; USER changes UID but is not a complete substitute for explicit capability drop/add in securityContext.
Exam caveat: NET_BIND_SERVICE is specifically about binding privileged ports; it is not a general “network admin” capability. Prefer non-privileged high ports plus a Service/Ingress in front when city policy allows, so you may not need NET_BIND_SERVICE at all. Operational check: inspect the Pod securityContext.capabilities after deploy; confirm drop includes ALL and add is limited to NET_BIND_SERVICE (or empty if high ports are used); verify the proxy still listens as designed, and that privileged remains false. Document why the city reverse-proxy needs low ports if NET_BIND_SERVICE is retained.