
Platform policy for ordinary city apps requires containers not to gain extra privileges beyond their start UID. Which securityContext field should be set to false by default?
Select an answer to reveal the explanation.
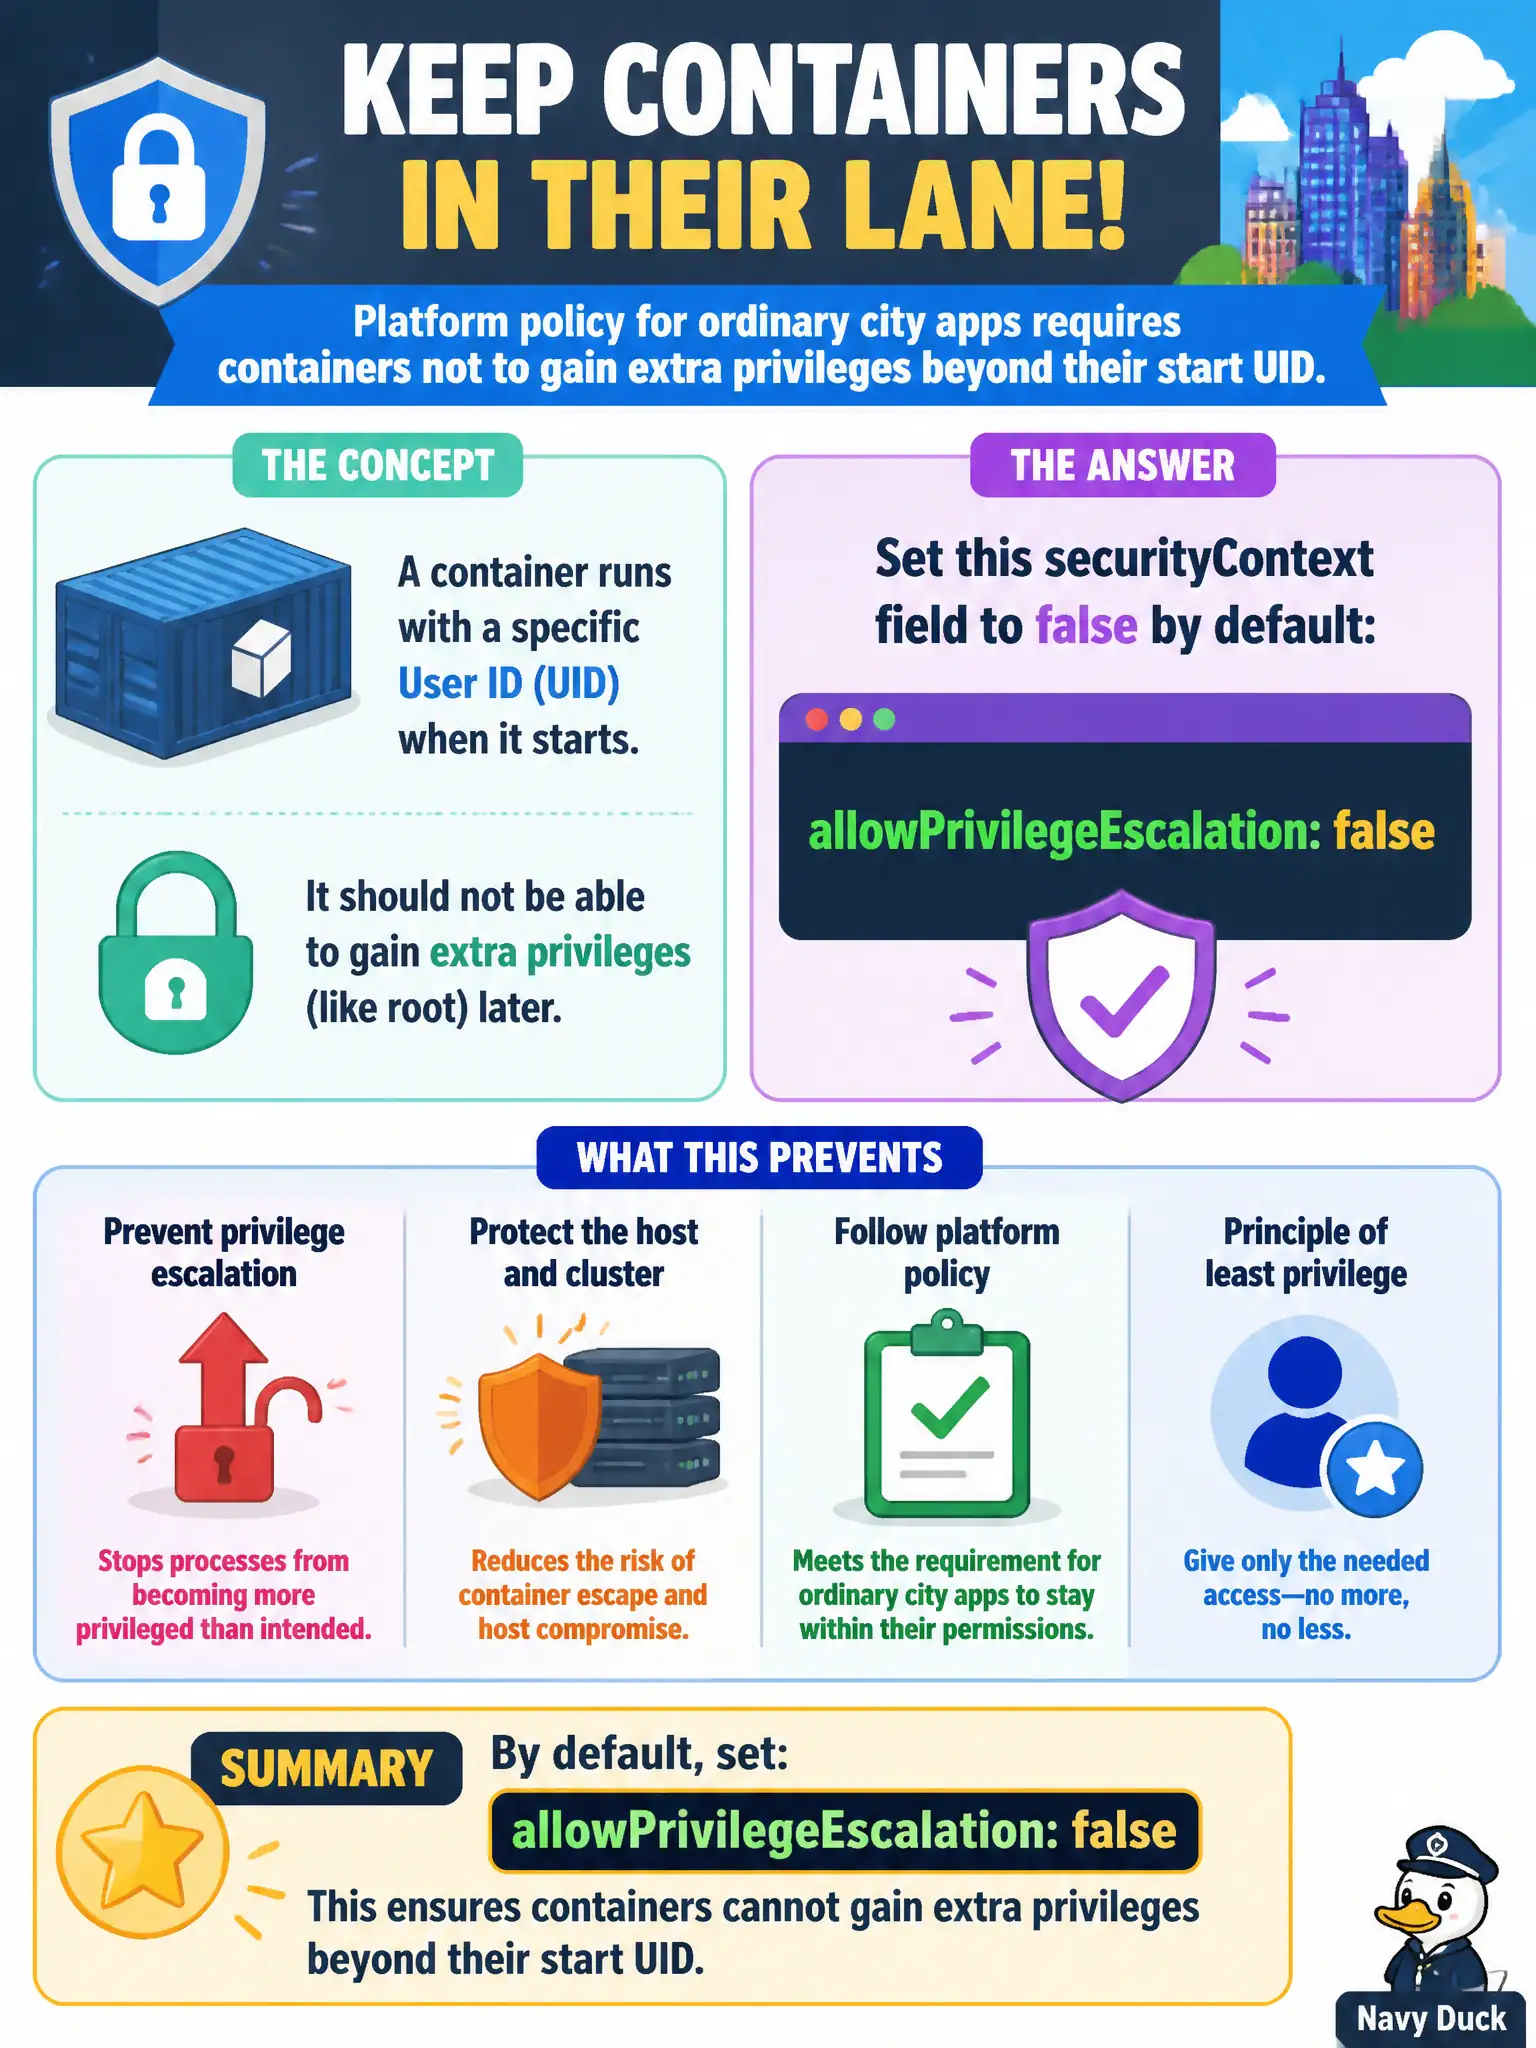
Short Explanation
allowPrivilegeEscalation is the "can this process grab a bigger badge later?" switch. Setting it false blocks setuid-style jumps above the container's start privileges. Turning other hardening flags off—or enabling privileged—goes the wrong way.
Full Explanation
Ordinary city application containers should not be allowed to gain privileges beyond those they start with. allowPrivilegeEscalation: false in the container securityContext blocks that path—for example, setuid binaries that would otherwise let a process obtain a higher effective privilege set than its parent. Platform baselines for municipal apps commonly set this to false by default so a compromised or poorly written process cannot escalate inside the container.
Setting readOnlyRootFilesystem: false only controls whether the root filesystem is writable; it is unrelated to privilege escalation and leaving it false is often the opposite of hardening. Setting runAsNonRoot: false explicitly allows root, which weakens identity policy rather than blocking escalation. Setting privileged: true grants broad host-level capabilities and is inappropriate as a default for ordinary apps; it is not the field that means “disallow escalation.”
Exam caveat: allowPrivilegeEscalation is a container securityContext field (not a Service or Ingress setting). Even with runAsNonRoot true, leaving allowPrivilegeEscalation true (or unset where the default permits escalation) can still allow privilege gains via setuid-style mechanisms depending on the runtime and image. Operational check: kubectl get deploy <app> -o yaml | grep -A20 securityContext and confirm allowPrivilegeEscalation: false on application containers; validate against Pod Security restricted expectations used by the city platform; try an image that relies on setuid and confirm the hardened Pod behaves as policy intends rather than silently escalating.